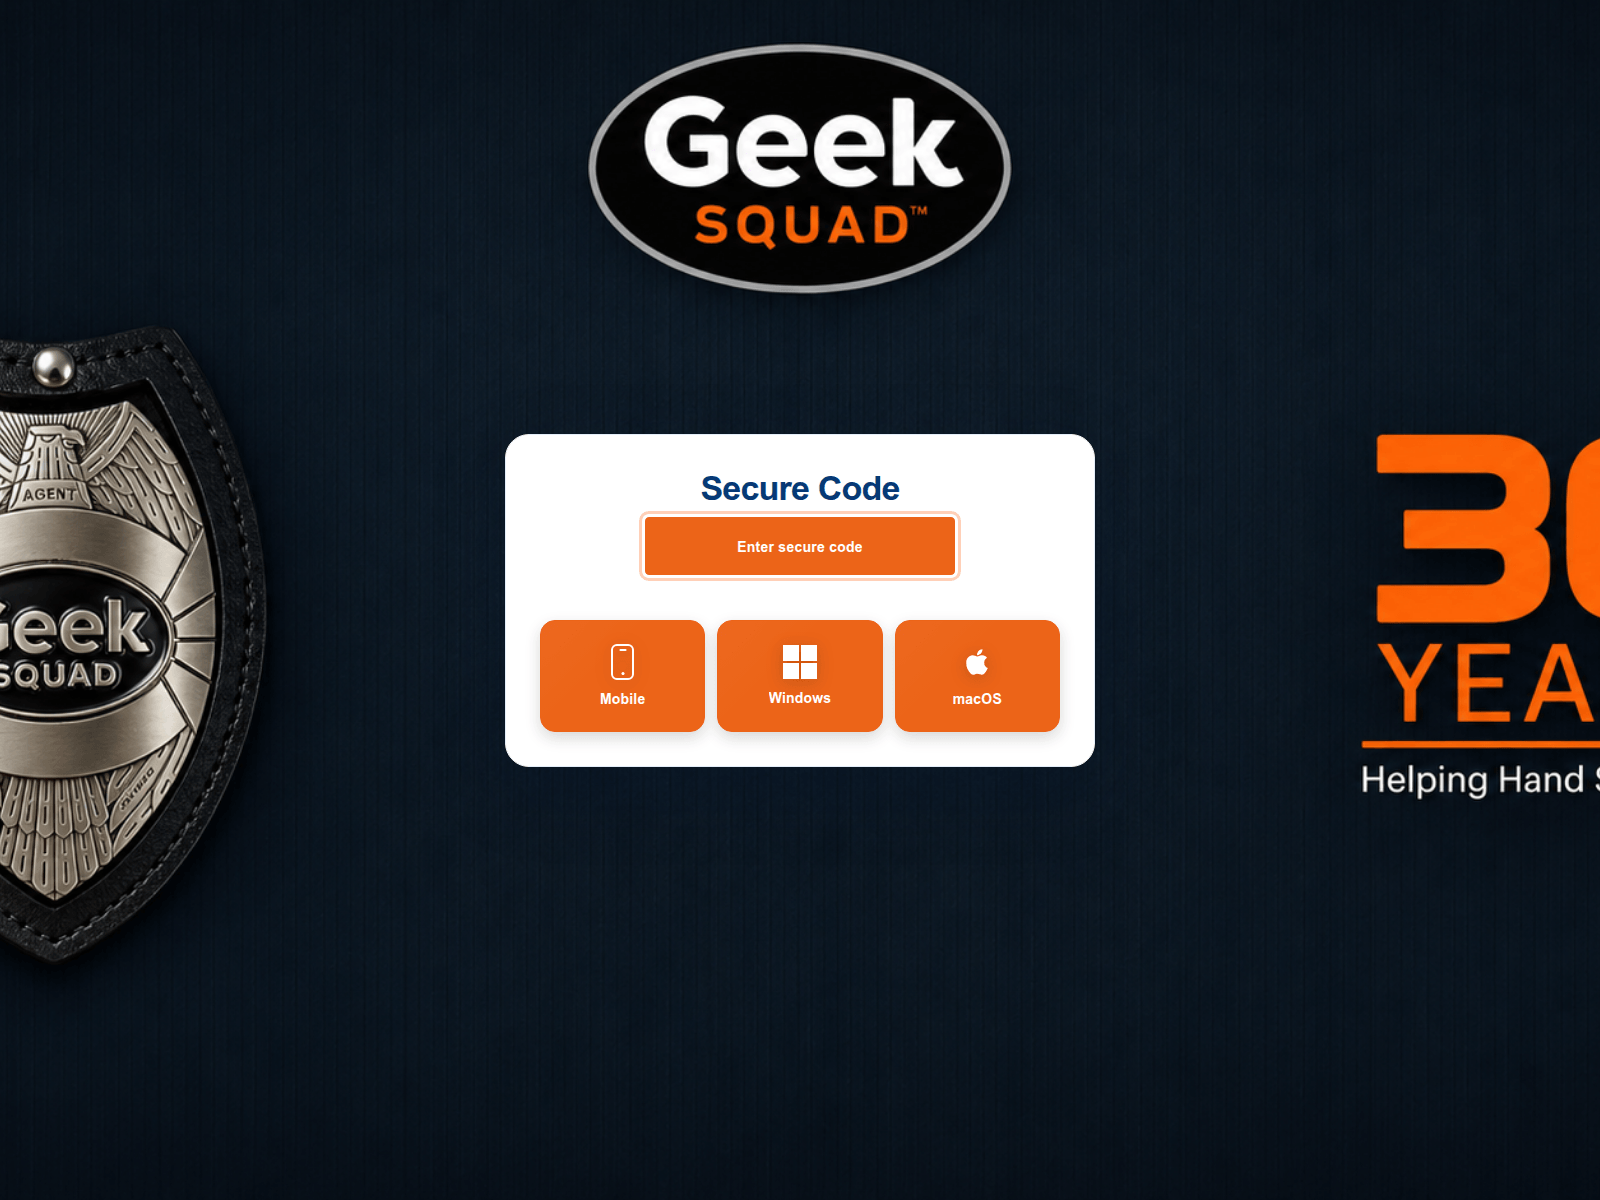
The page at gkksc.top mimics Geek Squad and asks visitors to enter a secure code across mobile or desktop options. If you visited this page and entered any codes or credentials, close the browser tab immediately and verify your account security through official channels.
분석 내용은 영어로만 제공됩니다.
페이지 제목: “Secure Server”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 1/92 엔진에서 경고했습니다. 악성: 0. 의심: 1. 분석 시간(저장된 표기): 2026-11-19 09:11 UTC. 조회 시간(저장된 표기): 2026-11-19 22:27 UTC. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
위험 신호
VirusTotal 탐지: 1/92Spamhaus DBL: 스팸 도메인젊은 도메인: 12일 전
URLScan 캡처 · 2026-11-19 22:45 UTC · SHA-256 231ddc0f…9e3062b
PhishDestroy 분석, 검토 완료된 버전
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Geek Squad support code interface
The page displays a dark background featuring the prominent "Geek Squad" oval logo at the top alongside a metallic badge graphic and text referencing thirty years of service. In the center, a white card titled "Secure Code" provides an orange button labeled "Enter secure code" and three options underneath marked "Mobile", "Windows", and "macOS". The design prompts visitors to select a platform or input a verification code provided during a support interaction. This visual arrangement mimics legitimate remote assistance portals to convince visitors they are interacting with official technical support staff.
Registration timeline and security standing
It was registered on 10 Nov 2026, 9 days before it was first reported. When a domain uses established brand assets while remaining newly registered, it typically indicates a fraudulent setup designed to intercept user verification codes during fake technical support interactions. Furthermore, Spamhaus DBL lists it as spam, VirusTotal showed 1 of 92 engines flagging it on 19 Nov 2026, and Cloudflare Radar rated it malicious (Security threats, phishing, Security Risks).
Recommended actions and next steps
If you reached this address through an unsolicited phone call or message and entered a secure code, your device or account may be compromised. Contact official support directly through verified corporate channels to check for unauthorized access or persistent remote management tools. Always verify web addresses carefully before inputting credentials or security tokens supplied by external agents.
서술 생성 날짜는 관측 날짜와 별개입니다. 이는 보존된 게시 필드일 뿐, 별도의 독립적인 탐지 결과가 아닙니다.
AI 제목
gkksc.top — Geek Squad secure code verification
AI 설명
gkksc.top features a Geek Squad secure code login form with device selection buttons, flagged by Spamhaus DBL and 1 VirusTotal engine. Avoid submitting.
AI 요약
Geek Squad support code interface The page displays a dark background featuring the prominent "Geek Squad" oval logo at the top alongside a metallic badge graphic and text referencing thirty years of service. In the center, a white card titled "Secure Code" provides an orange button labeled "Enter secure code" and three options underneath marked "Mobile", "Windows", and "macOS". The design prompts visitors to select a platform or input a verification code provided during a support interaction. This visual arrangement mimics legitimate remote assistance portals to convince visitors they are interacting with official technical support staff. Registration timeline and security standing It was registered on 10 Nov 2026, 9 days before it was first reported. When a domain uses established brand assets while remaining newly registered, it typically indicates a fraudulent setup designed to intercept user verification codes during fake technical support interactions. Furthermore, Spamhaus DBL lists it as spam, VirusTotal showed 1 of 92 engines flagging it on 19 Nov 2026, and Cloudflare Radar rated it malicious (Security threats, phishing, Security Risks). Recommended actions and next steps If you reached this address through an unsolicited phone call or message and entered a secure code, your device or account may be compromised. Contact official support directly through verified corporate channels to check for unauthorized access or persistent remote management tools. Always verify web addresses carefully before inputting credentials or security tokens supplied by external agents.
The website's owner is hiding his identity on WHOIS using a paid service This website does not have many visitors We found many low rated websites on the same server This website has only been registered recently. We could not analyze the content of the site
According to the SSL check the certificate is valid
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
Security threats 피싱 피싱 Security Risks New Domains
gkksc.top 관련 질문
gkksc.top은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 gkksc.top를 높음 위험 등급(증거 점수 68/100)으로 평가했으며, 이는 2026-11-19에 처음 기록되었습니다. 저장된 VirusTotal 결과: 1/92 엔진에서 경고했습니다. 악성: 0. 의심: 1. 분석 시간(저장된 표기): 2026-11-19 09:11 UTC. 조회 시간(저장된 표기): 2026-11-19 22:27 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
gkksc.top에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
gkksc.top을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
IP 평판72.51.59.1610/100악용 점수 · 이 서버의 IP 주소에 대한 악용 신고 건수이며, 도메인에 대한 신고 건수가 아닙니다. 점수가 높을수록 상황이 더 심각합니다.이 IP 주소는 아직 악용 데이터베이스에 신고되지 않았으나, 도메인 자체는 피싱으로 인식되고 있습니다.신고 0건확인됨 2026-11-20
1차 평가 변수활성 콘텐츠reason: Ordinary HTTP content served90% confidence
출처source: Current Http Probe
증거 레이어Availability: Content servingContent: Content served at rootDNS: Resolved
최신 HTTP 관측 결과활성 콘텐츠일반 HTTP 콘텐츠 제공90%2026-11-22 11:11 UTC
RDAP 등록
관측된 시간축last reachable: 2026-11-22 11:11 UTClast content: 2026-11-22 11:11 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
기술 · 2 identified
M
Microsoft HTTPAPI
웹 서버
Microsoft HTTPAPI is a kernel-mode HTTP driver in the Windows operating system responsible for handling HTTP requests and responses with efficiency, scalability, and security.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.

 PDR
 72.51.59.161


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT