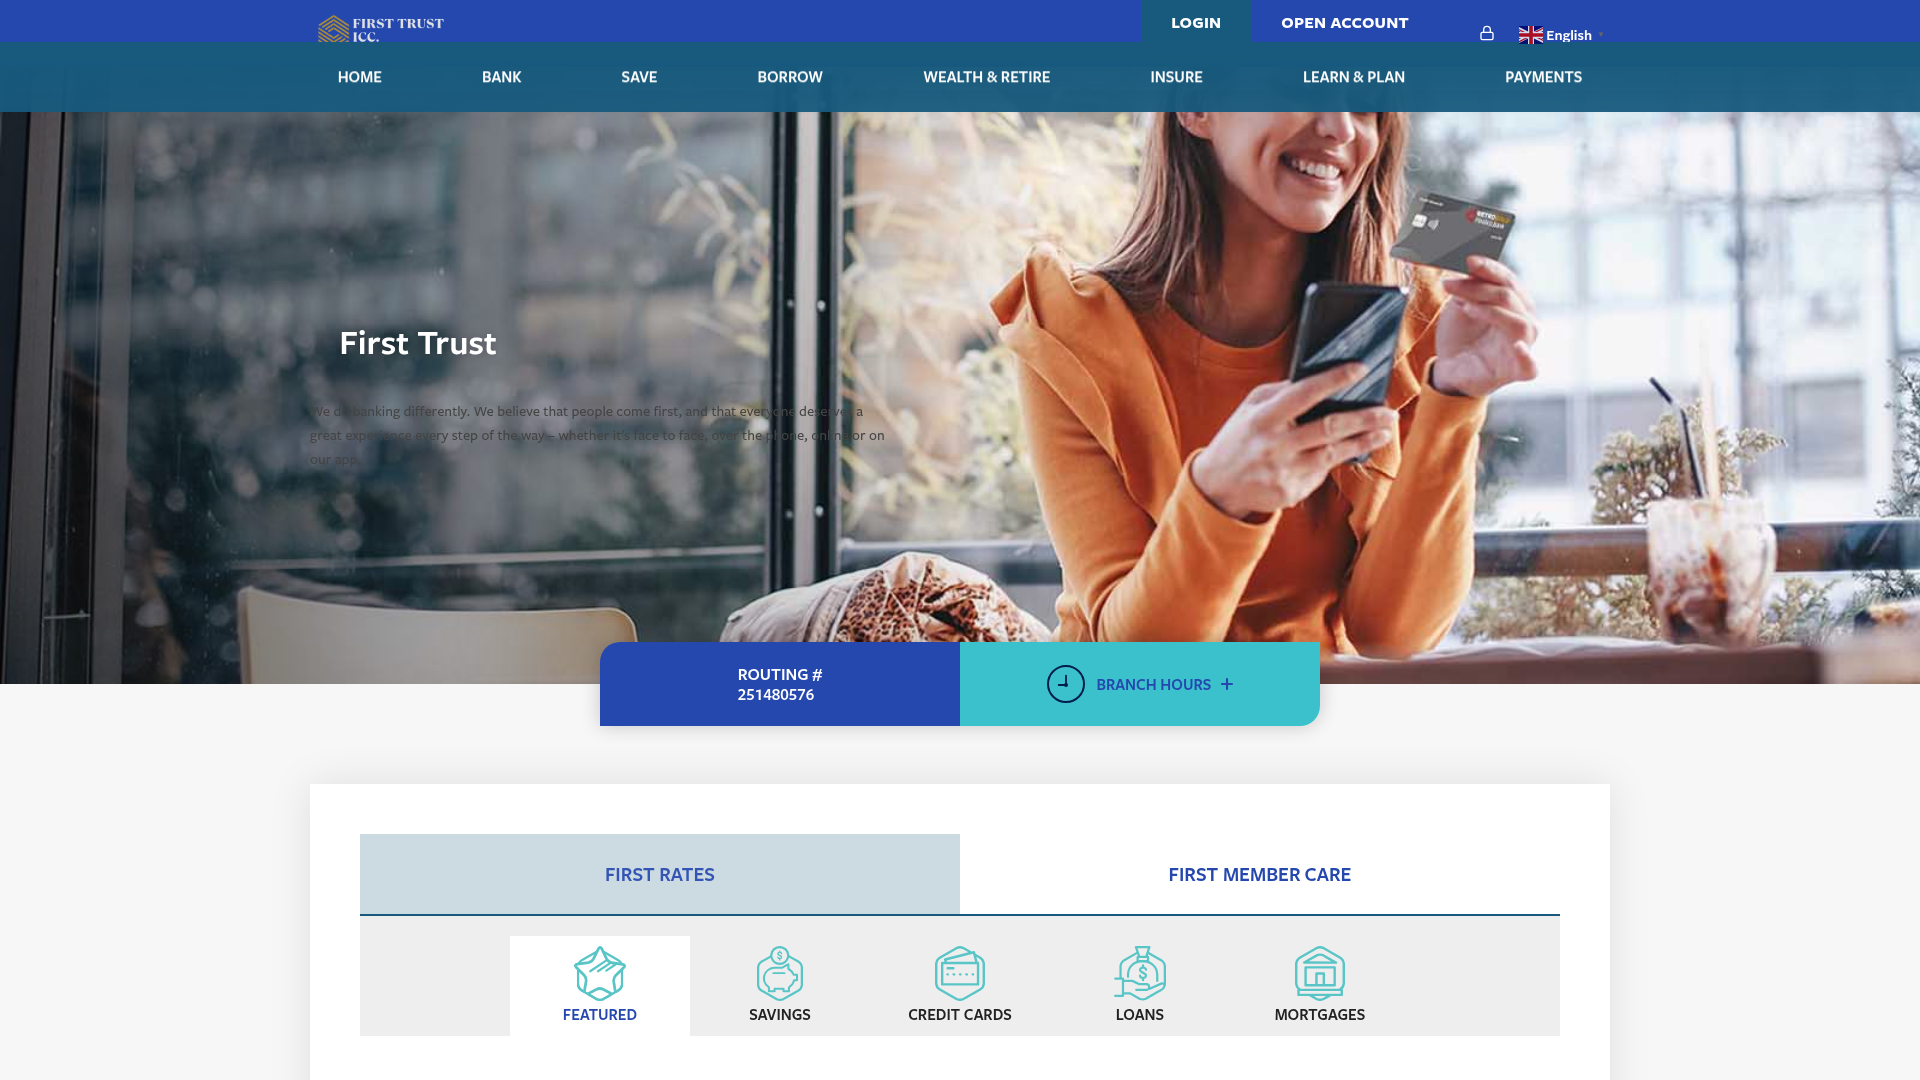
The domain firsttustt.xyz presents a banking portal styled after First Trust, prompting visitors to interact with login and account features. Anyone who entered credentials or personal details should immediately secure their accounts and contact their financial institution.
분석 내용은 영어로만 제공됩니다.
페이지 제목: “Home | Mobile Banking, Credit Cards, Mortgages, Auto Loan”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 4/92 엔진에서 경고했습니다. 악성: 1. 의심: 3. 분석 시간(저장된 표기): 2026-11-20 18:15 UTC. 조회 시간(저장된 표기): 2026-11-20 18:49 UTC. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
전문가용 보기에는 DNS, TLS, 네트워크 요청, 해시, 원시 JSON 등 모든 섹션이 포함되어 있습니다.
ABUSE NOTICE · 24H+ OPEN 발송된 악용 신고는 기록되며, 저장된 최신 가용성 증거에 따르면 해당 도메인은 여전히 접속 가능한 상태입니다.
통지 및 현재 상황 관련 증거
전송된 보고서 원장에는 첫 번째 발신 보고서가 . 기록된 수신자: abuse@cosmotown.com. 가장 최근에 저장된 가용성 정보에 따르면 해당 도메인은 여전히 접속 가능한 것으로 나타납니다.; 38 hours 첫 번째 발신 보고서 이후로 시간이 지났습니다.
ICANN RAA §3.18 등록기관의 악용 신고 연락처 및 처리 의무를 설명합니다. 이 섹션에는 발신 타임스탬프, 수신자 목록, 사건 식별자 및 추후 확인 가능 여부가 기록됩니다. 이 정보만으로는 수신, 확인, 조사, 시정 조치 또는 계약 불이행을 입증할 수 없습니다.
첫 보고 이후 경과한 기간
38 hours
발송된 신고
1
최신 사례 ID
PD-9B40AEC52BCFF2655995
현재 현황
HTTP 200 가장 최근에 저장된 검사 결과
보고서 요약
PhishDestroy에 firsttustt.xyz 기록이 저장되어 있습니다. 각 출처의 관측 날짜는 다르며, 검사가 없다는 사실은 안전을 의미하지 않습니다.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
분석
도메인 요약
PhishDestroy는 2026-11-20에 firsttustt.xyz를 처음 기록했습니다. 저장된 VirusTotal 결과: 4/92 엔진에서 경고했습니다. 악성: 1. 의심: 3. 분석 시간(저장된 표기): 2026-11-20 18:15 UTC. 조회 시간(저장된 표기): 2026-11-20 18:49 UTC. 위험도: 심각 (증거 점수 80/100). 등록 대행자: TuringSign. 상태: 마지막으로 확인된 활성 상태. 호스팅: NEW DHAKA HARDWARE. PhishDestroy는 악용 신고 1건을 보냈습니다. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Visual layout and design elements
The website firsttustt.xyz displays a deep blue top navigation bar bearing the logo "FIRST TRUST ICC." along with links for "HOME", "BANK", "SAVE", "BORROW", "WEALTH & RETIRE", "INSURE", "LEARN & PLAN", and "PAYMENTS", plus buttons labeled "LOGIN" and "OPEN ACCOUNT". The hero section features a large background image of a person holding a phone and a card, accompanied by the heading "First Trust" and subtitle text reading "We do banking differently. We believe that people come first...". Below the main image, two prominent buttons display "ROUTING # 251480576" and "BRANCH HOURS +". Further down, a card component provides tabs for "FIRST RATES" and "FIRST MEMBER CARE", alongside icons for "FEATURED", "SAVINGS", "CREDIT CARDS", "LOANS", and "MORTGAGES". The page asks visitors to explore standard banking products and directs them toward login or account opening routines.
Security vendor tracking and telemetry
urlscan classified the page as malicious, and 4 of 92 VirusTotal engines flagged it on 20 Nov 2026. PhishDestroy's evidence score for it is 45/100 (high). Netcraft, Forcepoint ThreatSeeker and Fortinet are among the security entities tracking the site, which helps confirm that the address is recognized as suspicious across multiple independent telemetry feeds.
Recommended protective actions
Visitors who have interacted with firsttustt.xyz by submitting login credentials or personal information must act immediately to protect their assets. Contact your actual financial institution to freeze affected accounts, change online banking passwords, and enable multi-factor authentication if it was not already active. Always verify that URLs match the official institution before entering sensitive data.
서술 생성 날짜는 관측 날짜와 별개입니다. 이는 보존된 게시 필드일 뿐, 별도의 독립적인 탐지 결과가 아닙니다.
AI 제목
firsttustt.xyz — First Trust banking layout clone
AI 설명
firsttustt.xyz copies First Trust financial pages and prompts users to log in, flagged by urlscan and 4 VirusTotal engines. Verify addresses before logging in.
AI 요약
Visual layout and design elements The website firsttustt.xyz displays a deep blue top navigation bar bearing the logo "FIRST TRUST ICC." along with links for "HOME", "BANK", "SAVE", "BORROW", "WEALTH & RETIRE", "INSURE", "LEARN & PLAN", and "PAYMENTS", plus buttons labeled "LOGIN" and "OPEN ACCOUNT". The hero section features a large background image of a person holding a phone and a card, accompanied by the heading "First Trust" and subtitle text reading "We do banking differently. We believe that people come first...". Below the main image, two prominent buttons display "ROUTING # 251480576" and "BRANCH HOURS +". Further down, a card component provides tabs for "FIRST RATES" and "FIRST MEMBER CARE", alongside icons for "FEATURED", "SAVINGS", "CREDIT CARDS", "LOANS", and "MORTGAGES". The page asks visitors to explore standard banking products and directs them toward login or account opening routines. Security vendor tracking and telemetry urlscan classified the page as malicious, and 4 of 92 VirusTotal engines flagged it on 20 Nov 2026. PhishDestroy's evidence score for it is 45/100 (high). Netcraft, Forcepoint ThreatSeeker and Fortinet are among the security entities tracking the site, which helps confirm that the address is recognized as suspicious across multiple independent telemetry feeds. Recommended protective actions Visitors who have interacted with firsttustt.xyz by submitting login credentials or personal information must act immediately to protect their assets. Contact your actual financial institution to freeze affected accounts, change online banking passwords, and enable multi-factor authentication if it was not already active. Always verify that URLs match the official institution before entering sensitive data.
According to Tranco this site has a low rank High number of suspicious websites on this server This website is (very) young. The website offers data-sensitive [financial] services hosted on a shared server.
This website offers "get your money back" friendly payment methods The SSL certificate is valid This website is safe according to DNSFilter
firsttustt.xyz 관련 질문
firsttustt.xyz은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 firsttustt.xyz를 심각 위험 등급(증거 점수 80/100)으로 평가했으며, 이는 2026-11-20에 처음 기록되었습니다. 저장된 VirusTotal 결과: 4/92 엔진에서 경고했습니다. 악성: 1. 의심: 3. 분석 시간(저장된 표기): 2026-11-20 18:15 UTC. 조회 시간(저장된 표기): 2026-11-20 18:49 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
firsttustt.xyz에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
firsttustt.xyz을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
IP 평판163.61.188.527/100악용 점수 · 이 서버의 IP 주소에 대한 악용 신고 건수이며, 도메인에 대한 신고 건수가 아닙니다. 점수가 높을수록 상황이 더 심각합니다.신고 245건피싱Web SpamBlog Spam포트 스캔해킹Brute-Force나쁜 웹 봇Exploited Host웹 애플리케이션 공격SSH확인됨 2026-11-20마지막 신고일
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.


 163.61.188.5


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT