전문가용 보기에는 DNS, TLS, 네트워크 요청, 해시, 원시 JSON 등 모든 섹션이 포함되어 있습니다.
ABUSE NOTICE · 7D+ OPEN 발송된 악용 신고는 기록되며, 저장된 최신 가용성 증거에 따르면 해당 도메인은 여전히 접속 가능한 상태입니다.
통지 및 현재 상황 관련 증거
전송된 보고서 원장에는 첫 번째 발신 보고서가 . 기록된 수신자: abuse@tencent.com. 가장 최근에 저장된 가용성 정보에 따르면 해당 도메인은 여전히 접속 가능한 것으로 나타납니다.; 27 days 첫 번째 발신 보고서 이후로 시간이 지났습니다.
ICANN RAA §3.18 등록기관의 악용 신고 연락처 및 처리 의무를 설명합니다. 이 섹션에는 발신 타임스탬프, 수신자 목록, 사건 식별자 및 추후 확인 가능 여부가 기록됩니다. 이 정보만으로는 수신, 확인, 조사, 시정 조치 또는 계약 불이행을 입증할 수 없습니다.
첫 보고 이후 경과한 기간
27 days
발송된 신고
1
최신 사례 ID
PD-20261025-75CD0A
현재 현황
가장 최근에 저장된 검사 시점에서 활성 상태로 관측됨
보고서 요약
PhishDestroy에 ebaymevip.com 기록이 저장되어 있습니다. 각 출처의 관측 날짜는 다르며, 검사가 없다는 사실은 안전을 의미하지 않습니다.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
분석
도메인 요약
PhishDestroy는 2026-10-25에 ebaymevip.com를 처음 기록했습니다. 저장된 VirusTotal 결과: 17/92 엔진에서 경고했습니다. 악성: 16. 의심: 1. 분석 시간(저장된 표기): 2026-10-25 15:22 UTC. 조회 시간(저장된 표기): 2026-10-25 20:20 UTC. Google 세이프 브라우징이 위험으로 표시. 위험도: 심각 (증거 점수 100/100). 등록 대행자: Aceville. 호스팅: Shenzhen Tencent Computer Systems Company Limited. PhishDestroy는 악용 신고 1건을 보냈습니다. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
심각
VirusTotal
17 / 92
사기 유형 (자동 생성 라벨)
사칭
호스팅
43.135.161.205Shenzhen Tencent Computer Systems Company Limited
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Overview
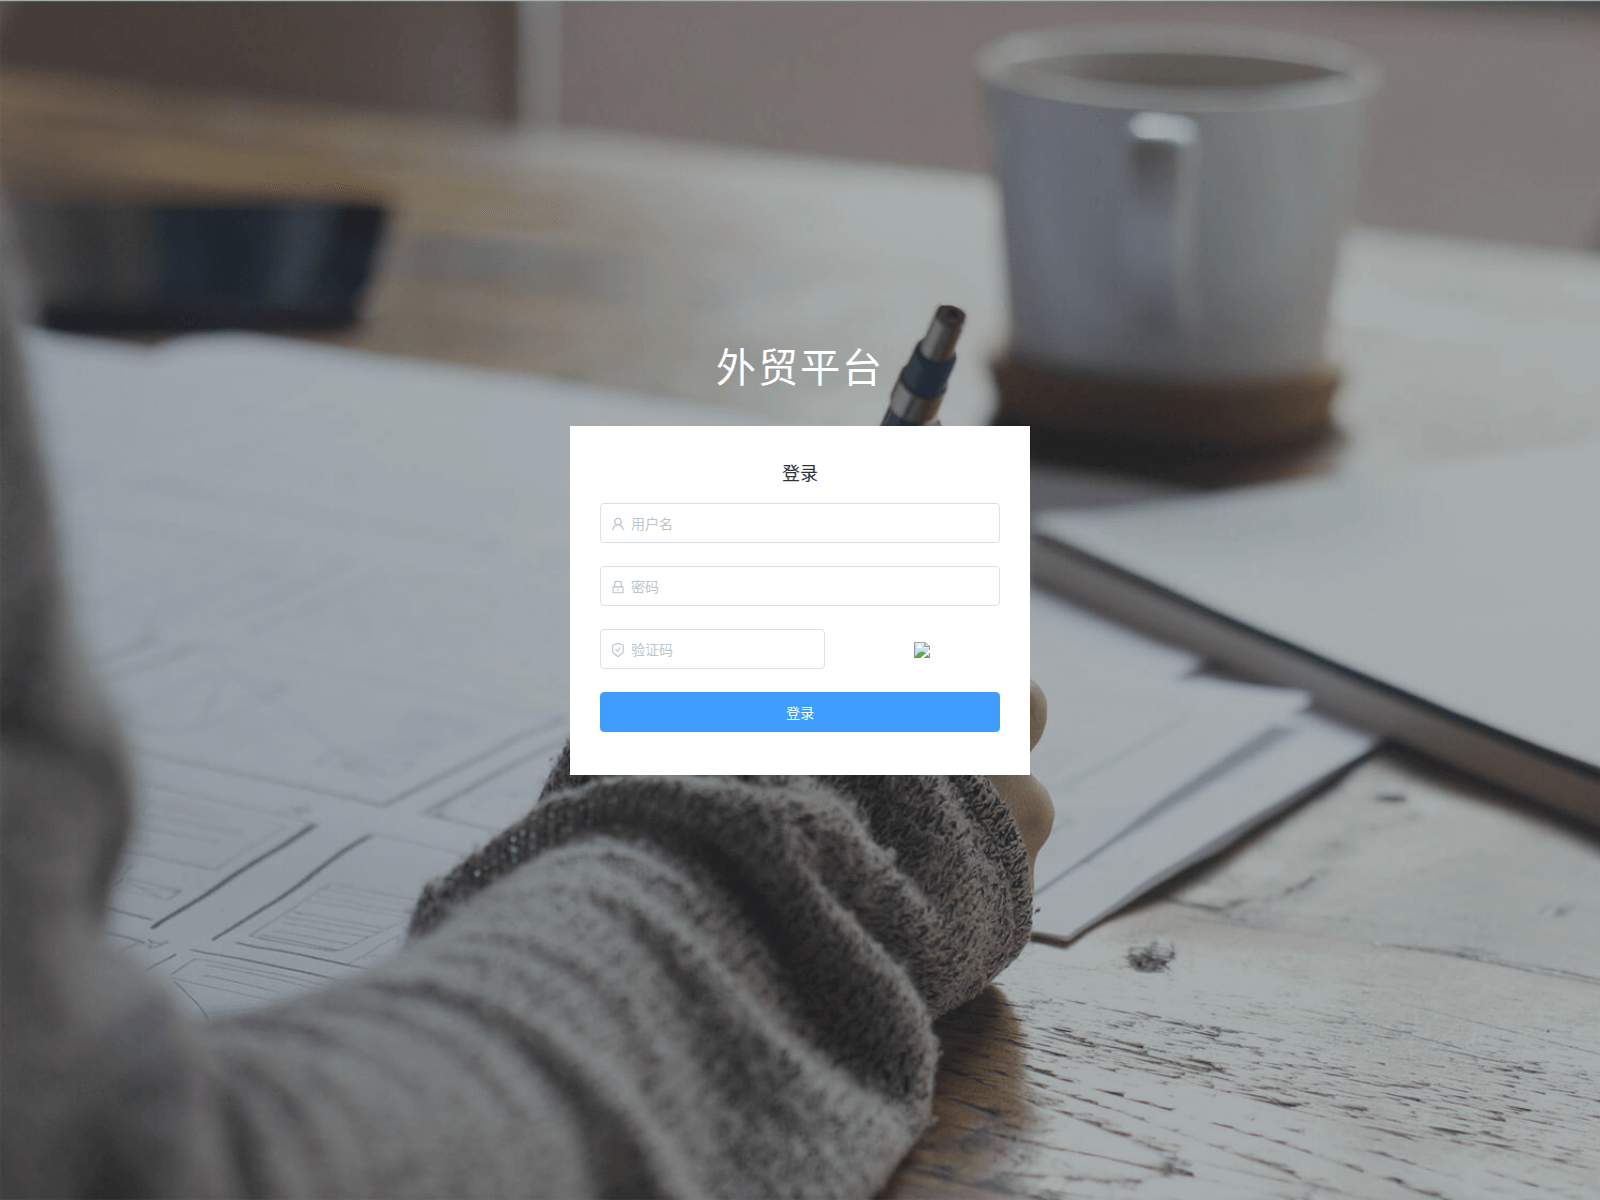
PhishDestroy’s automated assessment classifies ebaymevip.com as an impersonation phishing page. The domain was first observed by PhishDestroy on 2026-10-25, returning HTTP 200 after a 307 redirect from http to https. The recorded page title is simply “ebaymevip.com”.
사기 수법
Impersonation phishing sites mimic the look and language of legitimate brands to trick users into submitting login credentials, personal data, or payment information. Victims are typically lured via email, social media, or search results and directed to a fake login or verification page where the data is harvested for account takeover or fraud.
증거
Google Safe Browsing flagged the domain for SOCIAL_ENGINEERING on 2026-10-25. VirusTotal’s scan on the same date reported 17 detections from 92 engines, with 16 labeled malicious and 1 suspicious; vendors such as BitDefender, ESET, CRDF, DNS8, Forcepoint ThreatSeeker, G-Data and others marked it as phishing or malicious. urlscan.io captured the site on 2026-10-25; its machine‑learning engine gave a malicious score of 100 while the overall verdict was non‑malicious. Cloudflare Radar scanned the domain on 2026-10-25 and returned a malicious verdict categorised as phishing. PhishDestroy’s internal blocklist contains the domain and the external Phishunt list also lists it. OTX recorded three pulses referencing the domain as of 2026-10-25. Spamhaus DBL did not list the domain on that date.
인프라
The domain was registered on 2026-09-01 through Aceville Pte. Ltd., making it 54 days old at the time of observation. The recorded IP address is 43.135.161.205, associated with the network Shenzhen Tencent Computer Systems Company Limited and geolocated to the United States. The TLS certificate observed was issued to admin.bajj.cc by LiteSSL RSA CA 2025 and is valid until 2027-01-03. Nameservers were david.ns.cloudflare.com and sue.ns.cloudflare.com, indicating Cloudflare DNS. Open ports seen in the scan included 22, 80, 443 and 3306.
What to do
Anyone who may have entered credentials should change passwords on the legitimate service and enable multi‑factor authentication. Organizations should block the domain at DNS or proxy level, monitor outbound traffic to 43.135.161.205, and review logs for related connections. Security teams can use the VirusTotal and urlscan reports for deeper analysis and incident response.
서술 생성 날짜는 관측 날짜와 별개입니다. 이는 보존된 게시 필드일 뿐, 별도의 독립적인 탐지 결과가 아닙니다.
AI 제목
ebaymevip.com — Impersonation phishing page
AI 설명
PhishDestroy flagged ebaymevip.com on 2026-10-25 as an impersonation phishing page after Google Safe Browsing and VirusTotal flagged social‑engineering threats.
AI 요약
Overview PhishDestroy’s automated assessment classifies ebaymevip.com as an impersonation phishing page. The domain was first observed by PhishDestroy on 2026-10-25, returning HTTP 200 after a 307 redirect from http to https. The recorded page title is simply “ebaymevip.com”. How the scam works Impersonation phishing sites mimic the look and language of legitimate brands to trick users into submitting login credentials, personal data, or payment information. Victims are typically lured via email, social media, or search results and directed to a fake login or verification page where the data is harvested for account takeover or fraud. Evidence Google Safe Browsing flagged the domain for SOCIAL_ENGINEERING on 2026-10-25. VirusTotal’s scan on the same date reported 17 detections from 92 engines, with 16 labeled malicious and 1 suspicious; vendors such as BitDefender, ESET, CRDF, DNS8, Forcepoint ThreatSeeker, G-Data and others marked it as phishing or malicious. urlscan.io captured the site on 2026-10-25; its machine‑learning engine gave a malicious score of 100 while the overall verdict was non‑malicious. Cloudflare Radar scanned the domain on 2026-10-25 and returned a malicious verdict categorised as phishing. PhishDestroy’s internal blocklist contains the domain and the external Phishunt list also lists it. OTX recorded three pulses referencing the domain as of 2026-10-25. Spamhaus DBL did not list the domain on that date. Infrastructure The domain was registered on 2026-09-01 through Aceville Pte. Ltd., making it 54 days old at the time of observation. The recorded IP address is 43.135.161.205, associated with the network Shenzhen Tencent Computer Systems Company Limited and geolocated to the United States. The TLS certificate observed was issued to admin.bajj.cc by LiteSSL RSA CA 2025 and is valid until 2027-01-03. Nameservers were david.ns.cloudflare.com and sue.ns.cloudflare.com, indicating Cloudflare DNS. Open ports seen in the scan included 22, 80, 443 and 3306. What to do Anyone who may have entered credentials should change passwords on the legitimate service and enable multi‑factor authentication. Organizations should block the domain at DNS or proxy level, monitor outbound traffic to 43.135.161.205, and review logs for related connections. Security teams can use the VirusTotal and urlscan reports for deeper analysis and incident response. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1739e-a5f2-732a-958b-b32ff974a4bb/ Cloudflare Radar report: https://radar.cloudflare.com/scan/0b21bb4e-c2bc-496f-b3ec-770de23f01eb URLQuery report: https://urlquery.net/report/491b33ef-b348-4b0a-8774-199b9ac27666 Stored capture screenshot: https://urlscan.io/screenshots/01a1739e-a5f2-732a-958b-b32ff974a4bb.png Cloudflare Radar screenshot (2026-10-25T14:30:40Z): https://screenshots.phishdestroy.io/cf/0b21bb4e-c2bc-496f-b3ec-770de23f01eb.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/491b33ef-b348-4b0a-8774-199b9ac27666.png URLScan screenshot (2026-09-01T12:37:24Z): https://screenshots.phishdestroy.io/us/01a05cf9-41ae-733f-b8c6-862b4351fb0e.png URLScan capture report: https://urlscan.io/result/01a05cf9-41ae-733f-b8c6-862b4351fb0e/ URLScan screenshot (2026-09-04T12:57:50Z): https://screenshots.phishdestroy.io/us/01a06c7f-15d4-723d-85da-0cea0e0cbaa0.png URLScan capture report: https://urlscan.io/result/01a06c7f-15d4-723d-85da-0cea0e0cbaa0/ URLScan screenshot (2026-09-19T01:14:38Z): https://screenshots.phishdestroy.io/us/01a0b73a-b07b-7638-95d4-104021268770.png URLScan capture report: https://urlscan.io/result/01a0b73a-b07b-7638-95d4-104021268770/ URLScan screenshot (2026-09-20T05:34:52Z): https://screenshots.phishdestroy.io/us/01a0bd4f-4a28-7553-b719-a4a0231d1083.png URLScan capture report: https://urlscan.io/result/01a0bd4f-4a28-7553-b719-a4a0231d1083/ URLScan screenshot (2026-10-05T10:52:21Z): https://screenshots.phishdestroy.io/us/01a10bb1-5bc3-73dd-916f-ed5629094b3e.png URLScan capture report: https://urlscan.io/result/01a10bb1-5bc3-73dd-916f-ed5629094b3e/ URLScan screenshot (2026-10-25T14:57:35Z): https://screenshots.phishdestroy.io/us/01a17391-0069-71ad-b7e2-ab27a7ed46cd.png URLScan capture report: https://urlscan.io/result/01a17391-0069-71ad-b7e2-ab27a7ed46cd/ VirusTotal report: https://www.virustotal.com/gui/domain/ebaymevip.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=ebaymevip.com Archived copy: https://web.archive.org/web/20261025142621/https://ebaymevip.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
This website does not have many visitors We found many low rated websites on the same server We did not find a SSL certificate This website has only been registered recently. We could not analyze the content of the site IPQS has flagged this website as Malicious IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
DNSFilter considers this website safe
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
피싱 Security threats 피싱
ebaymevip.com 관련 질문
ebaymevip.com은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 ebaymevip.com를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-10-25에 처음 기록되었습니다. 저장된 VirusTotal 결과: 17/92 엔진에서 경고했습니다. 악성: 16. 의심: 1. 분석 시간(저장된 표기): 2026-10-25 15:22 UTC. 조회 시간(저장된 표기): 2026-10-25 20:20 UTC. Google 세이프 브라우징이 위험으로 표시. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
ebaymevip.com에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
ebaymevip.com을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
IP 평판43.135.161.2050/100악용 점수 · 이 서버의 IP 주소에 대한 악용 신고 건수이며, 도메인에 대한 신고 건수가 아닙니다. 점수가 높을수록 상황이 더 심각합니다.이 IP 주소는 아직 악용 데이터베이스에 신고되지 않았으나, 도메인 자체는 피싱으로 인식되고 있습니다.신고 0건확인됨 2026-10-25
기록된 이벤트: 15. 이 기록들은 수집된 증거, 발송된 알림 및 차단 목록 등재를 설명하며, 조사가 완료되었거나 해당 사이트가 차단되었음을 확인하는 것은 아닙니다.
선제적 탐지 및 데이터 수집위협 데이터 수집 완료기록됨
위협 데이터 수집 완료
ebaymevip.com이 탐지되어 전체 분석을 위해 대기열에 추가됨
위협 인텔리전스 확인URLScan.io 캡처 · URLScan 판정 결과 · Cloudflare Radar 보고서 · 웹 아카이브 · VirusTotal · Google Safe Browsing · OTX 커뮤니티 참조 자료 · Cloudflare Radar: 악성 · 자동 브랜드 라벨: EBay · 수집된 포렌식 증거 · 기록된 기술 분석 · VirusTotal 탐지 건수 +1기록됨
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.

 43.135.161.205


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT