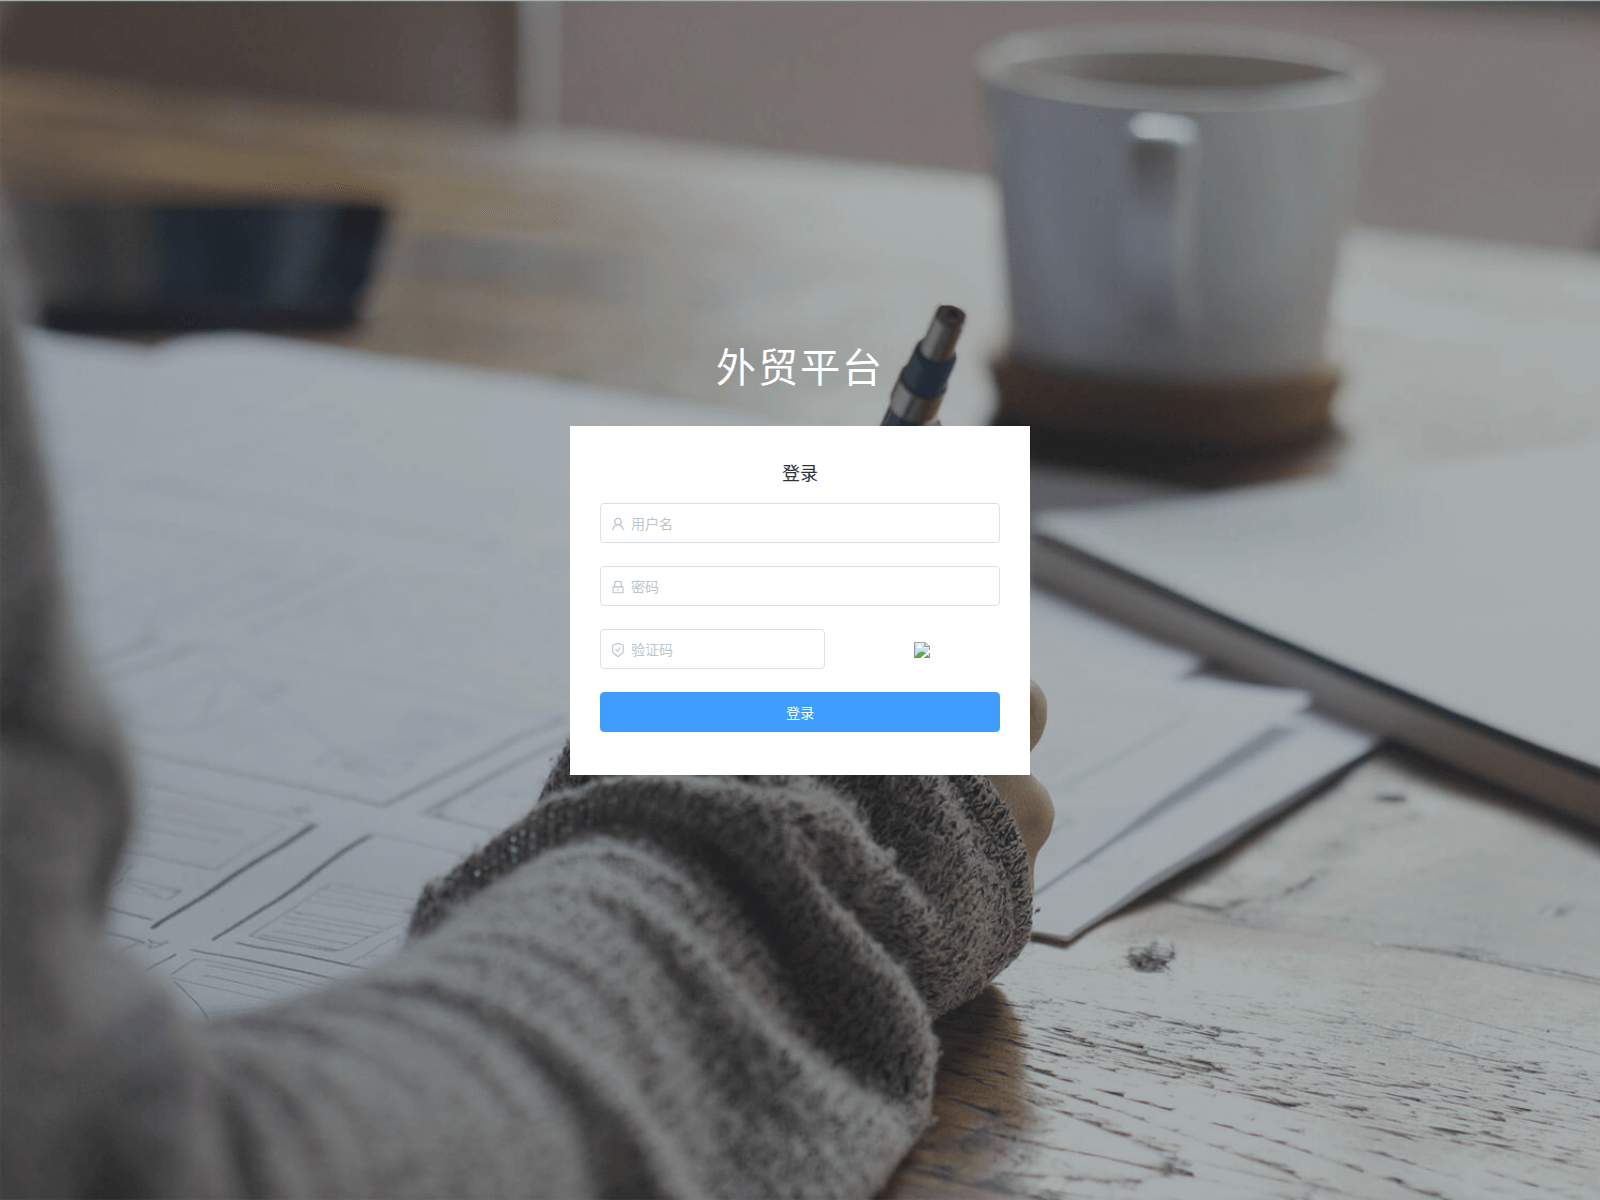
PhishDestroy’s automated assessment classifies ebaymevip.com as an impersonation phishing page. The domain was first observed by PhishDestroy on 2026-10-25, returning HTTP 200 after a 307 redirect from http to https. The recorded page title is simply “ebaymevip.com”.
诈骗手法解析
Impersonation phishing sites mimic the look and language of legitimate brands to trick users into submitting login credentials, personal data, or payment information. Victims are typically lured via email, social media, or search results and directed to a fake login or verification page where the data is harvested for account takeover or fraud.
证据
Google Safe Browsing flagged the domain for SOCIAL_ENGINEERING on 2026-10-25. VirusTotal’s scan on the same date reported 17 detections from 92 engines, with 16 labeled malicious and 1 suspicious; vendors such as BitDefender, ESET, CRDF, DNS8, Forcepoint ThreatSeeker, G-Data and others marked it as phishing or malicious. urlscan.io captured the site on 2026-10-25; its machine‑learning engine gave a malicious score of 100 while the overall verdict was non‑malicious. Cloudflare Radar scanned the domain on 2026-10-25 and returned a malicious verdict categorised as phishing. PhishDestroy’s internal blocklist contains the domain and the external Phishunt list also lists it. OTX recorded three pulses referencing the domain as of 2026-10-25. Spamhaus DBL did not list the domain on that date.
基础设施
The domain was registered on 2026-09-01 through Aceville Pte. Ltd., making it 54 days old at the time of observation. The recorded IP address is 43.135.161.205, associated with the network Shenzhen Tencent Computer Systems Company Limited and geolocated to the United States. The TLS certificate observed was issued to admin.bajj.cc by LiteSSL RSA CA 2025 and is valid until 2027-01-03. Nameservers were david.ns.cloudflare.com and sue.ns.cloudflare.com, indicating Cloudflare DNS. Open ports seen in the scan included 22, 80, 443 and 3306.
What to do
Anyone who may have entered credentials should change passwords on the legitimate service and enable multi‑factor authentication. Organizations should block the domain at DNS or proxy level, monitor outbound traffic to 43.135.161.205, and review logs for related connections. Security teams can use the VirusTotal and urlscan reports for deeper analysis and incident response.
PhishDestroy flagged ebaymevip.com on 2026-10-25 as an impersonation phishing page after Google Safe Browsing and VirusTotal flagged social‑engineering threats.
AI摘要
Overview PhishDestroy’s automated assessment classifies ebaymevip.com as an impersonation phishing page. The domain was first observed by PhishDestroy on 2026-10-25, returning HTTP 200 after a 307 redirect from http to https. The recorded page title is simply “ebaymevip.com”. How the scam works Impersonation phishing sites mimic the look and language of legitimate brands to trick users into submitting login credentials, personal data, or payment information. Victims are typically lured via email, social media, or search results and directed to a fake login or verification page where the data is harvested for account takeover or fraud. Evidence Google Safe Browsing flagged the domain for SOCIAL_ENGINEERING on 2026-10-25. VirusTotal’s scan on the same date reported 17 detections from 92 engines, with 16 labeled malicious and 1 suspicious; vendors such as BitDefender, ESET, CRDF, DNS8, Forcepoint ThreatSeeker, G-Data and others marked it as phishing or malicious. urlscan.io captured the site on 2026-10-25; its machine‑learning engine gave a malicious score of 100 while the overall verdict was non‑malicious. Cloudflare Radar scanned the domain on 2026-10-25 and returned a malicious verdict categorised as phishing. PhishDestroy’s internal blocklist contains the domain and the external Phishunt list also lists it. OTX recorded three pulses referencing the domain as of 2026-10-25. Spamhaus DBL did not list the domain on that date. Infrastructure The domain was registered on 2026-09-01 through Aceville Pte. Ltd., making it 54 days old at the time of observation. The recorded IP address is 43.135.161.205, associated with the network Shenzhen Tencent Computer Systems Company Limited and geolocated to the United States. The TLS certificate observed was issued to admin.bajj.cc by LiteSSL RSA CA 2025 and is valid until 2027-01-03. Nameservers were david.ns.cloudflare.com and sue.ns.cloudflare.com, indicating Cloudflare DNS. Open ports seen in the scan included 22, 80, 443 and 3306. What to do Anyone who may have entered credentials should change passwords on the legitimate service and enable multi‑factor authentication. Organizations should block the domain at DNS or proxy level, monitor outbound traffic to 43.135.161.205, and review logs for related connections. Security teams can use the VirusTotal and urlscan reports for deeper analysis and incident response. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1739e-a5f2-732a-958b-b32ff974a4bb/ Cloudflare Radar report: https://radar.cloudflare.com/scan/0b21bb4e-c2bc-496f-b3ec-770de23f01eb URLQuery report: https://urlquery.net/report/491b33ef-b348-4b0a-8774-199b9ac27666 Stored capture screenshot: https://urlscan.io/screenshots/01a1739e-a5f2-732a-958b-b32ff974a4bb.png Cloudflare Radar screenshot (2026-10-25T14:30:40Z): https://screenshots.phishdestroy.io/cf/0b21bb4e-c2bc-496f-b3ec-770de23f01eb.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/491b33ef-b348-4b0a-8774-199b9ac27666.png URLScan screenshot (2026-09-01T12:37:24Z): https://screenshots.phishdestroy.io/us/01a05cf9-41ae-733f-b8c6-862b4351fb0e.png URLScan capture report: https://urlscan.io/result/01a05cf9-41ae-733f-b8c6-862b4351fb0e/ URLScan screenshot (2026-09-04T12:57:50Z): https://screenshots.phishdestroy.io/us/01a06c7f-15d4-723d-85da-0cea0e0cbaa0.png URLScan capture report: https://urlscan.io/result/01a06c7f-15d4-723d-85da-0cea0e0cbaa0/ URLScan screenshot (2026-09-19T01:14:38Z): https://screenshots.phishdestroy.io/us/01a0b73a-b07b-7638-95d4-104021268770.png URLScan capture report: https://urlscan.io/result/01a0b73a-b07b-7638-95d4-104021268770/ URLScan screenshot (2026-09-20T05:34:52Z): https://screenshots.phishdestroy.io/us/01a0bd4f-4a28-7553-b719-a4a0231d1083.png URLScan capture report: https://urlscan.io/result/01a0bd4f-4a28-7553-b719-a4a0231d1083/ URLScan screenshot (2026-10-05T10:52:21Z): https://screenshots.phishdestroy.io/us/01a10bb1-5bc3-73dd-916f-ed5629094b3e.png URLScan capture report: https://urlscan.io/result/01a10bb1-5bc3-73dd-916f-ed5629094b3e/ URLScan screenshot (2026-10-25T14:57:35Z): https://screenshots.phishdestroy.io/us/01a17391-0069-71ad-b7e2-ab27a7ed46cd.png URLScan capture report: https://urlscan.io/result/01a17391-0069-71ad-b7e2-ab27a7ed46cd/ VirusTotal report: https://www.virustotal.com/gui/domain/ebaymevip.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=ebaymevip.com Archived copy: https://web.archive.org/web/20261025142621/https://ebaymevip.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
This website does not have many visitors We found many low rated websites on the same server We did not find a SSL certificate This website has only been registered recently. We could not analyze the content of the site IPQS has flagged this website as Malicious IPQS flagged this website for Phishing IPQS has flagged this website as suspicious

 43.135.161.205


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT