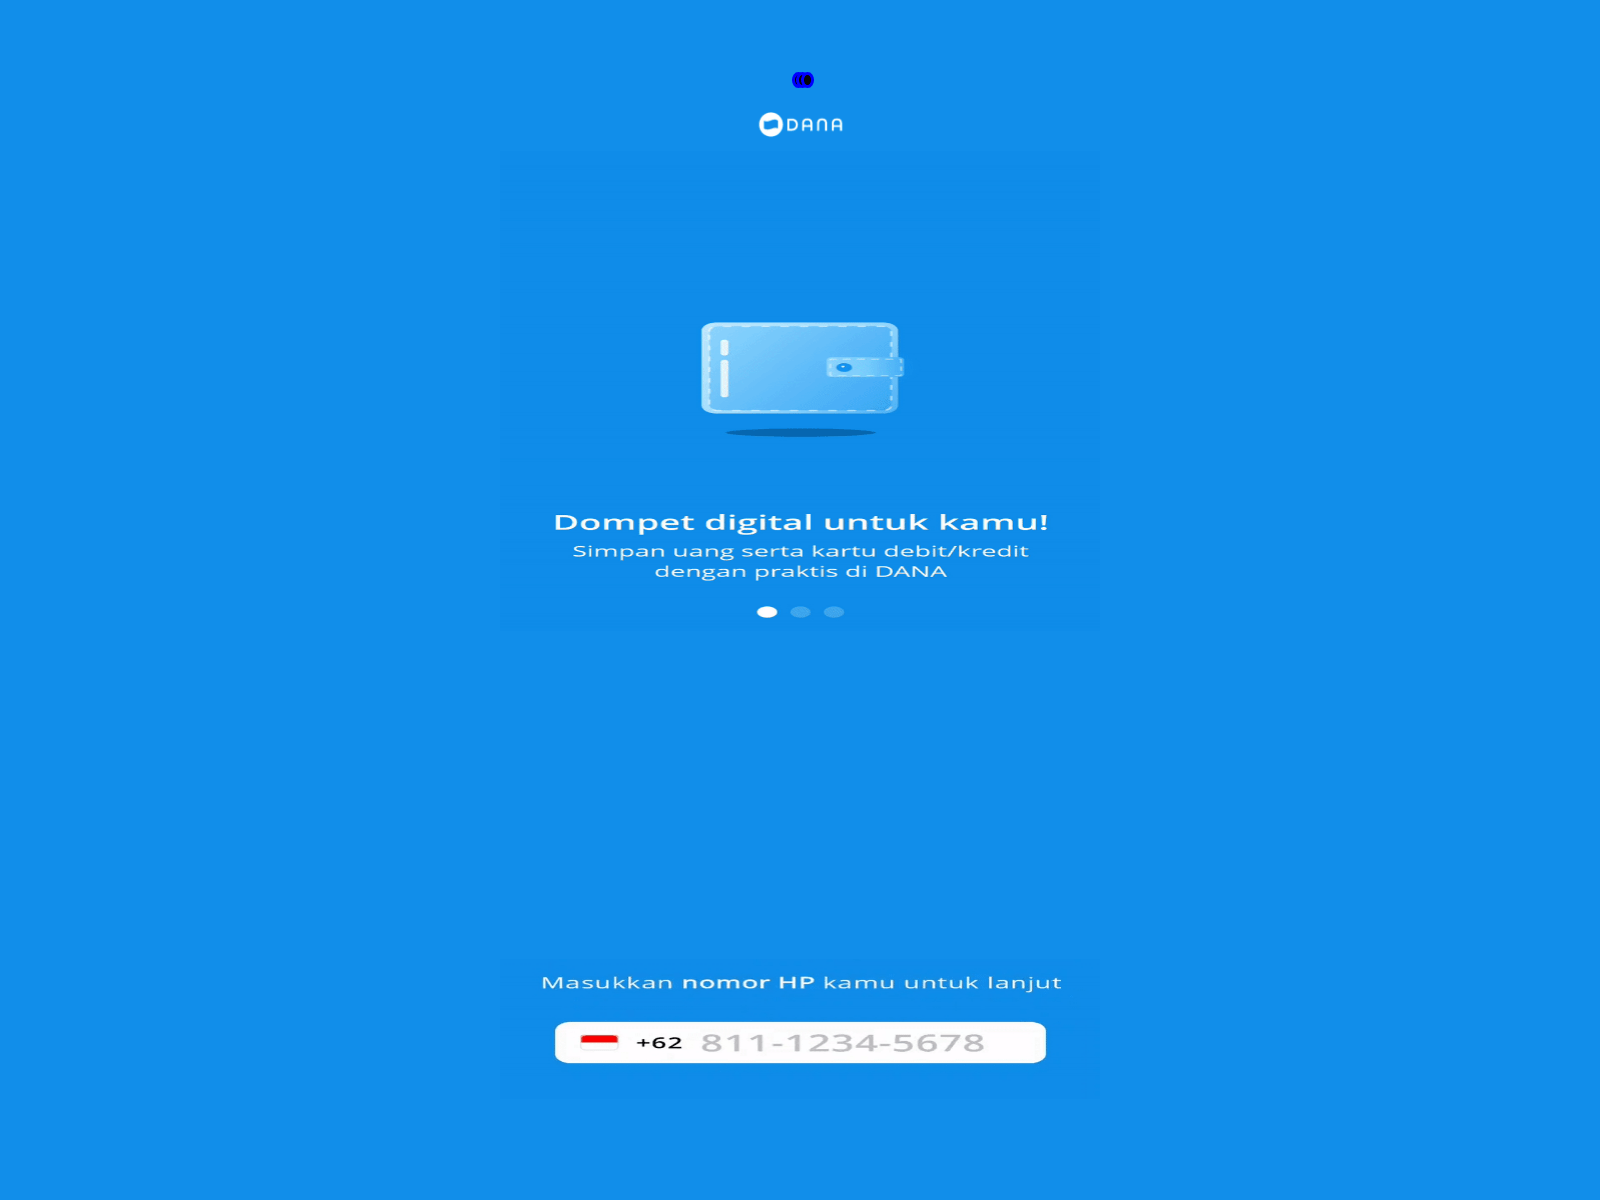
PhishDestroy는 2026-09-12에 danakagetrsm.vercel.app를 처음 기록했습니다. 저장된 VirusTotal 결과: 19/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-10-06 16:20 UTC. 조회 시간(저장된 표기): 2026-10-22 04:47 UTC. Google 세이프 브라우징이 위험으로 표시.
페이지 제목: “DANA E-wallet”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 19/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-10-06 16:20 UTC. 조회 시간(저장된 표기): 2026-10-22 04:47 UTC. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
위험 신호
VirusTotal 탐지: 19/92마지막으로 확인된 활성 상태Google Safe Browsing: 위협 표시 기록됨
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Overview
danakagetrsm.vercel.app is an impersonation phishing page that presents itself as "DANA E-wallet". It targets users of DANA, the Indonesian digital wallet, and its name echoes "DANA Kaget", the app's popular money-gift feature. PhishDestroy first detected it on 2026-09-12. It was still online and serving its phishing content when last checked on 2026-10-19.
사기 수법
Pages like this usually spread through chat groups and social media as a link to claim a surprise DANA balance or bonus. The victim is shown a copy of the DANA interface and asked to log in with their phone number, then enter their PIN and the one-time code DANA sends by SMS. Whatever is typed goes straight to the operators, who use it to take over the real DANA account and drain its balance or any linked payment methods. The victim never receives a bonus. They lose access to the account and the money in it.
증거
The classification is backed by several independent sources. On 2026-09-19, 18 of 89 VirusTotal engines flagged the site, including BitDefender, ESET, Fortinet, Emsisoft, G-Data, Forcepoint ThreatSeeker, Criminal IP and alphaMountain.ai. Google Safe Browsing lists it as social engineering, so Chrome and other browsers that use that service warn visitors. urlscan.io rated the page malicious and identified the DANA brand on it. The domain also appears on the PhishDestroy and PhishFeed blocklists.
인프라
The page sits on a free Vercel subdomain rather than a purchased domain, which lets the operators launch quickly and replace it cheaply once it is blocked. It resolves to Amazon-operated hosting in the United States. Its TLS certificate comes from Google Trust Services, issued automatically to Vercel deployments. The padlock in the browser only means the connection is encrypted and says nothing about whether the site is genuine.
What to do
If you entered your phone number, PIN or an OTP on this page, open the official DANA app right away, change your PIN and check your transaction history for transfers you did not make. Contact DANA customer support through the app to report the compromise and ask them to freeze the account if anything looks wrong. Never share an OTP with anyone, because DANA will not ask for it on a website. Warn the group or contact who sent you the link. Defenders should block the domain at DNS and proxy level and report it to Vercel for takedown.
서술 생성 날짜는 관측 날짜와 별개입니다. 이는 보존된 게시 필드일 뿐, 별도의 독립적인 탐지 결과가 아닙니다.
AI 제목
danakagetrsm.vercel.app — DANA E-wallet Phishing Page
AI 설명
danakagetrsm.vercel.app is a phishing page impersonating the DANA e-wallet, built to steal phone numbers, PINs and OTP codes from DANA users.
AI 요약
Overview danakagetrsm.vercel.app is an impersonation phishing page that presents itself as "DANA E-wallet". It targets users of DANA, the Indonesian digital wallet, and its name echoes "DANA Kaget", the app's popular money-gift feature. PhishDestroy first detected it on 2026-09-12. It was still online and serving its phishing content when last checked on 2026-10-19. How the scam works Pages like this usually spread through chat groups and social media as a link to claim a surprise DANA balance or bonus. The victim is shown a copy of the DANA interface and asked to log in with their phone number, then enter their PIN and the one-time code DANA sends by SMS. Whatever is typed goes straight to the operators, who use it to take over the real DANA account and drain its balance or any linked payment methods. The victim never receives a bonus. They lose access to the account and the money in it. Evidence The classification is backed by several independent sources. On 2026-09-19, 18 of 89 VirusTotal engines flagged the site, including BitDefender, ESET, Fortinet, Emsisoft, G-Data, Forcepoint ThreatSeeker, Criminal IP and alphaMountain.ai. Google Safe Browsing lists it as social engineering, so Chrome and other browsers that use that service warn visitors. urlscan.io rated the page malicious and identified the DANA brand on it. The domain also appears on the PhishDestroy and PhishFeed blocklists. Infrastructure The page sits on a free Vercel subdomain rather than a purchased domain, which lets the operators launch quickly and replace it cheaply once it is blocked. It resolves to Amazon-operated hosting in the United States. Its TLS certificate comes from Google Trust Services, issued automatically to Vercel deployments. The padlock in the browser only means the connection is encrypted and says nothing about whether the site is genuine. What to do If you entered your phone number, PIN or an OTP on this page, open the official DANA app right away, change your PIN and check your transaction history for transfers you did not make. Contact DANA customer support through the app to report the compromise and ask them to freeze the account if anything looks wrong. Never share an OTP with anyone, because DANA will not ask for it on a website. Warn the group or contact who sent you the link. Defenders should block the domain at DNS and proxy level and report it to Vercel for takedown. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a0ac8d-c09a-71db-8f76-9764b2fd7fdf/ VirusTotal report: https://www.virustotal.com/gui/domain/danakagetrsm.vercel.app Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=danakagetrsm.vercel.app Archived copy: https://web.archive.org/web/20260912155736/https://danakagetrsm.vercel.app/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Mau bayar apapun jadi semudah lewat sentuhan jari. Lewat DANA, kamu bisa melakukan transaksi apapun dengan praktis mulai dari pembayaran tagihan, transaksi barcode scan, hingga e-commerce. #GantiDompet dan nikmati metode pembayaran yang lebih cepat, praktis dan aman.
Last: 2026-09-22T01:50:29Z; First: 2026-03-06T02:43:45Z; Changes: 1; Days archived: 4; Scans per day: 0.02; Avg page bytes: 3487
페이지 제목 및 메타데이터
Ogurl: https://www.dana.id/; Title: DANA E-wallet; Ogimage: https://assets.kompasiana.com/items/album/2022/01/19/dana-heri-61e79b5c06310e2d0778d653.jpg; Ogtitle: DANA E-wallet; Generator: Dana E-wallet; Themecolor: #118EEA; Description: Mau bayar apapun jadi semudah lewat sentuhan jari. Lewat DANA, kamu bisa melakukan transaksi apapun dengan praktis mulai dari pembayaran tagihan, transaksi barcode scan, hingga e-commerce. #GantiDompet dan nikmati metode pembayaran yang lebih cepat, praktis dan aman.; Canonicalurl: https://www.dana.id/
No sri: https://cdn.rawgit.com/igorescobar/jQuery-Mask-Plugin/1ef022ab/dist/jquery.mask.min.js, https://cdnjs.cloudflare.com/ajax/libs/jquery.mask/1.14.15/jquery.mask.min.js, https://cdnjs.cloudflare.com/ajax/libs/jquery.inputmask/3.3.4/jquery.inputmask.bundle.min.js, https://ajax.googleapis.com/ajax/libs/jquery/1.11.1/jquery.min.js, https://ajax.googleapis.com/ajax/libs/jquery/1.10.2/jquery.min.js, https://ajax.googleapis.com/ajax/libs/jquery/2.0.3/jquery.min.js, https://cdnjs.cloudflare.com/ajax/libs/jquery/3.1.1/jquery.min.js, https://ajax.googleapis.com/ajax/libs/jquery/3.3.1/jquery.min.js; Third party scripts: 9
The owner of the website is using a service to hide their identity on WHOIS According to Tranco this site has a low rank This site is a website within another website This website uses a generic platform to host its website This website has been reported as unsafe by Maltiverse This website has been reported for Phishing by IPQS This website has been reported as Suspicious by IPQS
The SSL certificate is valid This website is (very) old This website is safe according to DNSFilter
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
피싱
danakagetrsm.vercel.app 관련 질문
danakagetrsm.vercel.app은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 danakagetrsm.vercel.app를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-09-12에 처음 기록되었습니다. 저장된 VirusTotal 결과: 19/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-10-06 16:20 UTC. 조회 시간(저장된 표기): 2026-10-22 04:47 UTC. Google 세이프 브라우징이 위험으로 표시. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
danakagetrsm.vercel.app에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
danakagetrsm.vercel.app을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
소셜 미리보기 카드danakagetrsm.vercel.app: Dana impersonation — Flagged by Google Safe Browsing, 18/89 VirusTotal engines. PhishDestroy risk score 100/100 (critical).v 6aa3dd24eee9
기록된 이벤트: 14. 이 기록들은 수집된 증거, 발송된 알림 및 차단 목록 등재를 설명하며, 조사가 완료되었거나 해당 사이트가 차단되었음을 확인하는 것은 아닙니다.
선제적 탐지 및 데이터 수집위협 데이터 수집 완료기록됨
위협 데이터 수집 완료
danakagetrsm.vercel.app이 탐지되어 전체 분석을 위해 대기열에 추가됨
위협 인텔리전스 확인URLScan.io 캡처 · URLScan 판정 결과 · Cloudflare Radar 보고서 · 웹 아카이브 · VirusTotal · Google Safe Browsing · Cloudflare Radar: 악성 · 자동 브랜드 라벨: Dana · 수집된 포렌식 증거 · 기록된 기술 분석 · 콘텐츠가 더 이상 이용 불가능한 것으로 확인됨기록됨
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.


 64.29.17.67


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 MyWOT