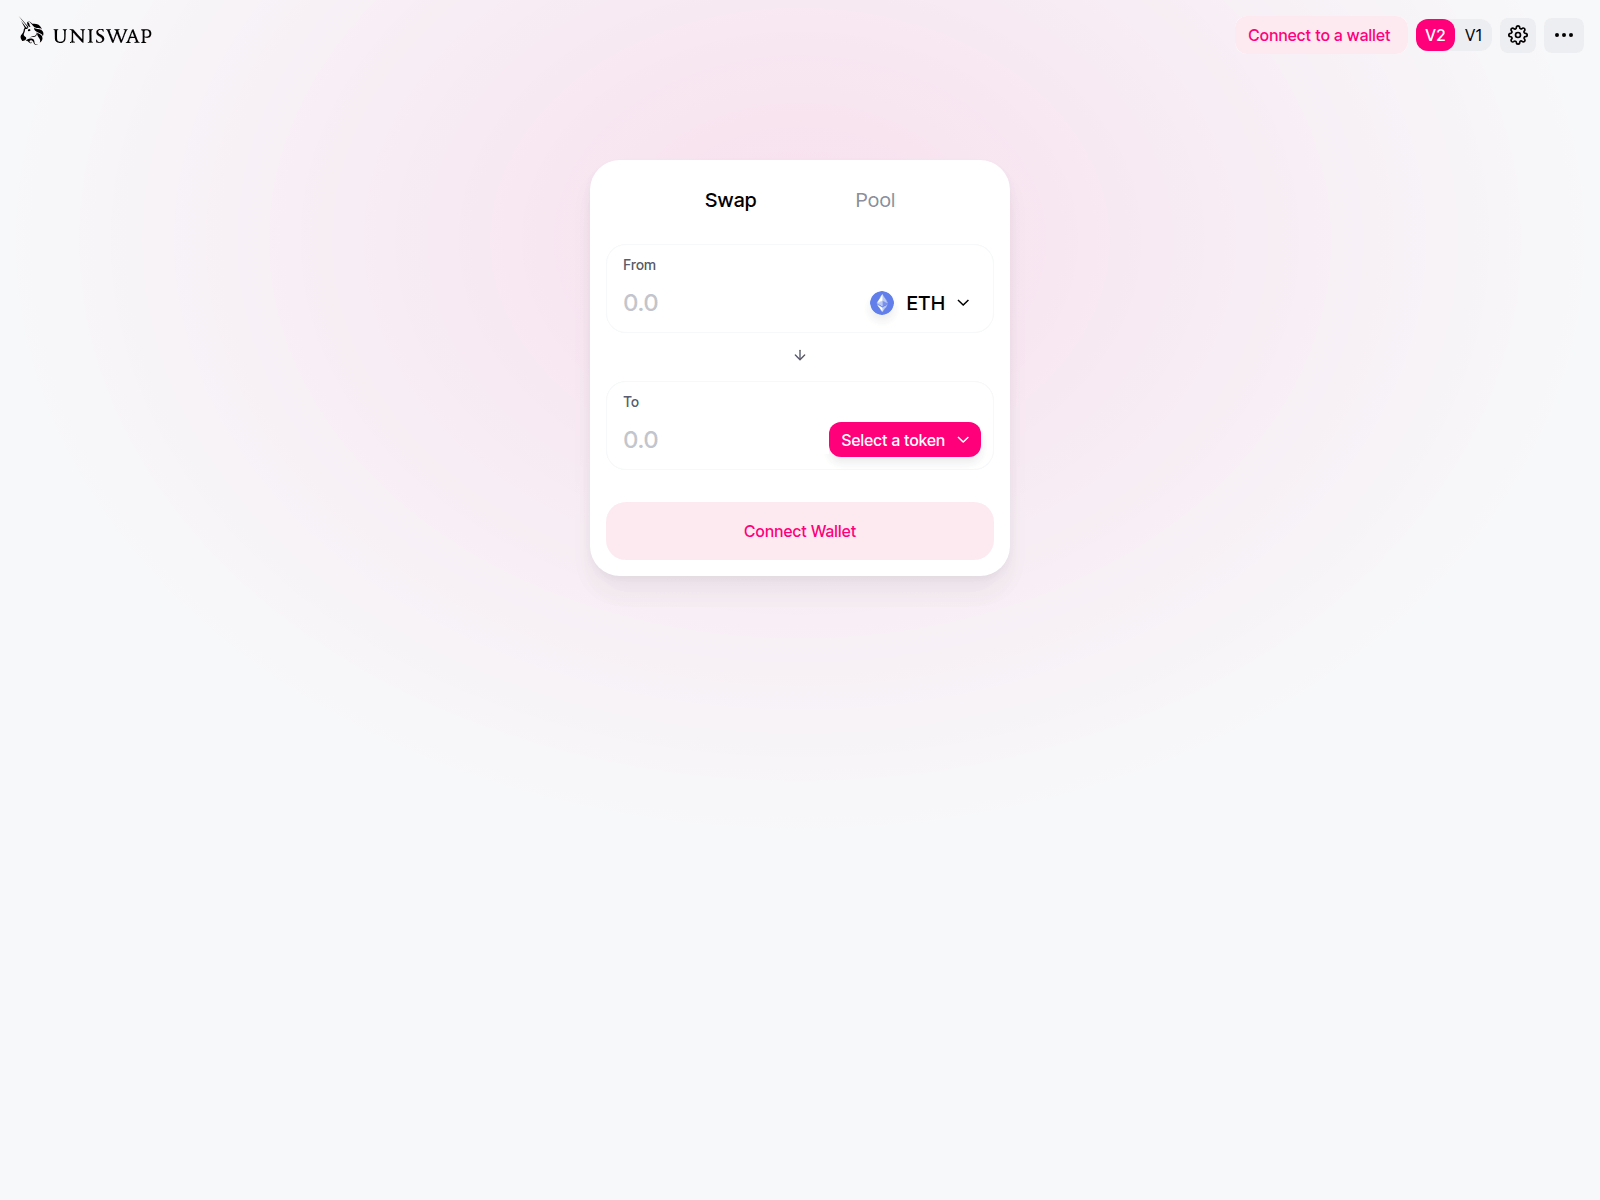
This page reproduces the Uniswap exchange interface and prompts visitors to connect a cryptocurrency wallet to trade tokens. Anyone who connected a wallet should immediately check token allowances and revoke any unauthorized permissions granted to unknown contracts.
분석 내용은 영어로만 제공됩니다.
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 16/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-11-22 04:55 UTC. 조회 시간(저장된 표기): 2026-11-22 15:29 UTC. 외부 차단 목록에 등재됨: OpenPhish. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
위험 신호
VirusTotal 탐지: 16/92저장된 차단 목록 일치 항목: 1Google Safe Browsing: 위협 표시 기록됨
URLScan 캡처 · 2026-11-22 15:26 UTC · SHA-256 c803c25f…8d0ce19
PhishDestroy 분석, 검토 완료된 버전
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Uniswap interface clone layout
The page hosted on 33357.github.io reproduces the layout of the Uniswap v2 application, featuring the brand name "Uniswap" in the top-left corner alongside a unicorn logo. In the upper right, buttons display "Connect to a wallet", "V2", and "V1", accompanied by settings icons. The central widget contains a token swap form titled "Swap" and "Pool", showing input fields labeled "From" with a default "ETH" token selector and "To" with a "Select a token" button. Below these fields sits a prominent pink button reading "Connect Wallet". The entire design mimics the authentic trading terminal to encourage visitors into connecting their cryptocurrency wallets without realizing they are interacting with a third-party clone on the platform.
Security telemetry and threat indicators
The address still responded on 22 Nov 2026 at 16:26 UTC, maintaining its deceptive structure on the platform github.io. urlscan classified the page as malicious, 16 of 92 engines on VirusTotal flagged it on 22 Nov 2026, and Google Safe Browsing flags it, where vendors such as Kaspersky, ESET and BitDefender classify the URL as malicious. PhishDestroy scores the evidence against it at 85/100 (critical). Because the real protocol operates exclusively on uniswap.org, hosting this interface on GitHub Pages is a tactic designed to deceive traders looking for the legitimate exchange.
Wallet connection risks
Fake decentralized exchange apps often prompt users to sign transactions that transfer ownership of assets rather than executing a standard trade. Anyone who has already connected their wallet and approved permissions on this page must use a blockchain explorer or security tool to revoke those allowances immediately.
출처 증거VirusTotal 16 / 92 · Google Safe Browsing: 표시됨5 개 출처
33357.github.io presents a Uniswap swap interface to capture wallet connections, flagged by urlscan and 16 VirusTotal engines. Use uniswap.org instead.
AI 요약
Uniswap interface clone layout The page hosted on 33357.github.io reproduces the layout of the Uniswap v2 application, featuring the brand name "Uniswap" in the top-left corner alongside a unicorn logo. In the upper right, buttons display "Connect to a wallet", "V2", and "V1", accompanied by settings icons. The central widget contains a token swap form titled "Swap" and "Pool", showing input fields labeled "From" with a default "ETH" token selector and "To" with a "Select a token" button. Below these fields sits a prominent pink button reading "Connect Wallet". The entire design mimics the authentic trading terminal to encourage visitors into connecting their cryptocurrency wallets without realizing they are interacting with a third-party clone on the platform. Security telemetry and threat indicators The address still responded on 22 Nov 2026 at 16:26 UTC, maintaining its deceptive structure on the platform github.io. urlscan classified the page as malicious, 16 of 92 engines on VirusTotal flagged it on 22 Nov 2026, and Google Safe Browsing flags it, where vendors such as Kaspersky, ESET and BitDefender classify the URL as malicious. PhishDestroy scores the evidence against it at 85/100 (critical). Because the real protocol operates exclusively on uniswap.org, hosting this interface on GitHub Pages is a tactic designed to deceive traders looking for the legitimate exchange. Wallet connection risks Fake decentralized exchange apps often prompt users to sign transactions that transfer ownership of assets rather than executing a standard trade. Anyone who has already connected their wallet and approved permissions on this page must use a blockchain explorer or security tool to revoke those allowances immediately.
Headers: Server: GitHub.com; Content type: text/html; charset=utf-8; Content security policy: default-src 'none'; style-src 'unsafe-inline'; img-src data:; connect-src 'self'; Via: 1.1 varnish; X cache: HIT; X cache hits: 2; X served by: cache-fra-etou8220069-FRA
33357.github.io 관련 질문
33357.github.io은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 33357.github.io를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-11-22에 처음 기록되었습니다. 저장된 VirusTotal 결과: 16/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-11-22 04:55 UTC. 조회 시간(저장된 표기): 2026-11-22 15:29 UTC. Google 세이프 브라우징이 위험으로 표시. 외부 차단 목록에 등재됨: OpenPhish. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
33357.github.io에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
33357.github.io을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.



 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT