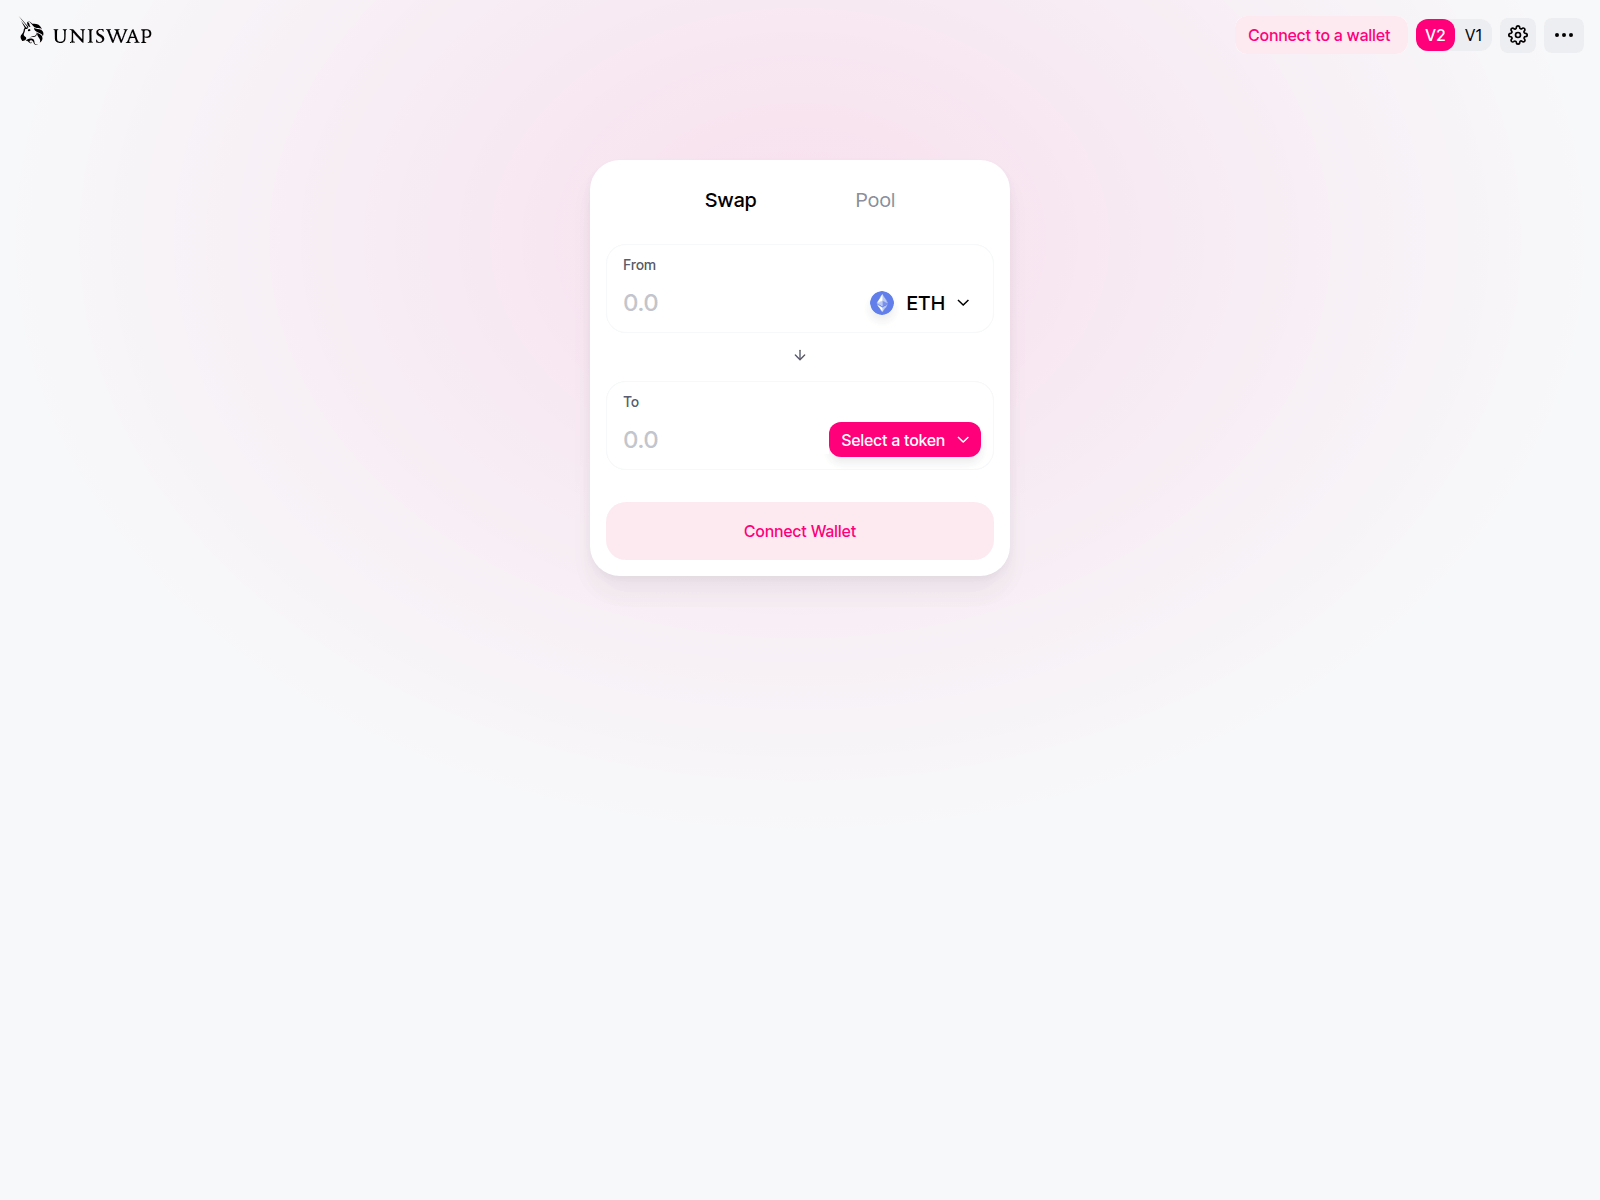
This page reproduces the Uniswap exchange interface and prompts visitors to connect a cryptocurrency wallet to trade tokens. Anyone who connected a wallet should immediately check token allowances and revoke any unauthorized permissions granted to unknown contracts.
URLScan截图 · 2026-11-22 15:26 UTC · SHA-256 c803c25f…8d0ce19
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Uniswap interface clone layout
The page hosted on 33357.github.io reproduces the layout of the Uniswap v2 application, featuring the brand name "Uniswap" in the top-left corner alongside a unicorn logo. In the upper right, buttons display "Connect to a wallet", "V2", and "V1", accompanied by settings icons. The central widget contains a token swap form titled "Swap" and "Pool", showing input fields labeled "From" with a default "ETH" token selector and "To" with a "Select a token" button. Below these fields sits a prominent pink button reading "Connect Wallet". The entire design mimics the authentic trading terminal to encourage visitors into connecting their cryptocurrency wallets without realizing they are interacting with a third-party clone on the platform.
Security telemetry and threat indicators
The address still responded on 22 Nov 2026 at 16:26 UTC, maintaining its deceptive structure on the platform github.io. urlscan classified the page as malicious, 16 of 92 engines on VirusTotal flagged it on 22 Nov 2026, and Google Safe Browsing flags it, where vendors such as Kaspersky, ESET and BitDefender classify the URL as malicious. PhishDestroy scores the evidence against it at 85/100 (critical). Because the real protocol operates exclusively on uniswap.org, hosting this interface on GitHub Pages is a tactic designed to deceive traders looking for the legitimate exchange.
Wallet connection risks
Fake decentralized exchange apps often prompt users to sign transactions that transfer ownership of assets rather than executing a standard trade. Anyone who has already connected their wallet and approved permissions on this page must use a blockchain explorer or security tool to revoke those allowances immediately.
来源证据VirusTotal 16 / 92 · Google Safe Browsing: 被标记5 个来源
33357.github.io presents a Uniswap swap interface to capture wallet connections, flagged by urlscan and 16 VirusTotal engines. Use uniswap.org instead.
AI摘要
Uniswap interface clone layout The page hosted on 33357.github.io reproduces the layout of the Uniswap v2 application, featuring the brand name "Uniswap" in the top-left corner alongside a unicorn logo. In the upper right, buttons display "Connect to a wallet", "V2", and "V1", accompanied by settings icons. The central widget contains a token swap form titled "Swap" and "Pool", showing input fields labeled "From" with a default "ETH" token selector and "To" with a "Select a token" button. Below these fields sits a prominent pink button reading "Connect Wallet". The entire design mimics the authentic trading terminal to encourage visitors into connecting their cryptocurrency wallets without realizing they are interacting with a third-party clone on the platform. Security telemetry and threat indicators The address still responded on 22 Nov 2026 at 16:26 UTC, maintaining its deceptive structure on the platform github.io. urlscan classified the page as malicious, 16 of 92 engines on VirusTotal flagged it on 22 Nov 2026, and Google Safe Browsing flags it, where vendors such as Kaspersky, ESET and BitDefender classify the URL as malicious. PhishDestroy scores the evidence against it at 85/100 (critical). Because the real protocol operates exclusively on uniswap.org, hosting this interface on GitHub Pages is a tactic designed to deceive traders looking for the legitimate exchange. Wallet connection risks Fake decentralized exchange apps often prompt users to sign transactions that transfer ownership of assets rather than executing a standard trade. Anyone who has already connected their wallet and approved permissions on this page must use a blockchain explorer or security tool to revoke those allowances immediately.



 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT