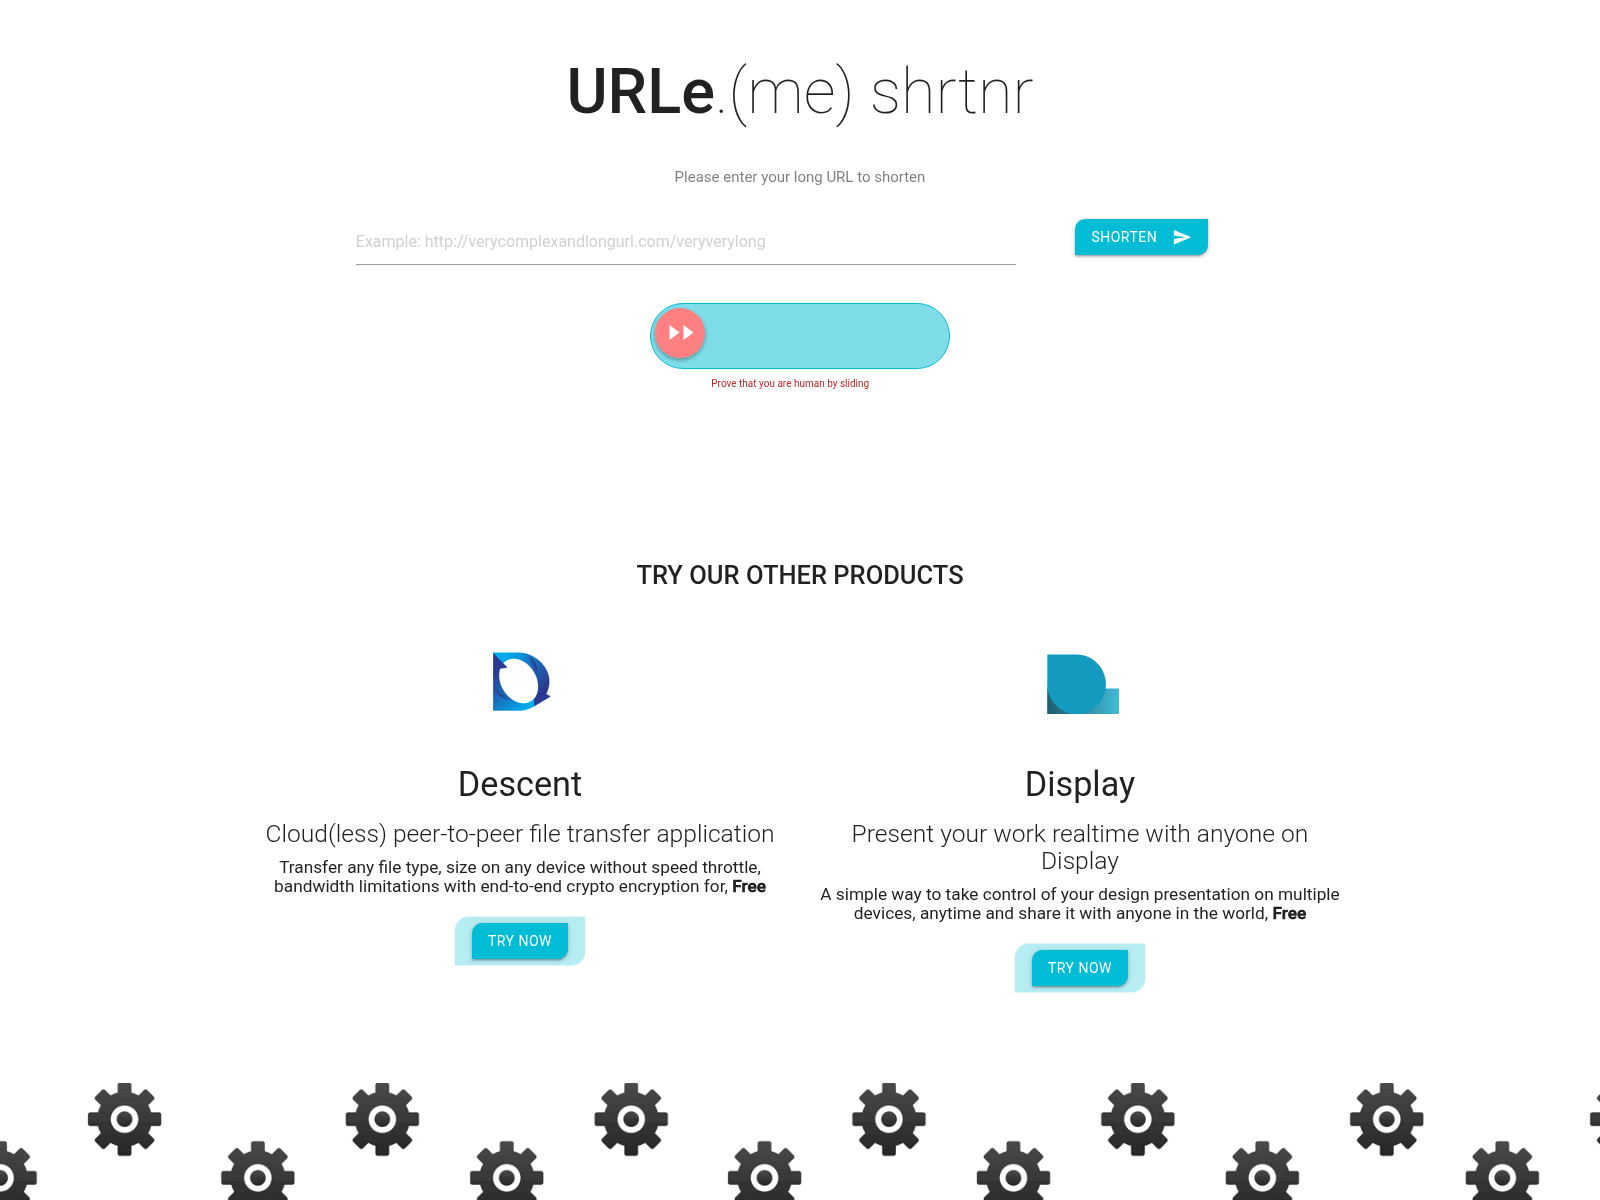
On 2026-11-09, urle.me displayed a URL shortening page branded "URLe.(me) shrtnr." The page asks visitors to enter a long URL to shorten, with an example placeholder and a "SHORTEN" button. Below the input, a slider control reads "Prove that you are human by sliding," requiring the user to drag it to proceed. Further down, a section titled "TRY OUR OTHER PRODUCTS" presents Descent, a cloudless peer-to-peer file transfer application, and Display, a realtime presentation tool, each with a "TRY NOW" button.
URLScanによるキャプチャ · 2026-11-09 03:09 UTC · SHA-256 a8f4fe65…011c6e0
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-11-09, urle.me displayed a URL shortening page branded "URLe.(me) shrtnr." The page asks visitors to enter a long URL to shorten, with an example placeholder and a "SHORTEN" button. Below the input, a slider control reads "Prove that you are human by sliding," requiring the user to drag it to proceed. Further down, a section titled "TRY OUR OTHER PRODUCTS" presents Descent, a cloudless peer-to-peer file transfer application, and Display, a realtime presentation tool, each with a "TRY NOW" button.
The stored VirusTotal domain result reports 7 detections out of 92 engines. VIPRE reported "phishing"; CyRadar reported "malicious".
urle.me: URL Shortener Page with Slider Human Check
AIによる説明
PhishDestroy records urle.me as a URL shortening page offering a link input, a slider human check, and links to Descent and Display products.
AIによる要約
On 2026-11-09, urle.me displayed a URL shortening page branded "URLe.(me) shrtnr." The page asks visitors to enter a long URL to shorten, with an example placeholder and a "SHORTEN" button. Below the input, a slider control reads "Prove that you are human by sliding," requiring the user to drag it to proceed. Further down, a section titled "TRY OUR OTHER PRODUCTS" presents Descent, a cloudless peer-to-peer file transfer application, and Display, a realtime presentation tool, each with a "TRY NOW" button. The stored VirusTotal domain result reports 7 detections out of 92 engines. VIPRE reported "phishing"; CyRadar reported "malicious".
No sri: https://www.googletagmanager.com/gtag/js, https://cdnjs.cloudflare.com/ajax/libs/materialize/1.0.0/js/materialize.min.js, https://ajax.googleapis.com/ajax/libs/jquery/1.11.1/jquery.min.js; Third party scripts: 3
Technologies: PHP, Materialize CSS, Animate.css, PayPal, Nginx, Cloudflare, Google Hosted Libraries, jQuery UI, jQuery, Google Analytics, Google Font API, cdnjs, PWA, Open Graph
The owner of the website is using a service to hide their identity on WHOIS According to Tranco this site has a low rank The registrar has a high % of spammers and fraud sites This website has been reported for phishing by iQ Abuse Scan This website has been marked as threat by DNSFilter in the last 30 days
This website offers "get your money back" friendly payment methods The SSL certificate is valid This website is (very) old
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:51 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:51 UTClast content: 2026-11-22 11:51 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 NameCheap


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT