元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
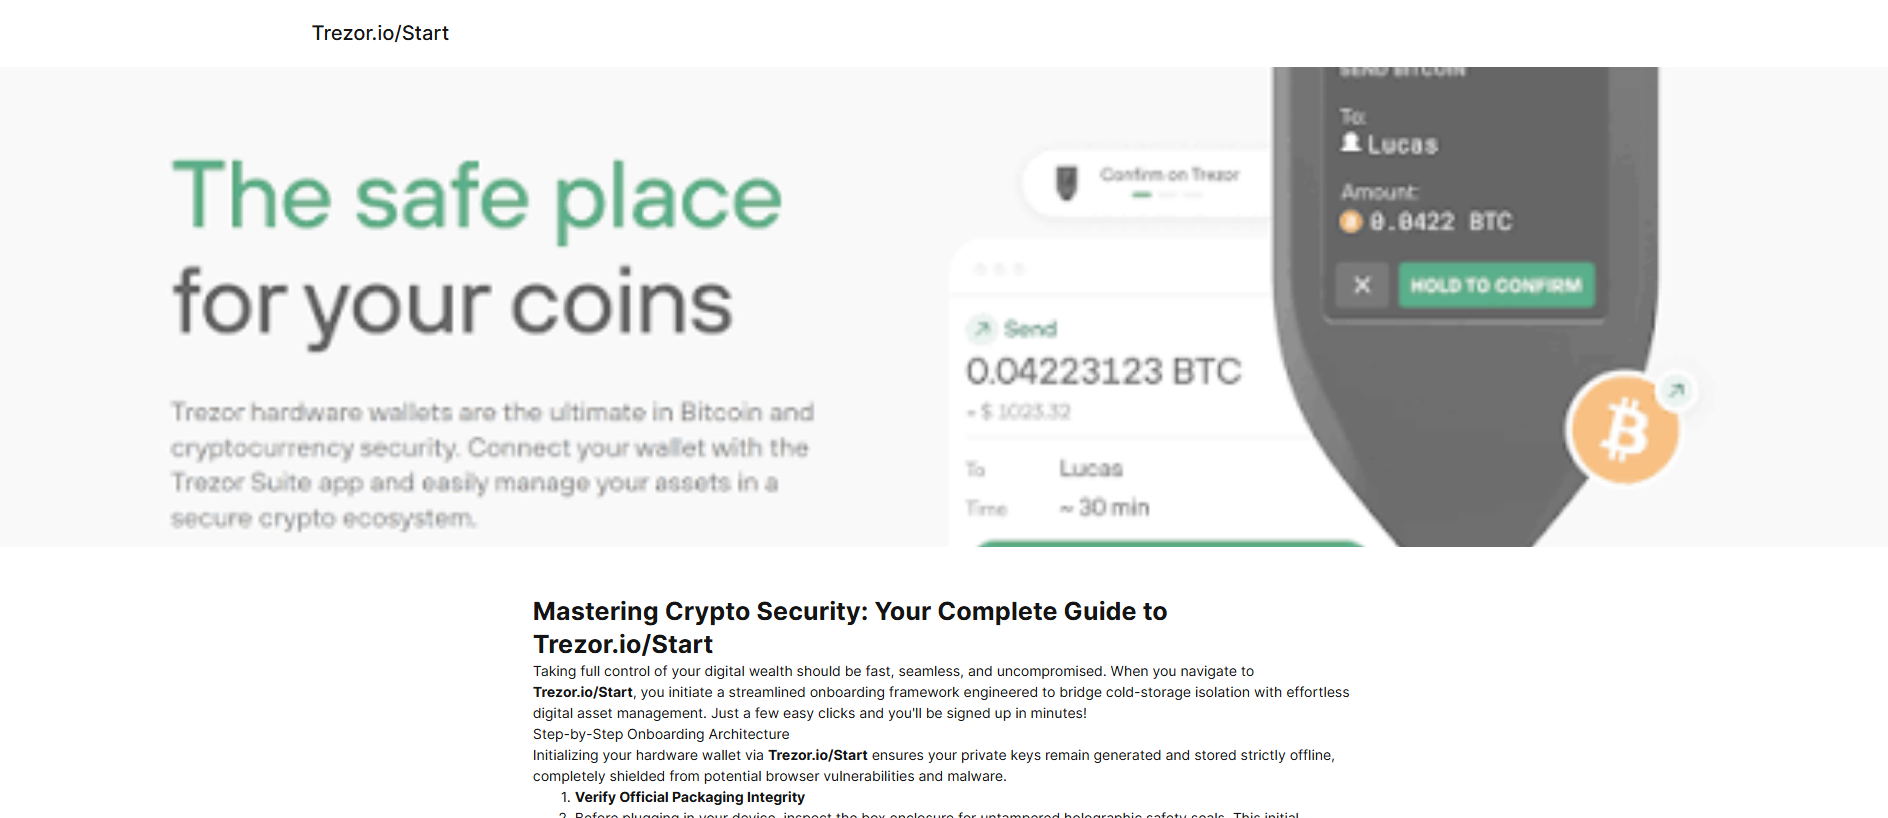
The captured screenshot dated 2026-10-26 shows a page styled as a Trezor hardware-wallet setup guide, headlined 'The safe place for your coins' with a mock Bitcoin send panel and an article titled 'Mastering Crypto Security'. PhishDestroy classified the domain as impersonation of Trezor and first saw it on 2026-10-26.
詐欺の手口
The page presented numbered onboarding steps covering packaging checks, software download, firmware installation, wallet creation and transcription of a 12-to-24-word recovery seed plus a device PIN. As a category risk, this kind of impersonation lures people seeking legitimate wallet setup into following attacker-controlled instructions and handing recovery words or account details to whoever operated the page.
証拠
The screenshot shows Trezor branding, the mock send confirmation, and repeated start-page wording. urlscan rated the capture malicious with an ML score of 100 and a phishing category on 2026-10-26; VirusTotal flagged the domain as malicious with phishing labels including Fortinet and Netcraft, and Phishunt plus PhishDestroy blocklisted it on 2026-10-26. On 2026-10-26 Spamhaus DBL and Google Safe Browsing recorded no listing and OTX recorded 0 pulses, while HTTP redirected to HTTPS with a 307 response. Site inspection revealed Vue-style frontend globals with a Square Online generator, Snowplow, Datadog, Sentry and Weebly Ads trackers, and five distinct artifact SHA256 hashes recorded for pivoting, for example 1ed7b345dc9c.
インフラ
Notable weaknesses: no Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy or COOP/COEP/CORP headers; HSTS present only with a short max-age value; DNSSEC unsigned. The page was served behind the Cloudflare WAF on Square Online hosting, with CAA records present. TLS ran as TLS 1.3 with AES-256-GCM, forward secrecy and ALPN h2.
What to do
If you entered credentials on trezoriostart-apps.square.site, change your password on the genuine service and enable two-factor authentication, and do not enter anything further there. If you disclosed a recovery phrase or installed software from the page, contact the vendor's official support immediately and treat that phrase as exposed. Defenders should block trezoriostart-apps.square.site and keep it listed on phishing blocklists.
PhishDestroy assesses trezoriostart-apps.square.site as an impersonation phishing page targeting Trezor wallet users.
AIによる要約
Overview The captured screenshot dated 2026-10-26 shows a page styled as a Trezor hardware-wallet setup guide, headlined 'The safe place for your coins' with a mock Bitcoin send panel and an article titled 'Mastering Crypto Security'. PhishDestroy classified the domain as impersonation of Trezor and first saw it on 2026-10-26. How the scam works The page presented numbered onboarding steps covering packaging checks, software download, firmware installation, wallet creation and transcription of a 12-to-24-word recovery seed plus a device PIN. As a category risk, this kind of impersonation lures people seeking legitimate wallet setup into following attacker-controlled instructions and handing recovery words or account details to whoever operated the page. Evidence The screenshot shows Trezor branding, the mock send confirmation, and repeated start-page wording. urlscan rated the capture malicious with an ML score of 100 and a phishing category on 2026-10-26; VirusTotal flagged the domain as malicious with phishing labels including Fortinet and Netcraft, and Phishunt plus PhishDestroy blocklisted it on 2026-10-26. On 2026-10-26 Spamhaus DBL and Google Safe Browsing recorded no listing and OTX recorded 0 pulses, while HTTP redirected to HTTPS with a 307 response. Site inspection revealed Vue-style frontend globals with a Square Online generator, Snowplow, Datadog, Sentry and Weebly Ads trackers, and five distinct artifact SHA256 hashes recorded for pivoting, for example 1ed7b345dc9c. Infrastructure Notable weaknesses: no Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy or COOP/COEP/CORP headers; HSTS present only with a short max-age value; DNSSEC unsigned. The page was served behind the Cloudflare WAF on Square Online hosting, with CAA records present. TLS ran as TLS 1.3 with AES-256-GCM, forward secrecy and ALPN h2. What to do If you entered credentials on trezoriostart-apps.square.site, change your password on the genuine service and enable two-factor authentication, and do not enter anything further there. If you disclosed a recovery phrase or installed software from the page, contact the vendor's official support immediately and treat that phrase as exposed. Defenders should block trezoriostart-apps.square.site and keep it listed on phishing blocklists. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17805-b95f-770f-b5bf-396ef43a901b/ Stored capture screenshot: https://i.ibb.co/jv8LRxPm/06527ae1afba.png URLScan screenshot (2026-10-25T16:01:24Z): https://screenshots.phishdestroy.io/us/01a173cb-3f14-76cb-8f0e-052f1e930812.png URLScan capture report: https://urlscan.io/result/01a173cb-3f14-76cb-8f0e-052f1e930812/ URLScan screenshot (2026-10-25T16:01:25Z): https://screenshots.phishdestroy.io/us/01a173cb-3fdb-70fb-ad15-8a4f92c4dc59.png URLScan capture report: https://urlscan.io/result/01a173cb-3fdb-70fb-ad15-8a4f92c4dc59/ URLScan screenshot (2026-10-26T01:03:28Z): https://screenshots.phishdestroy.io/us/01a175bb-8dcf-702b-ab31-9950e53a07a3.png URLScan capture report: https://urlscan.io/result/01a175bb-8dcf-702b-ab31-9950e53a07a3/ URLScan screenshot (2026-10-26T03:53:52Z): https://screenshots.phishdestroy.io/us/01a17657-bdea-715a-96dd-e2154b4b1782.png URLScan capture report: https://urlscan.io/result/01a17657-bdea-715a-96dd-e2154b4b1782/ URLScan screenshot (2026-10-26T07:09:17Z): https://screenshots.phishdestroy.io/us/01a1770a-9d8e-71d0-aa99-21946cc0a76a.png URLScan capture report: https://urlscan.io/result/01a1770a-9d8e-71d0-aa99-21946cc0a76a/ URLScan screenshot (2026-10-26T11:50:21Z): https://screenshots.phishdestroy.io/us/01a1780b-f975-73a5-a46d-53d477347ac5.png URLScan capture report: https://urlscan.io/result/01a1780b-f975-73a5-a46d-53d477347ac5/ VirusTotal report: https://www.virustotal.com/gui/domain/trezoriostart-apps.square.site Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=trezoriostart-apps.square.site Archived copy: https://web.archive.org/web/20261026114026/https://trezoriostart-apps.square.site/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
No sri: https://cdn3.editmysite.com/app/checkout/assets/checkout/locale-imports-map.67f8ca7f01b9f001.json, https://cdn3.editmysite.com/app/checkout/assets/checkout/system.c3b89b0b94f4ef0671b1.js, https://cdn3.editmysite.com/app/checkout/assets/checkout/imports.en.531994a61e25dcaf.js, https://cdn3.editmysite.com/app/website/js/runtime.dcc7f0f39ce4f00f0847.js, https://cdn3.editmysite.com/app/website/js/vue-modules.4a41b3ba298bf4563d97.js, https://cdn3.editmysite.com/app/website/js/languages/en.e51b3a49fda6f61e4bb1.js, https://cdn3.editmysite.com/app/website/js/site.879af28d8ba722506588.js; Third party scripts: 7
最新のHTTP観測結果RedirectingHTTP redirect observed80%2026-11-22 11:18 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:18 UTClast content: 2026-11-08 00:03 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 Square


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT