




ドメインのセキュリティと脅威インテリジェンス

send-usdc.network
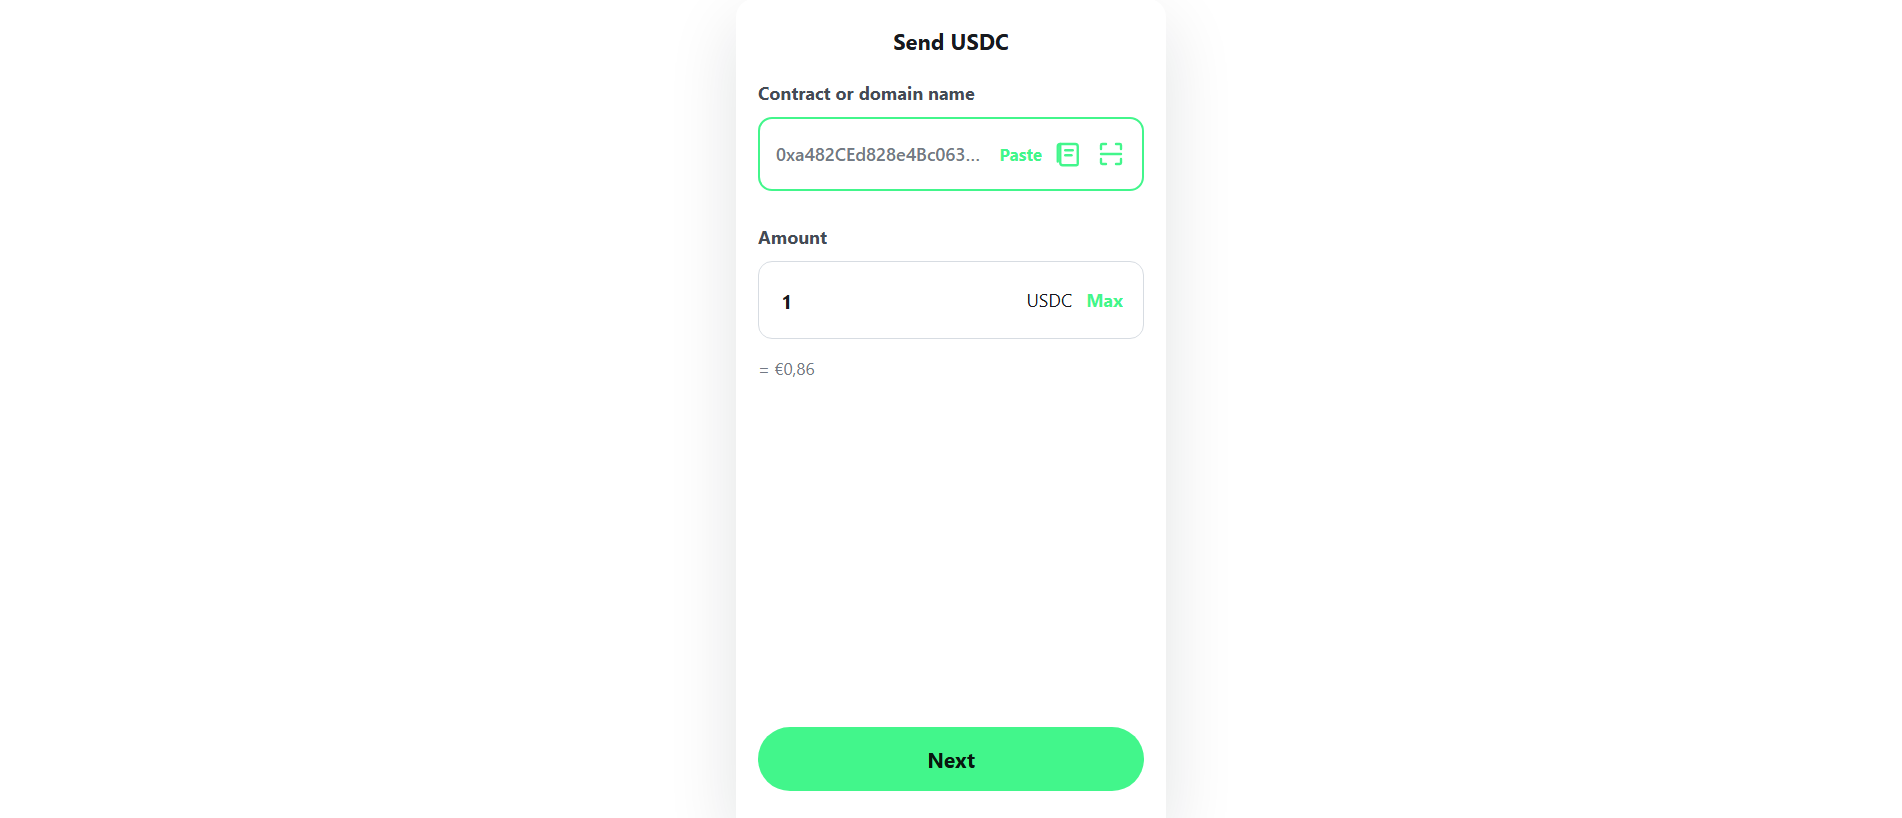
“Send USDC”
脅威の評決
クリティカル
96/100 証拠スコア
可用性
最後に確認されたアクティブな状態
最新の保存された到達可能性の観測
リスクシグナル
VirusTotal 検出数: 12/91
保存されたブロックリストの一致: 2
ブランドの偽装: Unknown
最後に確認されたアクティブな状態
Actions
API
ABUSE NOTICE · 7D+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@namecheap.com.
The latest stored availability evidence still shows the domain reachable; 2 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
2 months
Reports sent
1
Latest case ID
PD-20260628-CE392C
Current status
HTTP 302 at latest stored check
レポート概要
send-usdc.network — 最後に確認されたアクティブな状態 (HTTP 302). ブランドの偽装: Unknown; 詐欺タイプ: Impersonation. 証拠の概要: VirusTotal 12/91 (alphaMountain.ai, BitDefender, CRDF, Ermes, Forcepoint ThreatSeeker); 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 96/100. レジストラ: NameCheap.
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
証拠の概要
重要
This domain is flagged as an active phishing site designed to intercept USDC cryptocurrency transactions. The page title, 'Send USDC,' suggests a fraudulent interface mimicking legitimate crypto transfer services, likely tricking users into sending funds to attacker-controlled wallets. The domain specifically targets individuals attempting to transfer USD Coin (USDC), a stablecoin, by presenting a deceptive transaction portal that harvests wallet credentials or misdirects payments. Analysis indicates the site may employ social engineering tactics, such as urgency or fake confirmations, to expedite unauthorized transfers before victims detect the fraud. Infrastructure analysis reveals the domain was registered on June 25, 2026, through NameCheap, Inc., and currently resolves to the IP address 162.0.217.211. Despite its recent creation, the domain has not been flagged by any of the 95 security vendors on VirusTotal (0/95 detections), indicating it may still be operating under the radar. The SSL certificate is issued by Sectigo Limited, which, while legitimate, does not guarantee the site's safety. No blocklist entries or prior reports were identified, suggesting this is a newly deployed threat vector with no prior exposure. Users who have interacted with send-usdc.network should immediately cease all activity and revoke any wallet permissions granted to the site. If funds were transferred, report the transaction to the relevant blockchain explorer and contact the wallet provider or exchange for potential recovery options. Monitor connected accounts for unauthorized activity, as phishing sites often deploy secondary payloads or credential harvesting. Security teams should add the domain and its resolving IP (162.0.217.211) to network blocklists and investigate logs for prior connections. Given the domain's recent registration and lack of detection, heightened vigilance is advised for similar USDC-themed phishing campaigns.
VirusTotal
12 det.
URLScan
TLS証明書
Sectigo Limited
年齢
3 mo New
観測ステータス
最後に確認されたアクティブな状態 302

DestroyList
掲載あり
Reports Sent
1
データの網羅性
VirusTotal
12 / 91
URLQuery
source data unavailable
OTX
no community references
CFレーダー
scan completed
URLScan capture
保存されたレポート
URLScan verdict
分析完了
DNSブロック
14 確認済み — ブロックなし
TLS
valid certificate, 196d
WHOIS
3 mo old
スクリーンショット
2 captures · 2 sources
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
VirusTotal Detections Update Jun 28, 2026 · 18:34 UTCVirusTotal scanner detections updated from None to 0.
脅威対応 Pipeline
ディスカバリー
Checks
Reports
可用性
12/13
Sent Report Recorded
Stored sent-report record for registrar NameCheap, Inc., hosting provider, 1 abuse contact
abuse@namecheap.com
公開ブロックリスト登録状況
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not observed
- クローキングスコア
- 0/6
- Last cloaking scan
- Server header seen by scanner
LiteSpeed
Scanner note: redirect: raw=redirect_302; http=302; via=https_proxy; location=login.php; server=LiteSpeed
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
保存済みキャプチャ · 2 sources
ドメイン・インテリジェンス
ドメイン
URLScan Verdict
分析完了
score 0 report ↗
Wallet IoCs
1 format-validated
0xa482CEd828e4Bc063cBFDD3046061…
サーバー / ASN
LiteSpeed · AS22612 Namecheap, Inc.
IPレピュテーション
abuse score 0/100 0 reports checked 2026年8月28日
レジストラ
NameCheap
 (US)
(US)
IPアドレス
162.0.217.211

登録情報作成日 2026年6月25日 (86d · New) — Expires 2027年6月25日
HTTPステータス302 Found (Temporary)
技術詳細DNS、SSL SAN、タイムスタンプ
初確認2026年6月28日
DOM Analysis
IoC Extraction
Submitted URLhttp://send-usdc.network/
ネームサーバーdns1.namecheaphosting.comdns2.namecheaphosting.com
TLS Fingerprint
TLS Observation
TLS SAN Domainswww.send-usdc.network
ケース ID
ICANN OVERSIGHT
認定と RAA の背景
認定と RAA の背景
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
認定は契約であり、安全のお墨付きではありません。
ICANNの手数料を確認
RAA §3.18を読む
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
このドメインを報告する
証拠を提出し、他の人を守る手助けをしましょう
VirusTotalによる分析
12 / 91 セキュリティ ベンダーがこのドメインにフラグを立てました
View on VT
Last analyzed Previous stored snapshot: 10 detections
alphaMountain.ai
BitDefender
CRDF
Ermes
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
カスペルスキー
Lionic
SOCRadar
ソフォス
サイトパフォーマンス分析
Google PageSpeed Insights — mobile performance audit of send-usdc.network · checked Jun 28, 2026
99
Good
Performance
FCP
1.36s
First Contentful Paint
LCP
1.95s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
1.36s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
証拠および外部報告書
証券分析
送信済み証拠のスナップショット
Sent: Ledger records: 1
Case ID:
PD-20260628-CE392C Recipient: abuse@namecheap.com Page title stored with report: Problem loading page
PDF notice generated Notice text archived (289 chars)
Abuse notice text as sent to the provider
Registrar: Namecheap Inc (United States)
Policy Violations: Domain Registration Agreement prohibits hacking, misuse of domain to conduct attacks, scam and fraudulent activities; AUP allows immediate suspension
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
OSINTおよび情報分析
DNSとネットワーク
SEOとドメイン
このサイトによって何か影響を受けましたか?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
アカウント資格情報、個人情報、支払い情報を入力した場合、またはこのドメインからファイルをダウンロードした場合は、すぐに対処してください。インシデントを報告し、自分自身を守るのに役立つリソースを以下に示します。


PhishDestroy listing review 法執行機関の報告書ではありません
ドメイン異議申立て
このドメインを所有していて、リストが間違っていると思われる場合は、審査をリクエストしてください
復旧を装った詐欺に注意! 犯罪者は、捜査員、弁護士、または回収業者を装い、被害者に再び連絡を取る可能性があります。 前払い料金を支払ったり、資格情報を共有したりしないでください。 回復詐欺について詳しくはこちら →
お住まいの地域の当局へ報告してください
サイバー犯罪の公式連絡先 または 苦情草稿を作成する → を取得するには、国を選択してください。
97か国のディレクトリ
AI 支援ドラフト — インシデントの詳細は AI プロバイダーによって処理されます
自分で確認して送信する
関連インフラとレポート
Infrastructure map · send-usdc.network
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
同じレジストラ: NameCheap 6
Unknown impersonation 8
These domains also target 不明 users. View all Unknown threats →
Unknown kit 8
Part of the 不明 phishing campaign. View all campaign domains →
最近の脅威レポート 5
PhishDestroy データベースから最近追加されたレポート。これらの検出リンクは、共有インフラストラクチャや所有権を意味するものではありません。
 wrencapstead.digital
任意のドメインを確認する
保存されたブロックリスト、WHOIS、DNS、および公開スキャン証拠を使用した脅威分析
今すぐスキャンフィッシングを報告する
不審なドメインを当社の脅威データベースに報告してください — コミュニティを守りましょう
レポートリアルタイム脅威情報フィード
最近のフィッシングレポートと観察された可用性の変化
監視最新情報を入手し、安全を確保しましょう
リアルタイムの脅威を監視するか、誤検知だと思われる場合はこのリストに異議を申し立ててください