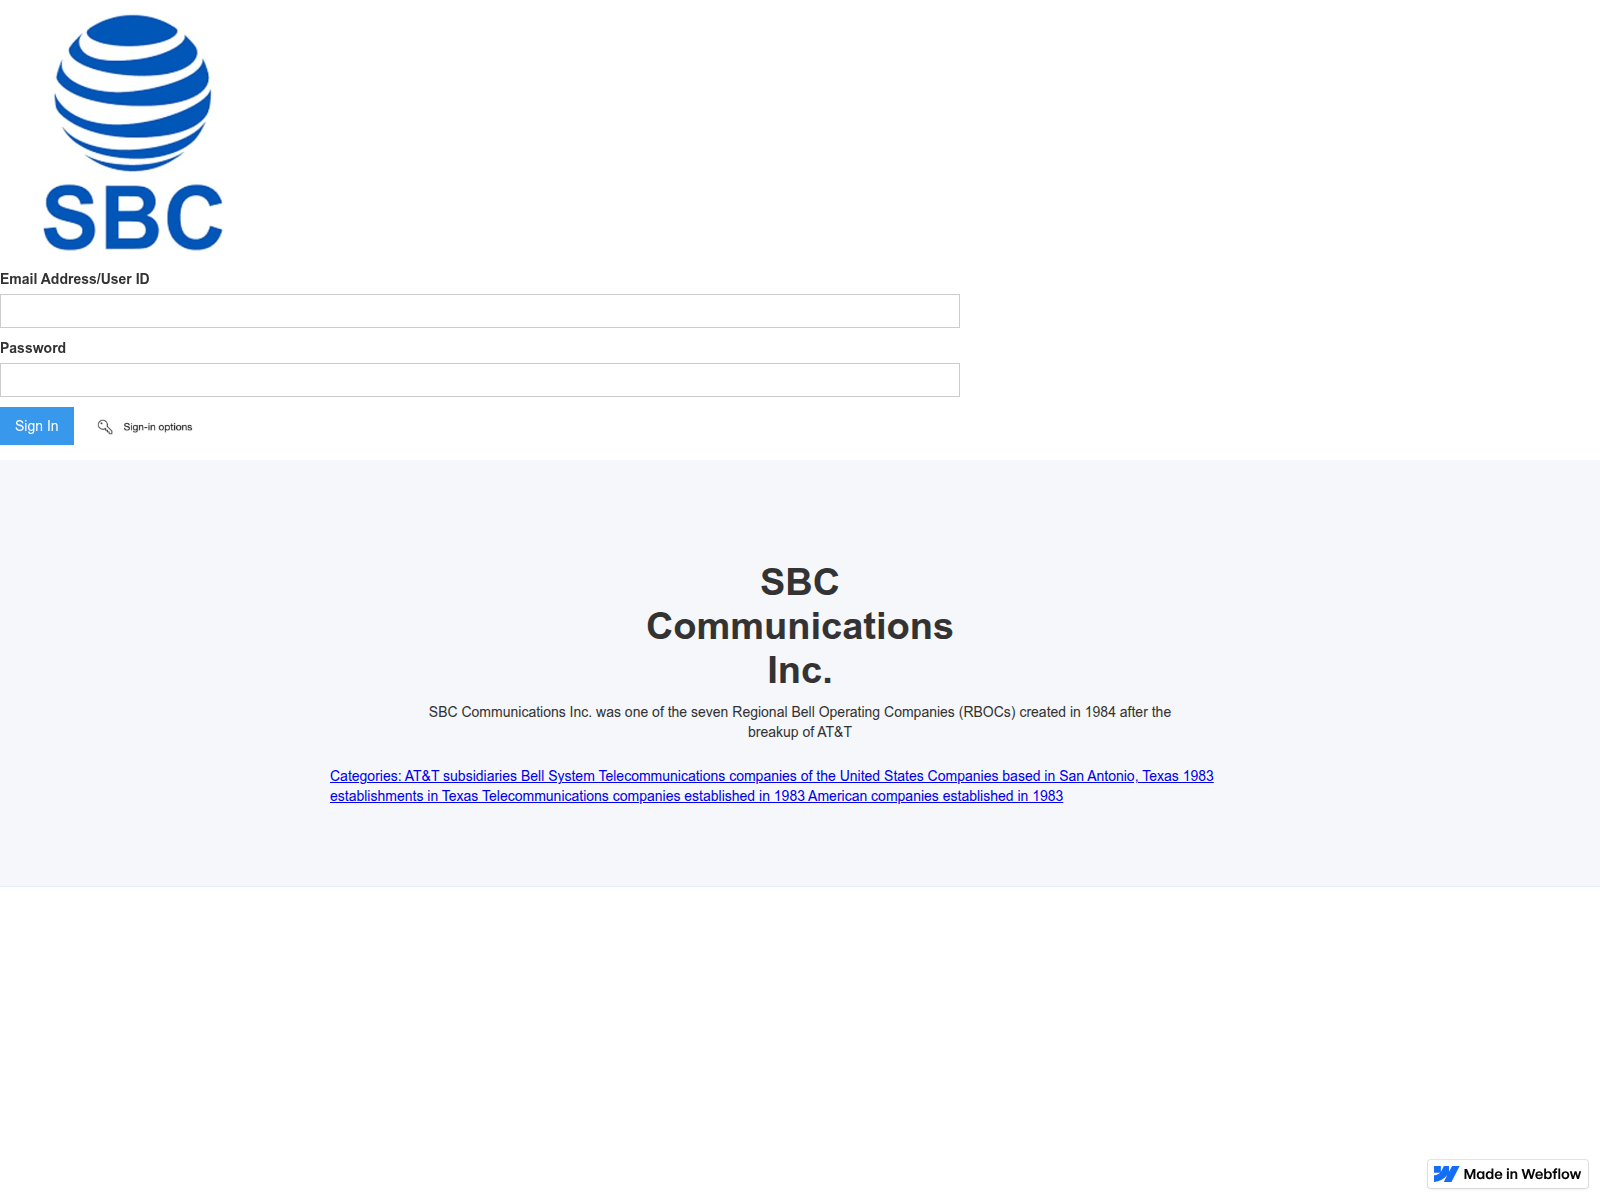
This page mimics an SBC Communications sign-in portal to harvest user credentials and account details. If you entered your password here, change it immediately on the official service.
URLScanによるキャプチャ · 2026-11-17 18:00 UTC · SHA-256 cbe21cb9…c2b6541
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Visual layout and credential harvesting interface
The page hosted at sbc-verifier-sign-in-5119de.webflow.io presents a clean white background featuring the prominent blue SBC globe logo and the text "SBC". Below the branding, it displays input fields labelled "Email Address/User ID" and "Password", accompanied by a blue "Sign In" button and a link for "Sign-in options". Further down the page, explanatory text describes "SBC Communications Inc." along with historical details referencing its origins from the breakup of AT&T and related category links. The layout is designed to trick visitors into believing they are accessing a legitimate telecom sign-in portal. By prompting users to submit their credentials directly into these fields, the site aims to capture sensitive login information for unauthorized access.
Security detections and independent threat verification
18 of 92 VirusTotal engines flagged it on 17 Nov 2026, and OpenPhish blocks it, which confirms that the risk is recognized across multiple security platforms. PhishDestroy's evidence score for it is 75/100 (critical), indicating a high level of threat for users who encounter the link. Because the site still responded on 18 Nov 2026 at 10:40 UTC, visitors continue to face active exposure if they navigate to the URL.
Recommended actions for affected visitors
Anyone who entered credentials on this page should immediately update their passwords on the legitimate service and any other accounts sharing the same credentials. Monitor associated email and financial accounts for unauthorized activity. Report the abusive URL directly to the platform provider at webflow.io to request removal.
sbc-verifier-sign-in-5119de.webflow.io — SBC credential form
AIによる説明
sbc-verifier-sign-in-5119de.webflow.io copies an SBC sign-in portal to capture credentials, noted as flagged by 18 VirusTotal engines. Protect your account.
AIによる要約
Visual layout and credential harvesting interface The page hosted at sbc-verifier-sign-in-5119de.webflow.io presents a clean white background featuring the prominent blue SBC globe logo and the text "SBC". Below the branding, it displays input fields labelled "Email Address/User ID" and "Password", accompanied by a blue "Sign In" button and a link for "Sign-in options". Further down the page, explanatory text describes "SBC Communications Inc." along with historical details referencing its origins from the breakup of AT&T and related category links. The layout is designed to trick visitors into believing they are accessing a legitimate telecom sign-in portal. By prompting users to submit their credentials directly into these fields, the site aims to capture sensitive login information for unauthorized access. Security detections and independent threat verification 18 of 92 VirusTotal engines flagged it on 17 Nov 2026, and OpenPhish blocks it, which confirms that the risk is recognized across multiple security platforms. PhishDestroy's evidence score for it is 75/100 (critical), indicating a high level of threat for users who encounter the link. Because the site still responded on 18 Nov 2026 at 10:40 UTC, visitors continue to face active exposure if they navigate to the URL. Recommended actions for affected visitors Anyone who entered credentials on this page should immediately update their passwords on the legitimate service and any other accounts sharing the same credentials. Monitor associated email and financial accounts for unauthorized activity. Report the abusive URL directly to the platform provider at webflow.io to request removal.
エビデンスレイヤーAvailability: Root path has no contentContent: Absent At RootDNS: Stale
最新のHTTP観測結果非アクティブHttp No Content70%2026-11-22 11:14 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-18 12:13 UTCcurrent episode first observed: 2026-11-19 00:08 UTCobserved RIP window: 2026-11-18 12:13 UTC → 2026-11-19 00:08 UTC · 11.92hmidpoint estimate ≈ 2026-11-18 18:10 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 Webflow
 172.64.151.8


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT