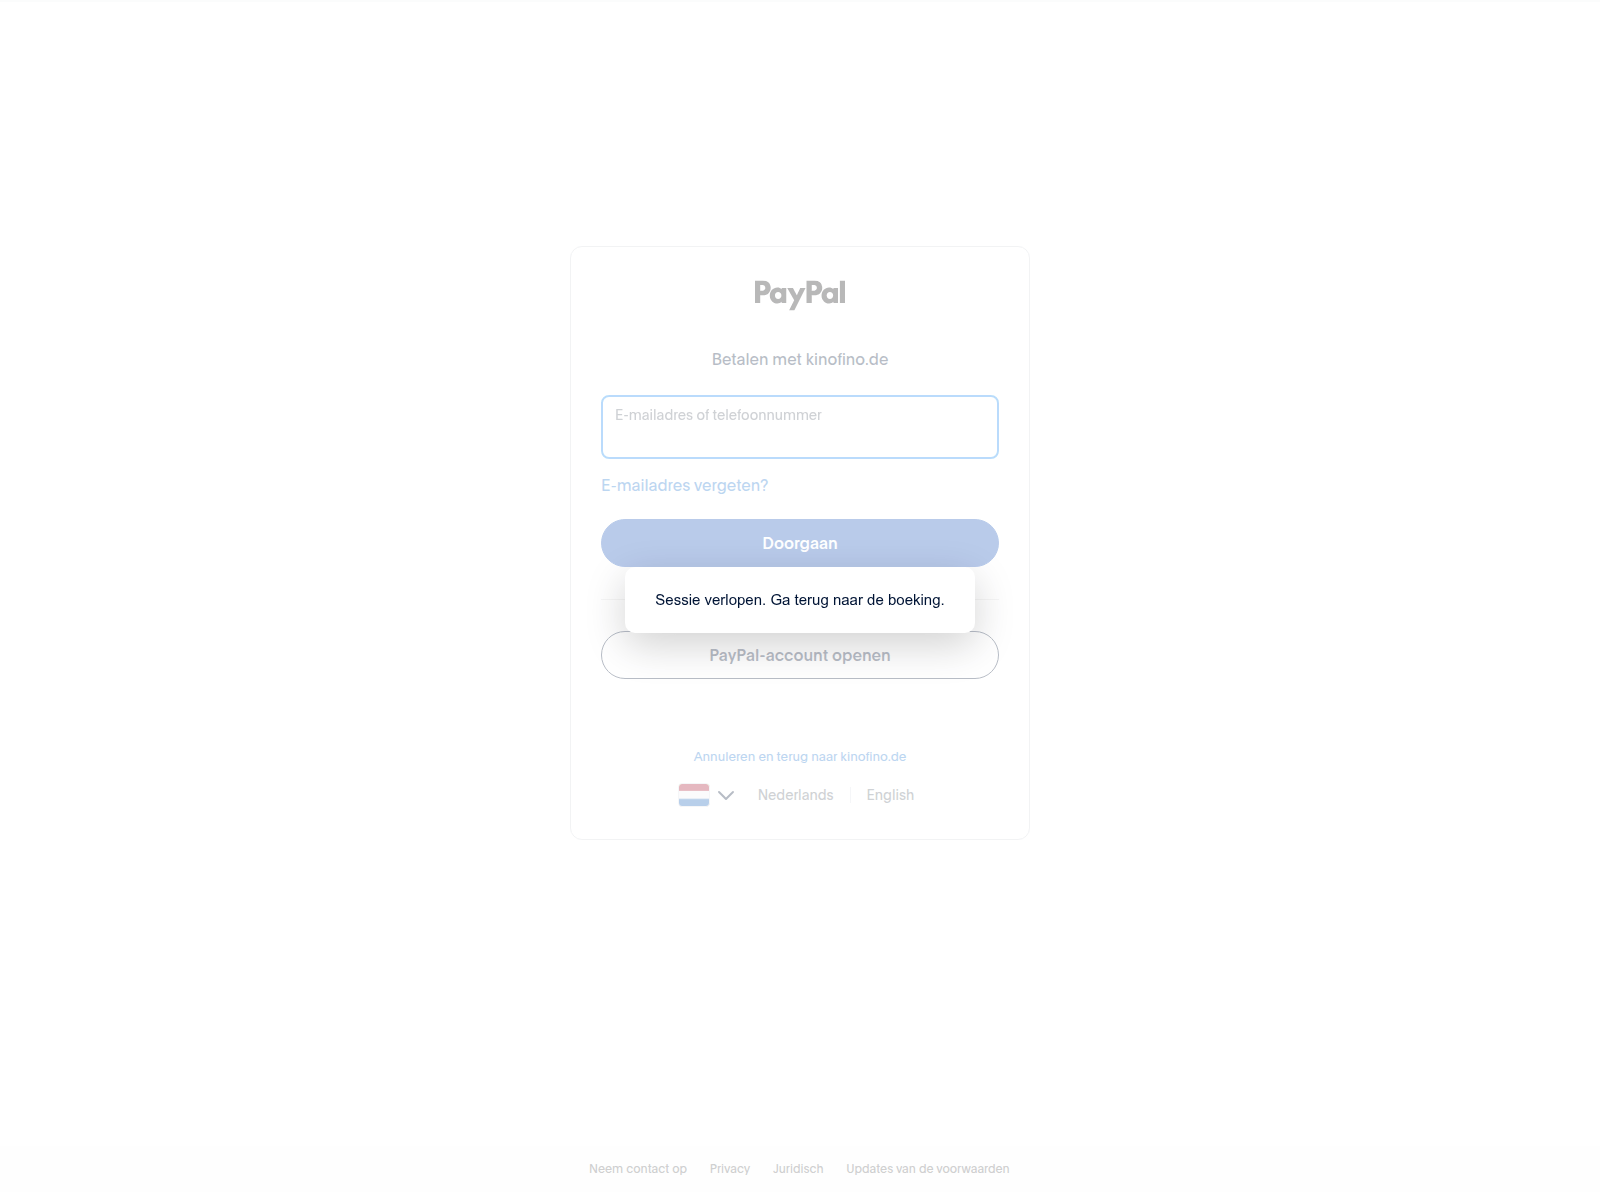
paypal.kinofino.de presents a fraudulent PayPal login page in Dutch designed to harvest user credentials. If you submitted your details, immediately secure your account on the official paypal.com website and review your recent transactions.
URLScanによるキャプチャ · 2026-11-21 22:44 UTC · SHA-256 d8defef5…bfaa18a
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Dutch PayPal login lure and page design
The page at paypal.kinofino.de opens with a centered PayPal logo above text reading "Betalen met kinofino.de". An overlaying notification box displays "Sessie verlopen. Ga terug naar de boeking." to simulate an expired session. A single input field asks visitors to enter their "E-mailadres of telefoonnummer", followed by a blue "Doorgaan" button. Additional elements include links for account recovery and a language selector with a Dutch flag. The address bar confirms this is an unauthorized domain rather than the official service at paypal.com.
Credential collection and independent security analysis
The form directly collects login details entered by unsuspecting visitors to compromise their accounts. Because Spamhaus DBL lists it as phishing, 23 of 92 VirusTotal engines flagged it on 12 Nov 2026, and Cloudflare Radar rated it malicious (phishing, Security threats), including vendors such as Kaspersky, ESET and BitDefender, this is a known threat rather than a false alarm. Furthermore, its PhishDestroy evidence score is 75/100 (critical).
Shared hosting infrastructure and related domains
Analyzing the server background reveals that 3 other reported domains resolve to the same IP address and 8 use the same nameserver pair. Specifically, domains such as paypal.kinoberry.de, paypal.kinoloft.de and paypal.kinodora.de point to the identical server setup. This clustering demonstrates a coordinated campaign utilizing shared hosting resources to deploy multiple harvesting pages simultaneously.
paypal.kinofino.de displays a fraudulent Dutch PayPal login page collecting account credentials, flagged by Spamhaus DBL and 23 VirusTotal engines.
AIによる要約
Dutch PayPal login lure and page design The page at paypal.kinofino.de opens with a centered PayPal logo above text reading "Betalen met kinofino.de". An overlaying notification box displays "Sessie verlopen. Ga terug naar de boeking." to simulate an expired session. A single input field asks visitors to enter their "E-mailadres of telefoonnummer", followed by a blue "Doorgaan" button. Additional elements include links for account recovery and a language selector with a Dutch flag. The address bar confirms this is an unauthorized domain rather than the official service at paypal.com. Credential collection and independent security analysis The form directly collects login details entered by unsuspecting visitors to compromise their accounts. Because Spamhaus DBL lists it as phishing, 23 of 92 VirusTotal engines flagged it on 12 Nov 2026, and Cloudflare Radar rated it malicious (phishing, Security threats), including vendors such as Kaspersky, ESET and BitDefender, this is a known threat rather than a false alarm. Furthermore, its PhishDestroy evidence score is 75/100 (critical). Shared hosting infrastructure and related domains Analyzing the server background reveals that 3 other reported domains resolve to the same IP address and 8 use the same nameserver pair. Specifically, domains such as paypal.kinoberry.de, paypal.kinoloft.de and paypal.kinodora.de point to the identical server setup. This clustering demonstrates a coordinated campaign utilizing shared hosting resources to deploy multiple harvesting pages simultaneously.

 150.241.66.223


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT