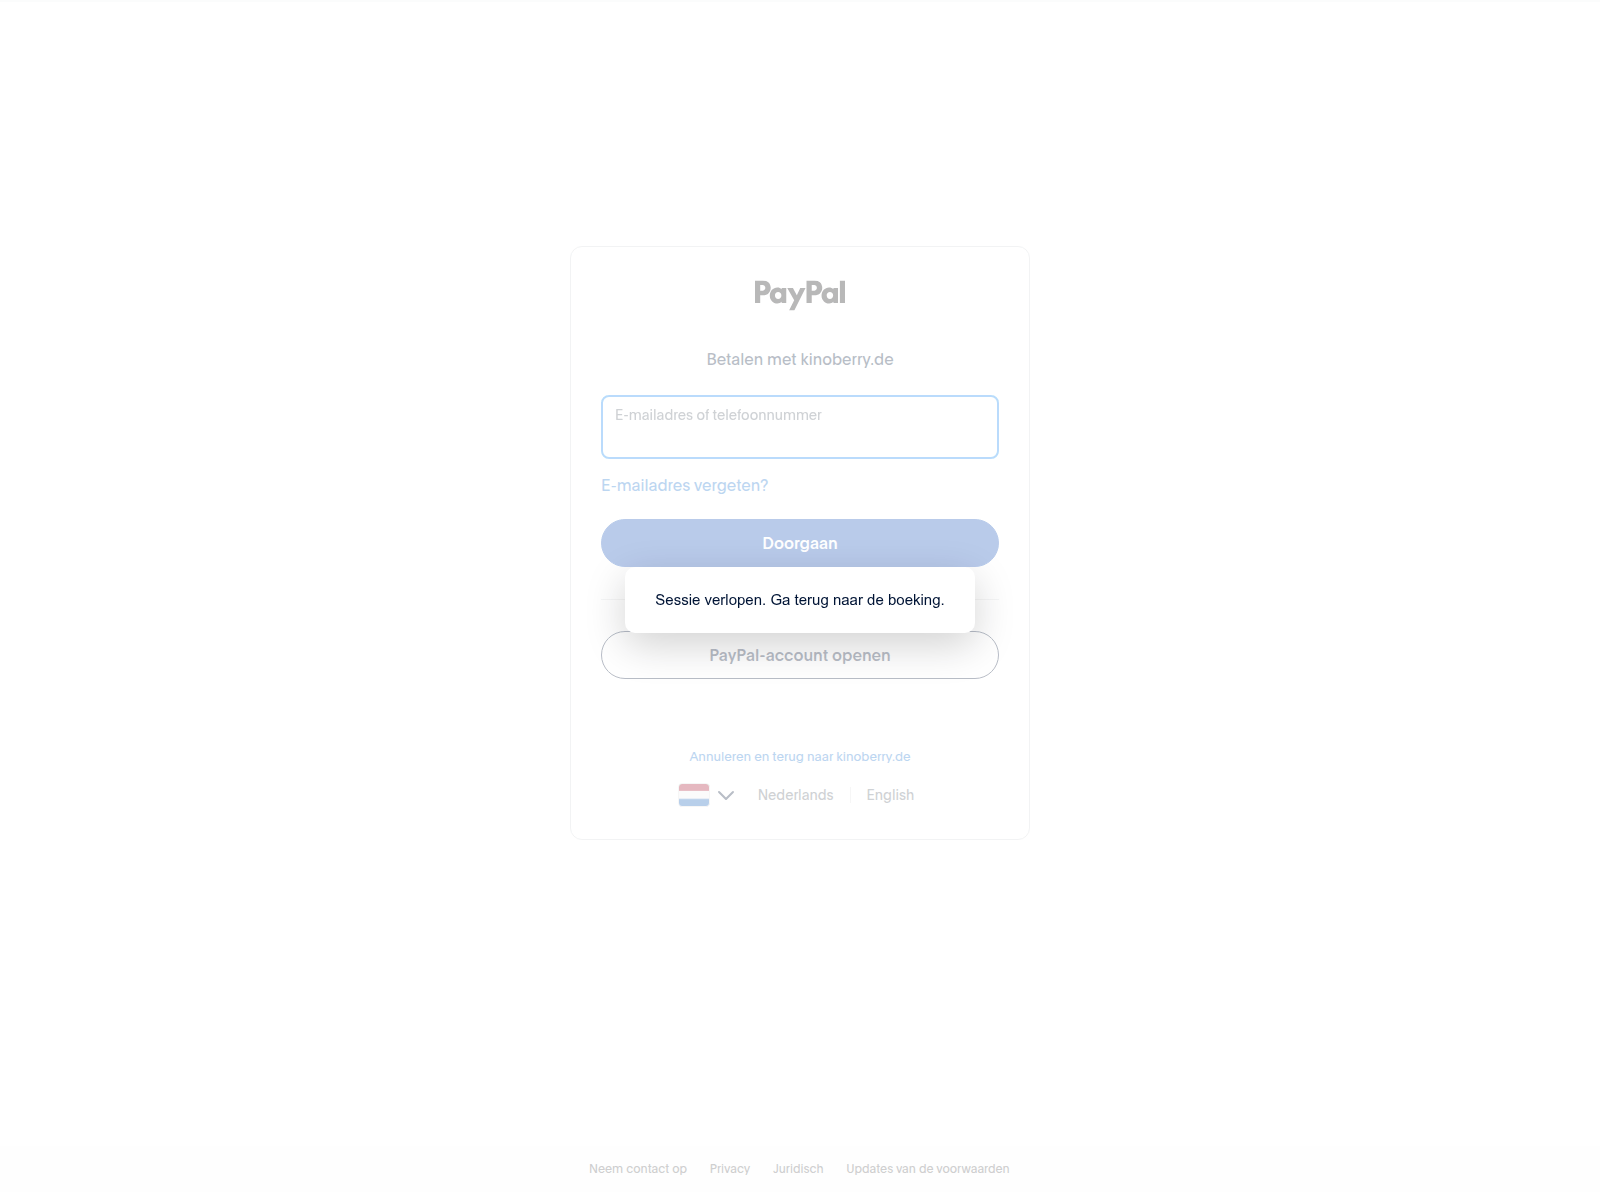
This site is a fake PayPal login portal in Dutch designed to capture user credentials through a standard password collection form. If you already submitted your details, immediately change your password on the official PayPal site at paypal.com and review your account activity.
URLScanによるキャプチャ · 2026-11-21 23:23 UTC · SHA-256 e58a4d81…79c67be
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
PayPal login clone layout and Dutch interface
The page displays the PayPal logo at the top followed by the text "Betalen met kinoberry.de". An input field asks for "E-mailadres of telefoonnummer", accompanied by a blue action button labeled "Doorgaan". A popup dialog in Dutch states "Sessie verlopen. Ga terug naar de boeking." Additional links offer options to create an account or return to the kinoberry.de domain, while language selectors for Dutch and English appear near the bottom. The interface is specifically designed to convince visitors they are authenticating a payment or booking through a legitimate PayPal integration.
Credential harvesting and security detections
The form requests your account identifier to capture login credentials under the guise of an active session. Because Spamhaus DBL lists it as phishing, 6 of 92 VirusTotal engines flagged it on 10 Nov 2026, and Cloudflare Radar rated it malicious (phishing), with Fortinet, Netcraft and Webroot among the engines flagging the malicious address, this page is actively identified as a credential harvesting threat rather than a mislabeled asset. PhishDestroy scores the evidence against it at 70/100 (critical).
Shared server infrastructure and campaign patterns
Analysis of the hosting environment reveals that 3 other reported domains resolve to the same IP address and 8 use the same nameserver pair, including paypal.kinoloft.de, paypal.kinodora.de and paypal.kinofino.de. The presence of multiple similarly named endpoints on the same server indicates an automated deployment pattern used by operators to continuously spin up new credential harvesting portals.
paypal.kinoberry.de presents a fake PayPal login form in Dutch, flagged by Spamhaus DBL and 6 VirusTotal engines. Never submit your credentials here.
AIによる要約
PayPal login clone layout and Dutch interface The page displays the PayPal logo at the top followed by the text "Betalen met kinoberry.de". An input field asks for "E-mailadres of telefoonnummer", accompanied by a blue action button labeled "Doorgaan". A popup dialog in Dutch states "Sessie verlopen. Ga terug naar de boeking." Additional links offer options to create an account or return to the kinoberry.de domain, while language selectors for Dutch and English appear near the bottom. The interface is specifically designed to convince visitors they are authenticating a payment or booking through a legitimate PayPal integration. Credential harvesting and security detections The form requests your account identifier to capture login credentials under the guise of an active session. Because Spamhaus DBL lists it as phishing, 6 of 92 VirusTotal engines flagged it on 10 Nov 2026, and Cloudflare Radar rated it malicious (phishing), with Fortinet, Netcraft and Webroot among the engines flagging the malicious address, this page is actively identified as a credential harvesting threat rather than a mislabeled asset. PhishDestroy scores the evidence against it at 70/100 (critical). Shared server infrastructure and campaign patterns Analysis of the hosting environment reveals that 3 other reported domains resolve to the same IP address and 8 use the same nameserver pair, including paypal.kinoloft.de, paypal.kinodora.de and paypal.kinofino.de. The presence of multiple similarly named endpoints on the same server indicates an automated deployment pattern used by operators to continuously spin up new credential harvesting portals.

 150.241.66.223


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT