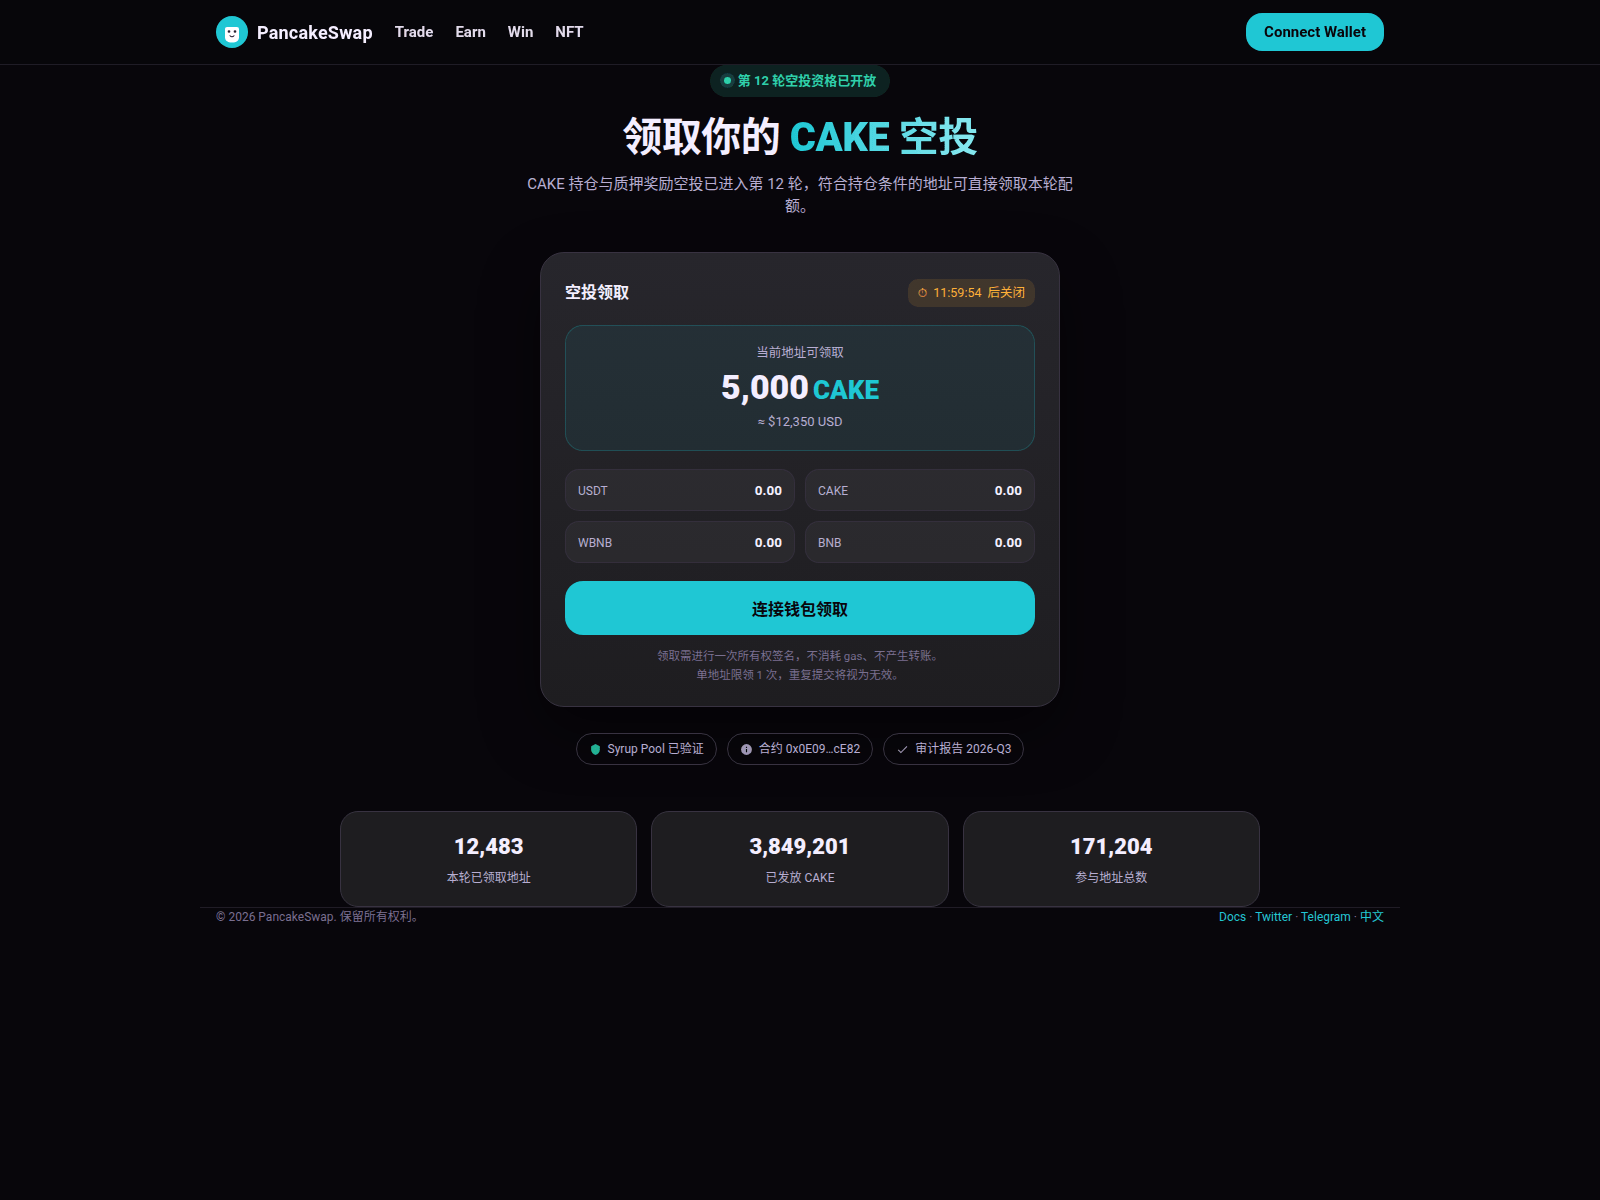
The domain pancakeswap-claim.xyz presents an unauthorized PancakeSwap airdrop page urging visitors to connect their cryptocurrency wallets to claim thousands of tokens. If you connected your wallet, immediately revoke any granted approvals through your wallet settings and disconnect all active sessions.
URLScanによるキャプチャ · 2026-11-22 07:21 UTC · SHA-256 37b7563e…1294ace
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
PancakeSwap airdrop claim interface
The page displays a dark-themed interface mimicking PancakeSwap, written in Chinese, featuring a top navigation bar with standard brand links and a prominent "Connect Wallet" button. Large header text reads "领取你的 CAKE 空投" alongside a countdown timer and a banner announcing the twelfth round of investments. A central modal highlights an eligible reward of "5,000 CAKE" valued at over ten thousand dollars, displaying user balances for USDT, CAKE, WBNB, and BNB. Below these figures, a bright teal button prompts the user to "连接钱包领取" to initiate the claim process. Smaller footer metrics claim over twelve thousand participating addresses, millions of distributed tokens, and a total address count. The real project operates exclusively at pancakeswap.finance, making this address an independent copy designed to deceive visitors.
Wallet connection and asset risk
By prompting users to link their cryptocurrency wallets, the site aims to execute malicious signature requests that can drain token balances or grant unauthorized spending approvals. 4 of 92 VirusTotal engines flagged it on 22 Nov 2026, with Forcepoint ThreatSeeker, LevelBlue and PhishFort among the engines flagging the URL. Its PhishDestroy evidence score is 45/100 (high), so this is a known malicious destination rather than a false alarm. Interacting with the claim button typically triggers a prompt that transfers control of deposited funds to the operator.
Recent domain registration timeline
It was registered on 20 Nov 2026, 1 day before it was first reported, utilizing the registrar NameSilo, LLC. This minimal lifespan sharply contrasts with the mature metrics and high claim numbers displayed across the page layout, highlighting a pattern typical of hastily deployed crypto token scams.
pancakeswap-claim.xyz displays an unofficial PancakeSwap token claim asking to link your crypto wallet, flagged by 4 VirusTotal engines. Avoid connecting.
AIによる要約
PancakeSwap airdrop claim interface The page displays a dark-themed interface mimicking PancakeSwap, written in Chinese, featuring a top navigation bar with standard brand links and a prominent "Connect Wallet" button. Large header text reads "领取你的 CAKE 空投" alongside a countdown timer and a banner announcing the twelfth round of investments. A central modal highlights an eligible reward of "5,000 CAKE" valued at over ten thousand dollars, displaying user balances for USDT, CAKE, WBNB, and BNB. Below these figures, a bright teal button prompts the user to "连接钱包领取" to initiate the claim process. Smaller footer metrics claim over twelve thousand participating addresses, millions of distributed tokens, and a total address count. The real project operates exclusively at pancakeswap.finance, making this address an independent copy designed to deceive visitors. Wallet connection and asset risk By prompting users to link their cryptocurrency wallets, the site aims to execute malicious signature requests that can drain token balances or grant unauthorized spending approvals. 4 of 92 VirusTotal engines flagged it on 22 Nov 2026, with Forcepoint ThreatSeeker, LevelBlue and PhishFort among the engines flagging the URL. Its PhishDestroy evidence score is 45/100 (high), so this is a known malicious destination rather than a false alarm. Interacting with the claim button typically triggers a prompt that transfers control of deposited funds to the operator. Recent domain registration timeline It was registered on 20 Nov 2026, 1 day before it was first reported, utilizing the registrar NameSilo, LLC. This minimal lifespan sharply contrasts with the mature metrics and high claim numbers displayed across the page layout, highlighting a pattern typical of hastily deployed crypto token scams.
Stored registration data identifies NameSilo as the registrar. PhishDestroy maintains separate registrar investigations; that broader material is contextual and is not an independent detection for this domain.

 NameSilo
 45.194.27.242


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT