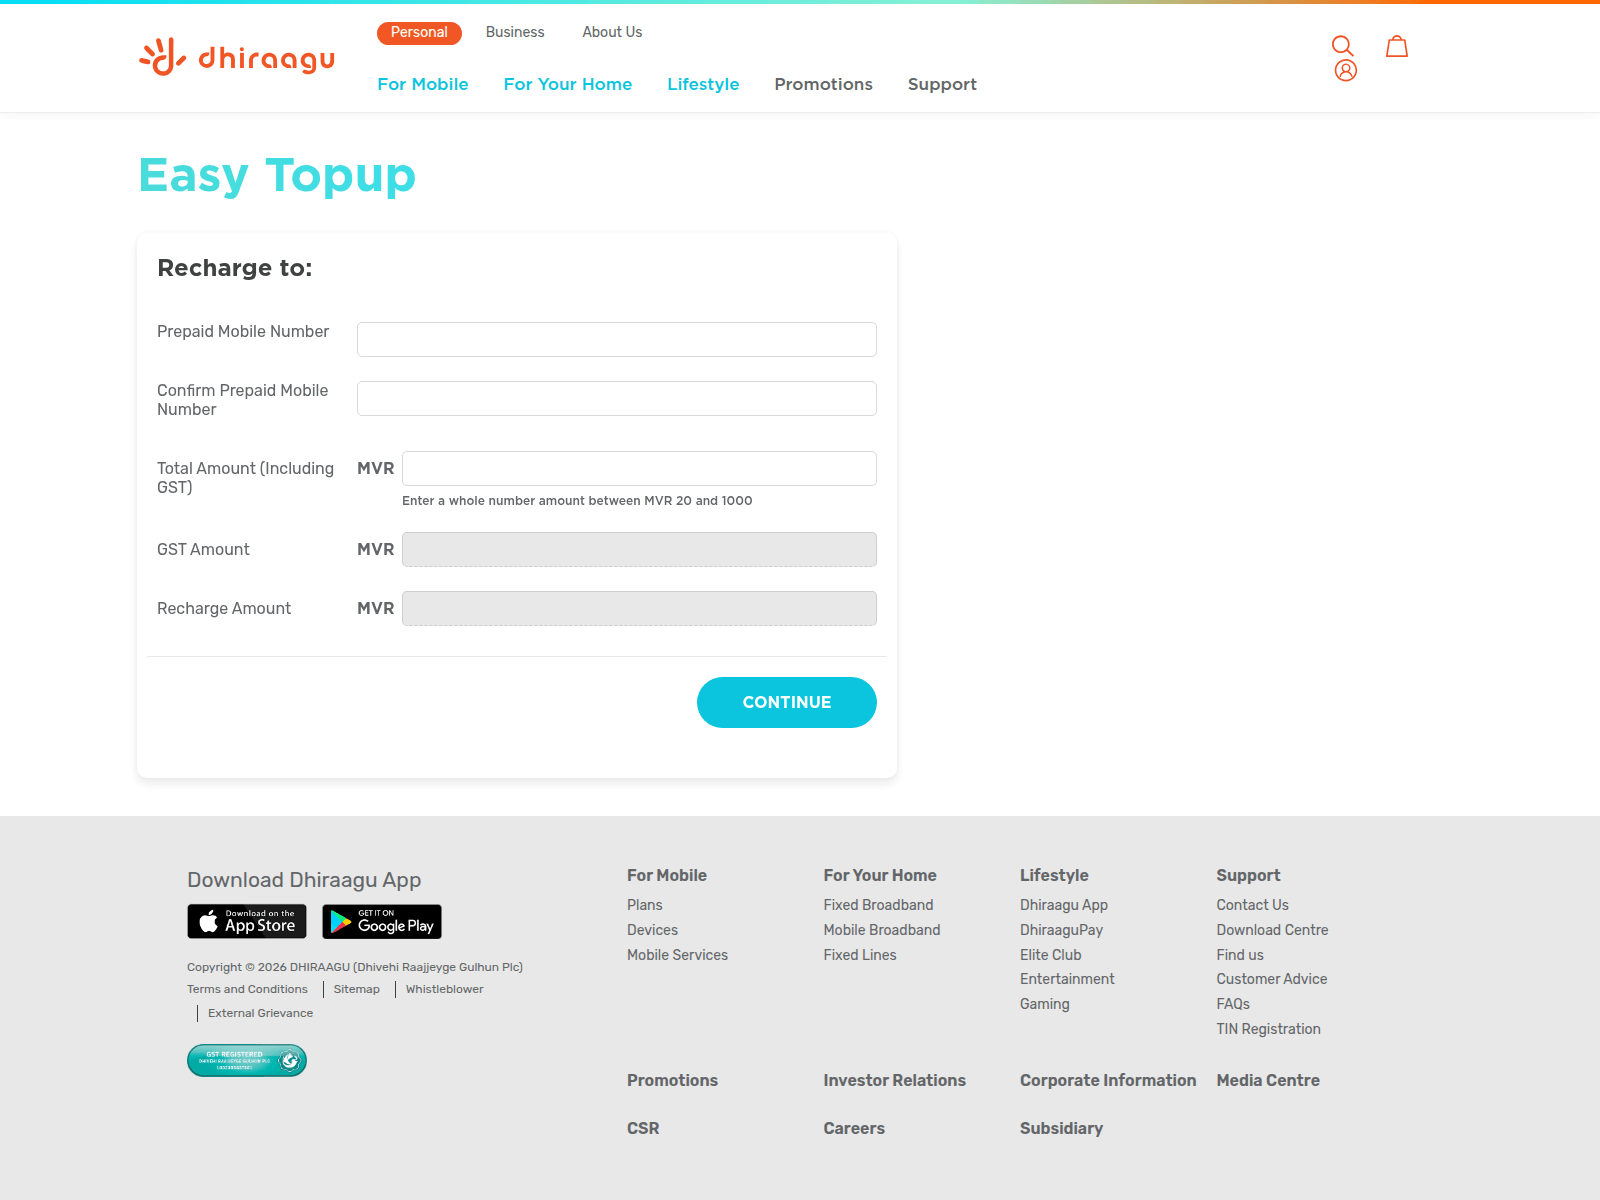
On 2026-11-06, mydhlraagu-app.com displayed an "Easy Topup" page under Dhiraagu branding, with navigation links for Personal, Business, For Mobile, For Your Home, Lifestyle, Promotions, and Support. The main panel is headed "Recharge to:" and contains fields for a prepaid mobile number, a confirmation of that number, and a total amount in MVR, with a note to enter a whole number between MVR 20 and 1000. Read-only fields show the GST amount and recharge amount, and a cyan "CONTINUE" button sits below the form.

URLScanによるキャプチャ · 2026-11-06 01:52 UTC · SHA-256 0ff1e0c3…a4ab012
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-11-06, mydhlraagu-app.com displayed an "Easy Topup" page under Dhiraagu branding, with navigation links for Personal, Business, For Mobile, For Your Home, Lifestyle, Promotions, and Support. The main panel is headed "Recharge to:" and contains fields for a prepaid mobile number, a confirmation of that number, and a total amount in MVR, with a note to enter a whole number between MVR 20 and 1000. Read-only fields show the GST amount and recharge amount, and a cyan "CONTINUE" button sits below the form.
The stored VirusTotal domain result reports 2 detections out of 92 engines. Fortinet reported "spam"; alphaMountain.ai reported "spam".
mydhlraagu-app.com: Recorded Easy Topup recharge form page
AIによる説明
PhishDestroy records mydhlraagu-app.com showing an Easy Topup page with a prepaid mobile recharge form, Dhiraagu branding, and a continue button.
AIによる要約
On 2026-11-06, mydhlraagu-app.com displayed an "Easy Topup" page under Dhiraagu branding, with navigation links for Personal, Business, For Mobile, For Your Home, Lifestyle, Promotions, and Support. The main panel is headed "Recharge to:" and contains fields for a prepaid mobile number, a confirmation of that number, and a total amount in MVR, with a note to enter a whole number between MVR 20 and 1000. Read-only fields show the GST amount and recharge amount, and a cyan "CONTINUE" button sits below the form. The stored VirusTotal domain result reports 2 detections out of 92 engines. Fortinet reported "spam"; alphaMountain.ai reported "spam".
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:23 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:23 UTClast content: 2026-11-22 11:23 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.