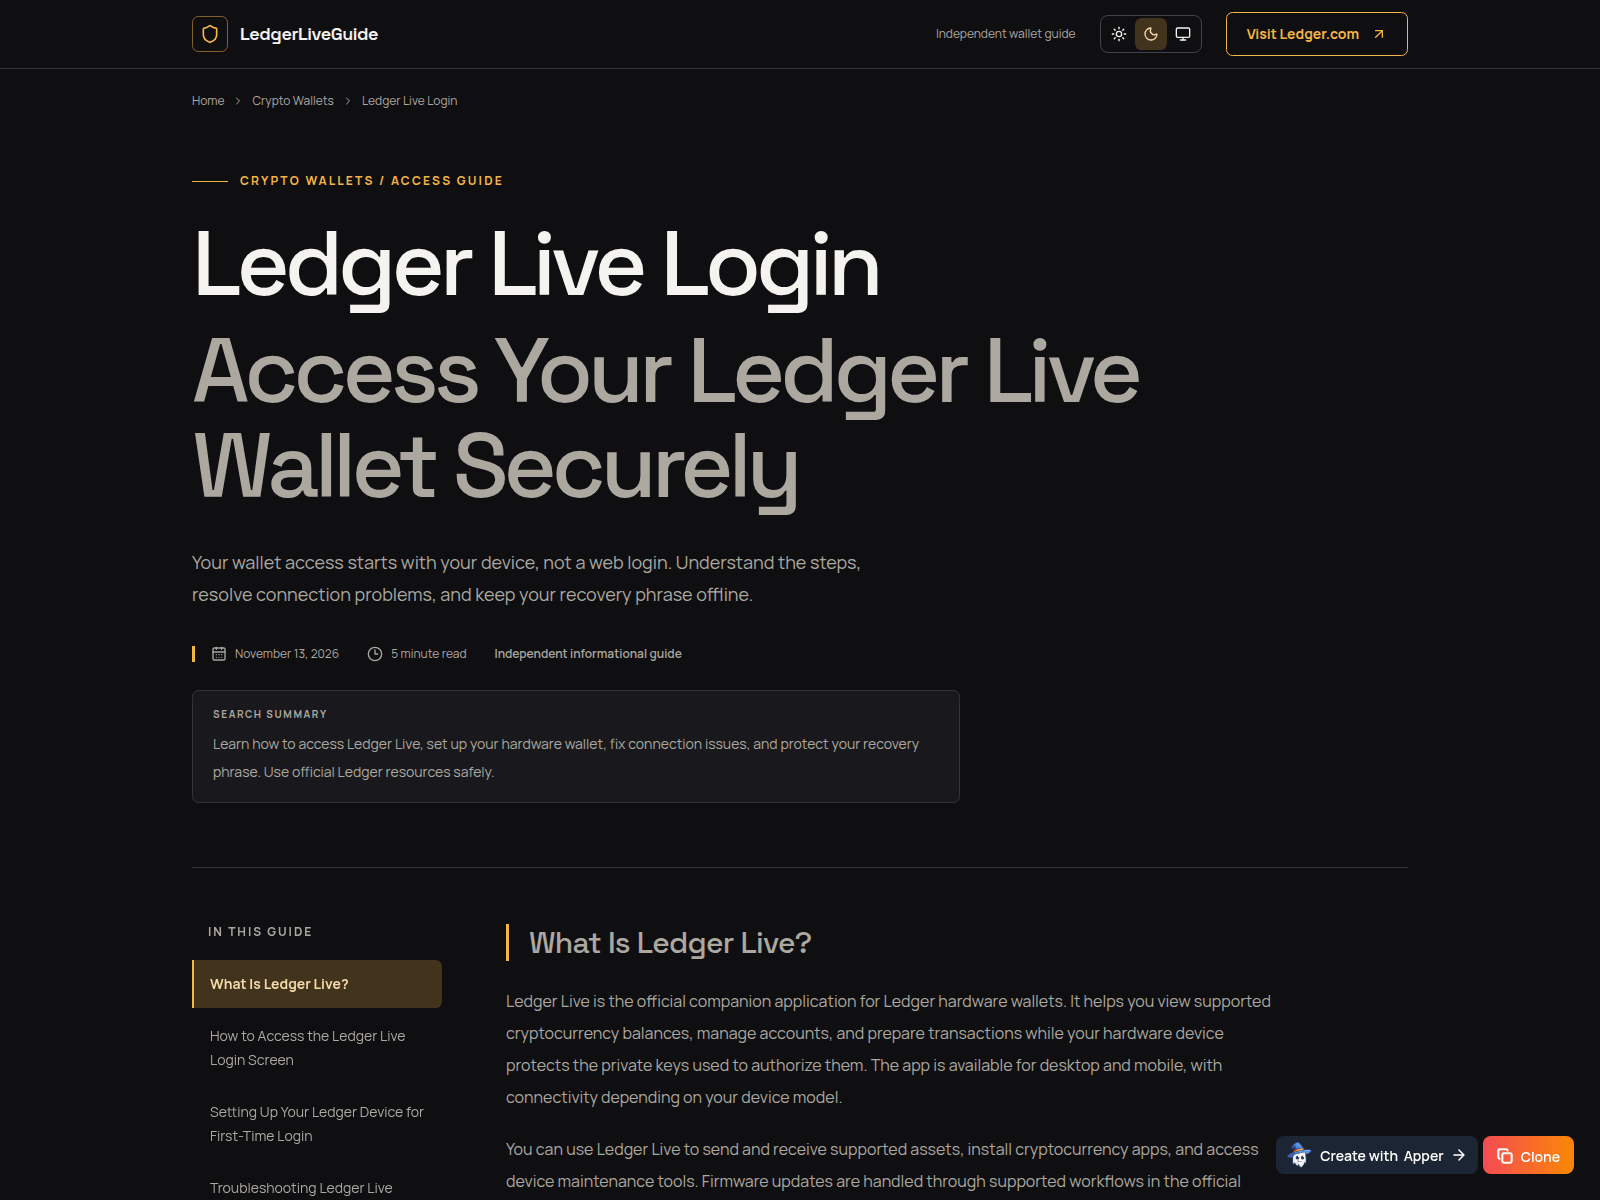
On 2026-11-16, learn-live-ldgr.apper.so displayed a LedgerLiveGuide-branded informational page titled Ledger Live Login. The interface presents headings about crypto wallets and access guides, stating that wallet access starts with a device and advising users to keep recovery phrases offline. Additional sections feature a search summary box, navigation links for setting up hardware devices, and introductory text describing Ledger Live as a companion application for managing cryptocurrency assets and viewing balances.
URLScanによるキャプチャ · 2026-11-16 19:41 UTC · SHA-256 8f82f57d…858249d
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-11-16, learn-live-ldgr.apper.so displayed a LedgerLiveGuide-branded informational page titled Ledger Live Login. The interface presents headings about crypto wallets and access guides, stating that wallet access starts with a device and advising users to keep recovery phrases offline. Additional sections feature a search summary box, navigation links for setting up hardware devices, and introductory text describing Ledger Live as a companion application for managing cryptocurrency assets and viewing balances.
The stored VirusTotal domain result reports 11 detections out of 92 engines. ESET reported "suspicious"; VIPRE reported "phishing".
PhishDestroy records learn-live-ldgr.apper.so hosting a LedgerLiveGuide-branded guide page discussing wallet access and login instructions.
AIによる要約
On 2026-11-16, learn-live-ldgr.apper.so displayed a LedgerLiveGuide-branded informational page titled Ledger Live Login. The interface presents headings about crypto wallets and access guides, stating that wallet access starts with a device and advising users to keep recovery phrases offline. Additional sections feature a search summary box, navigation links for setting up hardware devices, and introductory text describing Ledger Live as a companion application for managing cryptocurrency assets and viewing balances. The stored VirusTotal domain result reports 11 detections out of 92 engines. ESET reported "suspicious"; VIPRE reported "phishing".
エビデンスレイヤーAvailability: Root path has no contentContent: Absent At RootDNS: Resolved
最新のHTTP観測結果非アクティブHttp No Content70%2026-11-22 11:13 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-19 11:08 UTClast content: 2026-11-19 11:08 UTCcurrent episode first observed: 2026-11-19 23:08 UTCobserved RIP window: 2026-11-19 11:08 UTC → 2026-11-19 23:08 UTC · 12.00hmidpoint estimate ≈ 2026-11-19 17:08 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.