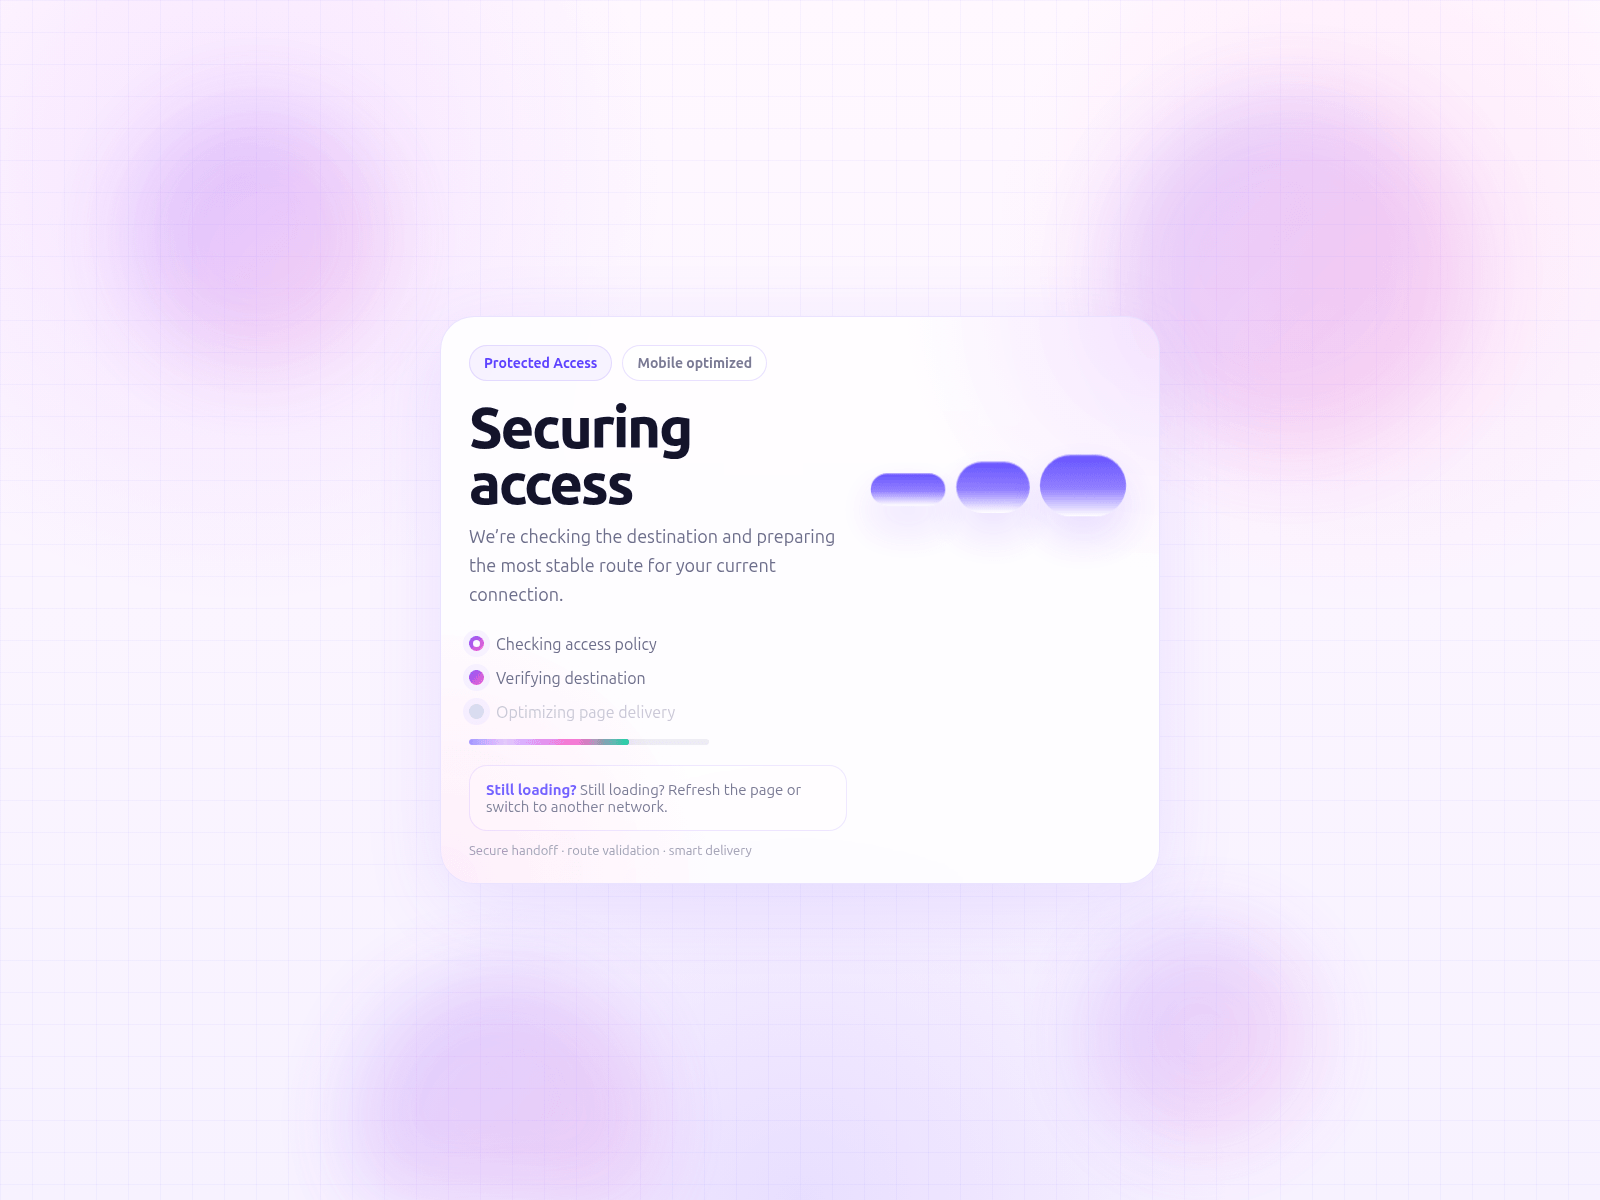
goodforgrill.forum displays an automated access check page that intercepts visitors before destination routing. Verify the connection source and avoid entering credentials or sensitive data if redirected.
URLScanによるキャプチャ · 2026-11-22 05:24 UTC · SHA-256 4a583870…64dfe23
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Page layout and routing check
The goodforgrill.forum domain served a minimalist interface styled with soft purple gradients and rounded containers. At the top, small pill tags read "Protected Access" and "Mobile optimized" above the prominent bold headline "Securing access". Subtitle text explains, "We're checking the destination and preparing the most stable route for your current connection." Below this message, three checklist items show progress steps: "Checking access policy", "Verifying destination", and "Optimizing page delivery", accompanied by a loading progress bar. A secondary text box adds, "Still loading? Still loading? Refresh the page or switch to another network." The footer displays small text noting "Secure handoff • route validation • smart delivery", while abstract graphical buttons sit on the right side of the card layout.
Registration timeline and independent security flags
It was registered on 17 Nov 2026, 4 days before it was first reported, which establishes that the domain is newly created and lacks historical operating context. Because urlscan classified the page as malicious, 1 of 92 VirusTotal engines flagged it on 20 Nov 2026, and Cloudflare Radar rated it suspicious (New Domains, Security Risks), with Fortinet among the evaluating vendors, the address is recognized by external security platforms as warranting caution rather than operating as an established service.
Shared hosting infrastructure and operator patterns
The domain operates alongside other questionable properties, because 8 other domains on PhishDestroy's list share its IP address. Specifically, phantom-card.cc, happyelephant.click and gettw.cc present identical "Securing access" landing pages, pointing to a centralized operator deploying standardized routing templates across multiple addresses.
goodforgrill.forum presents a securing access loading page with routing checks, flagged by urlscan, 1 VirusTotal engine and Cloudflare Radar.
AIによる要約
Page layout and routing check The goodforgrill.forum domain served a minimalist interface styled with soft purple gradients and rounded containers. At the top, small pill tags read "Protected Access" and "Mobile optimized" above the prominent bold headline "Securing access". Subtitle text explains, "We're checking the destination and preparing the most stable route for your current connection." Below this message, three checklist items show progress steps: "Checking access policy", "Verifying destination", and "Optimizing page delivery", accompanied by a loading progress bar. A secondary text box adds, "Still loading? Still loading? Refresh the page or switch to another network." The footer displays small text noting "Secure handoff • route validation • smart delivery", while abstract graphical buttons sit on the right side of the card layout. Registration timeline and independent security flags It was registered on 17 Nov 2026, 4 days before it was first reported, which establishes that the domain is newly created and lacks historical operating context. Because urlscan classified the page as malicious, 1 of 92 VirusTotal engines flagged it on 20 Nov 2026, and Cloudflare Radar rated it suspicious (New Domains, Security Risks), with Fortinet among the evaluating vendors, the address is recognized by external security platforms as warranting caution rather than operating as an established service. Shared hosting infrastructure and operator patterns The domain operates alongside other questionable properties, because 8 other domains on PhishDestroy's list share its IP address. Specifically, phantom-card.cc, happyelephant.click and gettw.cc present identical "Securing access" landing pages, pointing to a centralized operator deploying standardized routing templates across multiple addresses.
Stored registration data identifies NameSilo as the registrar. PhishDestroy maintains separate registrar investigations; that broader material is contextual and is not an independent detection for this domain.

 NameSilo
 196.251.107.223


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT