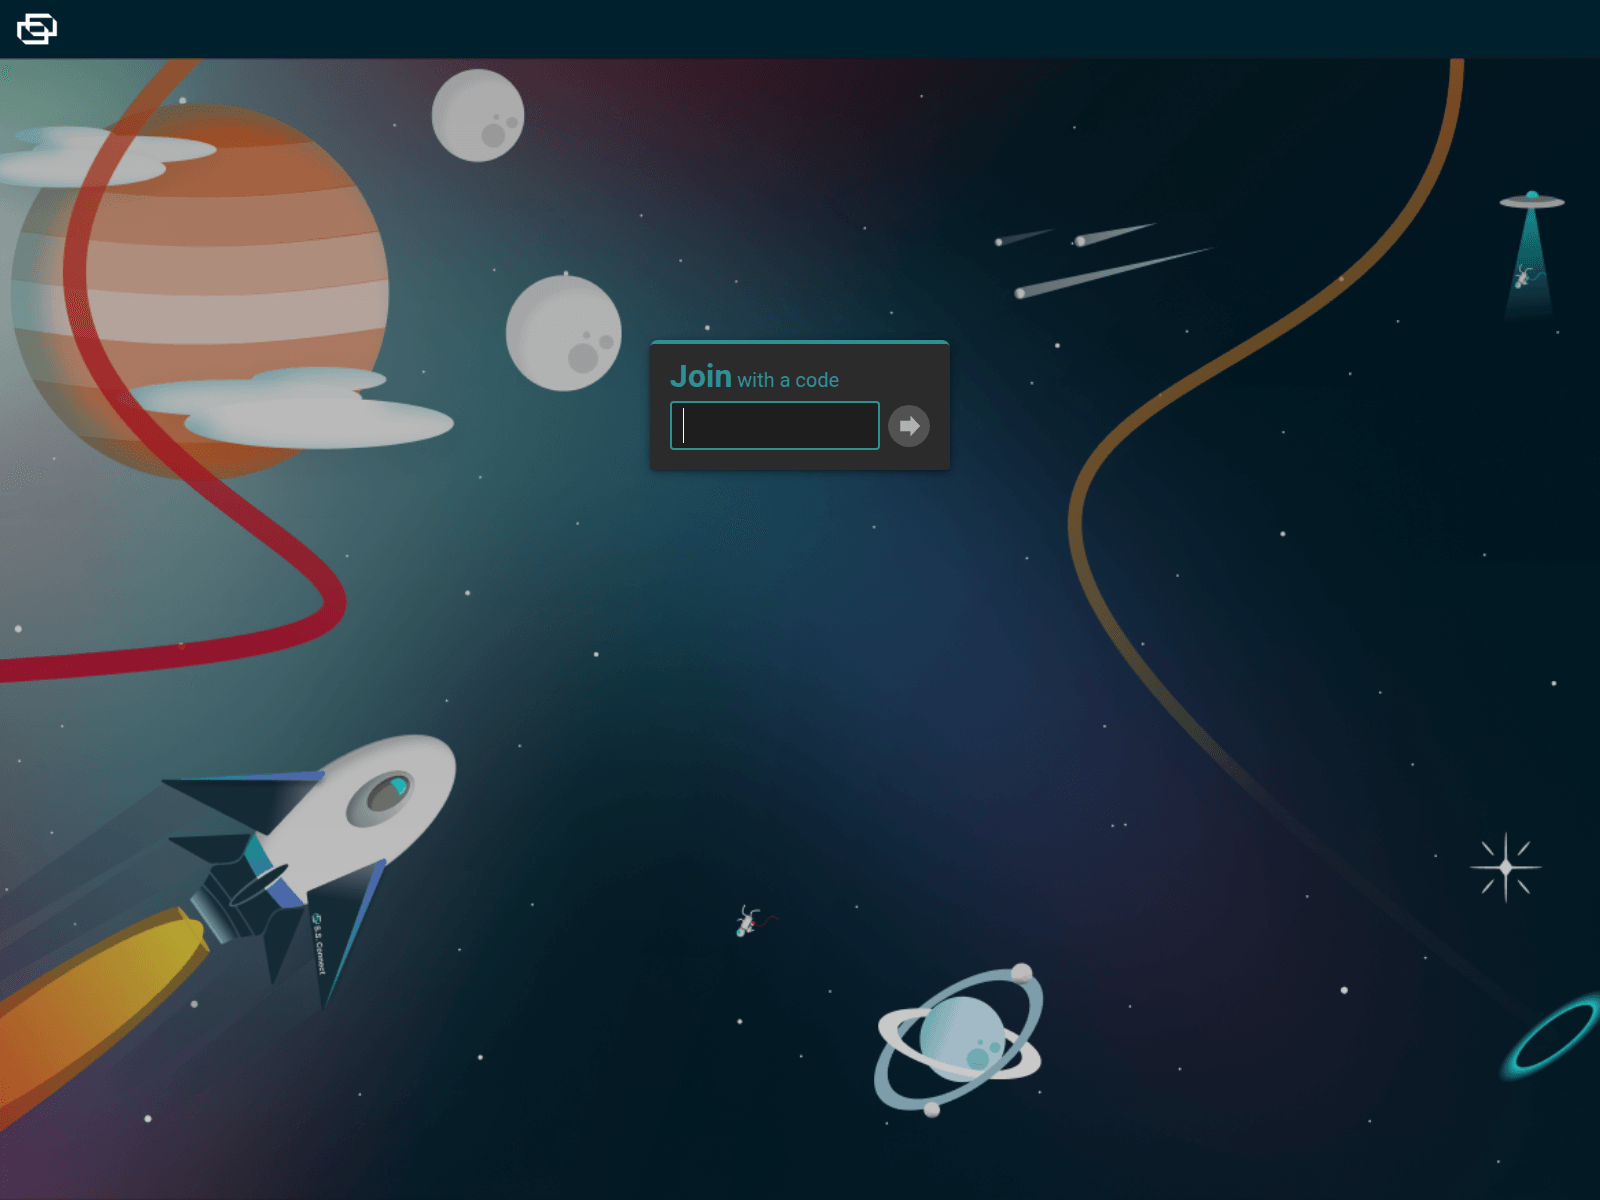
On 2026-11-09, ezn65t-h7.top displayed a space-themed page with a dark starry background featuring illustrated planets, a rocket, comets, and a UFO. Centered on the screen is a dark panel labeled "Join with a code" containing a text input field and a circular arrow button to submit the entered code. The panel sits against the illustrated backdrop, with a large ringed planet at the left, a smaller ringed planet below center, and a rocket ascending from the lower left corner.
URLScanによるキャプチャ · 2026-11-09 19:08 UTC · SHA-256 cff9692d…9623e95
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-11-09, ezn65t-h7.top displayed a space-themed page with a dark starry background featuring illustrated planets, a rocket, comets, and a UFO. Centered on the screen is a dark panel labeled "Join with a code" containing a text input field and a circular arrow button to submit the entered code. The panel sits against the illustrated backdrop, with a large ringed planet at the left, a smaller ringed planet below center, and a rocket ascending from the lower left corner.
The stored VirusTotal domain result reports 5 detections out of 92 engines. VIPRE reported "malware"; SOCRadar reported "suspicious".
ezn65t-h7.top: Space-Themed "Join with a code" Entry Page
AIによる説明
PhishDestroy records ezn65t-h7.top showing a space-themed page with a "Join with a code" entry field and submit arrow button on a starry background.
AIによる要約
On 2026-11-09, ezn65t-h7.top displayed a space-themed page with a dark starry background featuring illustrated planets, a rocket, comets, and a UFO. Centered on the screen is a dark panel labeled "Join with a code" containing a text input field and a circular arrow button to submit the entered code. The panel sits against the illustrated backdrop, with a large ringed planet at the left, a smaller ringed planet below center, and a rocket ascending from the lower left corner. The stored VirusTotal domain result reports 5 detections out of 92 engines. VIPRE reported "malware"; SOCRadar reported "suspicious".
Headers: Server: cloudflare; Content type: text/html; charset=utf-8; X content type options: nosniff
ネットワークセキュリティインテリジェンス レジストラの背景情報
レジストラの背景情報NameSilo
Stored registration data identifies NameSilo as the registrar. PhishDestroy maintains separate registrar investigations; that broader material is contextual and is not an independent detection for this domain.
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP登録
観測されたタイムラインlast reachable: 2026-11-11 11:34 UTClast content: 2026-11-11 11:34 UTCcurrent episode first observed: 2026-11-13 22:22 UTCobserved RIP window: 2026-11-11 11:34 UTC → 2026-11-13 22:22 UTC · 58.79hmidpoint estimate ≈ 2026-11-12 16:58 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 NameSilo
 104.21.9.238


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT