元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
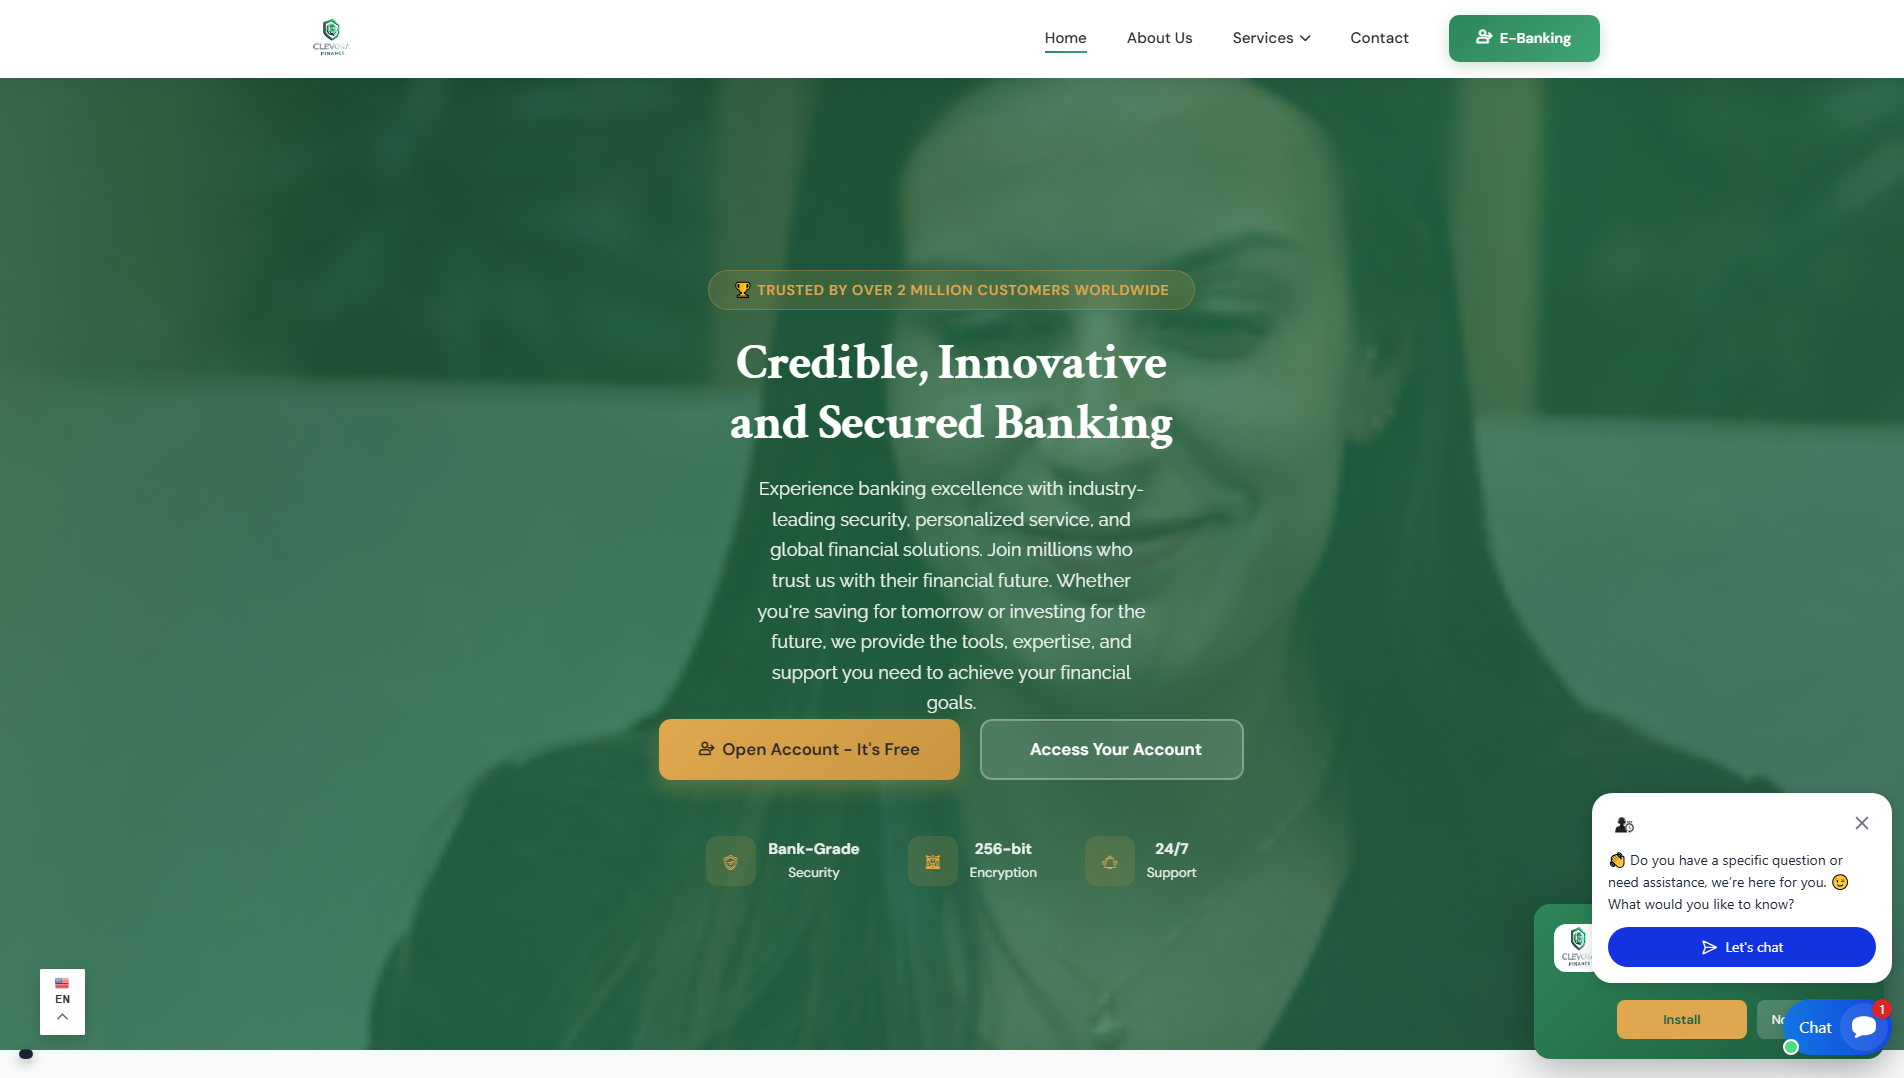
clevorafinance.com presented itself under the page title "Clevora finance", an impersonation phishing page built to look like a legitimate finance brand. It targeted people searching for or being steered toward Clevora Finance, especially investors and crypto users expecting a trustworthy platform. PhishDestroy first flagged it on 2026-08-30. The site has been offline since 2026-09-14, and as of 2026-10-19 its domain no longer resolves in DNS.
詐欺の手口
Impersonation pages like this copy the name, look and tone of a real or plausible finance service so visitors believe they are on the official site. Victims are typically pushed to sign up, log in or fund an account. Whatever they type, such as email, password, one-time codes and identity details, goes straight to the operators. Any money sent as a "deposit" or "investment" is gone, and follow-up demands for "verification" or "withdrawal fees" are a common way to extract more.
証拠
On 2026-09-12, 12 of 89 VirusTotal engines flagged the domain, including BitDefender, Fortinet, Forcepoint ThreatSeeker, G-Data, Gridinsoft, alphaMountain.ai, CyRadar and the Vietnamese anti-scam group Chong Lua Dao. That is a modest share, but these vendors reached the same verdict independently. Spamhaus lists the domain in its DBL as spam, and four AlienVault OTX threat pulses reference it, so other researchers tracked it too. The domain is also on the PhishDestroy blocklist.
インフラ
The domain was registered on 2026-05-24 through Realtime Register B.V., about three months before PhishDestroy caught it. That gap suggests it was prepared in advance rather than spun up on the day. It was hosted on OVH SAS infrastructure in Poland. Its Let's Encrypt certificate gave visitors a padlock, which only means the connection was encrypted and says nothing about who ran the site.
What to do
If you created an account or logged in, change that password everywhere you reused it and turn on app-based 2FA. If you sent money, contact your bank or exchange immediately and report the transfer. Treat anyone who later offers to "recover" your funds for a fee as a second scam. Defenders should block the domain, search mail and proxy logs for visits since 2026-05-24, and check whether staff or customers submitted credentials.
clevorafinance.com is an impersonation phishing page posing as Clevora Finance to steal logins, personal data and deposits from investors and crypto users.
AIによる要約
Overview clevorafinance.com presented itself under the page title "Clevora finance", an impersonation phishing page built to look like a legitimate finance brand. It targeted people searching for or being steered toward Clevora Finance, especially investors and crypto users expecting a trustworthy platform. PhishDestroy first flagged it on 2026-08-30. The site has been offline since 2026-09-14, and as of 2026-10-19 its domain no longer resolves in DNS. How the scam works Impersonation pages like this copy the name, look and tone of a real or plausible finance service so visitors believe they are on the official site. Victims are typically pushed to sign up, log in or fund an account. Whatever they type, such as email, password, one-time codes and identity details, goes straight to the operators. Any money sent as a "deposit" or "investment" is gone, and follow-up demands for "verification" or "withdrawal fees" are a common way to extract more. Evidence On 2026-09-12, 12 of 89 VirusTotal engines flagged the domain, including BitDefender, Fortinet, Forcepoint ThreatSeeker, G-Data, Gridinsoft, alphaMountain.ai, CyRadar and the Vietnamese anti-scam group Chong Lua Dao. That is a modest share, but these vendors reached the same verdict independently. Spamhaus lists the domain in its DBL as spam, and four AlienVault OTX threat pulses reference it, so other researchers tracked it too. The domain is also on the PhishDestroy blocklist. Infrastructure The domain was registered on 2026-05-24 through Realtime Register B.V., about three months before PhishDestroy caught it. That gap suggests it was prepared in advance rather than spun up on the day. It was hosted on OVH SAS infrastructure in Poland. Its Let's Encrypt certificate gave visitors a padlock, which only means the connection was encrypted and says nothing about who ran the site. What to do If you created an account or logged in, change that password everywhere you reused it and turn on app-based 2FA. If you sent money, contact your bank or exchange immediately and report the transfer. Treat anyone who later offers to "recover" your funds for a fee as a second scam. Defenders should block the domain, search mail and proxy logs for visits since 2026-05-24, and check whether staff or customers submitted credentials. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a05071-2989-76f7-a810-f602ee108e32/ VirusTotal report: https://www.virustotal.com/gui/domain/clevorafinance.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=clevorafinance.com Archived copy: https://web.archive.org/web/20260830021525/https://clevorafinance.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP登録
観測されたタイムラインlast reachable: 2026-09-13 22:17 UTCcurrent episode first observed: 2026-09-30 16:14 UTCobserved RIP window: 2026-09-13 22:17 UTC → 2026-09-30 16:14 UTC · 401.95hmidpoint estimate ≈ 2026-09-22 07:16 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 51.68.132.246


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT