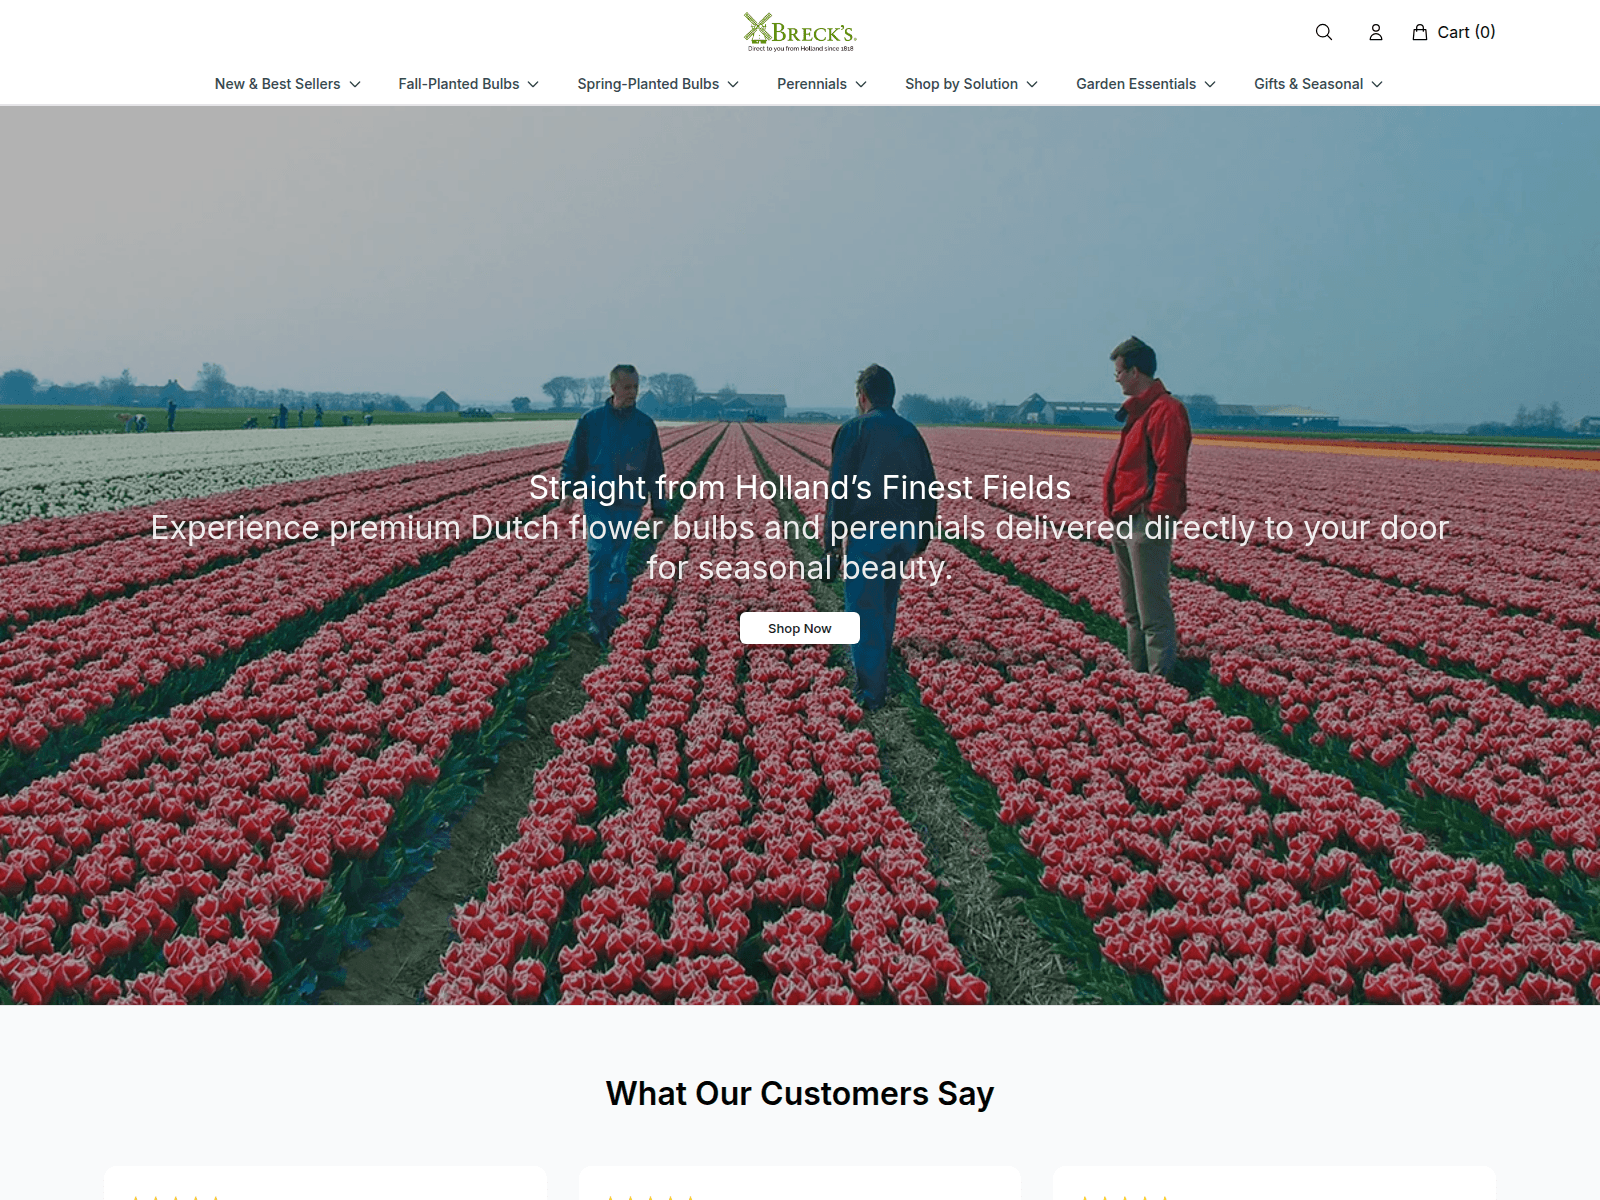
On 2026-10-02, brecksshop.shop was captured showing a storefront homepage branded with the Breck's logo and the tagline "Direct to you from Holland since 1886." The page features a large hero image of a tulip field with the headline "Straight from Holland's Finest Fields," describing premium Dutch flower bulbs and perennials delivered to the door, alongside a "Shop Now" button. Navigation categories include bulbs, perennials, garden essentials, and gifts, with a cart indicator showing zero items.
分析は英語でのみ利用可能です
ページタイトル: “Flower Bulbs - Dutch Bulbs Since 1818 | Breck's”
URLScanによるキャプチャ · 2026-10-02 16:20 UTC · SHA-256 99ad1e96…632213c
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-10-02, brecksshop.shop was captured showing a storefront homepage branded with the Breck's logo and the tagline "Direct to you from Holland since 1886." The page features a large hero image of a tulip field with the headline "Straight from Holland's Finest Fields," describing premium Dutch flower bulbs and perennials delivered to the door, alongside a "Shop Now" button. Navigation categories include bulbs, perennials, garden essentials, and gifts, with a cart indicator showing zero items.
The stored VirusTotal domain result reports 3 detections out of 92 engines. SOCRadar reported "suspicious"; Gridinsoft reported "suspicious".
brecksshop.shop: Recorded Dutch Flower Bulb Storefront Homepage
AIによる説明
PhishDestroy records the captured homepage of brecksshop.shop, showing a Breck's-branded storefront offering Dutch flower bulbs and perennials.
AIによる要約
On 2026-10-02, brecksshop.shop was captured showing a storefront homepage branded with the Breck's logo and the tagline "Direct to you from Holland since 1886." The page features a large hero image of a tulip field with the headline "Straight from Holland's Finest Fields," describing premium Dutch flower bulbs and perennials delivered to the door, alongside a "Shop Now" button. Navigation categories include bulbs, perennials, garden essentials, and gifts, with a cart indicator showing zero items. The stored VirusTotal domain result reports 3 detections out of 92 engines. SOCRadar reported "suspicious"; Gridinsoft reported "suspicious".
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:23 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:23 UTClast content: 2026-11-22 11:23 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 Dynadot
 185.234.12.89


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT