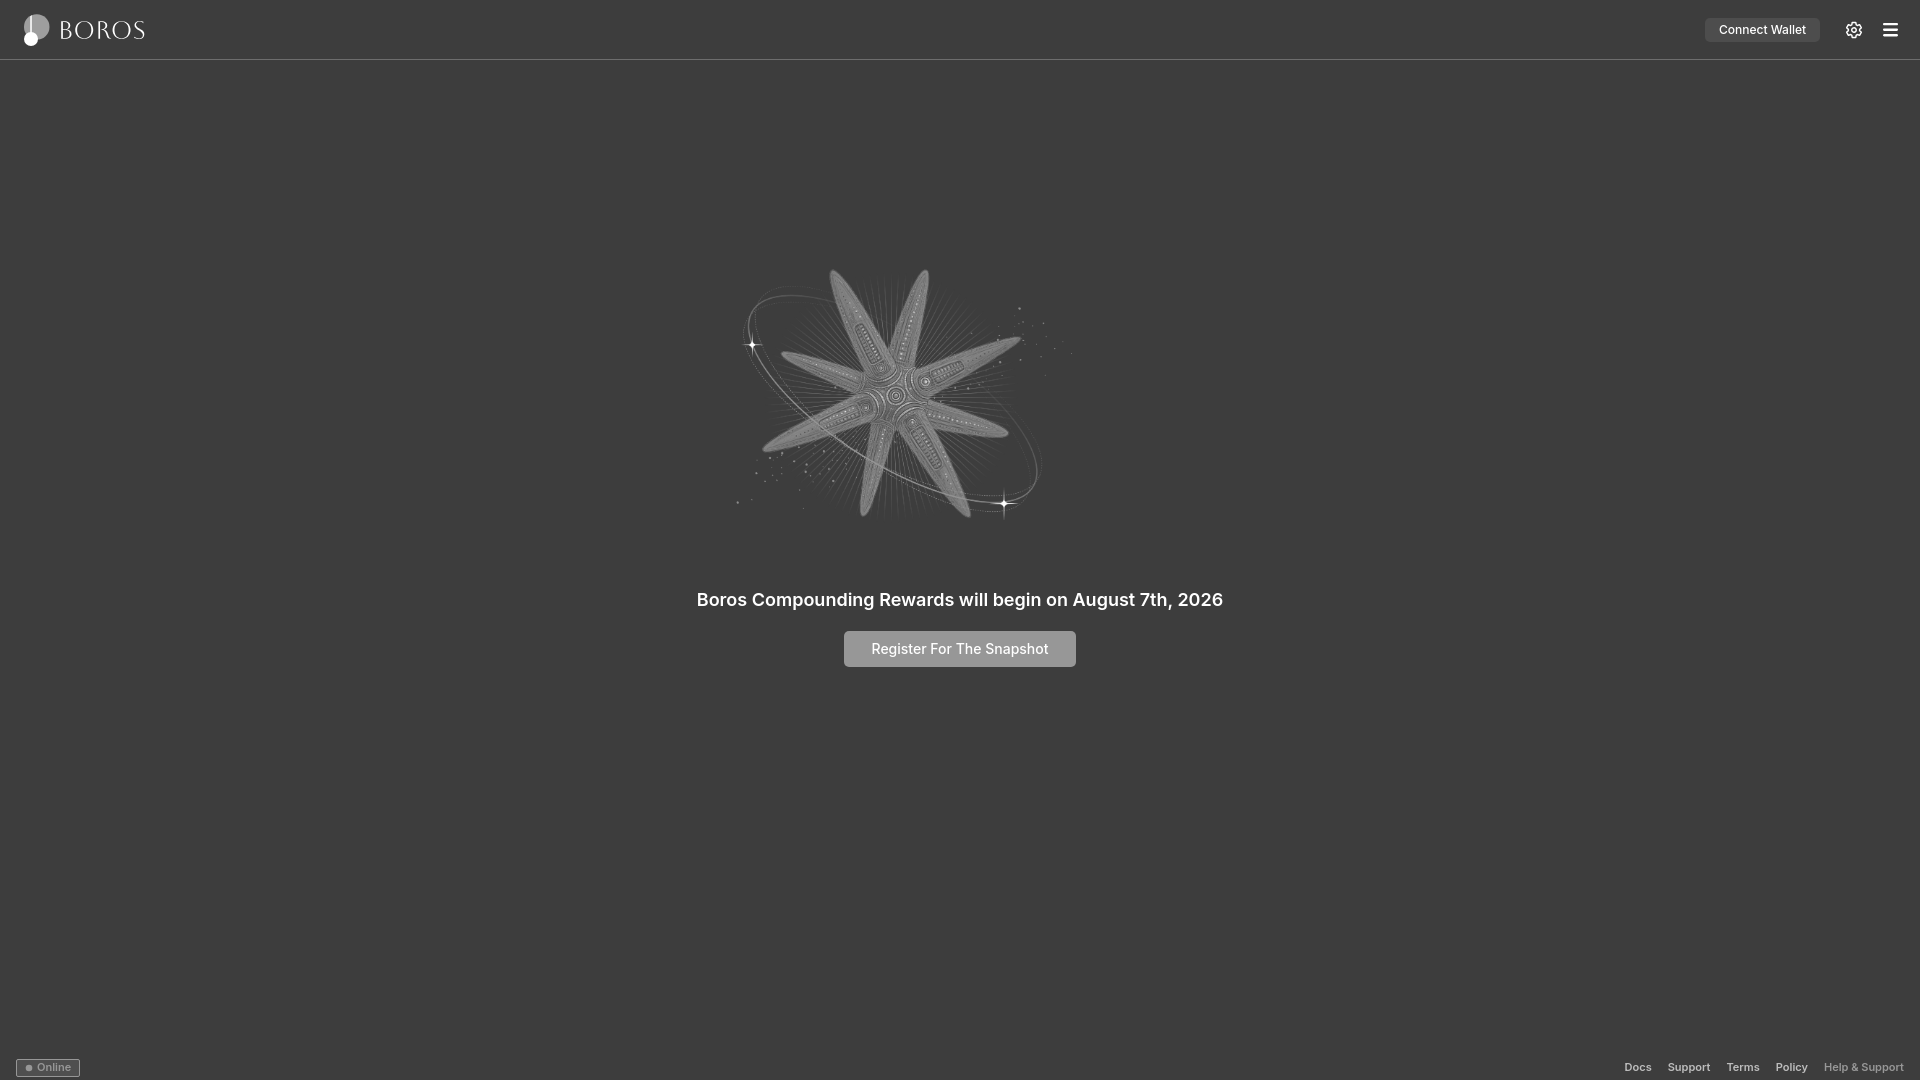
On 2026-07-22, borosfi-pendle.finance displayed a dark-themed page branded "BOROS" in the header, alongside a Connect Wallet button and a settings icon. The main area features a large ornamental star-like graphic centered on the screen, beneath which the page states that Boros Compounding Rewards will begin on August 7th, 2026. A "Register For The Snapshot" button sits directly below that announcement, and footer links for Docs, Support, Terms, Policy, and Help & Support are visible at the bottom.
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-07-22, borosfi-pendle.finance displayed a dark-themed page branded "BOROS" in the header, alongside a Connect Wallet button and a settings icon. The main area features a large ornamental star-like graphic centered on the screen, beneath which the page states that Boros Compounding Rewards will begin on August 7th, 2026. A "Register For The Snapshot" button sits directly below that announcement, and footer links for Docs, Support, Terms, Policy, and Help & Support are visible at the bottom.
The stored VirusTotal domain result reports 14 detections out of 92 engines. Bkav reported "malicious"; VIPRE reported "phishing".
borosfi-pendle.finance: Recorded Boros Compounding Rewards Snapshot Page
AIによる説明
PhishDestroy records borosfi-pendle.finance showing a Boros page announcing compounding rewards beginning August 7th, 2026 with a snapshot registration button.
AIによる要約
On 2026-07-22, borosfi-pendle.finance displayed a dark-themed page branded "BOROS" in the header, alongside a Connect Wallet button and a settings icon. The main area features a large ornamental star-like graphic centered on the screen, beneath which the page states that Boros Compounding Rewards will begin on August 7th, 2026. A "Register For The Snapshot" button sits directly below that announcement, and footer links for Docs, Support, Terms, Policy, and Help & Support are visible at the bottom. The stored VirusTotal domain result reports 14 detections out of 92 engines. Bkav reported "malicious"; VIPRE reported "phishing".
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
出典NICENIC INTERNATIONAL GROUP CO., LIMITEDmechanism: Registrar clientHoldsource: Rdap Status Collector
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAINRegistration: Registrar clientHold
RDAP登録レジストラのclientHoldNICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765RDAP HTTP 200source: Rdap Status CollectorclientDeleteProhibitedclientHoldclientTransferProhibitedexpires 2027-07-22 13:41 UTCチェック済み 2026-11-22 07:47 UTC
レジストラのアクションマーカー検証済みclientHoldマーカーNICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765当報告書との因果関係は立証されていない
観測されたタイムラインlast reachable: 2026-08-02 22:14 UTCcurrent episode first observed: 2026-08-05 01:45 UTCobserved RIP window: 2026-08-02 22:14 UTC → 2026-08-05 01:45 UTC · 51.53hmidpoint estimate ≈ 2026-08-03 23:59 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 NiceNIC
 104.21.51.49


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT