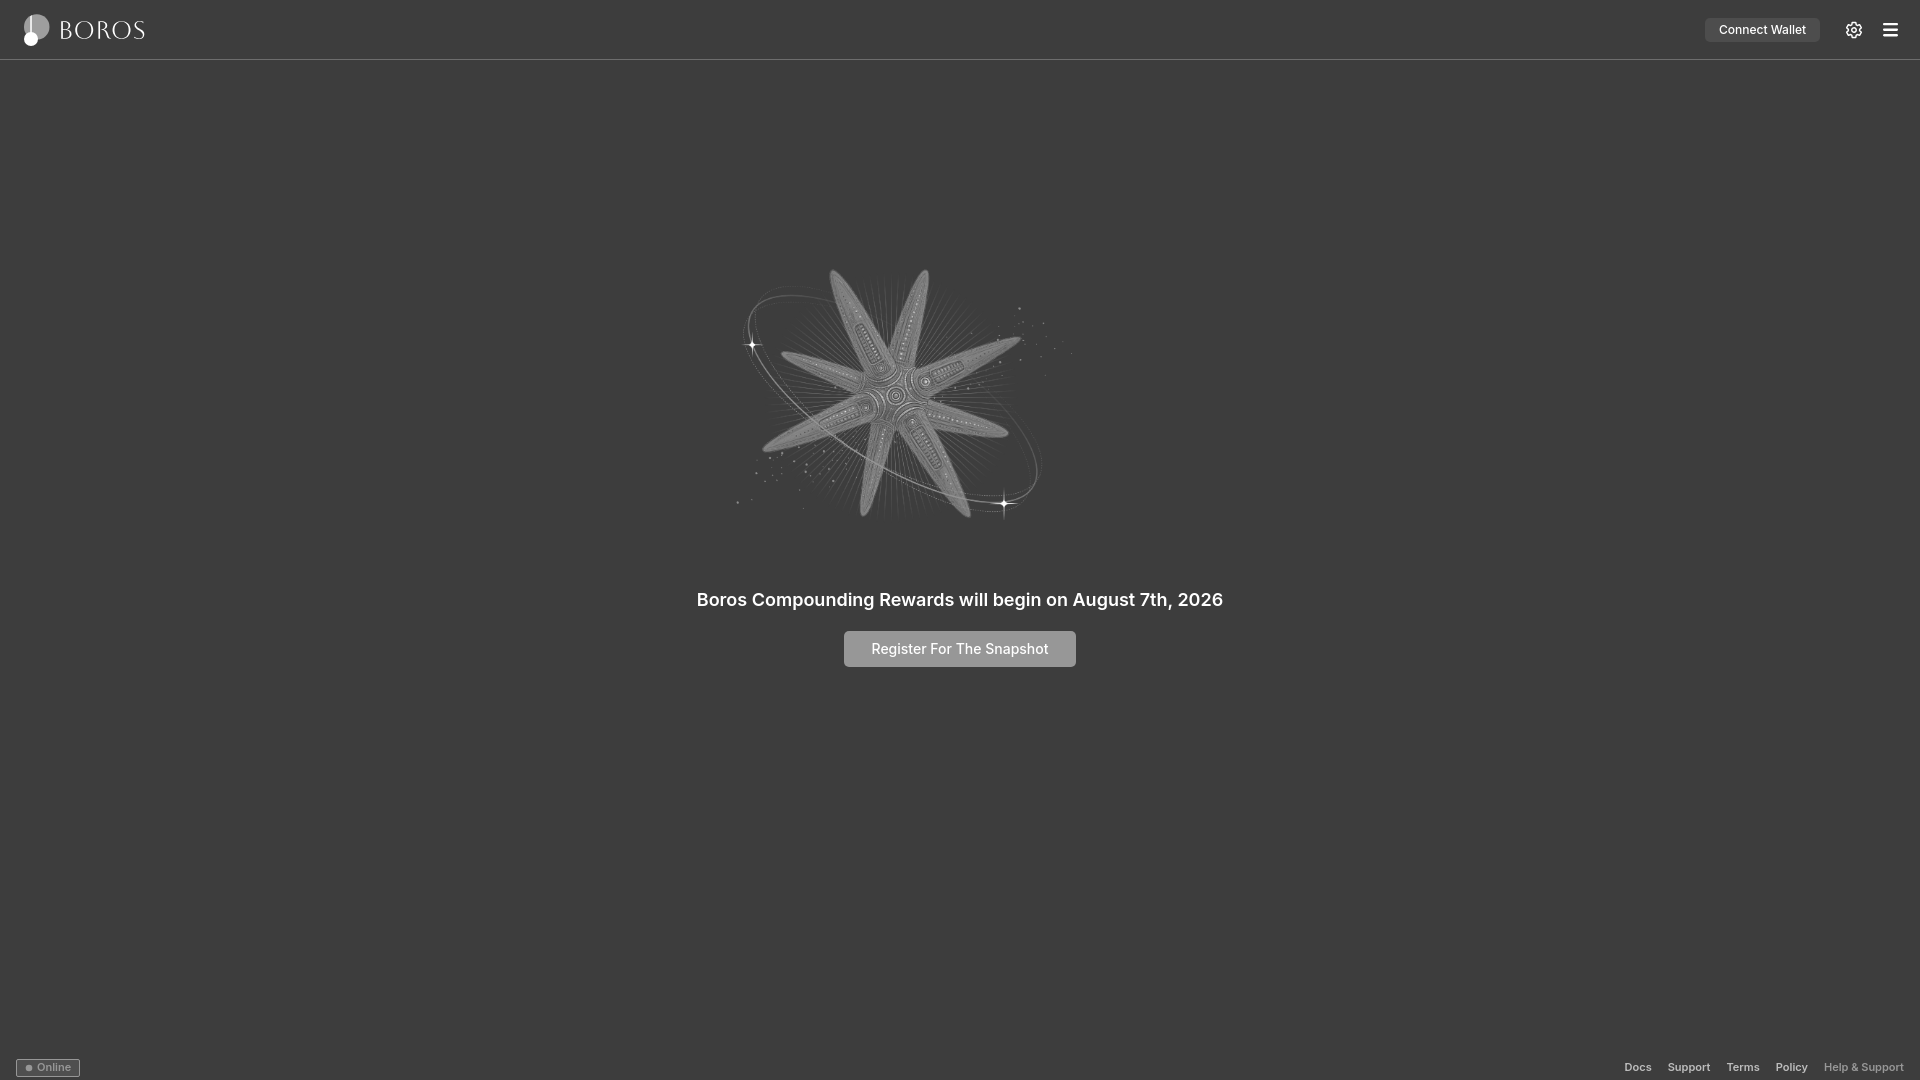
The captured page for boros-pendle.finance presents a rewards interface indicating that Boros Compounding Rewards will begin on August 7th, 2026. Central elements include a notice about the upcoming schedule and a prominent button to register for the snapshot. This visual capture documents the stated promotional layout and user interaction options available during the historical recording.
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
The captured page for boros-pendle.finance presents a rewards interface indicating that Boros Compounding Rewards will begin on August 7th, 2026. Central elements include a notice about the upcoming schedule and a prominent button to register for the snapshot. This visual capture documents the stated promotional layout and user interaction options available during the historical recording.
In the stored VirusTotal analysis from October 15, 2026, the domain scope result reports 14 detections out of 92 security vendors. Representative engines flagged the target, with Kaspersky labeling it as phishing, CRDF marking it as malicious, and VIPRE identifying it as phishing. These findings provide baseline security context from the recorded scan date without implying current active behavior.
Examine boros-pendle.finance through PhishDestroy to review its recorded compounding rewards interface and associated security metrics.
AIによる要約
The captured page for boros-pendle.finance presents a rewards interface indicating that Boros Compounding Rewards will begin on August 7th, 2026. Central elements include a notice about the upcoming schedule and a prominent button to register for the snapshot. This visual capture documents the stated promotional layout and user interaction options available during the historical recording. In the stored VirusTotal analysis from October 15, 2026, the domain scope result reports 14 detections out of 92 security vendors. Representative engines flagged the target, with Kaspersky labeling it as phishing, CRDF marking it as malicious, and VIPRE identifying it as phishing. These findings provide baseline security context from the recorded scan date without implying current active behavior.
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.

 NiceNIC
 62.60.226.88


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT