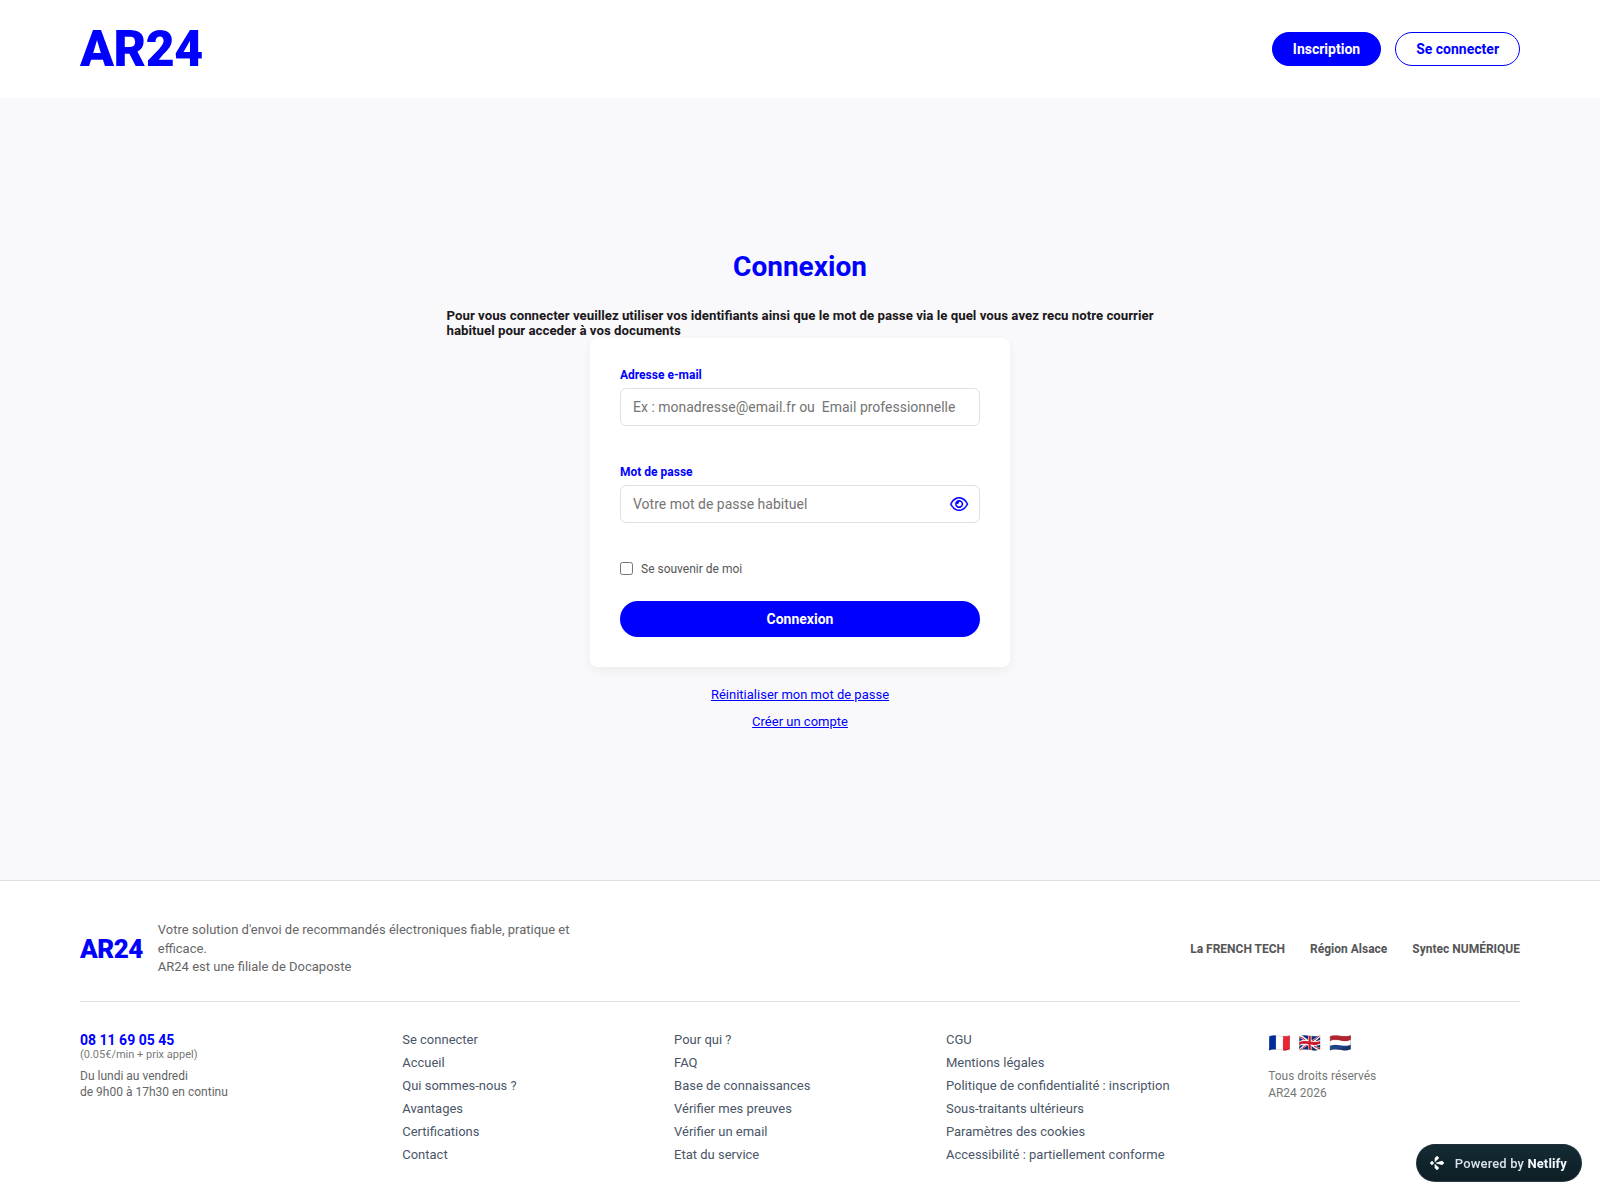
This site mimics the AR24 electronic registered mail portal to harvest email addresses and passwords through a fraudulent login form. If you entered your credentials here, immediately update your login details on the genuine service and secure any linked accounts.
URLScanによるキャプチャ · 2026-11-21 17:40 UTC · SHA-256 ad1be0c6…6bd06de
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
AR24 login page clone
The page on ar24courrielfr0.netlify.app presents a clean, blue-themed login interface replicating the AR24 electronic registered mail service in French. At the top, it displays the AR24 logo alongside registration and connection buttons, while the main container features a large header saying "Connexion" and explanatory text reading "Pour vous connecter veuillez utiliser vos identifiants ainsi que le mot de passe via le quel vous avez reçu notre courrier habituel pour acceder à vos documents". Below this text, the form includes input fields for "Adresse e-mail" with a placeholder example and "Mot de passe" equipped with a visibility toggle icon. A checkbox for "Se souvenir de moi" sits above a prominent blue button labeled "Connexion", accompanied by links for password reset and account creation. The footer lists standard company information, customer support phone numbers, legal links, and it still answered requests on 21 Nov 2026 at 18:41 UTC.
Credential harvesting and telemetry
The primary objective of this page is credential theft, as it captures the email address and password entered into the form fields. Vendors such as Kaspersky, ESET and BitDefender classify the URL as a credential harvesting phishing threat, while urlscan classified the page as malicious, VirusTotal showed 17 of 92 engines flagging it on 20 Nov 2026, and PhishFeed blocks it. Furthermore, PhishDestroy scores the evidence against it at 75/100 (critical).
Recommended actions for visitors
Visitors who have entered their email and password into this form face immediate risk of account compromise. You should immediately update your credentials on the genuine AR24 platform and check all linked email accounts for unauthorized access. Never enter sensitive details on subdomains hosted on third-party platforms like netlify.app when dealing with official services.
ar24courrielfr0.netlify.app presented a fake AR24 login interface to harvest emails and passwords, flagged by urlscan and 17 VirusTotal engines. Do not log in.
AIによる要約
AR24 login page clone The page on ar24courrielfr0.netlify.app presents a clean, blue-themed login interface replicating the AR24 electronic registered mail service in French. At the top, it displays the AR24 logo alongside registration and connection buttons, while the main container features a large header saying "Connexion" and explanatory text reading "Pour vous connecter veuillez utiliser vos identifiants ainsi que le mot de passe via le quel vous avez reçu notre courrier habituel pour acceder à vos documents". Below this text, the form includes input fields for "Adresse e-mail" with a placeholder example and "Mot de passe" equipped with a visibility toggle icon. A checkbox for "Se souvenir de moi" sits above a prominent blue button labeled "Connexion", accompanied by links for password reset and account creation. The footer lists standard company information, customer support phone numbers, legal links, and it still answered requests on 21 Nov 2026 at 18:41 UTC. Credential harvesting and telemetry The primary objective of this page is credential theft, as it captures the email address and password entered into the form fields. Vendors such as Kaspersky, ESET and BitDefender classify the URL as a credential harvesting phishing threat, while urlscan classified the page as malicious, VirusTotal showed 17 of 92 engines flagging it on 20 Nov 2026, and PhishFeed blocks it. Furthermore, PhishDestroy scores the evidence against it at 75/100 (critical). Recommended actions for visitors Visitors who have entered their email and password into this form face immediate risk of account compromise. You should immediately update your credentials on the genuine AR24 platform and check all linked email accounts for unauthorized access. Never enter sensitive details on subdomains hosted on third-party platforms like netlify.app when dealing with official services.
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Stale
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:59 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:59 UTClast content: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 63.176.8.218


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT