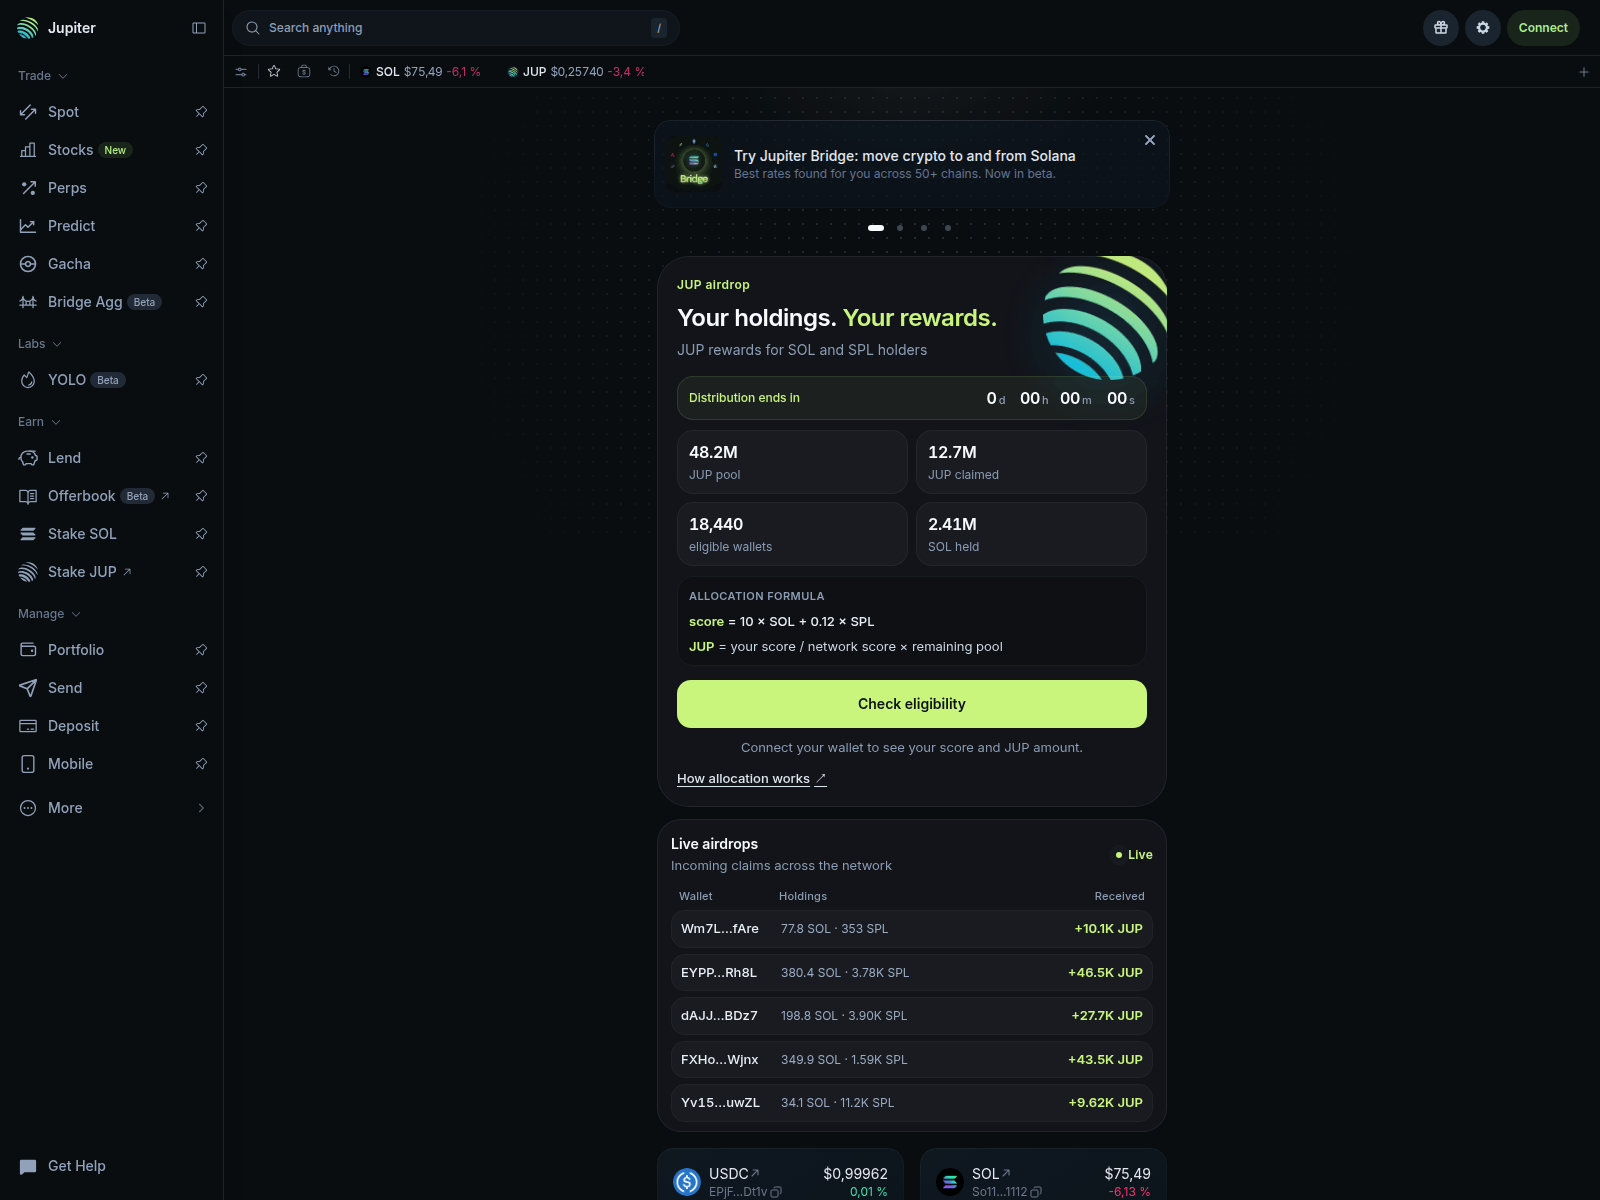
On 2026-11-14, appeals-grvt.com displayed a dark-themed page branded with a Jupiter logo and a left sidebar listing trading, earning and portfolio options. The main panel is headed "JUP airdrop" with the text "Your holdings. Your rewards." and describes JUP rewards for SOL and SPL holders, alongside a countdown, pool statistics and an allocation formula. A "Check eligibility" button invites users to connect a wallet to see their score and JUP amount, and a "Live airdrops" section lists incoming claims across the network.
URLScanによるキャプチャ · 2026-11-14 07:16 UTC · SHA-256 19bad62a…273d2bb
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-11-14, appeals-grvt.com displayed a dark-themed page branded with a Jupiter logo and a left sidebar listing trading, earning and portfolio options. The main panel is headed "JUP airdrop" with the text "Your holdings. Your rewards." and describes JUP rewards for SOL and SPL holders, alongside a countdown, pool statistics and an allocation formula. A "Check eligibility" button invites users to connect a wallet to see their score and JUP amount, and a "Live airdrops" section lists incoming claims across the network.
The stored VirusTotal domain result reports 9 detections out of 92 engines. CRDF reported "malicious"; G-Data reported "phishing".
appeals-grvt.com: Recorded JUP airdrop eligibility page with wallet connection
AIによる説明
PhishDestroy records appeals-grvt.com showing a JUP airdrop eligibility page with a wallet connection prompt and live claim listings, captured 2026-11-14.
AIによる要約
On 2026-11-14, appeals-grvt.com displayed a dark-themed page branded with a Jupiter logo and a left sidebar listing trading, earning and portfolio options. The main panel is headed "JUP airdrop" with the text "Your holdings. Your rewards." and describes JUP rewards for SOL and SPL holders, alongside a countdown, pool statistics and an allocation formula. A "Check eligibility" button invites users to connect a wallet to see their score and JUP amount, and a "Live airdrops" section lists incoming claims across the network. The stored VirusTotal domain result reports 9 detections out of 92 engines. CRDF reported "malicious"; G-Data reported "phishing".
Registrar: NICENIC INTERNATIONAL GROUP CO., LIMITED; Created: 2026-07-30T14:02:37Z; Updated: 2026-07-30T14:02:37Z; Expires: 2027-07-30T14:02:37Z; Status: clientDeleteProhibited https://icann.org/epp, clientTransferProhibited https://icann.org/epp; Nameservers: ns3.my-ndns.com, ns4.my-ndns.com
ネットワークセキュリティインテリジェンス レジストラの背景情報
レジストラの背景情報NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAINRegistration: Active
RDAP登録アクティブNICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765RDAP HTTP 200source: Rdap Status CollectorclientDeleteProhibitedclientTransferProhibitedexpires 2027-07-30 14:02 UTCチェック済み 2026-11-15 06:10 UTC
観測されたタイムラインlast reachable: 2026-11-18 12:02 UTClast content: 2026-11-18 05:35 UTCcurrent episode first observed: 2026-11-19 06:03 UTCobserved RIP window: 2026-11-18 12:02 UTC → 2026-11-19 06:03 UTC · 18.02hmidpoint estimate ≈ 2026-11-18 21:02 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.