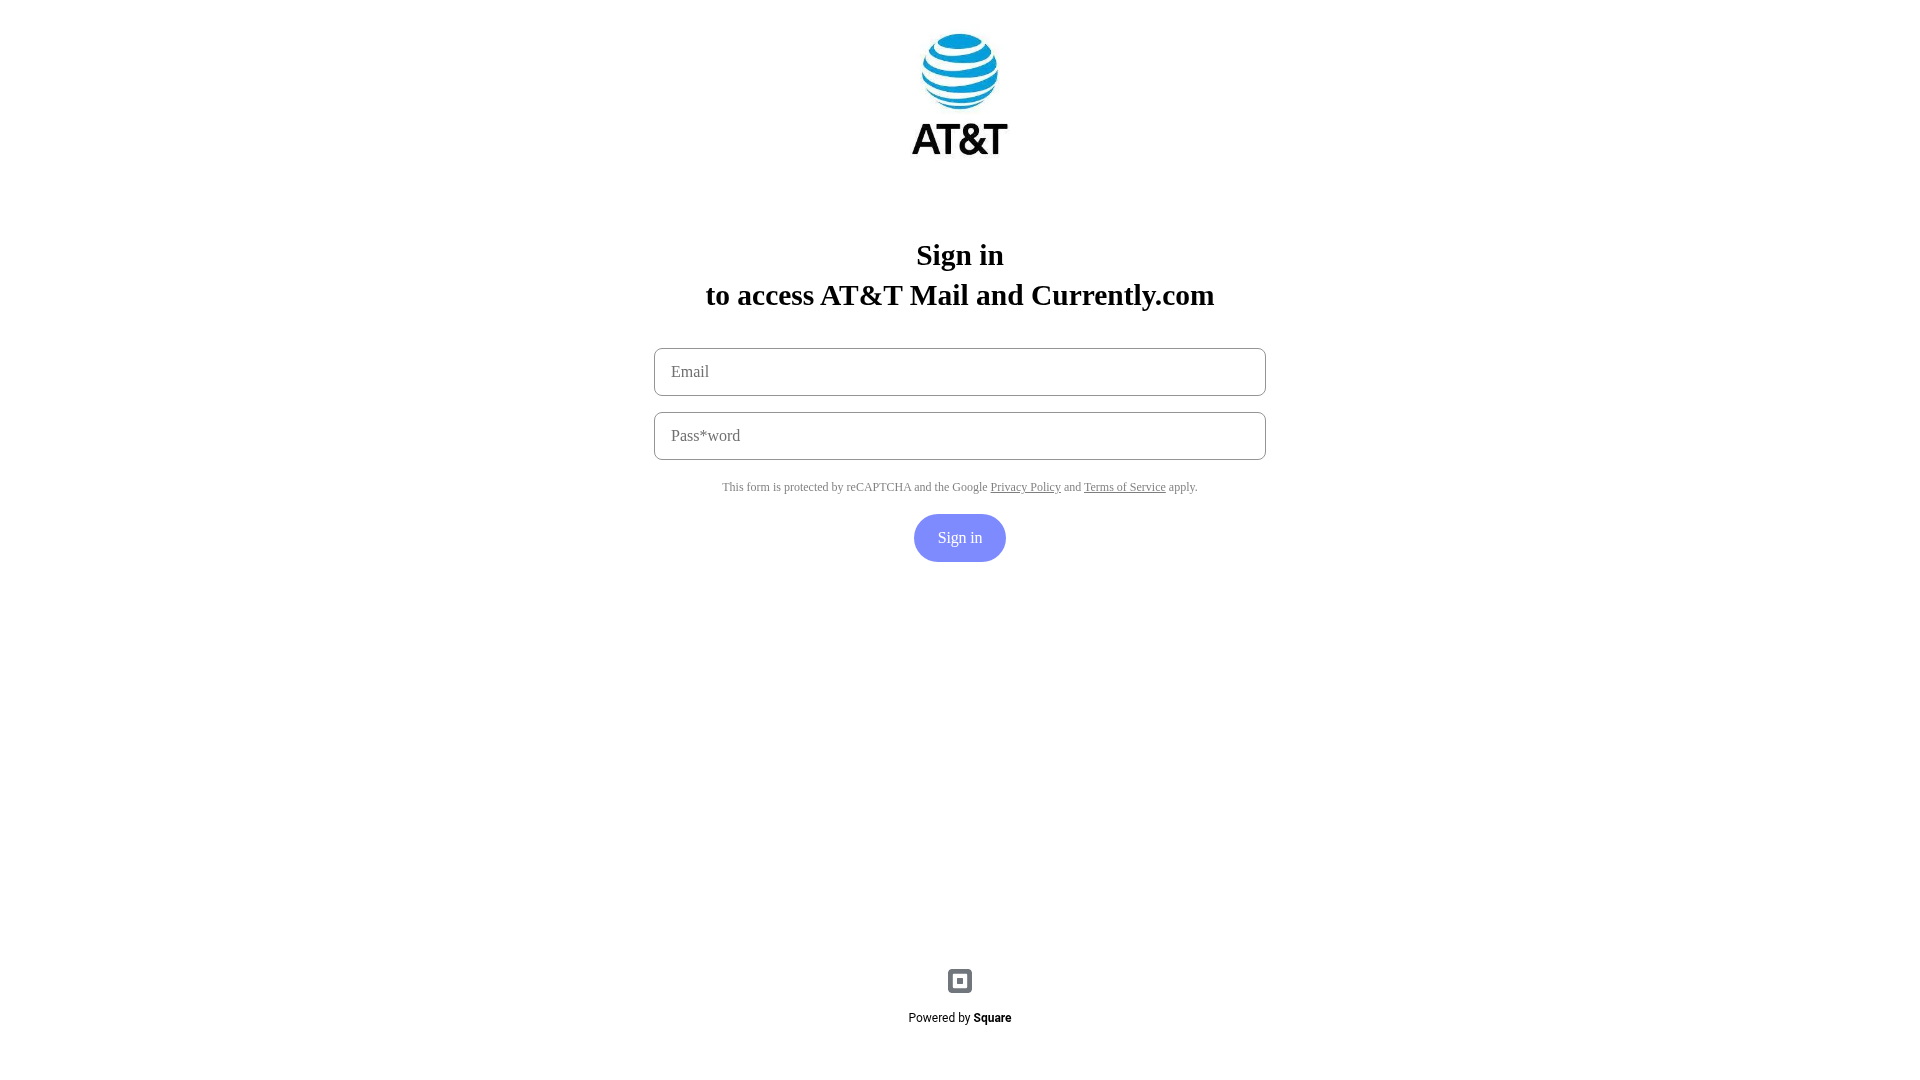
The page on ameribel-100067.square.site displays an AT&T login portal asking visitors to enter their email address and password. Anyone who has typed their credentials into this form should immediately change their password on the real AT&T account.
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
AT&T sign-in form hosted on the Square platform
The page displays the blue globe logo of AT&T at the top, centered directly above the brand name "AT&T". The central area contains two input fields labeled "Email" and "Pass*word". Underneath the input boxes, small text notes that the form is protected by reCAPTCHA, and a blue button labeled "Sign in" sits near the bottom. At the very footer, a small Square icon and the text "Powered by Square" appear, indicating the underlying tenant infrastructure.
Independent security analysis and threat telemetry
urlscan classified the page as malicious, and 21 of 92 VirusTotal engines flagged it on 20 Nov 2026. Kaspersky, ESET and BitDefender are among the engines that flag the site, while PhishDestroy's evidence score for it is 60/100 (high). These metrics demonstrate that the credential collection form is actively tracked by multiple independent analysis platforms.
Where credential harvesting portals lead
Pages mimicking major mail providers are designed to intercept login credentials submitted by unsuspecting visitors. Once a user inputs their email and password into the form fields, those credentials are transmitted directly to the operators behind the site. Attackers typically use harvested access details to compromise real accounts, access personal correspondence, or launch secondary attacks against associated services.
Recommended actions for affected visitors
Anyone who entered credentials on this page should immediately navigate to the official AT&T website to update their password. Review account settings for any unauthorized changes or forwarding rules established by external parties. Avoid reusing the same password across multiple online services to limit the impact of credential theft.
ameribel-100067.square.site displays an AT&T sign-in portal requesting email credentials, flagged by urlscan and 21 VirusTotal engines.
AIによる要約
AT&T sign-in form hosted on the Square platform The page displays the blue globe logo of AT&T at the top, centered directly above the brand name "AT&T". The central area contains two input fields labeled "Email" and "Pass*word". Underneath the input boxes, small text notes that the form is protected by reCAPTCHA, and a blue button labeled "Sign in" sits near the bottom. At the very footer, a small Square icon and the text "Powered by Square" appear, indicating the underlying tenant infrastructure. Independent security analysis and threat telemetry urlscan classified the page as malicious, and 21 of 92 VirusTotal engines flagged it on 20 Nov 2026. Kaspersky, ESET and BitDefender are among the engines that flag the site, while PhishDestroy's evidence score for it is 60/100 (high). These metrics demonstrate that the credential collection form is actively tracked by multiple independent analysis platforms. Where credential harvesting portals lead Pages mimicking major mail providers are designed to intercept login credentials submitted by unsuspecting visitors. Once a user inputs their email and password into the form fields, those credentials are transmitted directly to the operators behind the site. Attackers typically use harvested access details to compromise real accounts, access personal correspondence, or launch secondary attacks against associated services. Recommended actions for affected visitors Anyone who entered credentials on this page should immediately navigate to the official AT&T website to update their password. Review account settings for any unauthorized changes or forwarding rules established by external parties. Avoid reusing the same password across multiple online services to limit the impact of credential theft.


 74.115.51.5


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT