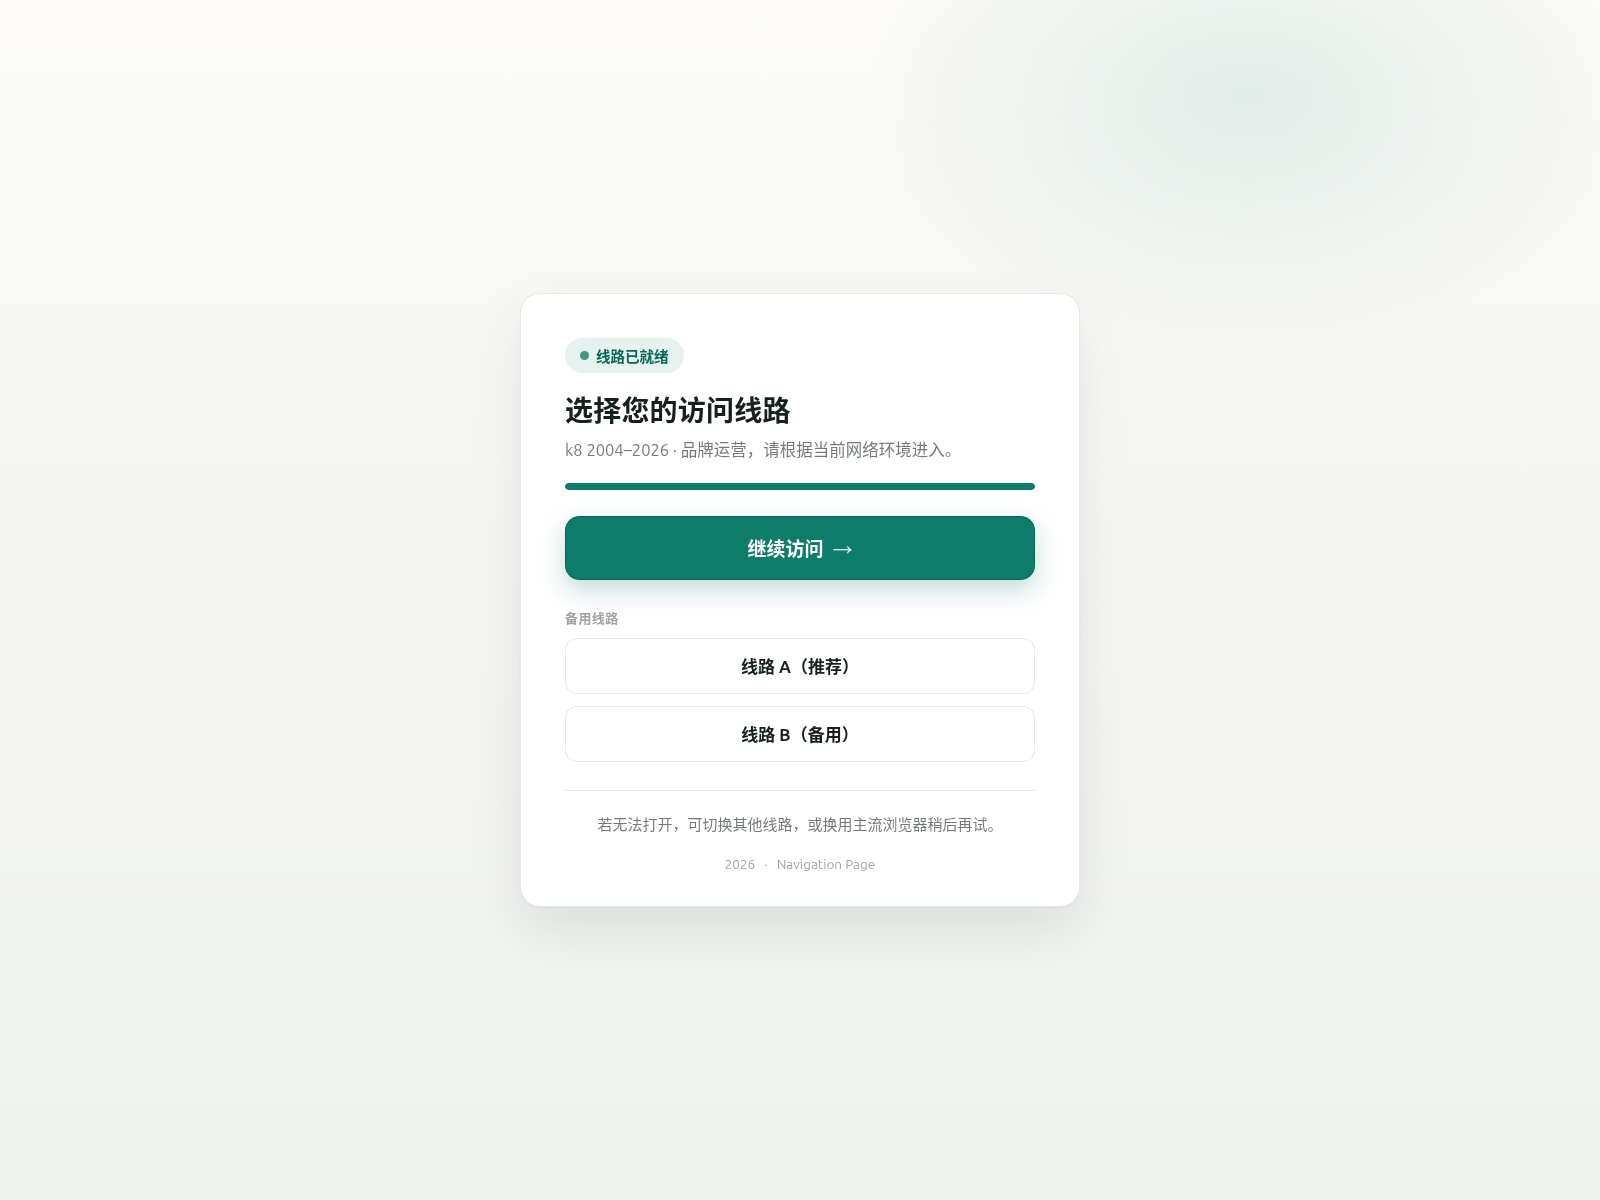
This site displays a Chinese language routing page asking visitors to select an access path. 4 of 92 VirusTotal engines flagged it on 19 Nov 2026, with Webroot, CRDF and SOCRadar flagging the domain as a potential risk.
URLScanによるキャプチャ · 2026-11-21 18:39 UTC · SHA-256 add11880…9cf56f0
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Minimalist Chinese language routing page layout
The page displays a clean, minimalist card interface in Chinese that prompts visitors to choose an access path. At the top, a small tag reads "线路已就绪" indicating routes are ready, while the main headline states "选择您的访问线路". Below this, subtext mentions "k8 2004-2026 · 品牌迵营" alongside a prominent button reading "继续访闧 →". Alternative options appear further down as "线路 A (推荐)" and "线路 B (备用)" for secondary routing. The footer advises users to switch browsers if links fail, concluding with a "2026 · Navigation Page" label.
Registration timeline and independent detections
It was registered on 10 Nov 2026, 11 days before it was first reported, which provides very little operating history for a navigation portal claiming years of operation. Because 4 of 92 VirusTotal engines flagged it on 19 Nov 2026, with Webroot, CRDF and SOCRadar among the flagging engines, this page is tracked by independent security scanners as a potential risk rather than an isolated false alarm.
Where navigation routing pages lead
Routing portals of this kind typically act as distribution hubs or front-ends designed to redirect visitors toward frequently changing secondary servers or external destinations. Following these links can expose your browser to unverified third-party content, malicious downloads, or secondary phishing campaigns. Always verify the ultimate destination address before trusting external links provided by unknown routing pages.
Precautions and recommended actions
Simply close the browser tab if you only viewed the page and did not interact with any links. If you clicked through the route buttons and downloaded files or entered credentials on subsequent destinations, scan your device immediately and change any compromised passwords. Report suspicious domains directly to their registrar, Key-Systems GmbH, or relevant hosting abuse contacts.
2566l5.com — Chinese access path selection card interface
AIによる説明
2566l5.com presents a Chinese routing page offering multiple access paths, flagged by 4 VirusTotal engines. Exercise caution with external routing links.
AIによる要約
Minimalist Chinese language routing page layout The page displays a clean, minimalist card interface in Chinese that prompts visitors to choose an access path. At the top, a small tag reads "线路已就绪" indicating routes are ready, while the main headline states "选择您的访问线路". Below this, subtext mentions "k8 2004-2026 · 品牌迵营" alongside a prominent button reading "继续访闧 →". Alternative options appear further down as "线路 A (推荐)" and "线路 B (备用)" for secondary routing. The footer advises users to switch browsers if links fail, concluding with a "2026 · Navigation Page" label. Registration timeline and independent detections It was registered on 10 Nov 2026, 11 days before it was first reported, which provides very little operating history for a navigation portal claiming years of operation. Because 4 of 92 VirusTotal engines flagged it on 19 Nov 2026, with Webroot, CRDF and SOCRadar among the flagging engines, this page is tracked by independent security scanners as a potential risk rather than an isolated false alarm. Where navigation routing pages lead Routing portals of this kind typically act as distribution hubs or front-ends designed to redirect visitors toward frequently changing secondary servers or external destinations. Following these links can expose your browser to unverified third-party content, malicious downloads, or secondary phishing campaigns. Always verify the ultimate destination address before trusting external links provided by unknown routing pages. Precautions and recommended actions Simply close the browser tab if you only viewed the page and did not interact with any links. If you clicked through the route buttons and downloaded files or entered credentials on subsequent destinations, scan your device immediately and change any compromised passwords. Report suspicious domains directly to their registrar, Key-Systems GmbH, or relevant hosting abuse contacts.
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:59 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:59 UTClast content: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 Key-Systems
 188.114.97.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT