FBI IC3
Laporkan kejahatan yang dimungkinkan oleh internet di Amerika Serikat
Federal tips line1-800-CALL-FBI

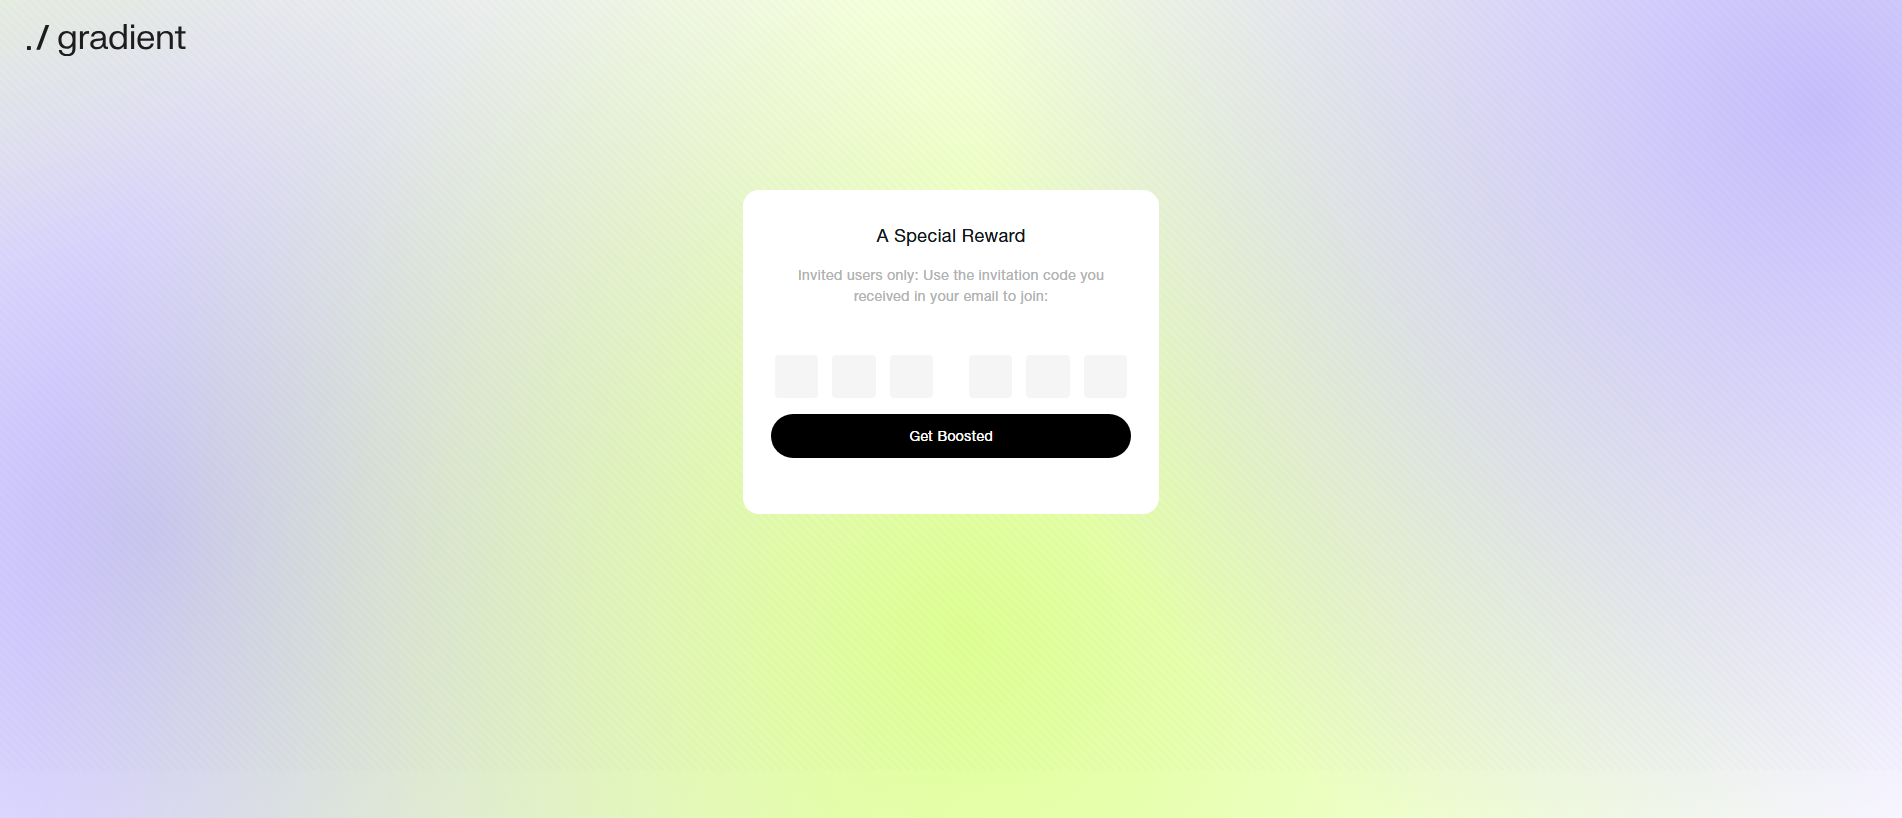
“Gradient Dashboard”
Analysis of my.graidient.network, observed on 12 July 2026, identifies it as an active high‑risk crypto‑drainer phishing site.
Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.
Analysis of my.graidient.network, observed on 12 July 2026, identifies it as an active high‑risk crypto‑drainer phishing site. The domain resolves to 162.244.92.2, hosted in the United States under AS965 Webhosting Holdings LLC. Registration records show NICENIC INTERNATIONAL GROUP CO., LIMITED as the registrar, with private nameservers ns1.private-nameserver.net, ns2.private-nameserver.net, and ns3.private-namese (truncated). The site presents a TLS certificate issued by Let’s Encrypt (YR1) and serves HTTP 200 responses using PHP on a LiteSpeed server with HTTP/3 enabled. VirusTotal reports two detections out of ninety‑one scanners, and the domain appears on two public blocklists, currently listed by PhishDestroy and ScamSniffer. The page title “Gradient Dashboard” offers no further indication of the malicious payload. No additional content analysis is available, leaving the exact phishing vector and credential capture mechanisms unconfirmed. Defenders should block the domain and its associated IP at perimeter controls, monitor DNS queries for the listed private nameservers, and incorporate the indicator set (domain, IP, registrar, SSL fingerprint) into threat‑intel feeds. Continuous re‑scanning is recommended to detect any change in detection count or hosting configuration.

Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
LiteSpeedScanner note: captcha: raw=captcha; http=200; via=https_proxy; server=LiteSpeed
 (RU)
PhishDestroy Investigation
For the registrable domain graidient.network behind this subdomain, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Google PageSpeed Insights — mobile performance audit of my.graidient.network · checked Jun 26, 2026
Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.


Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.
Infrastructure map · my.graidient.network
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
IP asal ini menghosting beberapa domain phishing — infrastruktur dapat digunakan bersama di seluruh kampanye.
These domains also target Tidak diketahui users. View all Unknown threats →
Part of the Tidak diketahui phishing campaign. View all campaign domains →
Laporan baru-baru ini ditambahkan dari database PhishDestroy. Tautan penemuan ini tidak berarti infrastruktur atau kepemilikan bersama.
Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik
Pindai SekarangLaporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas
LaporanLaporan phishing terbaru dan perubahan ketersediaan yang diamati
PantauPantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive
 ex-faucet.xyz
 ftx.case-debtors.com
 wrencapstead.digital
 zywa-capovin.pro
 xtradegrok36.com
 chat-trade-ai.live
 clawnchtoken.com