VirusTotal
1 / 93
Denunciar

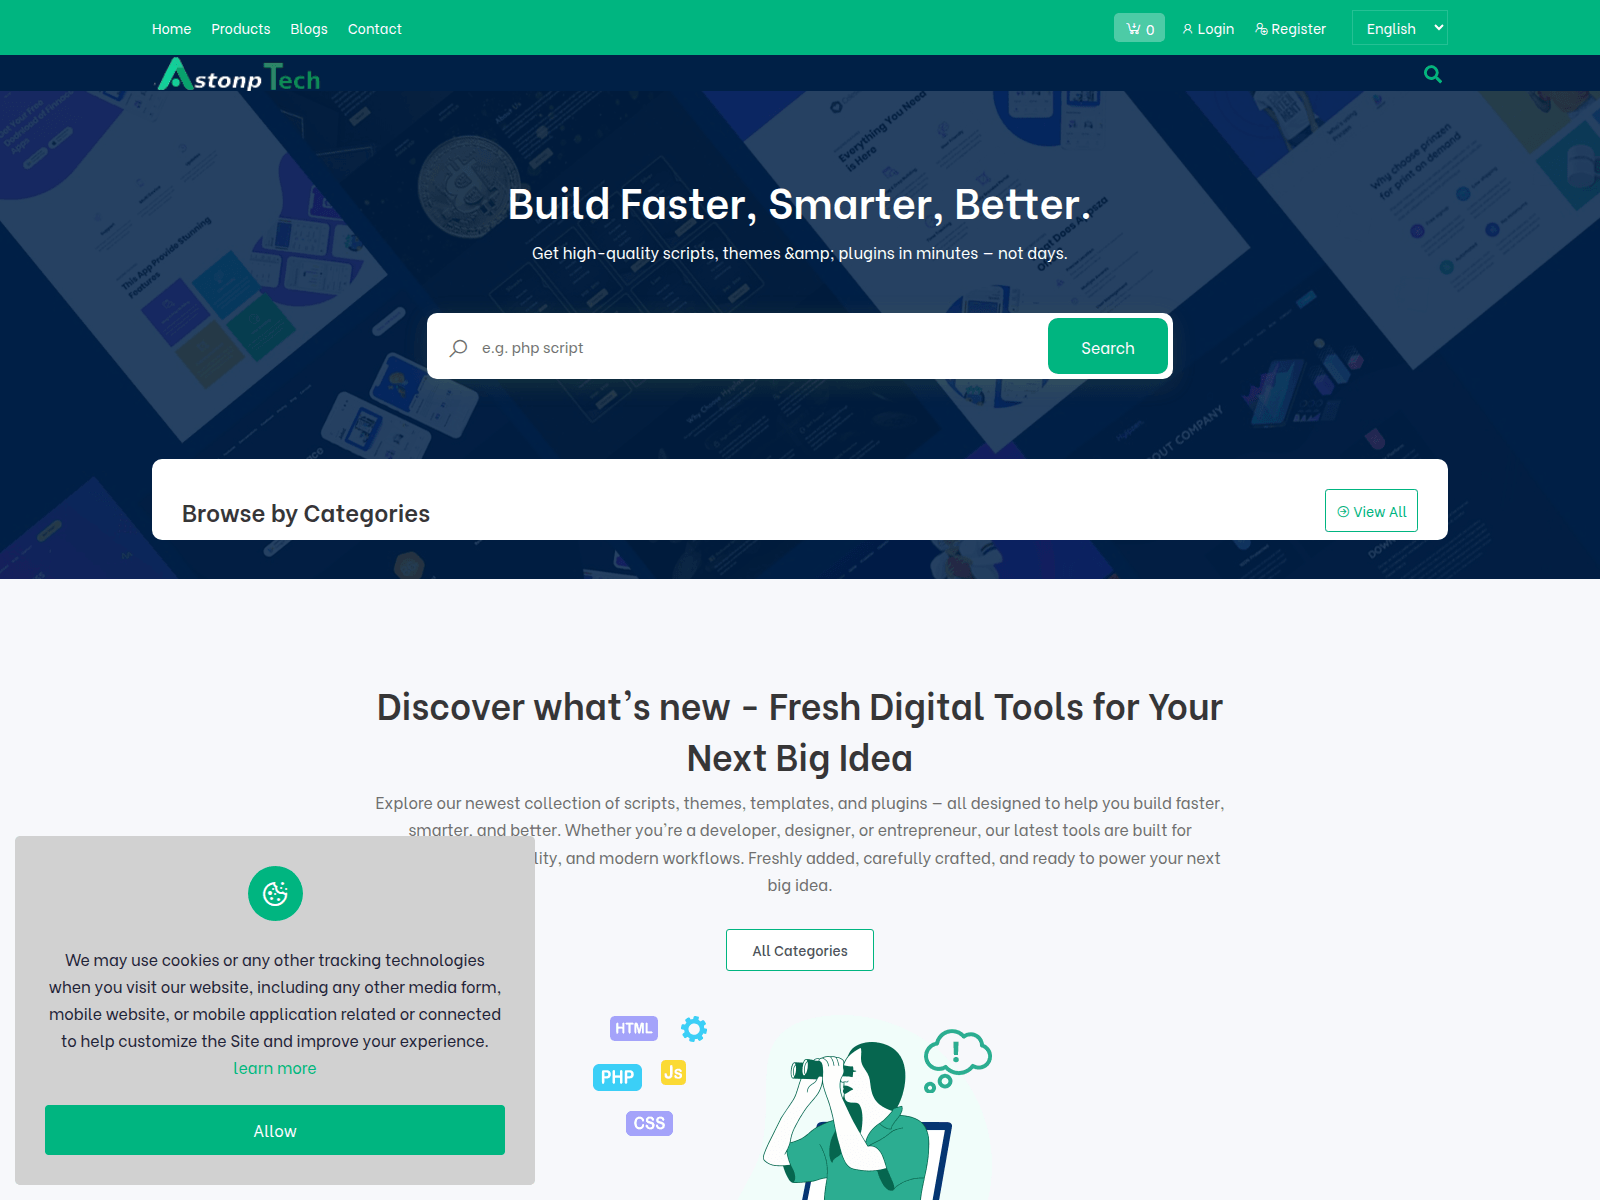
“Astonp Tech - Home”
stores.astonptech.com.ng — Contenido no disponible (HTTP 502). Tipo de estafa: Credential Phishing. Resumen de las pruebas: VirusTotal 1/93 (Gridinsoft); PhishDestroy score 56/100.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

On July 24, 2026 analysts observed that the domain stores.astonptech.com.ng was created on February 21, 2026 and is presently taken offline. The site presented the page title “Astonp Tech - Home”. An SSL certificate labeled R11 was associated with the domain, but no further certificate details were disclosed. The Gridinsoft trust score for the domain is 0 out of 100, indicating an extremely low trust rating.
PhishDestroy has already blocked the domain, confirming its involvement in malicious activity. VirusTotal analysis shows that one of ninety‑three security vendors flagged the domain, and the domain appears on a single external security blocklist. No additional data such as IP address, hosting provider, registrar, Safe Browsing status, or Open Threat Exchange entries were available.
Consequently, the observable evidence points to a credential‑harvesting phishing operation, yet the lack of broader infrastructure details limits attribution. Defenders should continue to block the domain at perimeter and endpoint layers, monitor DNS queries for any resurgence, and incorporate the domain into threat‑intel feeds. Ongoing vigilance is advised, especially given the recent creation date and the low trust score, which suggest a short‑lived but potentially impactful phishing campaign.
Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
Nota del escáner: transient_502: raw=transient_502; http=502; via=http_proxy
Location describes the IP network.
Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
8 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Reportado por 1 miembro de la comunidad; visto por primera vez el 08/08/2025
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Esta IP de origen aloja múltiples dominios de phishing; la infraestructura puede compartirse entre campañas.
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.