VirusTotal
15 / 91
Denunciar


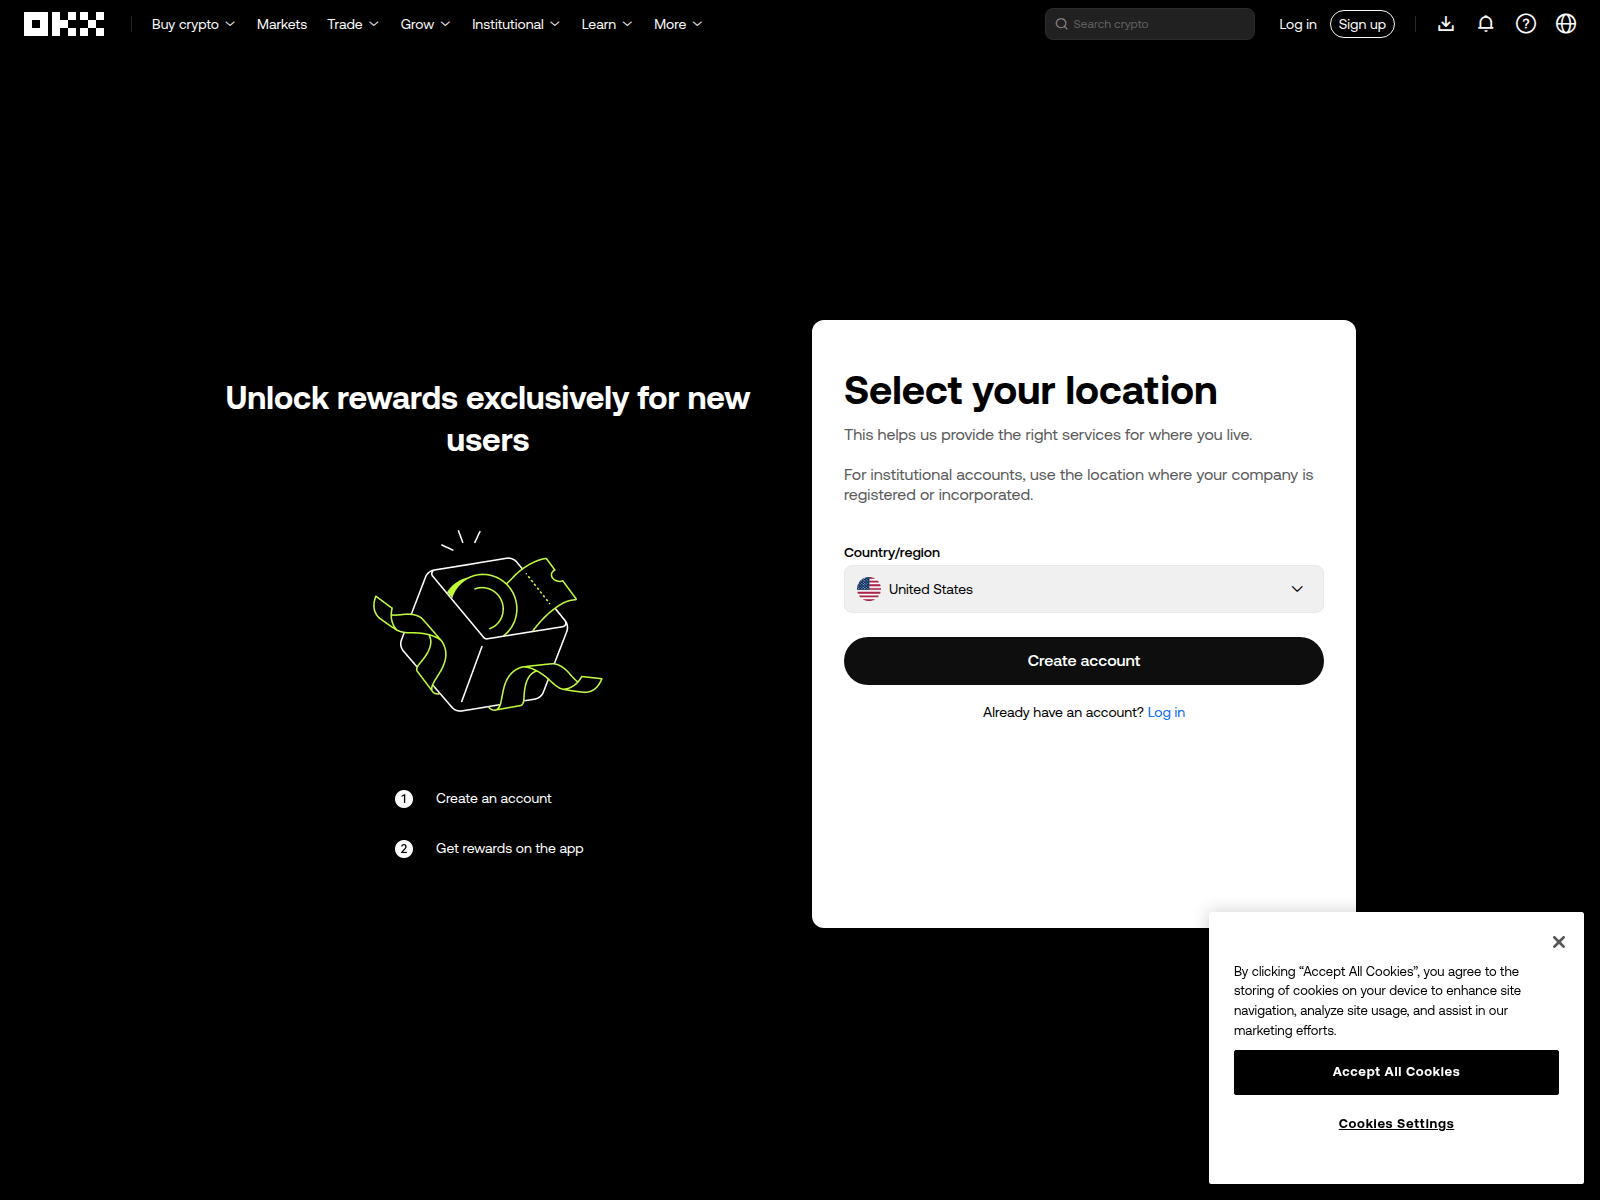
“Earn rewards when you get started on OKX | My referral code: 37602380 | OKX Europe”
cnouyi.org — Último activo conocido (HTTP 302). Suplantación de marca: OKX; Tipo de estafa: Brand Impersonation. Resumen de las pruebas: VirusTotal 15/91 (alphaMountain.ai, BitDefender, CyRadar, ESET, Emsisoft); URLQuery 3 alerts; URLScan malicious verdict; PhishDestroy score 100/100. Registrador: Dynadot.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

15 / 91
3 threat-system alerts
Denunciarmalicious
Denunciarchecked — no match recorded
23 community references
Denunciarprovider verdict: clean
Denunciarinforme almacenado
 Denunciar
12 comprobado — sin bloqueos
40/100
DenunciarChecked; no threat flag recorded
Denunciar| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Private YARA rules | static.okx.com/cdn/assets/okfe/util/ont/5.8.53/ont.js |
audit | Hunting_JS_WebAssembly |
| Hagezi Threat Feed | www.zhgwexpouy.net |
malicious | Sinkholed |
| DNS4EU | www.zhgwexpouy.net |
malicious | Sinkholed |
PhishDestroy identifies cnouyi.org as an active generic phishing domain posing as a fraudulent investment gateway designed to harvest cryptocurrency wallet credentials and private keys. This domain appears to deploy a drainer kit tailored to siphon digital assets under the guise of 'investment opportunities' or 'portfolio management tools.' No specific brand is directly mentioned in available telemetry, suggesting a generic financial-themed lure rather than a targeted impersonation. The threat actor behind this domain uses obfuscated JavaScript and fake transaction prompts to trick victims into connecting malicious wallet extensions or entering seed phrases.
This domain exhibits multiple red flags verified through forensic analysis. cnouyi.org was registered on December 18, 2025, through Dynadot Inc., just days ago. It resolves to IP 54.215.31.113 and leverages a legitimate SSL certificate from Let's Encrypt to appear trustworthy. However, VirusTotal analysis confirms only 1 out of 95 security vendors currently detect this threat, and it remains unflagged by Google Safe Browsing (GSB) as of the latest scan. The domain has not yet appeared on major blocklists, indicating a newly active campaign with low detection coverage.
As of current intelligence, cnouyi.org is flagged as 'active' with elevated risk. Immediate action is recommended: block this domain at network and endpoint levels, update browser and DNS blocklists, and warn users to avoid accessing financial services links from unsolicited emails or social media. While the current risk is elevated due to low detection, rapid response can mitigate potential victimization. However, the absence from major blocklists and fresh SSL issuance suggests the campaign may expand quickly. Users are advised to verify all financial websites via official channels and never enter wallet credentials on unofficial portals.
Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
Nota del escáner: redirect: raw=redirect_302; http=302; via=https_proxy; location=https://www.oyigwcn.systems/join/37602380
 (US)
ns2.dyna-ns.netLocation describes the IP network.
33906326804b7c872fc6aad93325d869edc6a0b0dbb3d3b0a8a99db7c768ef6aSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of cnouyi.org · checked Apr 19, 2026
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
89 dominios similares almacenados
Reportado por 1 miembro de la comunidad; visto por primera vez el 19/04/2026
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Forma parte de la campaña de phishing «Airdrop Scam». Ver todos los dominios de la campaña →
Esta IP de origen aloja múltiples dominios de phishing; la infraestructura puede compartirse entre campañas.
Estos dominios también se dirigen a los usuarios de OKX. Ver todas las amenazas de «OKX» →
Registrados a través del mismo proveedor de registro. Un proveedor de registro presta servicio a millones de clientes que no tienen relación entre sí, por lo que este dato solo agrupa los registros, en lugar de demostrar que exista un vínculo.
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.







