VirusTotal
14 / 89
Report

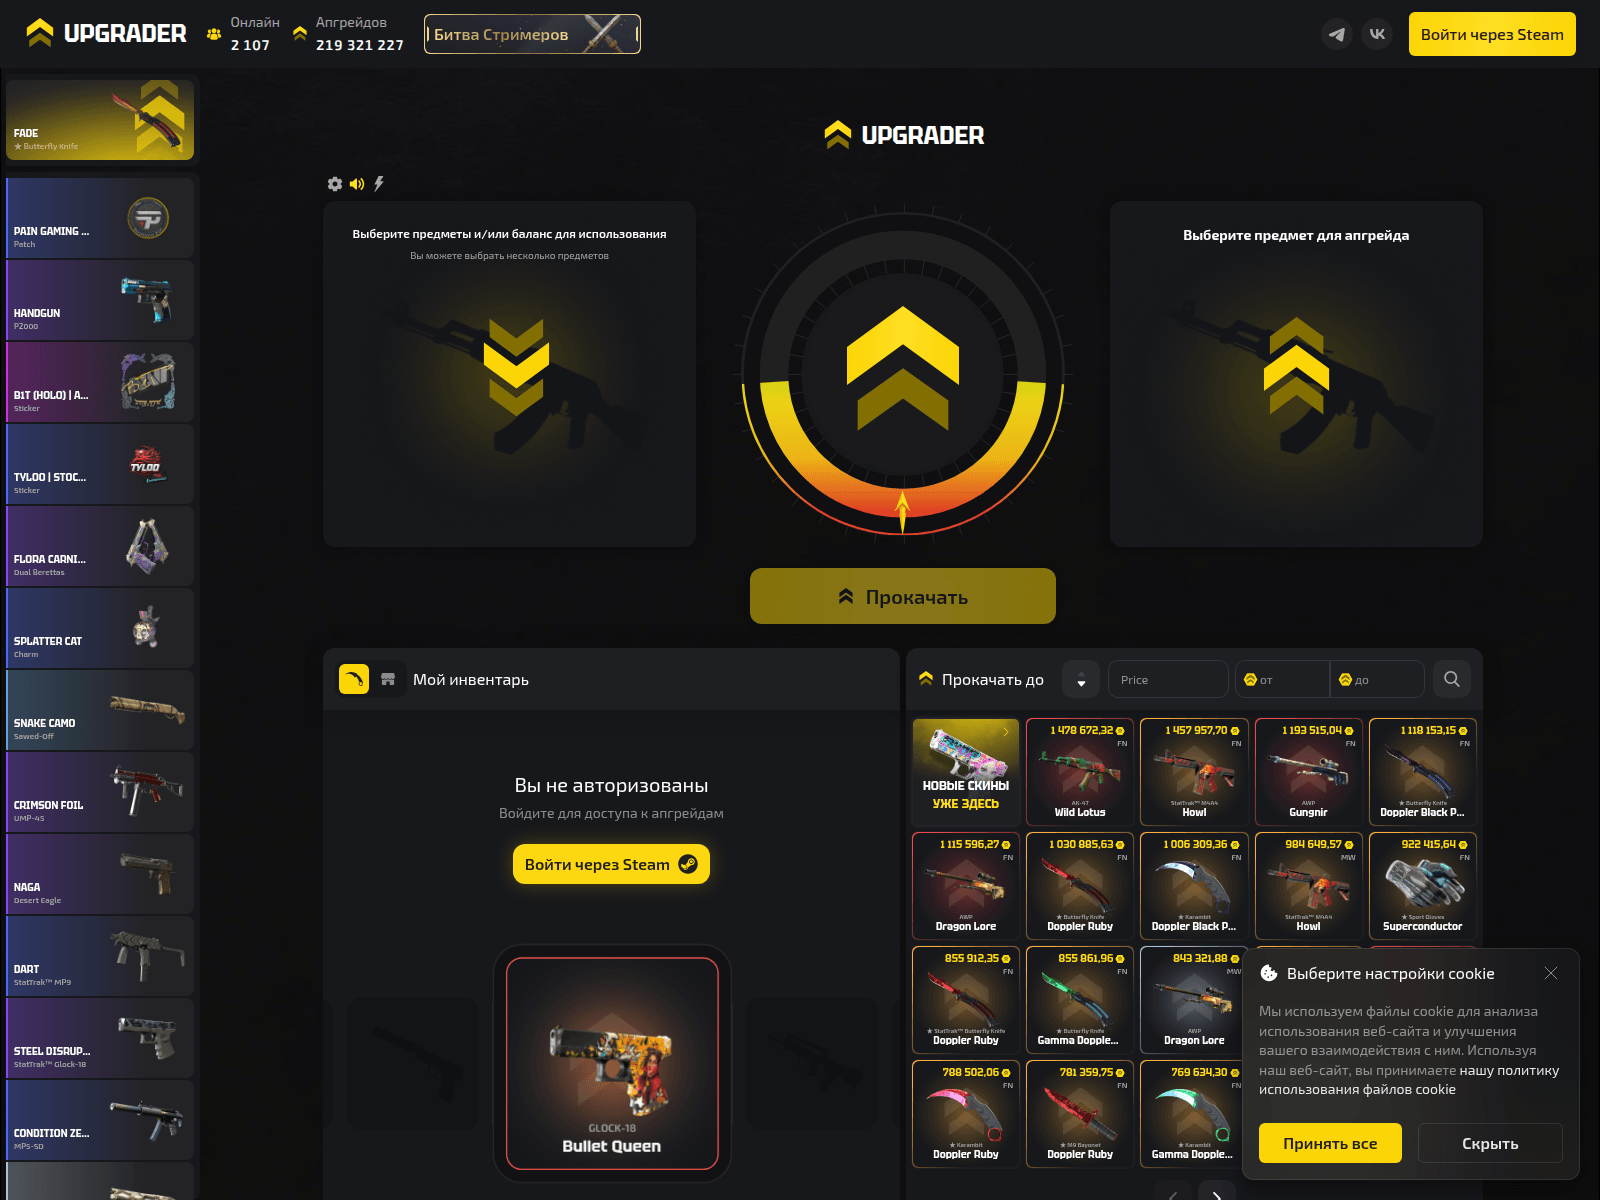
“Апгрейд предметов КС2: лучший Upgrader CS”
upgrder.com is a crypto drainer phishing domain impersonating wallet upgrades. Detected by 1/95 security vendors, this active threat targets digital asset theft
The detailed PhishDestroy AI analysis below remains in English to preserve the original forensic record.

This domain, upgrder.com, is identified as an active crypto drainer phishing site designed to deceive users into authorizing malicious transactions that siphon cryptocurrency from connected wallets. The site mimics legitimate wallet upgrade prompts, tricking victims into signing smart contracts that transfer funds to attacker-controlled addresses. Analysis of the domain reveals infrastructure commonly associated with high-risk financial fraud operations targeting decentralized finance (DeFi) users. Infrastructure analysis indicates the domain was registered on July 05, 2026, through Dominet (HK) Limited, a registrar frequently observed in phishing campaigns. It resolves to the IP address 109.172.84.90 and uses a Let's Encrypt SSL certificate to present a false sense of legitimacy. As of the latest assessment, only 1 out of 95 security vendors on VirusTotal flag this domain, suggesting low initial detection rates and potential evasion of automated defenses. The domain's recent creation date and minimal blocklist coverage further highlight its attempt to operate undetected. Users who have interacted with upgrder.com should immediately revoke any suspicious wallet authorizations and disconnect the site from connected applications. All cryptocurrency transactions initiated through this domain should be considered compromised, and affected wallets should be audited for unauthorized transfers. It is recommended to monitor wallet activity for unusual smart contract interactions and report the domain to relevant security platforms to improve detection and prevent further victimization.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
https://t.me/upgraderCSStored page referencehttps://t.me/upgrader_support_botStored page referenceIoC extraction recorded 2026-07-29 01:57:16 UTC
The page served one response to a browser-like visitor and another to a crawler or security scanner. Cloaking exists only to keep reviewers away from the real landing page.
status_splitScanner note: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='upgrder.com', port=80): Max retries exceeded with url: / (Caused by NewConnectionError("SO
 (HK)
Edge-IP reputation is not attributed to this domain.
ns-cloud-c1.googledomains.comns-cloud-c2.googledomains.comns-cloud-c3.googledomains.comns-cloud-c4.googledomains.comLocation describes the IP network.
757a925d7cb5f96c7fcf9447dc48ea6d260c12cf5cd47ce906bc825ef7d338cfwww.upgrder.comSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of upgrder.com · checked Jul 7, 2026
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
Part of the Unknown phishing campaign. View all campaign domains →
Shared edge IP; unrelated tenants may be present.
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive