Skip to security report
Redirect recorded qvaxum.icugoogle.com Details
qvaxum.icu favicon
Domain security and threat intelligence

qvaxum.icu

I was scammed — help me write a report
Share / download report
Post on X Send in Telegram Check via API
In short

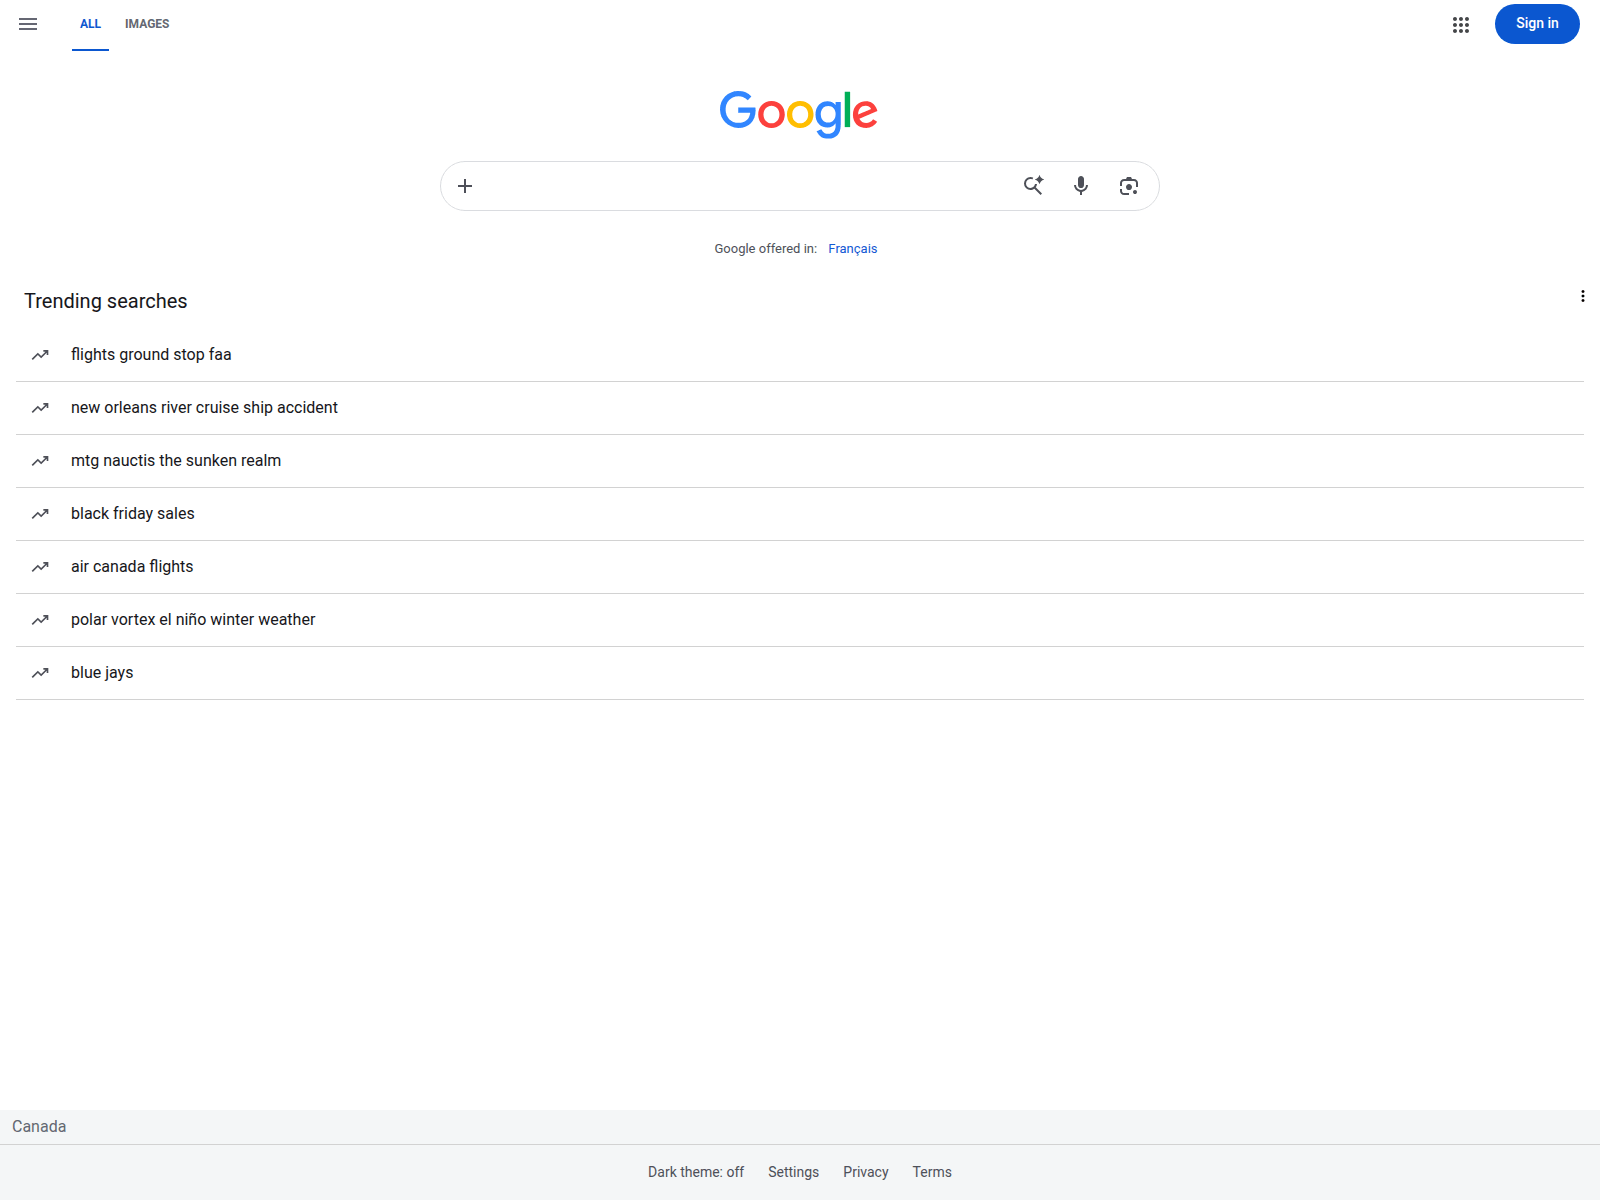
On 2026-11-14, qvaxum.icu redirected to www.google.com. The destination page shows the Google logo above a search box with microphone and image-search icons, a "Sign in" button, and a note that Google is offered in French. Below the search box, a "Trending searches" list displays items such as flights, weather, and sales queries, with a footer showing Canada and links for settings, privacy, and terms.

Page title: “Qvaxum: Unified DeFi Protocol for Global Markets”

More about the sources
Recorded security signals

Stored VirusTotal result: 2/92 engines flagged. Malicious: 0. Suspicious: 2. Analysis time (as stored): 2026-11-06 07:23 UTC. Retrieved (as stored): 2026-11-14 06:21 UTC. Use caution — do not enter credentials or personal information.

VirusTotal detections: 2/92 Spamhaus DBL: phishing domain Young domain: 16 days old
Registrar
RussiaNiceNIC
Resolved IP
Canada188.114.97.3CloudFlare, Inc. · CDN
Registered
2026-11-05
First seen by PhishDestroy
2026-11-14
URLQuery
detections
OTX
community references
Page captures
open gallery
Domain age
registered 2026-11-05 according to WHOIS · source data differ
Reports sent
view timeline
OTX: 4 refs 2026-11-14 1 Report Sent CDN

Risk score, higher = worse · How this score works

What to do right now

Pick what happened and tick the steps as you go. The ticks are kept only in this browser.

Entered a password0/3
Paid or entered card or bank details0/2
Downloaded a file0/2
Shared a seed phrase or private key0/3
Approved token spending (approve / permit)0/3
Connected a wallet but signed nothing0/2
Sent crypto0/3
Write a police report

Expert view has every section: DNS, TLS, network requests, hashes and the raw JSON.

Analysis

Domain summary

PhishDestroy first recorded qvaxum.icu on 2026-11-14. Stored VirusTotal result: 2/92 engines flagged. Malicious: 0. Suspicious: 2. Analysis time (as stored): 2026-11-06 07:23 UTC. Retrieved (as stored): 2026-11-14 06:21 UTC. Risk: high (evidence score 65/100). Registrar: NiceNIC. Status: Content unavailable. Hosting: Cloudflare, Inc. PhishDestroy sent 1 abuse report. Do not enter credentials or connect a wallet.

High
Status
Content unavailable
VirusTotal
2 / 92
Hosting
Canada188.114.97.3CloudFlare, Inc. · CDN
Registrar
RussiaNiceNIC
Registered
2026-11-05
OTX
4 community refs
Page captures
10

URLScan capture · 2026-11-14 05:43 UTC · SHA-256 fd8aeaeb…946e9e9

PhishDestroy analysis, reviewed version

On 2026-11-14, qvaxum.icu redirected to www.google.com. The destination page shows the Google logo above a search box with microphone and image-search icons, a "Sign in" button, and a note that Google is offered in French. Below the search box, a "Trending searches" list displays items such as flights, weather, and sales queries, with a footer showing Canada and links for settings, privacy, and terms.

The stored VirusTotal domain result reports 2 detections out of 92 engines. Fortinet reported "spam"; Forcepoint ThreatSeeker reported "suspicious".

Source evidenceVirusTotal 2 / 92 · OTX 4 references 8 sources

VirusTotal

2 / 92 engine detections

Analysis:
Open report
VirusTotalOriginal source recordObserved: 10 fields
Separate collector summary

This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.

Source
VirusTotal
Result state
observed
Numerator
2
Denominator
92
Vendors
Forcepoint ThreatSeeker, Fortinet
Observed at
2026-11-06 07:23:44
Checked at
2026-11-14 07:21:49
Fetched at
2026-11-14 06:21:49

Spamhaus DBL

phishing domain

OTX

4 community references

Open report

Cloudflare Radar

Scan report

Open report
Cloudflare RadarOriginal source recordObserved: 13 fields
Separate stored summary: clean

This summary differs from the dated scan above. It is retained for provenance and does not override the selected source observation.

Verdict
clean
Source path
phishdestroy.technologies.cf_radar
Scope
Separate stored summary; an absent observation date is not evidence of a clean scan.

URLScan

Page capture

SHA-256 b604e192…65ce1e4

Open report
URLScanOriginal source recordObserved: 25 fields

PhishDestroy DOM

10 / 100 · heuristic score · 1 brand reference · 0 classifications

Content heuristic only; not the final score

Open report
Technical metadata

PhishDestroy narrative

Narrative generation metadata

Open report
Title, description and generation record

The narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.

AI title
qvaxum.icu: Recorded redirect to www.google.com search page
AI description
PhishDestroy records a redirect from qvaxum.icu to www.google.com, whose captured page shows a search box, trending searches, and a sign-in button.
AI summary
On 2026-11-14, qvaxum.icu redirected to www.google.com. The destination page shows the Google logo above a search box with microphone and image-search icons, a "Sign in" button, and a note that Google is offered in French. Below the search box, a "Trending searches" list displays items such as flights, weather, and sales queries, with a footer showing Canada and links for settings, privacy, and terms. The stored VirusTotal domain result reports 2 detections out of 92 engines. Fortinet reported "spam"; Forcepoint ThreatSeeker reported "suspicious".
AI generated by
threat-v6-mimo
AI generated at
2026-11-14T06:25:08Z
Revision
22504e18db28d5982c3523d35f638c4156fdedf219baa390cc20b9115fa9277c
Mode
reviewed
Interpretation
Selected public package; text generation time is separate from source observation dates.

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Collected source details

Stored page, network and scanner observations, grouped by source and observation time.

Every stored field, with its source and date
Website checksOriginal source recordRetrieved: 25 fields

Mail configuration

SPF lookups
0

Protective DNS results

Resolvers checked
12
Blocking resolvers
0

Web archive observations

Last observation
First observation
Recorded changes
0
Archived days
1
Average page size, bytes
17447

Page title and metadata

Open Graph URL
https://qvaxum.com/
Page title
Qvaxum: Unified DeFi Protocol for Global Markets
Author
Qvaxum
Open Graph type
website
Indexing directives
index,follow,max-image-preview:large,max-snippet:-1,max-video-preview:-1
Open Graph image
https://qvaxum.com/assets/cardween-social.png
Open Graph title
Qvaxum — One Protocol. Every Market.
Open Graph site name
Qvaxum
Theme color
#020708
Description
Discover Qvaxum, the unified DeFi protocol for swapping crypto, tokenized stocks, gold and forex with atomic settlement and non-custodial access.
Twitter card
summary_large_image
Canonical URL
index.html
Open Graph description
Qvaxum unifies crypto, tokenized stocks, commodities and forex in one non-custodial DeFi protocol.

Trackers

Requests
1

Forms and mixed content

Third-party scripts
0

HTTP response

Reachable
Yes
HTTP status
200
Request timings, ms
DNS
2
TLS
16
Waiting
158
Connection
7
Download
1
Response time, ms
184

TLS connection

ALPN
h2
Cipher
TLS_AES_256_GCM_SHA384
Protocol
TLSv1.3
Supported versions
  • TLSv1
  • TLSv1.1
  • TLSv1.2
  • TLSv1.3
Certificate authorized
Yes
Forward secrecy
Yes

Ports

Open ports
  • 80
  • 443
  • 8080

Carbon estimate

Bytes
55952
CO₂, grams
0.002
Cleaner than, %
35

DNS servers

Nameservers
  • IP address
    172.64.35.104
    Host
    armfazh.ns.cloudflare.com
  • IP address
    172.64.34.94
    Host
    amalia.ns.cloudflare.com
DNS zone
qvaxum.icu

Cookies

Cookies
  • Name
    __Secure-STRP
    Secure
    Yes
    SameSite
    Strict
  • Name
    SEARCH_SAMESITE
    SameSite
    Strict
  • Name
    AEC
    Secure
    Yes
    HTTP-only
    Yes
    SameSite
    Lax
  • Name
    NID
    Secure
    Yes
    HTTP-only
    Yes
    SameSite
    None

Location

IP address
2a06:98c1:3121::3
ASN
13335
Organization
Cloudflare, Inc.
City
Washington
Country
US

TLS certificate

Issuer
Google Trust Services / WE1
Subject
qvaxum.icu

DNS records

A
  • 188.114.96.3
  • 188.114.97.3
NS
  • armfazh.ns.cloudflare.com
  • amalia.ns.cloudflare.com
SOA
Primary nameserver
amalia.ns.cloudflare.com
Hostmaster
dns.cloudflare.com
Serial
2419390940
Refresh, seconds
10000
Retry, seconds
2400
Expiry, seconds
604800
Minimum TTL, seconds
1800
AAAA
  • 2a06:98c1:3120::3
  • 2a06:98c1:3121::3

DNSSEC

DS record
No
RRSIG
No
DNSKEY
No

HSTS

Observation
Site does not serve any HSTS headers.

HTTP security policies

X-Frame-Options
No
Referrer-Policy
No
X-XSS-Protection
No
Permissions-Policy
No
X-Content-Type-Options
No
Content-Security-Policy
No
Strict-Transport-Security
No
Cross-Origin-Opener-Policy
No
Cross-Origin-Embedder-Policy
No
Cross-Origin-Resource-Policy
No

Web application firewall

WAF product
Cloudflare
WAF detected
Yes

IP lookup

IP address
2a06:98c1:3120::3
IP version
6

Redirects

Redirect chain
  • https://qvaxum.icu

Technology stack

Technologies
  • lit-html
  • lit-element
  • Cloudflare
  • HTTP/3

Page links

Internal links
12

Registration record

Registrar
NICENIC INTERNATIONAL GROUP CO., LIMITED
Registered
Updated
Expires
Status
  • serverTransferProhibited https://icann.org/epp
  • clientTransferProhibited https://icann.org/epp
  • clientDeleteProhibited https://icann.org/epp
Nameservers
  • amalia.ns.cloudflare.com
  • armfazh.ns.cloudflare.com

HTTP headers

Response headers
Server
cloudflare
Content-Type
text/html
Original source fields · JSON
Mail configuration
Spf lookups: 0
Protective DNS results
Resolvers: 12; Blocked count: 0
Web archive observations
Last: 2026-11-05T21:35:47Z; First: 2026-11-05T21:35:47Z; Changes: 0; Days archived: 1; Avg page bytes: 17447
Page title and metadata
Ogurl: https://qvaxum.com/; Title: Qvaxum: Unified DeFi Protocol for Global Markets; Author: Qvaxum; Ogtype: website; Robots: index,follow,max-image-preview:large,max-snippet:-1,max-video-preview:-1; Ogimage: https://qvaxum.com/assets/cardween-social.png; Ogtitle: Qvaxum — One Protocol. Every Market.; Ogsitename: Qvaxum; Themecolor: #020708; Description: Discover Qvaxum, the unified DeFi protocol for swapping crypto, tokenized stocks, gold and forex with atomic settlement and non-custodial access.; Twittercard: Summary large image; Canonicalurl: index.html; Ogdescription: Qvaxum unifies crypto, tokenized stocks, commodities and forex in one non-custodial DeFi protocol.
Trackers
Requests: 1
Forms and mixed content
Third party scripts: 0
Status
Up: ✓; Code: 200; Timings: DNS: 2; TLS: 16; Wait: 158; Connect: 7; Download: 1; Response ms: 184
TLS connection
Alpn: h2; Cipher: TLS_AES_256_GCM_SHA384; Protocol: TLSv1.3; Versions: TLSv1, TLSv1.1, TLSv1.2, TLSv1.3; Authorized: ✓; Forward secrecy: ✓
Ports
Open: 80, 443, 8080
Carbon
Bytes: 55952; Co2 grams: 0.002; Cleaner than: 35
DNS server
NS: (IP: 172.64.35.104; Host: armfazh.ns.cloudflare.com), (IP: 172.64.34.94; Host: amalia.ns.cloudflare.com); Zone: qvaxum.icu
Cookies
Cookies: (Name: __Secure-STRP; Secure: ✓; Same site: Strict), (Name: SEARCH_SAMESITE; Same site: Strict), (Name: AEC; Secure: ✓; HTTP only: ✓; Same site: Lax), (Name: NID; Secure: ✓; HTTP only: ✓)
Location
IP: 2a06:98c1:3121::3; ASN: 13335; Org: Cloudflare, Inc.; City: Washington; Country: US
SSL
Issuer: Google Trust Services / WE1; Subject: qvaxum.icu
DNS records
A: 188.114.96.3, 188.114.97.3; NS: armfazh.ns.cloudflare.com, amalia.ns.cloudflare.com; Soa: Nsname: amalia.ns.cloudflare.com; Hostmaster: dns.cloudflare.com; Serial: 2419390940; Refresh: 10000; Retry: 2400; Expire: 604800; Minttl: 1800; Aaaa: 2a06:98c1:3120::3, 2a06:98c1:3121::3
Dnssec
Ds: ✗; Rrsig: ✗; Dnskey: ✗
Hsts
Message: Site does not serve any HSTS headers.
HTTP security policies
Xframeoptions: ✗; Referrerpolicy: ✗; Xxssprotection: ✗; Permissionspolicy: ✗; Xcontenttypeoptions: ✗; Contentsecuritypolicy: ✗; Stricttransportpolicy: ✗; Crossoriginopenerpolicy: ✗; Crossoriginembedderpolicy: ✗; Crossoriginresourcepolicy: ✗
Firewall
Waf: Cloudflare; Has waf: ✓
Get IP
IP: 2a06:98c1:3120::3; Family: 6
Redirects
Chain: https://qvaxum.icu
Tech stack
Technologies: lit-html, lit-element, Cloudflare, HTTP/3
Page links
Internal count: 12
Registration record
Registrar: NICENIC INTERNATIONAL GROUP CO., LIMITED; Created: 2026-11-05T18:50:54Z; Updated: 2026-11-10T18:54:49Z; Expires: 2027-11-05T23:59:59Z; Status: serverTransferProhibited https://icann.org/epp, clientTransferProhibited https://icann.org/epp, clientDeleteProhibited https://icann.org/epp; Nameservers: amalia.ns.cloudflare.com, armfazh.ns.cloudflare.com
HTTP headers
Headers: Server: cloudflare; Content type: text/html
Network Security Intelligence Registrar context
Registrar context NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
NiceNIC Verdict Full Investigation

Questions about qvaxum.icu

Is qvaxum.icu legit?

PhishDestroy rates qvaxum.icu as high risk (evidence score 65/100) from the recorded evidence; it was first recorded on 2026-11-14. Stored VirusTotal result: 2/92 engines flagged. Malicious: 0. Suspicious: 2. Analysis time (as stored): 2026-11-06 07:23 UTC. Retrieved (as stored): 2026-11-14 06:21 UTC. The local score and a listing do not prove fraud. Check each source’s date and the exact URL.

Is qvaxum.icu safe to connect a wallet?

Because of the risk signals above, do not connect a wallet, sign messages or approve token permissions on qvaxum.icu. A confirmed blockchain transaction cannot be reversed.

What should I do if I used qvaxum.icu?

  • Entered a password — change it on that service and on every other site where you used the same password
  • Turn on two-factor authentication — where the service offers it; an authenticator app is stronger than SMS codes
  • Paid or entered card or bank details — contact your bank or payment service through the contacts on your card or its official website
  • Connected a wallet but signed nothing — disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds
  • Approved token spending (approve / permit) — revoke that approval with a token-approval checker
  • Shared a seed phrase or private key — move the remaining funds to a new wallet with a new seed phrase; the exposed wallet is no longer safe
  • Downloaded a file — do not open it and scan the device with security software

Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority. A report does not guarantee that money is returned. Step-by-step help: emergency guide.

Explore

Blocklist matchesPhishDestroy 1
PhishDestroy PhishDestroy list View source

Page captures (10)

All capture links and hashes (10)
Observed page title
Qvaxum: Unified DeFi Protocol for Global Markets
Automated brand references
Google
TLS Certificate
Issued by WE1 · stored validity ends in 73 days

Domain details

Domain
URLScan verdict Analysis completed score 0 report ↗
IP Context Canada188.114.97.3 Cloudflare shared edge origin IP hidden Edge-IP reputation is not attributed to this domain.
OTX tags 2026-11activeall-domainsblocklistcontentcryptodomainsdrainerfraudlivemonthlyphishdestroyphishingscam
Registrar NiceNIC RU(RU) PhishDestroy Investigation
Abuse contactabuse@nicenic.net
RegistrationCreated 2026-11-05 (16d · Very New!) — Expires 2027-11-05
Time to First Unavailability 2 days
What we count Elapsed time from the first stored abuse report to the first observation that the content was unavailable. This does not establish the cause.
What each report contains Stored outgoing-report records may reference evidence available at the time, such as vendor verdicts, registration data, hosting details, classifications, or screenshots. This page does not infer the exact payload delivered, receipt, acknowledgement, or action by a recipient.
LLM Report Plain-text dossier structured for AI agents
Technical detailsProvenance & timestamps
First Detected2026-11-14
DOM Analysisanalyzed 2026-11-14score 10/1001 brand signal
Submitted URLhttps://qvaxum.icu/
Favicon Hash
Case ID
SHORTDOT ZONE · PUBLIC EVIDENCE .icu

ShortDot zone evidence

The linked repository preserves daily zone observations across seven ShortDot-operated TLDs, including registration volume and abuse-related indicators. This registry context is supporting background and is not an independent detection for the domain in this report.

ShortDot SA · Luxembourg 7 zones · full-zone evidence updated daily Open the ShortDot evidence repository (GitLab)
ICANN OVERSIGHT

Accreditation and RAA context

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Nothing is sent automatically.

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
Canada188.114.97.3
Network ASN
AS13335
Organization
CloudFlare, Inc.
Observed location
CanadaToronto, CA
Server header
cloudflare

Edge-IP reputation is not attributed to this domain.

Nameservers 2

  • amalia.ns.cloudflare.com
  • armfazh.ns.cloudflare.com

SOA

  • nsname: amalia.ns.cloudflare.com
  • hostmaster: dns.cloudflare.com
  • serial: 2419390940
  • refresh: 10000
  • retry: 2400
  • expire: 604800
  • minttl: 1800

Location describes the IP network.

TLS certificate

Issuer
WE1
Valid from
2026-11-05 18:00:25
Valid until
2027-02-03 19:00:23
Hostname match
Yes
Validity
Within stored validity dates
Collection source
PhishDestroy collector
Certificate fingerprint406cf04e179cacdaa93a612a0cc7a4f2e8a9885b2ee3fe085500fd291f9658f2
Certificate names · 2 SANs
  • qvaxum.icu
  • *.qvaxum.icu

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-11-22 06:03 UTC

The domain no longer resolves in DNS.

Technical details
Primary outcome DNS inactive reason: DNS NXDOMAIN 80% confidence
Attribution source: Dns Cache
Evidence layers Availability: DNS inactive Content: Unreachable DNS: NXDOMAIN Registration: Active
RDAP registration Active NICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765 RDAP HTTP 200 source: Rdap Status Collector clientDeleteProhibitedclientTransferProhibitedServertransferprohibited expires 2027-11-05 23:59 UTC checked 2026-11-15 06:20 UTC
Observed timeline last reachable: 2026-11-16 03:43 UTC last content: 2026-11-16 03:43 UTC current episode first observed: 2026-11-17 05:12 UTC observed RIP window: 2026-11-16 03:43 UTC → 2026-11-17 05:12 UTC · 25.49h midpoint estimate ≈ 2026-11-16 16:28 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Technologies · 5 identified
Open complete records

VirusTotal Analysis

2 / 92 security vendors flagged this domain
View on VT
Last analyzed First positive result retrieved by PhishDestroy
Fortinet
Forcepoint ThreatSeeker
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: https://qvaxum.icu/
Qvaxum: Unified DeFi Protocol for Global Markets
Discover Qvaxum, the unified DeFi protocol for swapping crypto, tokenized stocks, gold and forex with atomic settlement and non-custodial access.
Response
HTTP 200
HTML body
55.0 KB
Compressed
15.0 KB
Links
43 internal · 1 external
Detected technologies
cloudflare
Selected response headers
Content-Type: text/html
CF-Cache-Status: HIT
Cache-Control: public, max-age=0, must-revalidate
Content-Encoding: gzip
Server: cloudflare
HSTS: not observed DNSSEC: not observed WAF / firewall: observed Cloaking flag: not observed
Favicon fingerprint: bfd988ebb3d1c56b57e237295d0021817221c461865d9faf622fe0f3be1337f0
Open Graph title: Qvaxum — One Protocol. Every Market.
Open Graph description: Qvaxum unifies crypto, tokenized stocks, commodities and forex in one non-custodial DeFi protocol.
Twitter card: summary_large_image
Saved response-header values · 13
Alt-Svc
h3=":443"; ma=86400
Cache-Control
public, max-age=0, must-revalidate
CF-Cache-Status
HIT
CF-RAY
a5a3b5d388a01bea-CDG
Connection
keep-alive
Content-Encoding
gzip
Content-Type
text/html
Date
Sat, 14 Nov 2026 05:45:28 GMT
NEL
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
Report-To
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=COGabzpjddmX8S9ful77aDkaeI4iJsyoklArPVGGR3QPF%2FWJ5gllLz1K2L8X9yEdy5W2YWFjlHxQfftzx2CcixEcVppT8RLZ8Vq%2FY5j4sMBIwrETatL%2FqVqaRbz7"}]}
Server
cloudflare
Server-Timing
cfCacheStatus;desc="HIT"
Transfer-Encoding
chunked

Values retained by the collector; long values may be shortened during collection.

Registration & observation details16

Registration evidence

RDAP statuses
clientdeleteprohibited · clienttransferprohibited · servertransferprohibited
RDAP response
200
Registrar in registration evidence
NICENIC INTERNATIONAL GROUP CO., LIMITED
Registrar IANA ID
3765
Expiration recorded by RDAP
Registration observation
Registration source
rdap_status_collector

Availability observations

Last reachable observation
Last content observation
Outcome first observed
Observation window starts
Observation window ends
Estimated change time
Observation window · hours
25.49
Estimate basis
Bounded by observations
Estimate precision
Medium

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

All stored data124
Open complete records

Captured network requests

Network requests: 69 SHA-256 hashes: 66 URLScan scan:

Network requests that the URLScan browser recorded while loading the page. URLScan does not provide a hash for every request. PhishDestroy retrieved this list on 2026-11-14 05:48 UTC.

Open this scan on URLScan 01a1d895-0991-7013-8c83-4b569531f7b9 ↗

Stored observation history6

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Availability monitor · Recorded state

    Not resolving in DNS

    domain does not exist in DNS

  2. Availability monitor · Recorded state

    Serving page content

    page content returned

  3. Availability monitor · Recorded state

    Serving page content

    page content returned

  4. Availability monitor · Recorded state

    Serving page content

    page content returned

  5. Availability monitor · Recorded state

    Serving page content

    page content returned

Earlier observations 1
  1. Domain monitor · First collection record

    Reachable

Separate monitor HTTP observation

Source: domain_monitor. This stored snapshot does not establish current availability.

Observed · UTC
Recorded HTTP status
200
Probe value as recorded
200
Original source timestamp
2026-11-12 22:28:19
All retained availability observations21
Open complete records

Threat Response Pipeline

  1. Discovery · recorded
  2. Analysis · recorded
  3. Notifications · recorded
  4. Monitoring · recorded

Recorded events: 13. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Pre-emptive Discovery & IngestionThreat Ingested recorded
  • Threat Ingested
    qvaxum.icu detected and queued for full analysis
Threat Intelligence ChecksSpamhaus DBL · URLScan.io Capture · Cloudflare Radar Report · VirusTotal · OTX Community References · Registrar Context: NiceNIC · Forensic Evidence Collected · Technical Analysis Recorded recorded
Notification RecordsSent Report Recorded recorded
  • Sent Report Recorded
    Stored record of an abuse report about this domain; registrar at the time: NICENIC INTERNATIONAL GROUP CO., LIMITED. Abuse contacts: 1.
    • abuse@nicenic.net
Publication & AvailabilityDestroyList Published · Content Observed Unavailable · Time to First Unavailability recorded
  • DestroyList Published
    Listed in the public repository PhishDestroy/DestroyList
  • Content Observed Unavailable
    The latest stored checks indicate that the reported content is unavailable; this does not establish who or what caused the change.
  • Time to First Unavailability
    Hours from detection to the first unavailable observation: 58

Recorded activity

7 entries

Lifecycle

  1. Domain registered
  2. VirusTotal analysis with detections+12 h 32 min
  3. Added to PhishDestroy+7 d 22 h
  4. First abuse report sent+2 min

Reported 8 d 10 h after registration

  1. NiceNIC

    Replied to the report

    +47 h 37 min
  2. AlienVault OTX

    4 community references

    same minute
  3. Cloudflare Radar

    Phishing

    +34 min
  4. Abuse report sent

    PD-2CC82E584C1766B17BC9 · Receipt 84871

    abuse@nicenic.net
    +2 min
  5. Added to PhishDestroy

    qvaxum.icu

    same minute
  6. URLScan

    Page captured

    +7 d 22 h
  7. VirusTotal

    2/92 engine detections

How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

All stored records by source

Browse this domain’s complete history by source. The download includes every record of the selected source. Dates retain their original field labels.

Download all records as JSON

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

qvaxum.icu

Evidence & External Reports

Submitted Evidence Snapshot
Sent: Ledger records: 1 Case ID: PD-2CC82E584C1766B17BC9 Recipient: abuse@nicenic.net
Page title stored with report: Google
PDF notice generated
Deep Analysis

Were You Affected by This Site?

You are not alone and there is nothing to be ashamed of. Scammers are sophisticated criminals who exploit trust. Reporting your experience is the most powerful weapon against fraud — your report can prevent others from becoming victims and help law enforcement take action. Secure your accounts and funds first, then report. If credentials were compromised, report immediately. Do not engage with recovery scammers.

Act on what you actually did. Entered a password: change it, and wherever you reused it. Paid or gave card details: contact your bank or payment service. Downloaded a file: scan the device. Then report the incident.

Where to report

The draft stays only with you.

First secure your money: call your bank or revoke wallet approvals. Immediate steps →

More: international and crypto channels

Official reporting routes

More official reporting routes
SEAL 911 Worldwide

Emergency help from security researchers when a crypto wallet is being drained right now.

FTC ReportFraud United States

Report scams and fraud to the US Federal Trade Commission. Reports go into a database used by law enforcement.

IdentityTheft.gov United States

Official identity theft report with a step-by-step recovery plan.

CISA United States

Report cyber incidents and phishing to the US Cybersecurity and Infrastructure Security Agency.

CSIRTs Network European Union

Directory of national incident response teams (CSIRTs) in the EU. Find the team for your country.

FIRST Worldwide

Worldwide directory of incident response teams, searchable by country and sector.

ReportCyber Australia

Report cybercrime to the Australian Cyber Security Centre and police.

Scamwatch Australia

Report scams to the National Anti-Scam Centre run by the ACCC.

After a phishing incident

Recommendations & Advice for Victims

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

What should I do immediately?

Urgent

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Entered a password — change it on that service and on every other site where you used the same password
  • Turn on two-factor authentication — where the service offers it; an authenticator app is stronger than SMS codes
  • Paid or entered card or bank details — contact your bank or payment service through the contacts on your card or its official website
  • Downloaded a file — do not open it and scan the device with security software
  • Shared a seed phrase or private key — move the remaining funds to a new wallet with a new seed phrase; the exposed wallet is no longer safe
  • Connected a wallet but signed nothing — disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds
  • Approved token spending (approve / permit) — revoke that approval with a token-approval checker (revoke.cash)
  • Sent crypto — save the transaction hash, your address and the receiving address; blockchain transactions cannot be reversed

What information should I collect for my report?

FBI guidelines

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Exact dates & times — of each transaction and first contact with scammer
  • Screenshots — scam website, chat messages, emails, wallet transactions, social media
  • All URLs & domains used by the scammer (including qvaxum.icu)
  • Communications — emails, texts, phone numbers, usernames the scammer used

Even if you don't have all details — file a report anyway. Partial information still helps investigations.

Where should I report the scam?

  • FBI IC3 — Internet Crime Complaint Center (US federal reporting)
  • Europol — European cybercrime reporting (EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Local police — creates an official record, even if they can't act immediately

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Fake websites — pixel-perfect clones of legitimate sites with slightly altered domains
  • Pig butchering — trust built over weeks via Telegram/WhatsApp/dating apps, then money stolen
  • Recovery scams — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • AI-powered scams — deepfakes, automated phishing, and AI-generated sites making fraud harder to detect

How can I protect myself in the future?

  • Bookmark official sites — never click links from emails, DMs, or ads
  • Verify domains — check on PhishDestroy before interacting. Check HTTPS, spelling, domain age
  • "Too good to be true" = scam — guaranteed returns, celebrity endorsements, urgent deadlines

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive

Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/qvaxum.icu"
  title="PhishDestroy threat report for qvaxum.icu"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>