


 ChainPatrol
 Web-Check
 SOCRadar
 LeakIX

ABUSE NOTICE · 7D+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@namemart.com.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
1 month
Reports sent
1
Latest case ID
PD-20260717-4E71EB
Current status
Observed active at latest stored check
Domain security and threat intelligence

j68v.vip
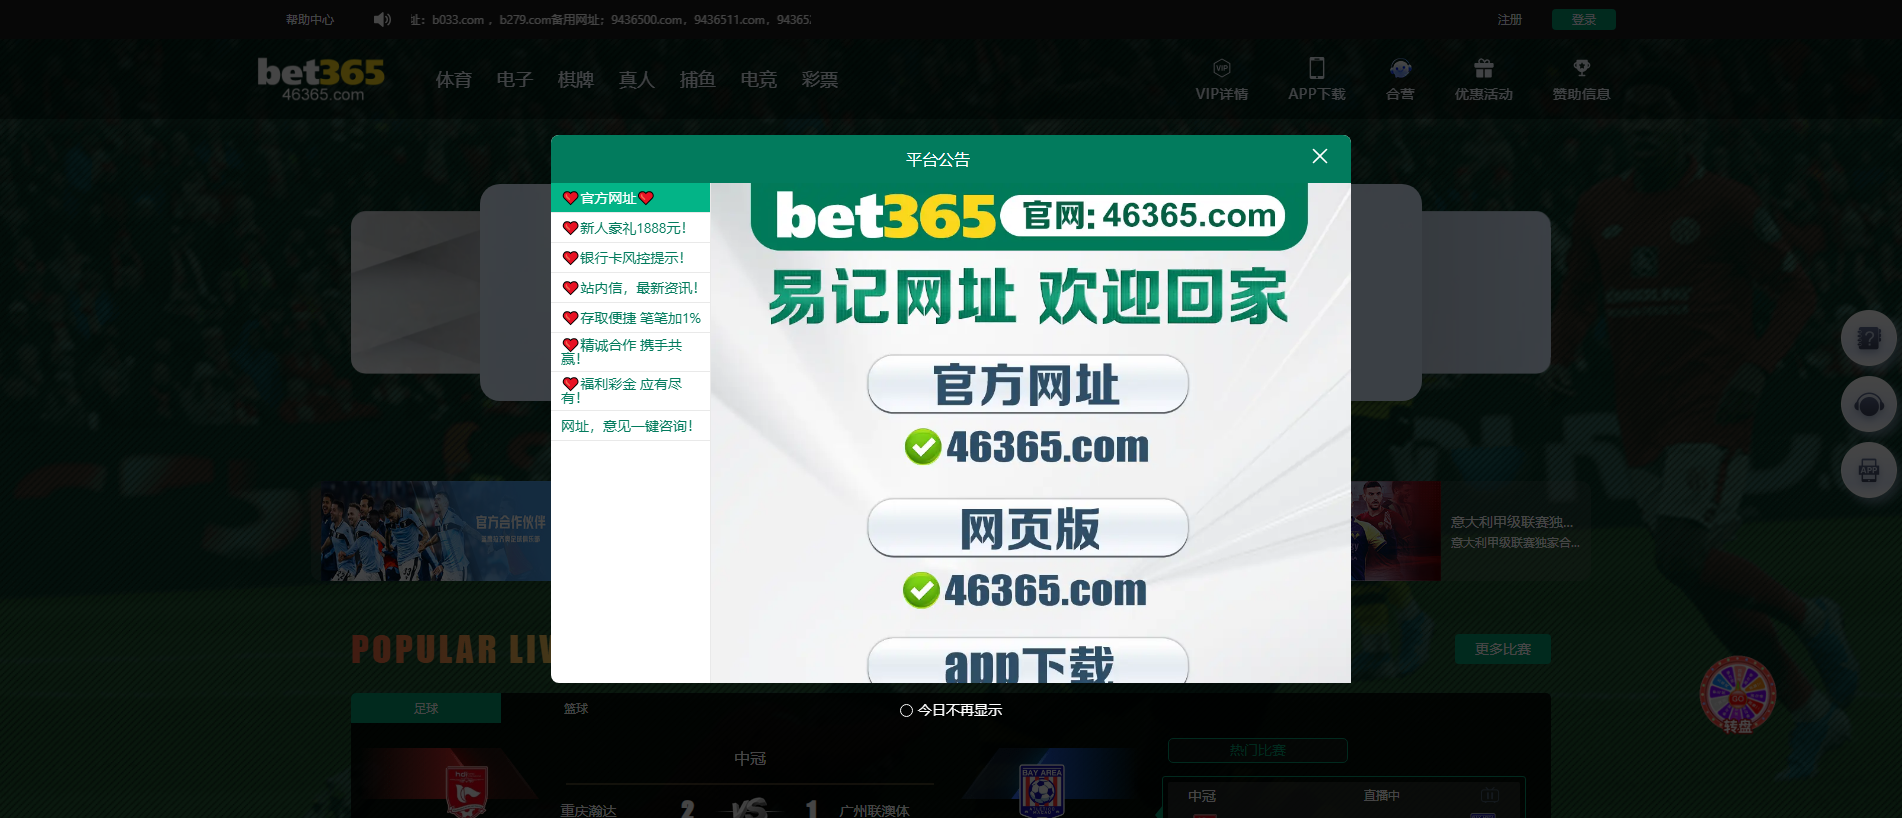
“welcome-BET365”
Threat verdict
Critical
95/100 evidence score
Availability
Unverified
Current reachability is unverified
Risk signals
VirusTotal detections: 18/91
Spamhaus DBL: DBL_SPAM
URLQuery threat systems: 9 alerts
Brand impersonation: Bet365
Evidence Summary
CRITICAL
The domain j68v.vip was registered on 24 May 2026 through NameMart Pte. Ltd. and remains active as of the report date. DNS resolution points to the IPv4 address 103.27.177.164, and the domain is served by four nameservers (ns1‑ns4.1111343.com). VirusTotal analysis shows that 14 of 91 security vendors have flagged the domain, indicating a notable level of detection across multiple scanning engines. The threat classification provided is generic_phishing with a high risk rating, suggesting that the domain is likely being used to harvest credentials or personal data. No additional intelligence such as hosted content, observed payloads, or targeted brands is available at this time, leaving the exact phishing vector and victim profile uncertain. Defenders should block network traffic to j68v.vip, monitor DNS queries for the associated nameservers, and incorporate the IP address 103.27.177.164 into intrusion‑prevention rules. Continuous monitoring of VirusTotal and other threat‑intel feeds is recommended to capture any changes in detection rates or new indicators of compromise linked to this infrastructure.
VirusTotal
18 det.
URLQuery
9 threat alerts
CF Radar
Malicious
URLScan
Scamadviser
80/100
TLS Certificate
Let's Encrypt / YR2 2d
Age
4 mo
Observed status
Unverified

DestroyList
Listed
Reports Sent
1
Data coverage
VirusTotal
18 / 91
URLQuery
9 threat-system alerts
PhishStats
not checked
OTX
no community references
CF Radar
provider verdict: malicious
URLScan capture
stored report
URLScan verdict
Analysis completed
DNS blocks
not checked
TLS
valid certificate, 2d
WHOIS
4 mo old
Screenshot
3 captures · 3 sources
Redirect chain
not probed
Scamadviser
80/100
Network Security Intelligence
Threat Detection Systems
9 alerts
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DNS4EU | 17651.xyz |
malicious | Sinkholed |
| Hagezi Threat Feed | img.esportsdata.cc |
malicious | Sinkholed |
| DNS4EU | img.esportsdata.cc |
malicious | Sinkholed |
| Cloudflare DNS | j68v.vip |
malicious | Sinkholed |
| OpenDNS | j68v.vip |
phishing | Phishing Block |
| DigiCert UltraDNS | j68v.vip |
malicious | Sinkholed |
| Hagezi Threat Feed | j68v.vip |
malicious | Sinkholed |
| DNS4EU | j68v.vip |
malicious | Sinkholed |
| DNS4EU | ssl.hw301.xyz |
malicious | Sinkholed |
Threat Response Pipeline
Discovery
Checks
Reports
Availability
12/13
Sent Report Recorded
Stored sent-report record for registrar NameMart Pte. Ltd., hosting provider, 1 abuse contact
abuse@namemart.com
Public Blocklist Status
Submitted Evidence Snapshot
- Sent
- Ledger records
- 1
- Case ID
PD-20260717-4E71EB
Blocklist coverage
11 monitored external feeds · stored snapshot Sep 10, 2026
Stored Capture
Domain Intelligence
Domain
URLScan Verdict
Analysis completed
score 0 report ↗
Server / ASN
Nginx · AS18186 NEBULA-GLOBAL - Nebula Global LLC, US
IP Reputation
abuse score 0/100 0 reports checked Aug 15, 2026
Registrar
NameMart
 (CN)
(CN)
IP Address
154.39.104.144

Geo Hong Kong, HK
Hong Kong, HKNetworkAS18186 · AS135357 HONG KONG KOWLOON TELECOMMUNICATIONS CO.,LIMITED
RegistrationCreated May 24, 2026 (108d) — Expires May 24, 2027
Technical detailsDNS, SSL SANs, timestamps
First DetectedJul 16, 2026
DOM Analysis
IoC Extraction
Submitted URLhttp://j68v.vip/
Nameserversns1.1111343.comns2.1111343.comns3.1111343.comns4.1111343.com
TLS Fingerprint
TLS Observation
TLS SAN Domainsj68g.vipj68h.vipj68i.vipj68j.vipj68k.vipj68l.vipj68m.vipj68n.vipj68o.vipj68p.vipj68q.vipj68r.vipj68s.vipj68t.vipj68u.vip+32
Case ID
ICANN OVERSIGHT
Accreditation and RAA context
Accreditation and RAA context
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Accreditation is a contract, not a safety seal.
Verify ICANN fees
Read RAA §3.18
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Technologies · 5 identified
V
Vue.js
JavaScript frameworks
Vue.js is an open-source model–view–viewmodel JavaScript framework for building user interfaces and single-page applications.
vuejs.org 100% confidence
N
Nginx
Web servers
Reverse proxies
Nginx is a web server that can also be used as a reverse proxy, load balancer, mail proxy and HTTP cache.
nginx.org 100% confidence
H
HSTS
Security
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
www.rfc-editor.org 100% confidence
Cloudflare
CDN
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
www.cloudflare.com 100% confidence
H
HTTP/3
Miscellaneous
HTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
httpwg.org 100% confidence
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain
Submit evidence & help protect others
VirusTotal Analysis
18 / 91 security vendors flagged this domain
View on VT
Last analyzed Previous stored snapshot: 19 detections
alphaMountain.ai
BitDefender
Cluster25
CRDF
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
LevelBlue
Lionic
Seclookup
SOCRadar
Sophos
VIPRE
Webroot
Technologies
5 high-confidence technologies identified
Vue.js
Nginx
HSTS
Cloudflare
HTTP/3
Cloudflare Radar
Evidence & External Reports
Security Analysis
Submitted Evidence Snapshot
Sent: Ledger records: 1
Case ID:
PD-20260717-4E71EB Recipient: abuse@namemart.com OSINT & Intelligence
DNS & Network
SEO & Domain
Were You Affected by This Site?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Action Fraud
Report fraud and cybercrime in England, Wales and Northern Ireland
Contact centre0300 123 2040
PhishDestroy listing review Not a law-enforcement report
Domain Appeal
Request a review if you own this domain and believe the listing is incorrect
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
Report to Your Local Authorities
Select your country to get official cybercrime contacts, or create a complaint draft →.
97-country directory
Template-based draft • optional AI wording assistance requires separate consent
Review and submit it yourself
Related Infrastructure & Reports
Infrastructure map · j68v.vip
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 4
Shared IP 154.39.104.144 6
Multiple reports share this IP.
 v36o.top
 j61j.vip
Same registrar: NameMart 6
 drugs.matanga.top
 74239.vip
 coinupw.com
Bet365 impersonation 8
These domains also target Bet365 users. View all Bet365 threats →
Recent threat reports 4
Recently added threat reports.
 xmr-mixer.com
Check Any Domain
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowReport Phishing
Submit suspicious domains to our threat database — protect the community
ReportLive Threat Feed
Recent phishing reports and observed availability changes
MonitorStay Informed, Stay Safe
Monitor live threats or contest this listing if you believe it's a false positive