


 ChainPatrol
 Web-Check
 SOCRadar
 LeakIX

Domain security and threat intelligence

j105e.vip
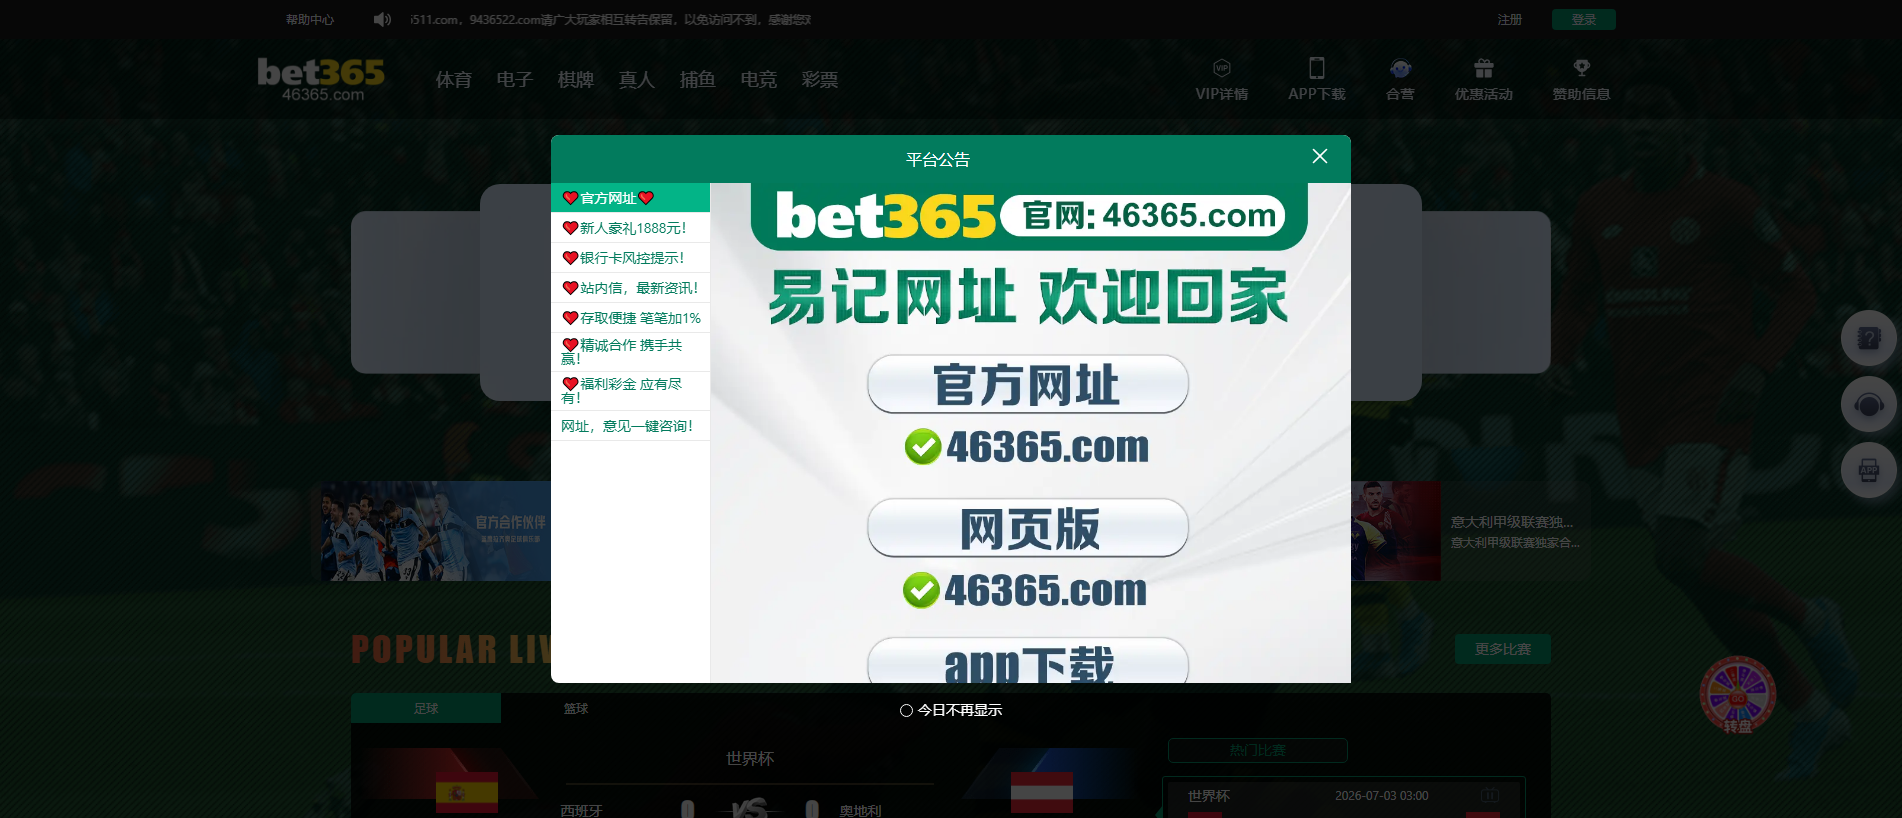
“welcome-BET365”
Threat verdict
Critical
95/100 evidence score
Availability
Content unavailable
Content was unavailable in the latest observation
Risk signals
VirusTotal detections: 19/91
Spamhaus DBL: DBL_SPAM
Brand impersonation: Bet365
Evidence Summary
CRITICAL
j105e.vip was registered on 26 June 2026 through NameMart Pte. Ltd. and is currently offline. The domain resolves to 154.39.104.138, an address owned by AS135357 Hong Kong Kowloon Telecommunications Co., Limited, placing the hosting infrastructure in Hong Kong. DNS resolution is provided by a set of six name servers (ns1.1111343.com, ns2.1111343.com, ns3.1111343.com, ns4., ns1.dnsbm.com, ns2.dnsbm.com), a pattern previously observed in other brand‑impersonation campaigns. The site presented the page title “welcome‑BET365”, directly referencing the targeted betting brand Bet365.
A Let's Encrypt certificate (YR2) was issued for the domain, indicating the site operated over HTTPS. Threat intelligence sources have flagged the domain: AlienVault OTX includes it in one pulse, VirusTotal recorded 19 positive detections out of 91 scanning engines, and at least one public blocklist lists it. PhishDestroy has also blocked the domain. The elevated risk rating reflects the combination of brand impersonation, active TLS, and multiple vendor detections.
Defenders should ensure that outbound web proxies, DNS filtering solutions, and endpoint URL reputation controls block both the domain name and its resolving IP. Monitoring for re‑registration of the same second‑level domain or for additional domains using the same name‑server set is recommended. Because the site is currently taken offline, incident response teams can focus on containment and on reviewing any logs for connections to 154.39.104.138 during the window of activity. Continuous ingestion of updates from OTX, VirusTotal, and the blocklist provider will help maintain coverage against potential re‑emergence.
VirusTotal
19 det.
URLQuery
3 det.
OTX references
URLScan
TLS Certificate
Let's Encrypt / YR2 18d
Age
3 mo New
Observed status
Content unavailable

DestroyList
Listed
Reports Sent
1
Data coverage
VirusTotal
19 / 91
URLQuery
3 det.
PhishStats
not checked
OTX
1 community reference
CF Radar
scan completed
URLScan capture
stored report
URLScan verdict
Analysis completed
DNS blocks
not checked
TLS
valid certificate, 18d
WHOIS
3 mo old
Screenshot
2 captures · 2 sources
Redirect chain
not probed
Threat Response Pipeline
Discovery
Checks
Reports
Availability
14/14
Sent Report Recorded
Stored sent-report record for registrar NameMart Pte. Ltd., hosting provider, 1 abuse contact
abuse@namemart.com
Public Blocklist Status
Submitted Evidence Snapshot
- Sent
- Ledger records
- 1
- Case ID
PD-20260702-D68897- Captured page title
- welcome-BET365
Blocklist coverage
11 monitored external feeds · stored snapshot Sep 10, 2026
Stored Capture
Domain Intelligence
Domain
URLScan Verdict
Analysis completed
score 0 report ↗
Server / ASN
Nginx · AS18186 NEBULA-GLOBAL - Nebula Global LLC, US
IP Reputation
abuse score 0/100 0 reports checked Jul 2, 2026
Registrar
NameMart
 (CN)
(CN)
IP Address
154.39.104.138

Geo Hong Kong, HK
Hong Kong, HKNetworkAS18186 · AS135357 HONG KONG KOWLOON TELECOMMUNICATIONS CO.,LIMITED
RegistrationCreated Jun 26, 2026 (75d · New) — Expires Jun 26, 2027
Technical detailsDNS, SSL SANs, timestamps
First DetectedJul 2, 2026
DOM Analysis
IoC Extraction
Submitted URLhttp://j105e.vip/
Nameserversns1.1111343.comns1.dnsbm.comns2.1111343.comns2.dnsbm.comns3.1111343.comns4.1111343.com
TLS Fingerprint
TLS Observation
TLS SAN Domainsb40e.topb40s.topb40t.topb41i.topb41j.topf36l.topf36n.topf36o.toph30e.toph30g.toph30m.toph30n.toph30o.topj101y.vipj101z.vip+84
Case ID
ICANN OVERSIGHT
Accreditation and RAA context
Accreditation and RAA context
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Accreditation is a contract, not a safety seal.
Verify ICANN fees
Read RAA §3.18
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Report This Domain
Submit evidence & help protect others
VirusTotal Analysis
19 / 91 security vendors flagged this domain
View on VT
Last analyzed Previous stored snapshot: 19 detections
BitDefender
Chong Lua Dao
Cluster25
CRDF
CyRadar
ESET
Emsisoft
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
LevelBlue
Lionic
Netcraft
OpenPhish
SOCRadar
Sophos
Webroot
Evidence & External Reports
Security Analysis
Submitted Evidence Snapshot
Sent: Ledger records: 1
Case ID:
PD-20260702-D68897 Recipient: abuse@namemart.com Page title stored with report: welcome-BET365
Blocklist hits included with submission: OpenPhish
OSINT & Intelligence
DNS & Network
SEO & Domain
Were You Affected by This Site?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Action Fraud
Report fraud and cybercrime in England, Wales and Northern Ireland
Contact centre0300 123 2040
PhishDestroy listing review Not a law-enforcement report
Domain Appeal
Request a review if you own this domain and believe the listing is incorrect
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
Report to Your Local Authorities
Select your country to get official cybercrime contacts, or create a complaint draft →.
97-country directory
Template-based draft • optional AI wording assistance requires separate consent
Review and submit it yourself
Related Infrastructure & Reports
Infrastructure map · j105e.vip
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 4
Shared IP 154.39.104.138 6
Multiple reports share this IP.
Same registrar: NameMart 6
 drugs.matanga.top
 g36b.top
 74239.vip
 coinupw.com
Bet365 impersonation 8
These domains also target Bet365 users. View all Bet365 threats →
Recent threat reports 4
Recently added threat reports.
 xmr-mixer.com
 capitalvaultpeak.com
Check Any Domain
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowReport Phishing
Submit suspicious domains to our threat database — protect the community
ReportLive Threat Feed
Recent phishing reports and observed availability changes
MonitorStay Informed, Stay Safe
Monitor live threats or contest this listing if you believe it's a false positive