Scamadviser
1/100
Trust score, lower = worse
Open report

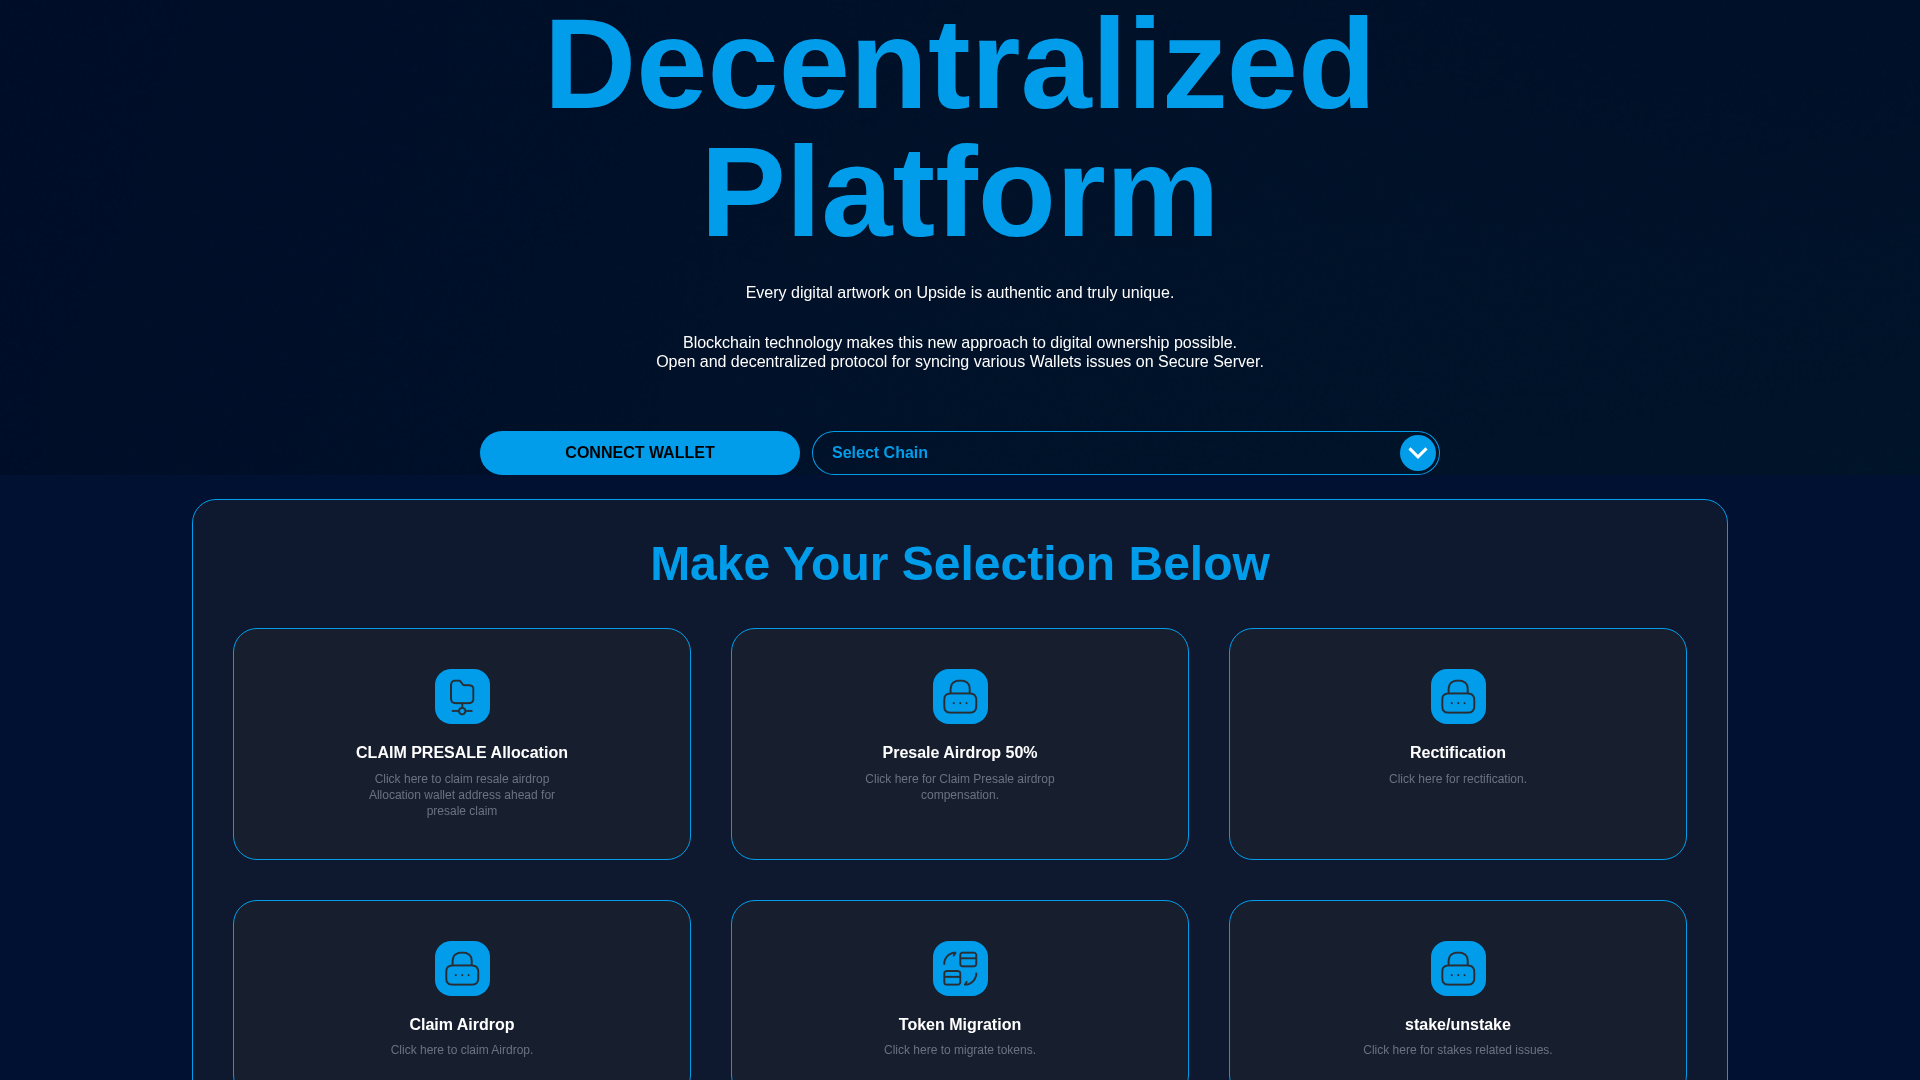
On 2026-11-12, authprotocol.pages.dev displayed a dark blue page headed "Decentralized Platform" with a subtitle stating that every digital artwork on Upside is authentic and truly unique, and describing an open and decentralized protocol for syncing various wallet issues on a secure server. A blue CONNECT WALLET button sits beside a Select Chain dropdown, and below a heading reading "Make Your Selection Below" are cards offering options such as CLAIM PRESALE Allocation, Presale Airdrop 50%, Rectification, Claim Airdrop, Token Migration, and stake/unstake.
Page title: “Decentralized Platform”
Listed by external blocklists: MetaMask, ScamSniffer, SEAL. Use caution — do not enter credentials or personal information.
 188.114.96.3CloudFlare, Inc. · CDN
Risk score, higher = worse · How this score works
Pick what happened and tick the steps as you go. The ticks are kept only in this browser.
Expert view has every section: DNS, TLS, network requests, hashes and the raw JSON.
PhishDestroy first recorded authprotocol.pages.dev on 2026-11-12. Listed by external blocklists: MetaMask, ScamSniffer, SEAL. Risk: critical (evidence score 79/100). Status: Reachable · access restricted. Hosting: Cloudflare, Inc. Do not enter credentials or connect a wallet.
188.114.96.3CloudFlare, Inc. · CDN Cloudflare Radar capture · 2026-11-12 07:20 UTC · SHA-256 495546a7…c1d5bad
PhishDestroy analysis, reviewed version
On 2026-11-12, authprotocol.pages.dev displayed a dark blue page headed "Decentralized Platform" with a subtitle stating that every digital artwork on Upside is authentic and truly unique, and describing an open and decentralized protocol for syncing various wallet issues on a secure server. A blue CONNECT WALLET button sits beside a Select Chain dropdown, and below a heading reading "Make Your Selection Below" are cards offering options such as CLAIM PRESALE Allocation, Presale Airdrop 50%, Rectification, Claim Airdrop, Token Migration, and stake/unstake.
The stored VirusTotal domain result reports 0 detections out of 92 engines.
1/100
Trust score, lower = worse
Open reportScan report
Open reportThis summary differs from the dated scan above. It is retained for provenance and does not override the selected source observation.
Page capture
SHA-256 44ec1786…88e0fb5
Separate stored monitor snapshot; does not replace the primary report record or establish current availability.
25 / 100 · heuristic score · 3 brand references · 1 classification
Content heuristic only; not the final score
Open reportThis dated monitor analysis is separate from the primary PhishDestroy analysis above. A heuristic score is not a measured probability.
Narrative generation metadata
Open reportThe narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.
Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
Stored page, network and scanner observations, grouped by source and observation time.
| Mail configuration | Spf lookups: 0 |
|---|---|
| Protective DNS results | Resolvers: 12; Blocked count: 0 |
| Page title and metadata | Title: Decentralized Platform |
| Trackers | Requests: 19 |
| Forms and mixed content | Third party scripts: 0 |
| Status | Up: ✓; Code: 200; Timings: DNS: 2; TLS: 23; Wait: 54; Connect: 9; Download: 0; Response ms: 88 |
| TLS connection | Alpn: h2; Cipher: TLS_AES_256_GCM_SHA384; Protocol: TLSv1.3; Versions: TLSv1.2, TLSv1.3; Authorized: ✓; Forward secrecy: ✓ |
| Ports | Open: 80, 443, 8080 |
| Carbon | Bytes: 20310; Co2 grams: 0.0007; Cleaner than: 56 |
| DNS server | NS: (IP: 173.245.58.103; Host: beth.ns.cloudflare.com), (IP: 172.64.33.145; Host: tim.ns.cloudflare.com); Zone: authprotocol.pages.dev |
| Location | IP: 2a06:98c1:3121::3; ASN: 13335; Org: CloudFLARENET-EU; City: London; Country: GB |
| SSL | Issuer: Let's Encrypt / YE2; Subject: authprotocol.pages.dev |
| DNS records | A: 188.114.97.3, 188.114.96.3; NS: beth.ns.cloudflare.com, tim.ns.cloudflare.com; Soa: Nsname: beth.ns.cloudflare.com; Hostmaster: dns.cloudflare.com; Serial: 2419547811; Refresh: 10000; Retry: 2400; Expire: 604800; Minttl: 1800; Aaaa: 2a06:98c1:3120::3, 2a06:98c1:3121::3 |
| Dnssec | Ds: ✗; Rrsig: ✗; Dnskey: ✗ |
| Hsts | Message: Site does not serve any HSTS headers. |
| HTTP security policies | Xframeoptions: ✗; Referrerpolicy: strict-origin-when-cross-origin; Xxssprotection: ✗; Permissionspolicy: ✗; Xcontenttypeoptions: nosniff; Contentsecuritypolicy: ✗; Stricttransportpolicy: ✗; Crossoriginopenerpolicy: ✗; Crossoriginembedderpolicy: ✗; Crossoriginresourcepolicy: ✗ |
| Firewall | Waf: Cloudflare; Has waf: ✓ |
| Get IP | IP: 2a06:98c1:3120::3; Family: 6 |
| Redirects | Chain: https://authprotocol.pages.dev |
| Tech stack | Technologies: HSTS, Cloudflare, HTTP/3 |
| HTTP headers | Headers: Server: cloudflare; Content type: text/html; charset=utf-8; X content type options: nosniff; Referrer policy: strict-origin-when-cross-origin |
 Scamadviser Warnings 1/100
PhishDestroy rates authprotocol.pages.dev as critical risk (evidence score 79/100) from the recorded evidence; it was first recorded on 2026-11-12. Listed by external blocklists: MetaMask, ScamSniffer, SEAL. The local score and a listing do not prove fraud. Check each source’s date and the exact URL.
Because of the risk signals above, do not connect a wallet, sign messages or approve token permissions on authprotocol.pages.dev. A confirmed blockchain transaction cannot be reversed.
Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority. A report does not guarantee that money is returned. Step-by-step help: emergency guide.
Last checked
495546a7…c1d5bad SHA-256 of the prepared copy given to the model: 2b5906a2…28d9ed4 495546a76dda81c9bf6c87f56e976b8d4fca49b866b58e9bbb5ccba99c1d5bad · 388539 bytes f83c42ac0dee4ce6fc3acfe016c5c515de51def1e038c0539c6d337d61d52c94 · 258290 bytes 188.114.96.3 Cloudflare shared edge origin IP hidden Edge-IP reputation is not attributed to this domain. 188.114.96.3Toronto, CAEdge-IP reputation is not attributed to this domain.
beth.ns.cloudflare.comtim.ns.cloudflare.comnsname: beth.ns.cloudflare.comhostmaster: dns.cloudflare.comserial: 2419547811refresh: 10000retry: 2400expire: 604800minttl: 1800Location describes the IP network.
c69f2965a18ab585d52bb40d3af69955c06adbee7fccc6b2de61d12f80c00a86*.authprotocol.pages.devauthprotocol.pages.devSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of authprotocol.pages.dev ·
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Network requests: 24 SHA-256 hashes: 23 URLScan scan:
Network requests that the URLScan browser recorded while loading the page. URLScan does not provide a hash for every request. PhishDestroy retrieved this list on 2026-11-12 07:19 UTC.
Open this scan on URLScan 01a1ce9b-a891-721e-ae95-659473e121a0 ↗
Loads saved data; the suspicious site is not opened.
| # | Network request | HTTP method · status | Type | Uncompressed size | Response body SHA-256 |
|---|
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
Our scanner could not complete this check.
authprotocol.pages.dev Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Blocked
Cloudflare antiphishing · Cloudflare · Phishing interstitial
Blocked
Cloudflare antiphishing · Cloudflare · Phishing interstitial
Blocked
Cloudflare antiphishing · Cloudflare · Phishing interstitial
Blocked
Cloudflare antiphishing · Cloudflare · Phishing interstitial
Blocked
Cloudflare antiphishing · Cloudflare · Phishing interstitial
Blocked
Cloudflare antiphishing · Cloudflare · Phishing interstitial
Reachable→Unavailable
Reachable
Recorded events: 10. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
Lifecycle
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
 GoogleSafe Browsing↗ GoogleWeb Risk↗
 MicrosoftSmartScreen↗
 VirusTotalURL analysis↗
 CloudflareRadar / abuse reporting↗
 YandexSafe Browsing↗
 URLScan.ioPublic scan↗
 ESETSample / URL submission↗
 BitdefenderURL submission↗
 NortonSafe Web↗
 SymantecSiteReview↗
 AviraURL reporting↗
 Avast / AVGURL reporting↗
 KasperskyOpenTIP↗
 Dr.WebOnline scanner↗
 NetcraftAbuse reporting↗
 PhishTankCommunity reporting↗
 APWG eCXPhishing intelligence↗
 PhishStatsPublic feed↗
 Phish.ReportHosting abuse↗
 SpamhausDomain reputation↗
 PolySwarmMulti-engine analysis↗
 CheckPhishURL scan↗
 QutteraMalware scan↗
 URLqueryBrowser analysis↗
 Criminal IPAsset intelligence↗
 CRDFThreat Center↗ ScamadviserReputation check↗
 MyWOTCommunity reputation↗
Browse this domain’s complete history by source. The download includes every record of the selected source. Dates retain their original field labels.
Download all records as JSON| ID | Stored data |
|---|
239 stored lookalike domains
Names that imitate the brand, found by dnstwist. A similar name alone does not prove the same owner.
A similar name alone does not prove fraud. Send the list to services that check each address themselves. Report a domain as phishing only if you saw a fake page on it.
Where to send it:
Nothing matches. Clear the search or choose another filter.
Showing 12 of 239
Showing 100 of 239
Same favicon Supporting signal 3
Similar title Supporting signal 4
Each spoke is one reason a domain is linked to this report. Node size marks VirusTotal detections, dashed nodes are already offline, and the full lists follow below. Full list of related reports
Same favicon file hash, or a recorded page title that starts with the same 20 characters. A content match does not establish a shared phishing kit or owner.
Shared with 3 other domains
Act on what you actually did. Entered a password: change it, and wherever you reused it. Paid or gave card details: contact your bank or payment service. Downloaded a file: scan the device. Then report the incident.
The draft stays only with you.
First secure your money: call your bank or revoke wallet approvals. Immediate steps →



Emergency help from security researchers when a crypto wallet is being drained right now.

Report scams and fraud to the US Federal Trade Commission. Reports go into a database used by law enforcement.


Report cyber incidents and phishing to the US Cybersecurity and Infrastructure Security Agency.

Forward scam emails and text messages to the National Cyber Security Centre, which takes down the malicious sites it finds.
Emailreport@phishing.gov.uk Text messages7726
Directory of national incident response teams (CSIRTs) in the EU. Find the team for your country.

Forward phishing emails to the Anti-Phishing Working Group.
Emailreportphishing@apwg.org
National Cyber Crime Reporting Portal. For financial fraud, also call the 1930 helpline straight away.
Helpline1930


Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
authprotocol.pages.dev)Even if you don't have all details — file a report anyway. Partial information still helps investigations.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.