


 ChainPatrol
 Web-Check
 SOCRadar
 LeakIX

ABUSE NOTICE · 7D+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse-reports@cloudzy.com.
The latest stored availability evidence still shows the domain reachable; 2 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
2 months
Reports sent
1
Latest case ID
PD-20260612-7C385E
Current status
Observed active at latest stored check
Domain security and threat intelligence

140bae[.]senes[.]at
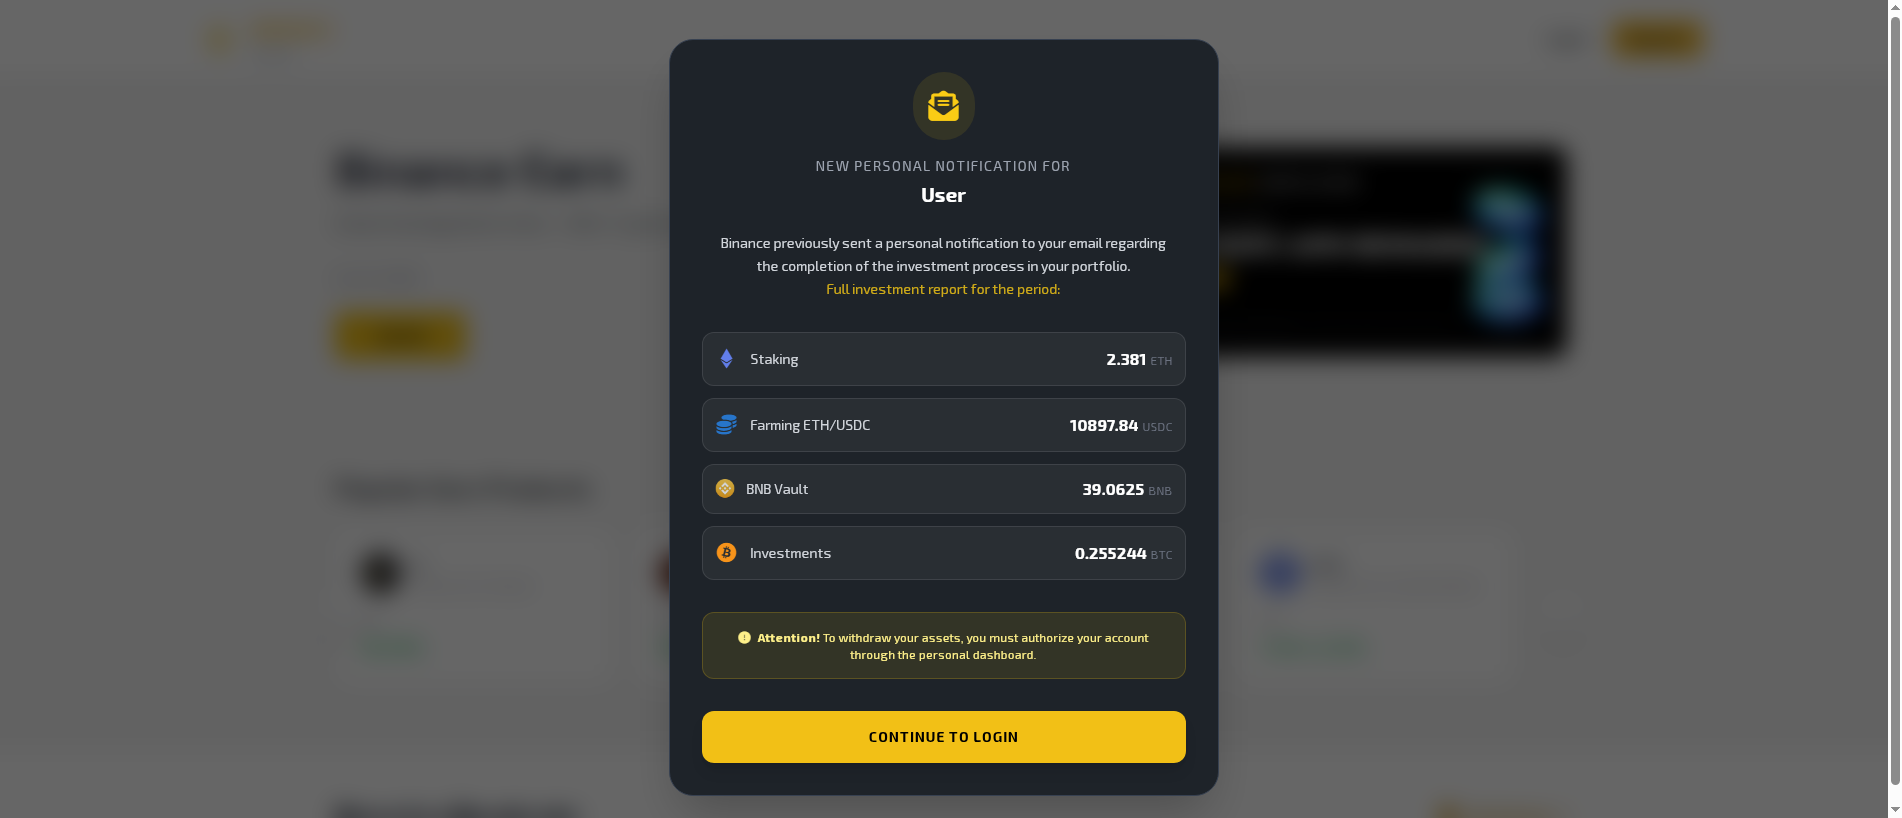
“Binance”
Threat verdict
Critical
95/100 evidence score
Availability
Unverified
Current reachability is unverified
Risk signals
VirusTotal detections: 19/91
Spamhaus DBL: DBL_PHISH
URLQuery threat systems: 5 alerts
Brand impersonation: Binance
Evidence Summary
CRITICAL
This domain, 140bae.senes.at, is flagged as a generic phishing site. It poses a significant risk of credential theft and financial fraud. Users should avoid interacting with this domain to prevent potential security breaches and personal data loss.
Analysis of the domain indicates that it has been flagged by 18 out of 95 security vendors on VirusTotal, suggesting a consensus among security experts that the site is malicious. The domain was created on June 12, 2026, and is currently offline, which can be a tactic used by attackers to avoid detection and maintain the threat's longevity. The SSL certificate is issued by Let's Encrypt / R13, a commonly used certificate authority that does not verify the legitimacy of the domain, making it easier for attackers to mimic legitimate sites.
If a user has visited 140bae.senes.at, it is recommended to immediately change passwords for any accounts that may have been compromised. Conduct a full system scan using up-to-date antivirus software to detect and remove any malicious software that may have been installed. Additionally, monitor financial and personal accounts for any unusual activity. Users should also consider enabling two-factor authentication (2FA) on their important accounts to add an extra layer of security.
VirusTotal
19 det.
URLQuery
5 threat alerts
URLScan
TLS Certificate
Expired or unverified -55d
Age
3 mo New
Observed status
Unverified

DestroyList
Listed
Reports Sent
1
Data coverage
VirusTotal
19 / 91
URLQuery
5 threat-system alerts
PhishStats
not checked
OTX
no community references
CF Radar
no data
URLScan capture
stored report
URLScan verdict
Analysis completed
DNS blocks
not checked
TLS
Expired or unverified
WHOIS
3 mo old
Screenshot
3 captures · 3 sources
Redirect chain
not probed
Network Security Intelligence
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | 140bae.senes.at |
malicious | Sinkholed |
| DNS4EU | 140bae.senes.at |
malicious | Sinkholed |
| OpenDNS | 140bae.senes.at |
phishing | Phishing Block |
| Hagezi Threat Feed | 140bae.senes.at |
malicious | Sinkholed |
| Quad9 DNS | 140bae.senes.at |
malicious | Sinkholed |
Threat Response Pipeline
Discovery
Checks
Reports
Availability
10/11
Sent Report Recorded
Stored sent-report record for domain registrar, hosting provider, 1 abuse contact
abuse-reports@cloudzy.com
Public Blocklist Status
Stored Capture
Domain Intelligence
Domain
URLScan Verdict
Analysis completed
score 0 report ↗
Server / ASN
nginx · AS30823 aurologic GmbH
IP Reputation
abuse score 0/100 1 report checked Aug 12, 2026
Registrar (base domain)
Unknown
 (AUSTRIA)
IP Address
172.86.95.123

Registration (base domain)senes.at · Created Jun 12, 2026 (84d · New)
Technical detailsDNS, SSL SANs, timestamps
First DetectedJun 12, 2026
IoC Extractionscanned Aug 1, 20260 wallet · 0 Telegram IoCs
Submitted URLhttp://140bae.senes.at/bncearn/incnb.php
Nameserversa.dnspod.comc.dnspod.com
TLS Fingerprint
TLS Observationvalid from Apr 13, 2026scanned Jun 12, 2026
TLS SAN Domainssenes.at
Case ID
Report This Domain
Submit evidence & help protect others
VirusTotal Analysis
19 / 91 security vendors flagged this domain
View on VT
Last analyzed Previous stored snapshot: 21 detections
alphaMountain.ai
BitDefender
Chong Lua Dao
CyRadar
ESET
Emsisoft
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
Lionic
MalwareURL
Netcraft
Seclookup
SOCRadar
Sophos
VIPRE
Webroot
Evidence & External Reports
Security Analysis
Submitted Evidence Snapshot
Sent: Ledger records: 1
Case ID:
PD-20260612-7C385E Recipient: abuse-reports@cloudzy.com Page title stored with report: Binance
OSINT & Intelligence
DNS & Network
SEO & Domain
Were You Affected by This Site?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Action Fraud
Report fraud and cybercrime in England, Wales and Northern Ireland
Contact centre0300 123 2040
PhishDestroy listing review Not a law-enforcement report
Domain Appeal
Request a review if you own this domain and believe the listing is incorrect
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
Report to Your Local Authorities
Select your country to get official cybercrime contacts, or create a complaint draft →.
97-country directory
Template-based draft • optional AI wording assistance requires separate consent
Review and submit it yourself
Related Infrastructure & Reports
Shared IP 172.86.95.123 3
Multiple reports share this IP.
Binance impersonation 8
These domains also target Binance users. View all Binance threats →
Recent threat reports 6
Recently added threat reports.
 trusthora.online
 bancaenlinea.co
 promo-p.org
 nova-play.org
 origin-protocol.org
Check Any Domain
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowReport Phishing
Submit suspicious domains to our threat database — protect the community
ReportLive Threat Feed
Recent phishing reports and observed availability changes
MonitorStay Informed, Stay Safe
Monitor live threats or contest this listing if you believe it's a false positive