Zum Sicherheitsbericht springen

innovastasset.com

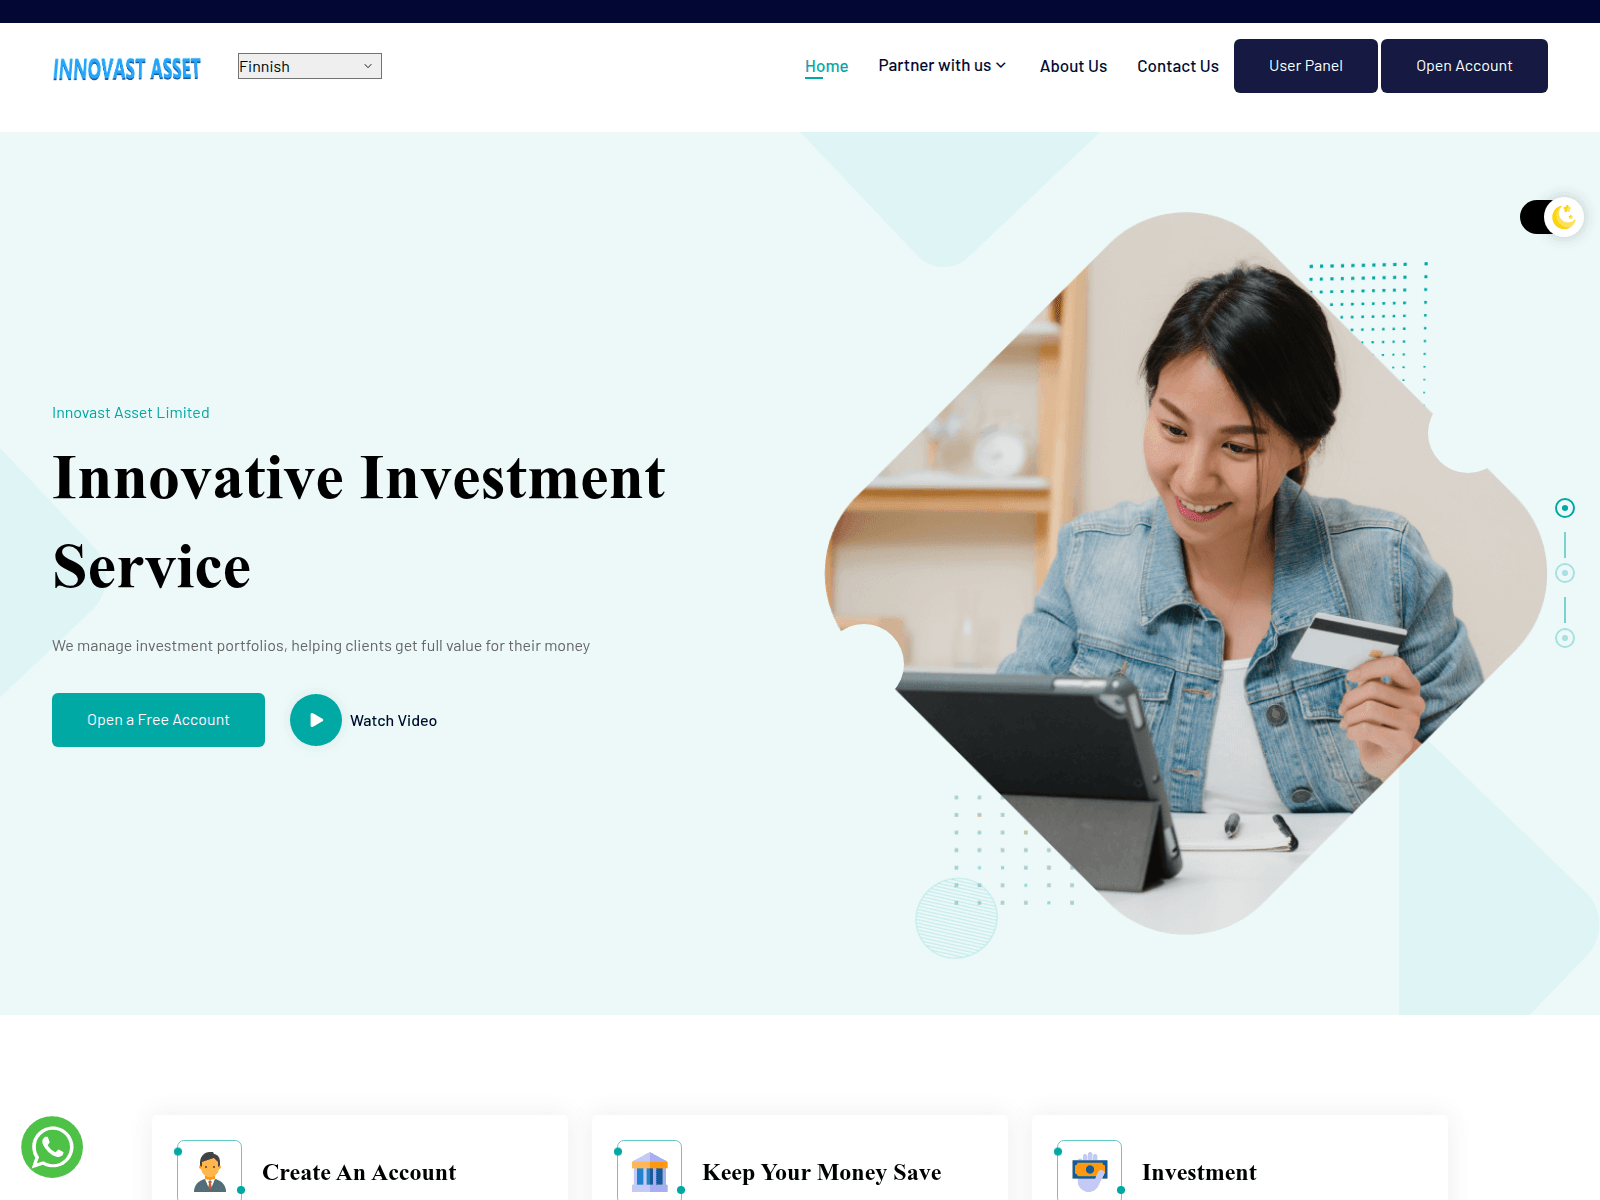
Page title: “Innovast Asset Limited - Online Investment Company”

Availability last checked First listed 26.02.2026 VirusTotal analysed Feb 24, 2026 UTC

PhishDestroy verdict Hoch 68/100 evidence score

Based on 1 recorded source signal. The score is a heuristic over stored detections, not a probability or confidence level.

View evidence
Availability · last observation Inhalt nicht verfügbar

Der Inhalt war in der letzten Beobachtung nicht verfügbar

· Source: HTTP probe

Reachability is not a safety rating.

Key evidence

  • VirusTotal-Erkennungen: 6/93
Registered
21.02.2026
IP
102.209.117.141
Stored capture 1 of 2 · Feb 26, 2026 UTC · Primary capture OpenAll capturesWayback

Evidence

Source checks and detection results recorded for this domain, with the time each was observed.

Berichtsübersicht

innovastasset.com — Inhalt nicht verfügbar. Zusammenfassung der Beweislage: VirusTotal 6/93 (alphaMountain.ai, CyRadar, Fortinet, Kaspersky, Netcraft); PhishDestroy score 68/100.

Die ausführliche Analyse von PhishDestroy AI bleibt auf Englisch, damit der ursprüngliche forensische Bericht unverändert bleibt.

Source evidence

8 sources

VirusTotal

6 / 93

Melden

URLQuery

Report stored; detailed verdict not recorded

Melden

OTX

no community references

Melden

CF-Radar

provider verdict: safe

Melden

URLScan capture

gespeicherter Bericht

Stored URLScan capture preview
Melden

URLScan verdict

Analyse abgeschlossen

Melden

DNS-Sperren

14 geprüft — keine Sperren

Google Safe Browsing

Checked; no threat flag recorded

Melden
Detailed resultsVirusTotal vendor list · written summary · threat-intel cross-reference · cloaking analysis

Evidence summary

Stored written summary, generated Jun 18, 2026. It is not updated when source results change.

This summary quotes VirusTotal 6/95. The current stored result is 6/93 (analysed Feb 24, 2026).

PhishDestroy identifies innovastasset.com as a generic phishing domain posing as Innovast Asset Limited, an online investment company, potentially utilizing a credential theft kit to deceive victims.

Read full summary

This domain was flagged due to its suspicious nature, with a VirusTotal score of 6/95, registered with an unknown registrar, resolving to the IP address 102.209.117.141, created on February 21, 2026, and currently having a Google Safe Browsing status of not available, while being listed on 1 security blocklist.

The current status of innovastasset.com is offline, however, the risk level remains elevated, as the domain may be reactivated or similar domains may be created to continue the phishing campaign, therefore, users are advised to remain cautious and avoid interacting with any suspicious emails or links related to Innovast Asset Limited, and to report any similar incidents to the relevant authorities to ensure their safety and security.

VirusTotal-Analyse

6 / 93 Sicherheitsanbieter haben diese Domain markiert
View on VT
Last analyzed
alphaMountain.ai
CyRadar
Fortinet
Kaspersky
Netcraft
Sophos
Analyse von Erkennung und Umgehung

Überprüfung der Cloaking- und Traffic-Verteilung

Noch nicht eingescannt Bislang wurde noch kein Unterschied zwischen Crawler und Browser festgestellt.

Gespeicherte Beobachtungen zum Vergleich zwischen Crawler und Browser für diesen Host sowie eine Echtzeit-Fingerabdruckprüfung für Verkehrsverteilungssysteme im Keitaro-Stil.

Gespeichertes Cloaking-Flag
Noch nicht eingescannt
Letzter Tarnungsscan

Anmerkung des Scanners: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='innovastasset.com', port=80): Max retries exceeded with url: / (Caused by NewConnectionErr

Live-TDS-Fingerabdruckprüfung
Sieben Keitaro-Fingerabdrücke sowie ein Vergleich zwischen Crawler und Browser, der vom „PhishDestroy“-Scanner ausgeführt wird, wenn dieses Fenster geöffnet ist.
Warten

Domain & infrastructure

registered 21.02.2026 · IP 102.209.117.141 · TLS R10

Domain details

Domain
URLScan Verdict Analyse abgeschlossen score 0 report ↗
IP-Reputation abuse score 0/100 1 report checked 15.06.2026
RegistrierungErstellt 21.02.2026 (235d)
Zeit bis zur ersten Nichtverfügbarkeit 132 days
Was wir zählen Verstrichene Zeit von der ersten gespeicherten Missbrauchsmeldung bis zur ersten Feststellung, dass der Inhalt nicht verfügbar war. Damit ist die Ursache nicht geklärt.
Was jeder Bericht enthält Gespeicherte Ausgangsberichtsaufzeichnungen können auf zu diesem Zeitpunkt verfügbare Beweise verweisen, wie z. B. Urteile von Anbietern, Registrierungsdaten, Hosting-Details, Klassifizierungen oder Screenshots. Diese Seite lässt keine Rückschlüsse auf die genaue zugestellte Nutzlast, den Empfang, die Bestätigung oder die Aktion eines Empfängers zu.
Technische DetailsProvenance & timestamps
Erstmals entdeckt26.02.2026
DOM Analysisanalyzed 29.07.2026score 63/100

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
102.209.117.141
Network ASN
AS329184
Organization
Host Africa (Pty) Ltd
Observed location
Johannesburg, ZA
Server header
LiteSpeed

Location describes the IP network.

TLS-Zertifikat

Issuer
R10
Hostname coverage
Hostname coverage not recorded
Collection source
PhishDestroy collector

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Technologien · 2 identified
Detected via Cloudflare Radar · Wappalyzer engine
Website-Performanceanalyse

Google PageSpeed Insights — mobile performance audit of innovastasset.com · checked Mar 2, 2026

100
Good
Performance
FCP
0.75s
First Contentful Paint
LCP
0.75s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
0.91s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Aufnahmen

2 stored captures

Gespeicherte Aufnahme · 2 captures

Seitentitel
Innovast Asset Limited - Online Investment Company
TLS-Zertifikat
Hostname coverage not recorded · Ausgestellt von R10

Reports & history

No abuse reports recorded · first listed 26.02.2026 · detection timeline

Latest Classified Outcome 2026-10-14 20:21:26 UTC

Primary outcome DNS inaktiv reason: DNS NXDOMAIN 80% confidence
Attribution source: Dns Cache
Evidence layers Availability: DNS inactive Content: Unreachable DNS: NXDOMAIN Registration: Unknown
Latest HTTP observation Unbekannt Probe Inconclusive 20% 2026-10-13 01:10:12 UTC
RDAP registration Unbekannt
Observed timeline last reachable: 2026-03-16 05:05:04 UTC current episode first observed: 2026-09-30 16:14:55 UTC observed RIP window: 2026-03-16 05:05:04 UTC → 2026-09-30 16:14:55 UTC · 4,763.16h midpoint estimate ≈ 2026-06-23 10:39:59 UTC · precision very low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Cloudflare Radar Scan 2026-03-02 21:02:22 UTC
    Cloudflare Radar scan registered: View Radar report.

Pipeline zur Reaktion auf Sicherheitsbedrohungen

Entdeckung
Analysis
Monitoring

10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Community-Meldungen

Von 1 Community-Mitglied gemeldet; erstmals gesehen am 09.08.2025

Gespeicherte Meldungen
1
Eindeutige gemeldete URLs
1
Akzeptiert1

Get help

Official reporting channels, a complaint draft, and listing review

Wurden Sie von dieser Website betroffen?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Wenn Sie Kontoanmeldeinformationen, persönliche oder Zahlungsinformationen eingegeben oder eine Datei von dieser Domain heruntergeladen haben, ergreifen Sie sofort Maßnahmen. Nachfolgend finden Sie Ressourcen, die Ihnen helfen, den Vorfall zu melden und sich zu schützen.

Europol
Finden Sie den offiziellen Meldekanal für Ihr EU-Land
National police directory
Vorsicht vor Betrügern, die mit der Rückforderung von Geldern locken! Kriminelle nehmen unter Umständen erneut Kontakt zu Opfern auf und geben dabei vor, Ermittler, Anwälte oder Beitreibungsbeamte zu sein. Zahlen Sie keine Vorabgebühren und geben Sie keine Anmeldeinformationen weiter. Erfahren Sie mehr über Betrug im Zusammenhang mit Wiederaufbaumaßnahmen →

Melden Sie sich bei Ihren örtlichen Behörden

Wählen Sie Ihr Land aus, um Offizielle Kontakte im Bereich Cyberkriminalität oder einen Beschwerdeentwurf erstellen → zu erhalten.

97-Länder-Verzeichnis
KI-gestützter Entwurf – Vorfalldetails werden vom KI-Anbieter verarbeitet · Überprüfen Sie es und reichen Sie es selbst ein

Tools & export

External lookups, JSON / PDF export, API and embed code
Analyze on destroy.tools Run a fresh external analysis of innovastasset.com (opens in a new tab)

Nachweise und externe Berichte

Eingehende Analyse
HTML · IFRAME

Diesen Bericht einbetten

Teilen Sie diese Bedrohungsinformationen auf Ihrer Website oder in Ihrem Blog

embed.html
<iframe
  src="https://phishdestroy.io/de/embed/domain/innovastasset.com"
  title="PhishDestroy threat report for innovastasset.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>

Jede beliebige Domain prüfen

Bedrohungsanalyse anhand gespeicherter Blocklisten, WHOIS, DNS und öffentlicher Scan-Beweise

Jetzt scannen

Phishing melden

Melden Sie verdächtige Domains an unsere Bedrohungsdatenbank – schützen Sie die Community

Melden

Echtzeit-Bedrohungsfeed

Aktuelle Phishing-Meldungen und beobachtete Verfügbarkeitsänderungen

Überwachen

Bleiben Sie auf dem Laufenden, bleiben Sie sicher

Beobachten Sie aktuelle Bedrohungen oder legen Sie Widerspruch gegen diesen Eintrag ein, wenn Sie der Meinung sind, dass es sich um einen Fehlalarm handelt

Echtzeit-Bedrohungsfeed Einspruch gegen diesen Eintrag einlegen