VirusTotal
2 / 95
إبلاغ


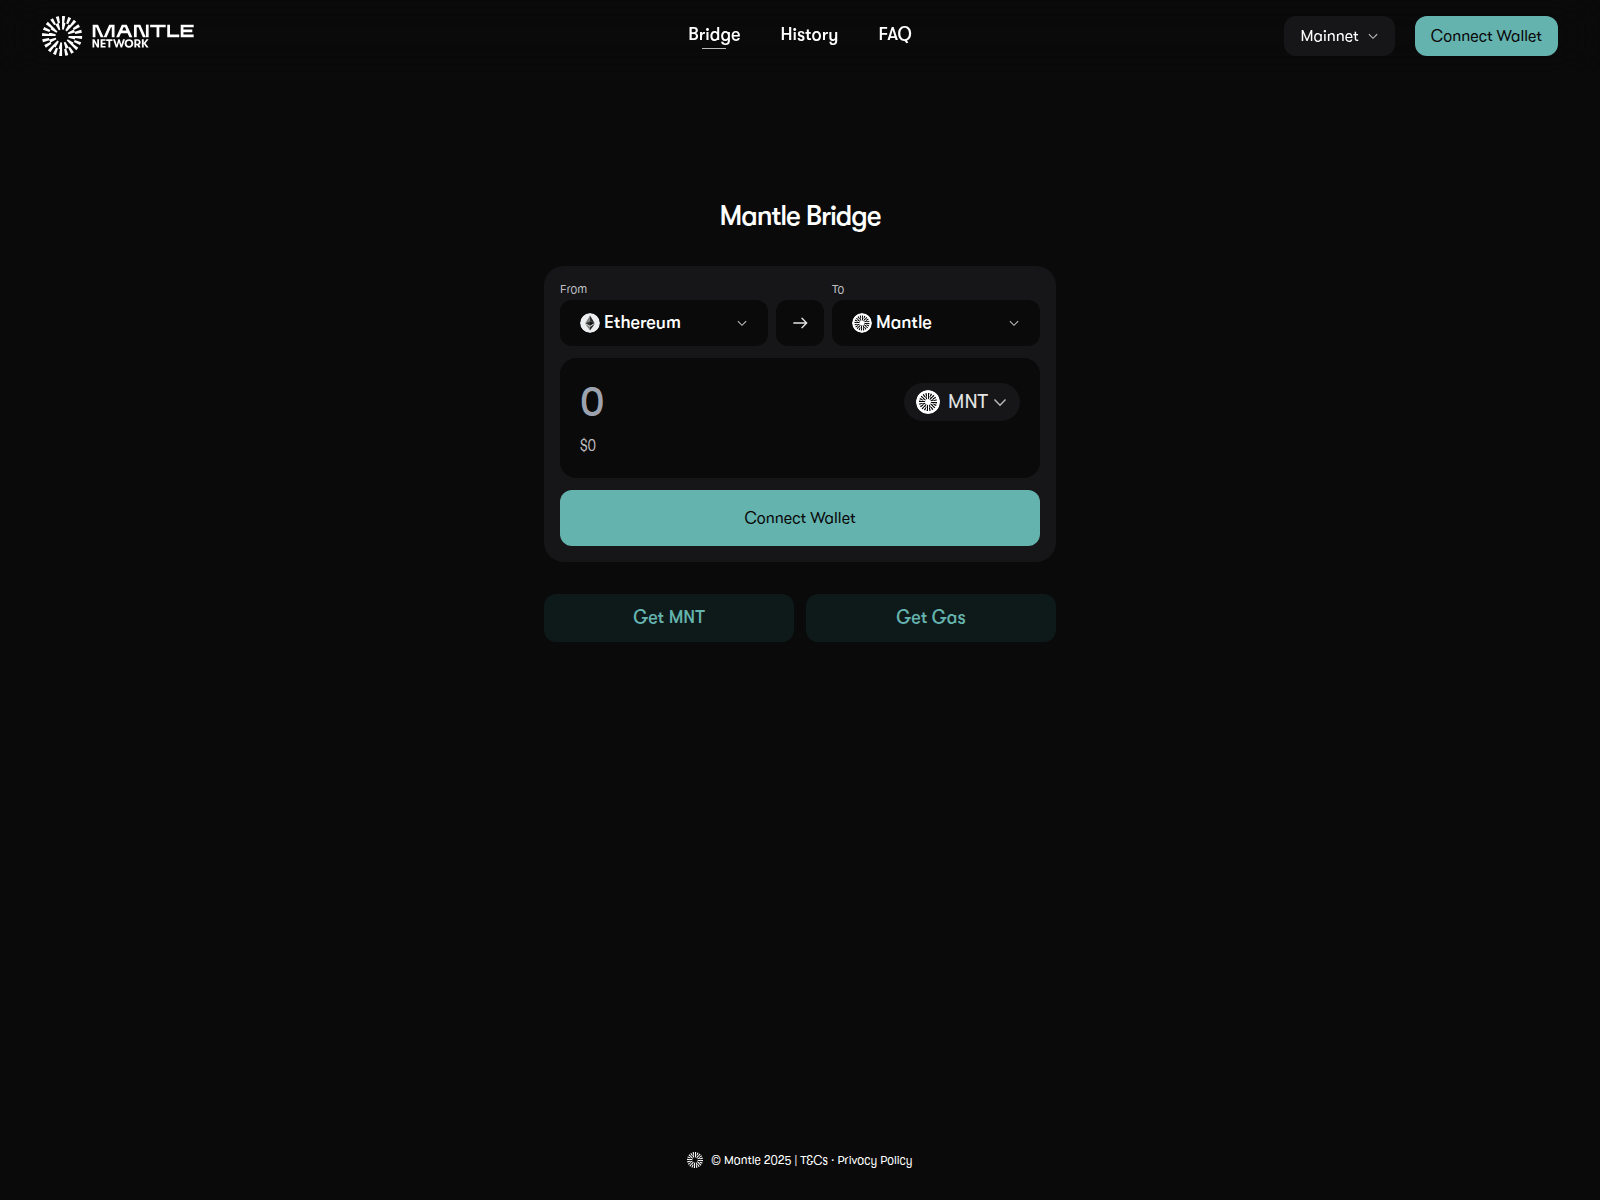
“Bridge Your Rocket-Fueled Assets Seamlessly with Mantle Bridge”
duplicate-disabled-11076.invalid — المحتوى غير متوفر. انتحال العلامة التجارية: Mantle; نوع الاحتيال: Wallet/seed Phishing; Drainer: Angel Drainer. ملخص الأدلة: VirusTotal 2/95 (G-Data, SOCRadar); PhishDestroy score 85/100. مسجّل النطاق: NameSilo.
يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.
The domain www.mantlew.org, impersonating the brand Mantle, has a high threat score of 70/100 and is currently down. It has been flagged as malicious by 2 out of 95 security vendors, including G-Data and SOCRadar, and is listed on one public blocklist. Google Safe Browsing has not flagged this domain, indicating it may not have been widely recognized yet. The domain is associated with the Angel Drainer crypto scam.
Registered with NameSilo, LLC, the domain was created on September 12, 2025, and first detected on September 24, 2025. The hosting IP is 104.21.23.212. Given the high threat level, block the domain at the perimeter and submit a report to the registrar's abuse desk.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
https://t.me/mantlenetworkStored page referenceIoC extraction recorded 2026-08-02 04:37:02 UTC
الملاحظات المخزنة المتعلقة بالمقارنة بين برامج الزحف والمتصفح لهذا المضيف، بالإضافة إلى فحص مباشر للبصمة الرقمية لأنظمة توزيع حركة المرور على غرار «كيتارو».
ملاحظة خاصة بالماسح الضوئي: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='duplicate-disabled-11076.invalid', port=80): Max retries exceeded with url: / (Caused by N
 (US)
PhishDestroy Investigation
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
لا تُنسب سمعة Edge-IP إلى هذا المجال.
bethany.ns.cloudflare.comnoah.ns.cloudflare.comLocation describes the IP network.
11 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
إذا تفاعلت مع هذا المجال، أو أدخلت معلومات شخصية، أو قمت بالاتصال بمحفظة عملة مشفرة، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.


حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.
Template-based draft · optional AI wording assistance requires separate consent
كل مسار يمثل سببًا واحدًا لربط نطاق ما بهذا المضيف. يشير حجم العقدة إلى عمليات الكشف التي أجرتها VirusTotal، أما العقد المتقطعة فهي غير متصلة بالإنترنت بالفعل. وترد القوائم الكاملة أدناه.
نفس هاش أيقونة المفضلة أو نفس عنوان الصفحة الخاص بهذا المضيف.
يتم حل هذه التقارير إلى نفس عنوان IP للحافة المشتركة. إنها تساعد في اكتشاف التقارير ولكنها لا تتضمن ملكية مشتركة أو خادم أصل مشترك.
كما تستهدف هذه النطاقات مستخدمي موقع Mantle. عرض جميع التهديدات المتعلقة بـ «Mantle» →
تم تسجيلها عبر نفس الجهة المسجلة. وتقدم الجهة المسجلة خدماتها لملايين العملاء الذين لا تربطهم أي صلة ببعضهم البعض، لذا فإن هذا الأمر يُشير إلى وجود تجميع للتقارير وليس دليلاً على وجود صلة بينهما.
التقارير المضافة مؤخرًا من قاعدة بيانات PhishDestroy. لا تتضمن روابط الاكتشاف هذه بنية تحتية أو ملكية مشتركة.
تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة
امسح الآنأرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع
إبلاغتقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة
مراقبةراقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب
يُقدَّر أن $51 billion تدفقت إلى محافظ عملات مشفرة غير مشروعة في عام 2024 (source). إذا كنت قد تفاعلت مع duplicate-disabled-11076.invalid — تصرف الآن.
وفقًا لـ مكتب التحقيقات الفيدرالي (FBI)، وأهم التفاصيل هي بيانات المعاملات:
0x5856...35985)duplicate-disabled-11076.invalid)حتى لو لم تكن جميع التفاصيل متوفرة — تقديم بلاغ على أي حال. فحتى المعلومات الجزئية تساعد في التحقيقات.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.