记录来源摘要
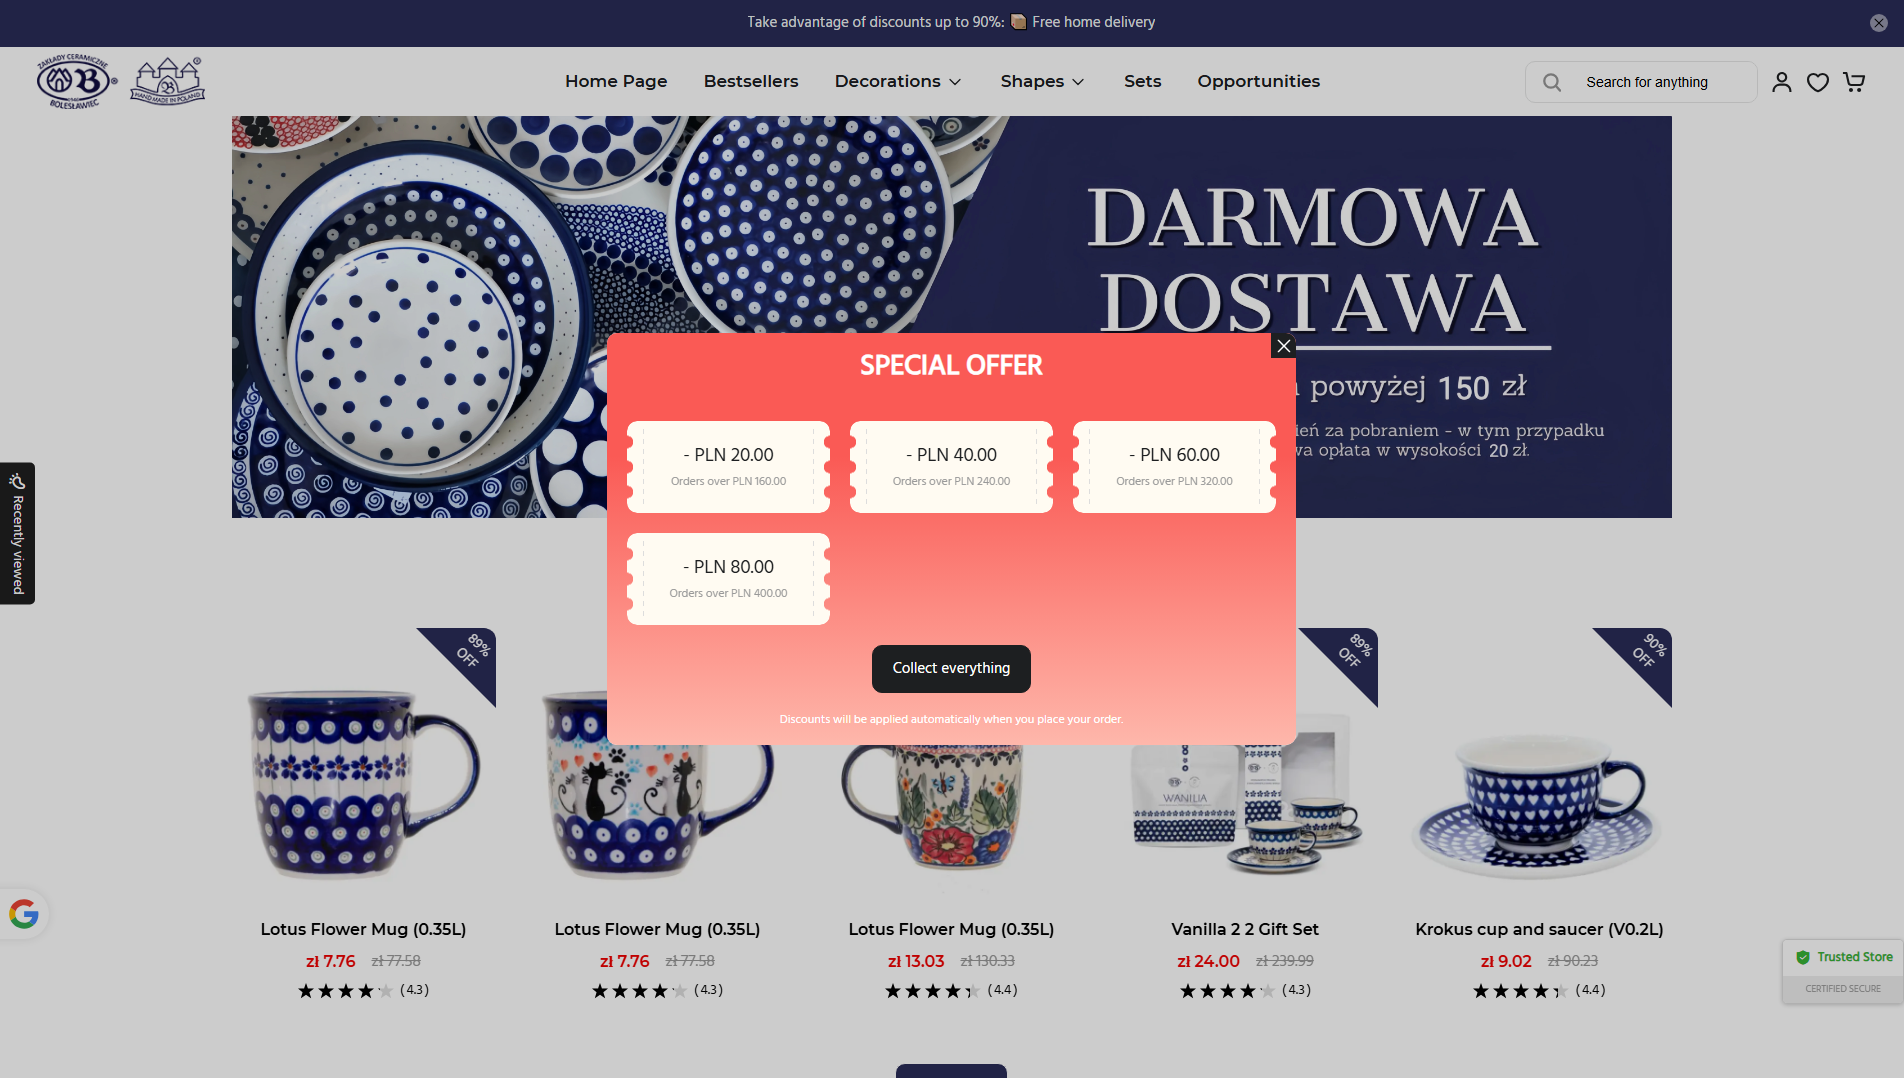
PhishDestroy first observed zakladyboleslawiechome-pl.shop on Nov 18, 2026. Stored content metadata identifies TikTok as the apparent target. The captured page title is “500 Internal Server Error”. Current evidence score: 100/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and Spamhaus DBL. VirusTotal recorded 18 detections among 92 engines: CRDF, DNS8, ESET, VIPRE, G-Data, Lionic, Sophos, CyRadar, Fortinet, Netcraft, SOCRadar, Kaspersky, LevelBlue, Seclookup, Gridinsoft, BitDefender, alphaMountain.ai, Forcepoint ThreatSeeker on Oct 31, 2026 at 00:35 UTC. Spamhaus DBL: DBL_SPAM on Nov 18, 2026 at 03:31 UTC. Additional recorded evidence: AlienVault OTX listed 1 community pulse reference (not vendor detections) on Nov 18, 2026 at 05:13 UTC.
HTTP 200 was recorded on Nov 22, 2026 at 11:13 UTC. Latest classified outcome: redirect observed; cause http redirect on Nov 21, 2026 at 10:15 UTC. Registration records for the domain list Dynadot Inc. as the registrar and Jul 9, 2026 as the creation date. At collection time, the hostname resolved to 43.172.114.23 on AS132203 (TENCENT-NET-AP-CN - Tencent Building, Kejizhongyi Avenue, CN). The recorded endpoint location is Santa Clara, US. The stored server header is nginx. DOM analysis on Nov 18, 2026 at 03:20 UTC returned 0/100; the source detections above were recorded separately. The evidence archive retains 6 visual captures from PhishDestroy and URLScan. TLS metadata lists YR1 as the certificate issuer with validity through Dec 29, 2026.
The content indicators and 2 positive source findings support the current TikTok impersonation and phishing classification. The target field identifies TikTok.


 Dynadot


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT