Cloudflare Radar

扫描报告
打开报告
PhishDestroy 保存了 ww19.ijntuit.com 的记录。各来源的观测有各自的日期;缺少检查并不代表安全。
选择实际发生的情况,并随着操作进程逐项勾选相应步骤。勾选记录仅保存在当前浏览器中。
专家视图包含所有部分:DNS、TLS、网络请求、哈希值以及原始 JSON 数据。
PhishDestroy 保存了 ww19.ijntuit.com 的记录。各来源的观测有各自的日期;缺少检查并不代表安全。
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
 208.91.196.145Confluence Networks Inc
PhishDestroy分析,早期未经审核的版本
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
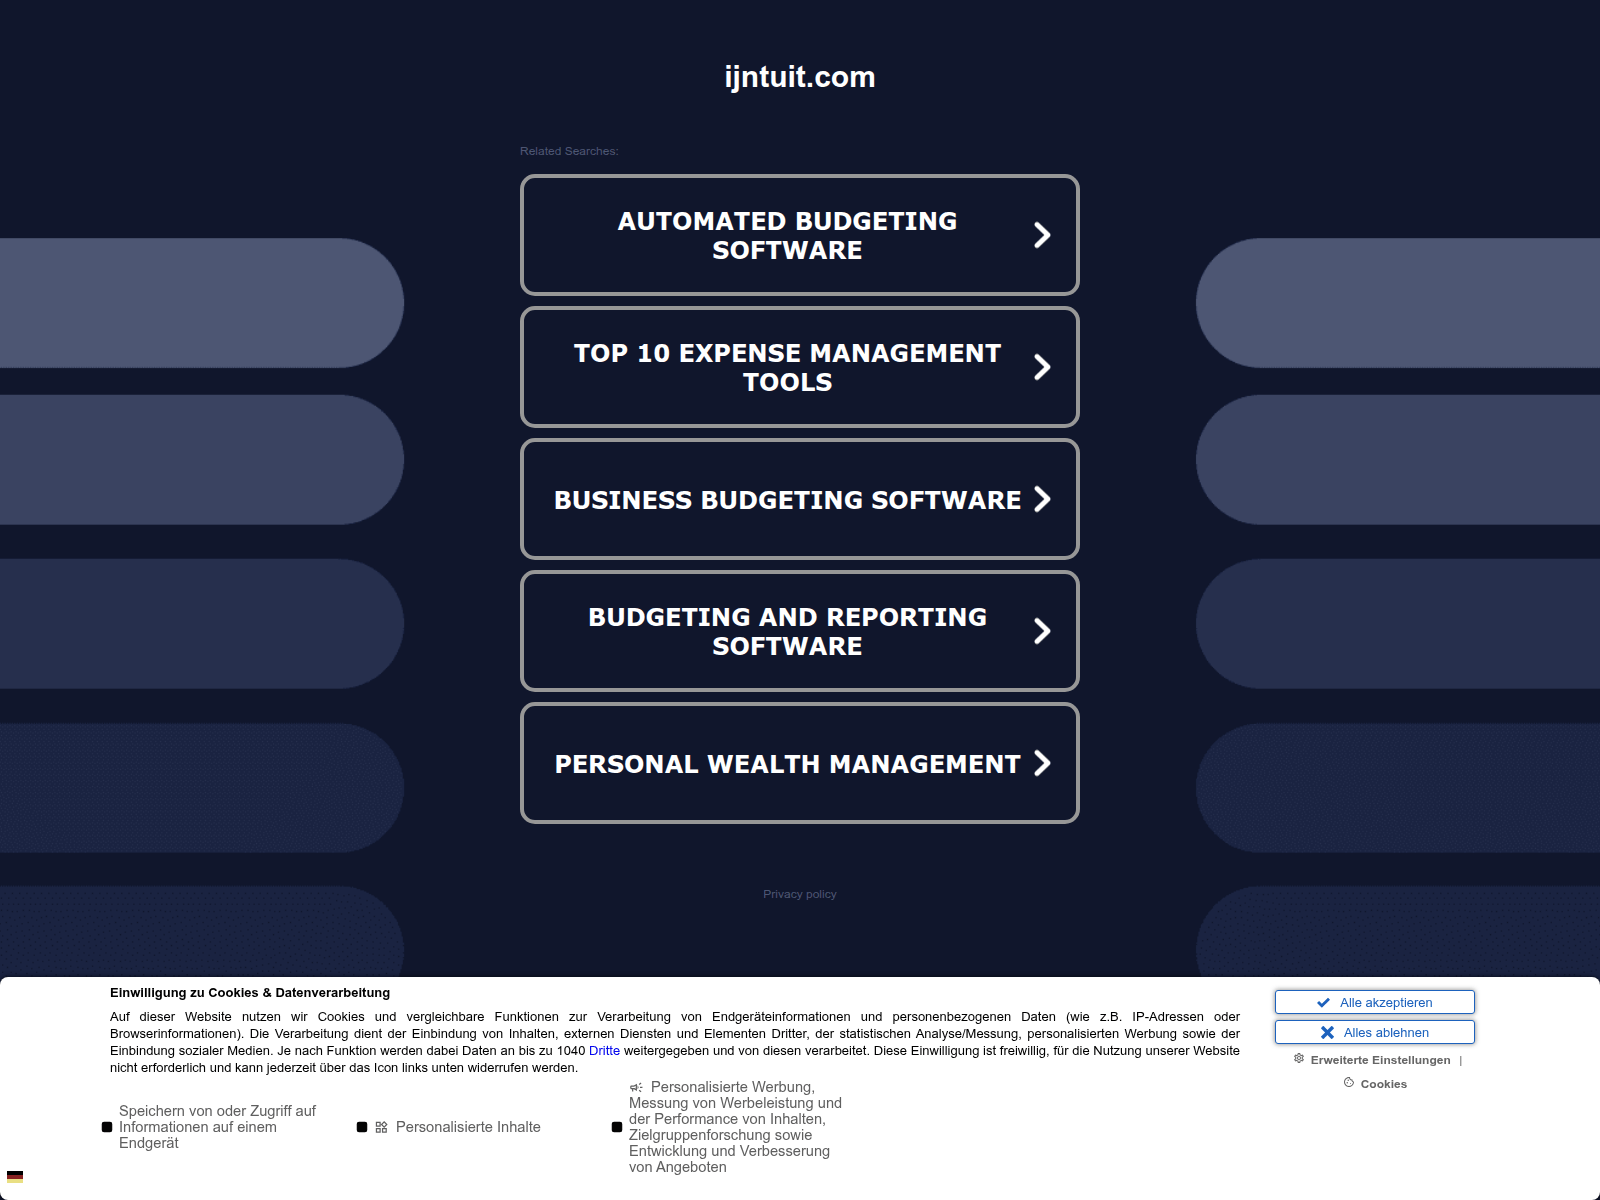
The captured screenshot shows a dark landing page headed by an apex-name wordmark, a Related Searches label, five large buttons offering travel and expense software, expense tracking, personal finance services, small business accounting software and top expense management tools, and a privacy policy link at the foot. PhishDestroy listed the domain after a trusted report received on 2026-10-25, with first sighting on 2026-10-25.
The page operates as a search-monetization redirect: each related-search button is a lure that hands the visitor onward to a third-party software offer funnel. In this category, such funnels commonly harvest credentials or push installs and paid subscriptions behind a trusted-looking offer. No credential form was visible in the capture, so the risk sits in the outbound click path rather than an on-page request.
The captured screenshot shows the five expense, finance and accounting offer buttons and the privacy link, with no credential form present. A URLScan capture from 2026-10-19 carried an engine verdict of malicious with an ML score of 2 while its overall verdict stayed non-malicious, and its recorded funnel showed a sibling host redirecting into this host before an HTTPS upgrade. VirusTotal did not flag the domain as malicious. Google Safe Browsing showed no flag on 2026-10-26, Spamhaus DBL was not listed on 2026-10-25, external blocklists counted 0 entries against an internal PhishDestroy listing on 2026-10-26, and OTX recorded 0 pulses on 2026-10-25; page inspection found a consent-management framework and Microsoft Clarity analytics with 1 tracker request, and one recorded document hash beginning ba7ad2b1be0f.
Notable weaknesses: Content-Security-Policy, HSTS and strict-transport, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP all absent; SPF set with a -all policy but no DKIM or DMARC; CAA records present; DNSSEC unsigned. TLS 1.3 with AES_128_GCM from a ZeroSSL certificate issued 2026-10-10. Hosting was recorded on the Confluence Networks Inc network, the server header was OpenResty, and the response code checked on 2026-10-26 was 200.
If you clicked an offer and entered credentials or payment details, change your password on the genuine service, enable two-factor authentication, and monitor financial statements for unexpected charges; do not reuse that password elsewhere. For defenders, block ww19.ijntuit.com at proxy, DNS and mail gateways and track sibling lookalike hosts.
扫描报告
打开报告页面快照
SHA-256 8a1890eb…7d81149
71 / 100 · 启发式得分 · 0 个品牌引用 · 0 个分类
仅为内容启发式评分;并非最终评分
打开报告叙事生成元数据
打开报告叙述生成日期与观测日期不同。这些是保留的出版字段,并非额外的独立检测结果。
结果反映各来源的采集时间。零检出不代表安全。OTX 引用为社区发布的内容。
已存档的页面、网络和扫描器观测结果,按来源和观测时间分组。
| 邮件配置 | MX: ~; Spf: v=spf1 a -all; Spf lookups: 1 |
|---|---|
| CAA 记录 | Domain: ww19.ijntuit.com |
| DNS防护结果 | Resolvers: 12; Blocked count: 0 |
| 网络档案观察 | Last: 2026-10-25T15:04:42Z; First: 2026-10-25T15:04:42Z; Changes: 0; Days archived: 1; Avg page bytes: 8318 |
| 爬行器规则 | Agents: *, Googlebot, Slurp, MSNBot, Ia archiver; Present: ✓ |
| Security contact file | Present: ✓; Found in: /.well-known/security.txt |
| 追踪器 | Requests: 1 |
| 表单与混合内容 | Third party scripts: 0 |
| 状态 | Up: ✓; Code: 200; Timings: DNS: 126; TLS: 2456; Wait: 275; Connect: 140; Download: 1; Response ms: 2998 |
| 端口 | Open: 80, 443 |
| Carbon | Bytes: 122; Co2 grams: 0; Cleaner than: 95 |
| DNS server | NS: (IP: 85.17.21.143; Host: ns2.hastydns.com), (IP: 69.162.80.50; Host: ns1.hastydns.com); Zone: ijntuit.com |
| 位置 | IP: 208.91.196.145; ASN: 40034; Org: Confluence Networks Inc; City: Road Town; Country: VG |
| DNS 记录 | A: 208.91.196.145; MX: Exchange: ~; Priority: 300; NS: ns1.cnomy.com, ns2.cnomy.com; Ptr: ns1.cnomy.com; Soa: Nsname: ns1.cnomy.com; Hostmaster: abuse.confluence-networks.com; Serial: 2011062801; Refresh: 3600; Retry: 900; Expire: 604800; Minttl: 86400; Txt: v=spf1 a -all; Cname: 9145.searchmagnified.com |
| DNSsec | Ds: ✗; Rrsig: ✗; Dnskey: ✓ |
| Hsts | Message: Site does not serve any HSTS headers. |
| HTTP 安全策略 | Xframeoptions: ✗; Referrerpolicy: ✗; Xxssprotection: ✗; Permissionspolicy: ✗; Xcontenttypeoptions: ✗; Contentsecuritypolicy: ✗; Stricttransportpolicy: ✗; Crossoriginopenerpolicy: ✗; Crossoriginembedderpolicy: ✗; Crossoriginresourcepolicy: ✗ |
| Get IP | IP: 208.91.196.145; Family: 4 |
| 重定向 | Chain: https://ww19.ijntuit.com |
| 子域名 | Count: 1; Subdomains: ww1.ijntuit.com |
| 注册记录 | Registrar: Media Elite Holdings Limited, S.A.; Created: 2019-06-03T07:39:38Z; Updated: 2023-09-02T02:19:31Z; Expires: 2027-06-03T07:39:38Z; Status: clientTransferProhibited https://icann.org/epp; Nameservers: ns1.hastydns.com, ns2.hastydns.com |
| HTTP 头 | Headers: Server: openresty; Content type: text/html; Via: 1.1 google |
e959fd54a51eca6d4635548106029a9d52ddb837ac0f755e97b5674f1fb71cd2 · 62050 bytes e92a1503d5c88cc2ddf4e4d9539c2f9a470d5704f20898416421761445073cd5 · 58363 bytes 35c5a6c523fa8121fbad7c68b1e22cb1b0f3d4d670303b1879f76b2dff487f2f · 70797 bytes 9731e82a1b71c9ac4f7e9f9b1038bcc2fa193a3c4f2fa9149f4ed2d4577d5c13 · 202443 bytes  208.91.196.145 0/100滥用评分 · 针对该服务器IP地址的滥用报告,而非针对该域名的报告;分数越高,情况越严重 该IP地址的滥用评分较低,但该域名本身已被认定为钓鱼网站。 0 条举报 已检查 2026-10-25 最近一次举报 · 不在统计期间内 208.91.196.145Road Town, VG
ns1.hastydns.comns2.hastydns.comnsname: ns1.cnomy.comhostmaster: abuse.confluence-networks.comserial: 2011062801refresh: 3600retry: 900expire: 604800minttl: 86400~priority 300位置信息描述的是 IP 网络。
dc089b581029503d5044eb08857ea68acff24a40f06c92020f00f486fe3d1478ww19.ijntuit.com已保存的证书元数据。未带时区的证书日期按存档原样显示。传输加密并不能证明该网站值得信任。
Google PageSpeed Insights — 移动端性能审核: ww19.ijntuit.com ·
由本地采集流程保留的带时间戳的响应元数据。以下各项数值均对应所显示的存档时间。
http://ww19.ijntuit.com/服务器: nginx/1.28.0Content-Type: text/htmlContent-Encoding: gzip4236a047946cb67d6a7e839ec4fee7092e36705e2ebb69f80a5614aa3adf8eeekeep-alivegziptext/htmlSun, 25 Oct 2026 15:05:19 GMTnginx/1.28.0chunked1.1 google21-qw8z由采集器保留的数值;较长的值可能在采集时被截短。
估算时间描述的是一个观测时间窗口。它并不能证明注册商采取了措施,也不代表网站变为不可访问的确切时刻。
网络请求: 22 SHA-256 哈希值: 22 URLScan扫描:
URLScan在加载页面时记录的网络请求。URLScan并非为每个请求都提供哈希值。 PhishDestroy 于 2026-10-29 01:57 UTC 检索到了此列表。
在 URLScan 上打开此扫描 01a151c4-0cbe-774c-be44-819d8b20aa74 ↗
加载已保存的数据;不会打开该可疑网站。
| # | 网络请求 | HTTP方法 · 状态码 | 类型 | 未压缩大小 | 响应正文的SHA-256哈希值 |
|---|
已记录事件:8。这些记录描述了收集到的证据、外发通知及黑名单发布情况;它们并不意味着调查已完全结束或该网站已被下线。
生命周期
我们扫描可疑网址,审查公开检测结果,并通过相应的滥用举报渠道提交证据。上方的带日期事件记录了该域名的相关记录。下方的目录说明了更全面的工作流程。
捕获渲染后的页面、请求以及可见的基础设施。
比较各引擎的检测结果,并保留分析时间戳。
检查Google当前是否将该URL列为不安全。
查看公开扫描结果及其记录的网络和分类数据。
查找相关指标参考及相关社区情报。
对比存档的截图并保留历史背景信息。
查找匹配的指标及相关威胁记录。
检查证书记录及相关主机名。
比较安全解析器的响应,并记录观察到的拦截情况。
检查公共DNS、TLS、HTTP及技术暴露面。
用于扫描、信誉检查和报告的安全服务列于下方。某项服务被列出并不意味着该服务已收到、接受或针对该特定域名采取了行动。已记录的提交内容显示在上方通知历史记录中。
 GoogleSafe Browsing↗ GoogleWeb Risk↗
 MicrosoftSmartScreen↗
 VirusTotalURL分析↗
 Cloudflare雷达 / 滥用行为举报↗
 YandexSafe Browsing↗
 URLScan.io公开扫描↗
 ESET示例 / URL 提交↗
 BitdefenderURL提交↗
 NortonSafe Web↗
 Symantec网站评审↗
 AviraURL 报告↗
 Avast / AVGURL 报告↗
 卡巴斯基OpenTIP↗
 Dr.Web在线扫描器↗
 Netcraft滥用行为报告↗
 PhishTank社区举报↗
 APWG eCX网络钓鱼情报↗
 PhishStats公开信息流↗
 Phish.Report主机滥用↗
 Spamhaus域名声誉↗
 PolySwarm多引擎分析↗
 CheckPhishURL 扫描↗
 Quttera恶意软件扫描↗
 URLquery浏览器分析↗
 Criminal IP资产情报↗
 CRDFThreat Center↗
 Scamadviser信誉检查↗
 MyWOT社区声誉↗
按来源浏览该域名的完整历史记录。下载内容包含所选来源的每条记录。日期将保留其原始字段标签。
将所有记录下载为 JSON 格式| ID | 存储的数据 |
|---|
相同 IP 208.91.196.145 辅助信号 6
注册商:Media Elite Holdings 仅限探索 6
每条辐条代表该域名与本报告相关联的一个原因。节点大小表示VirusTotal的检测结果,虚线节点表示已下线,完整列表如下。 相关报告完整列表
该源 IP 托管多个网络钓鱼域 - 基础设施可以在各个活动之间共享。
该 IP 地址的其他 PhishDestroy 报告:47 下方列出 VirusTotal 检测数最多的 6 条报告。
通过同一家注册商注册。一家注册商通常为数百万互不相关的客户提供服务,因此这仅表明数据归属同一群体,而非证明存在关联。
最近添加了来自 PhishDestroy 数据库的报告。这些发现链接并不意味着共享基础设施或所有权。
比较浏览器与爬虫各自收到的内容,并检查是否存在 Keitaro 流量分发。
ww19.ijntuit.com 根据您实际采取的行动采取相应措施。如果输入了密码:请立即更改密码,并检查是否在其他地方重复使用过该密码。如果支付过款项或提供过银行卡信息:请联系您的银行或支付服务商。如果下载了文件:请对设备进行病毒扫描。然后报告该事件。
该草稿仅供您个人保留。
首先确保资金安全:致电您的银行或撤销钱包授权。 当务之急 →
请根据您提供过的信息选择相应的步骤。请将本报告的副本与您自己的记录一并保存。
停止使用可疑网站。请通过官方应用或您已信任的网址访问真正的服务。
请将原始邮件、收据、消息和截图保存在安全的地方。基于事实的时间线有助于受理机构了解事件经过。 IC3 证据指南 ↗
ww19.ijntuit.com)即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。
举报并不能保证追回损失或启动调查,但及时、准确的交易数据可以帮助执法机构和服务提供商追踪事件。
使用存储的阻止列表、WHOIS、DNS 和公共扫描证据进行威胁分析
立即扫描将可疑域名提交至我们的威胁数据库——保护社区
报告最近的网络钓鱼报告和观察到的可用性变化
监控本报告汇总了已保存的页面快照、注册与网络记录、扫描器结果以及 PhishDestroy 举报历史。每个来源均保留各自的观测日期。打开来源报告即可查看原始结果。
AI 辅助分析的撰写时间: . 该内容描述了当时可获得的证据;后续的来源核查可能会导致情况发生变化。
快照记录的是当时显示的内容。扫描器结果记录的是该服务商在检查时的评估。有效证书或零检出结果都不能保证安全。