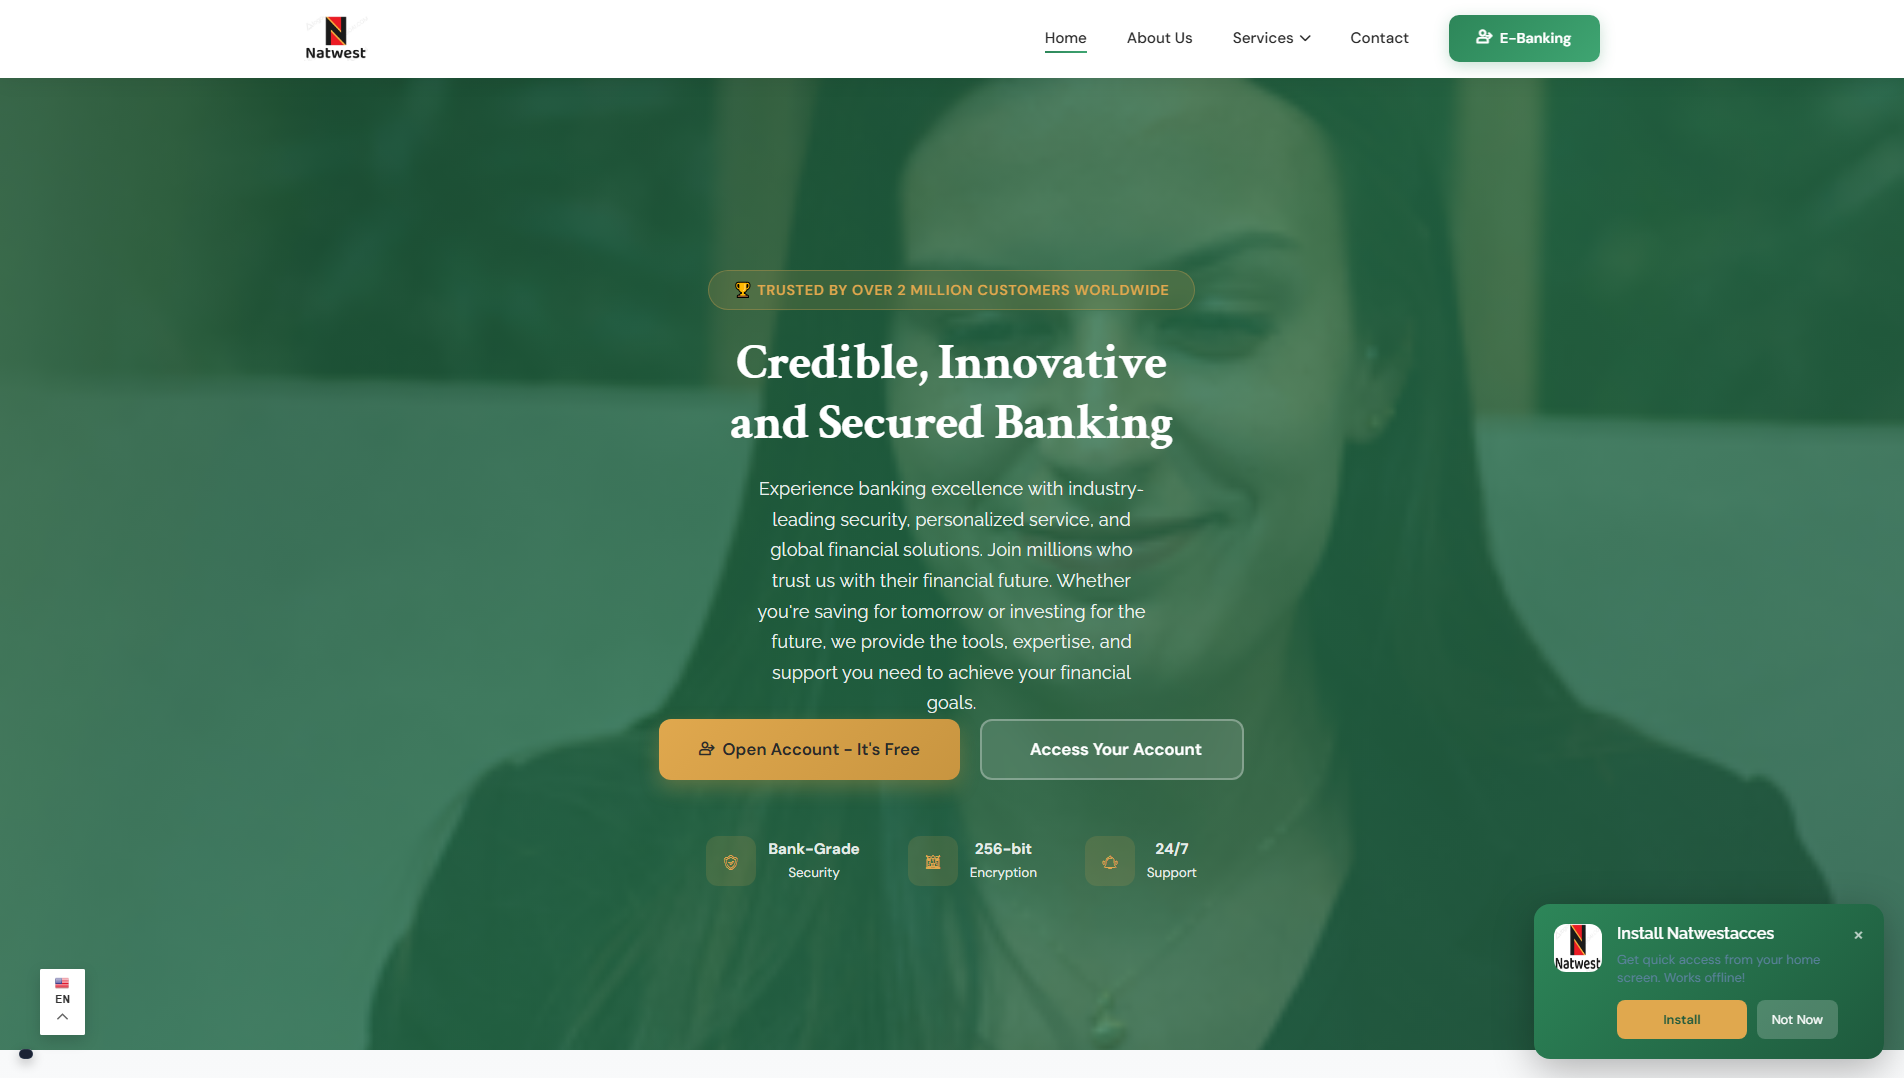
web.natwestaccessfinance.com is an impersonation phishing page posing as NatWest under the title "Natwestaccessfinance." It targets NatWest customers and anyone looking for finance from the bank. PhishDestroy first flagged it on 2026-08-30. The site has been offline since 2026-09-11, and on 2026-10-19 its DNS was still inactive.
诈骗手法解析
The page title and the domain both combine the NatWest name with "access finance" to look like an official bank or lending portal. Victims typically arrive through a text, email or ad and see a login or application screen. That screen captures customer numbers, passwords, PINs, one-time codes and personal details. The attackers use them to sign in to the real account, move money or approve payments before the victim notices.
证据
Ten of 91 VirusTotal engines flagged the domain when it was checked on 2026-08-31. The engines that flagged it include alphaMountain.ai, BitDefender, CRDF, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft and Kaspersky. These are separate vendors, so their agreement supports the phishing verdict independently of our own classification. Spamhaus lists the domain on its DBL as a phishing domain, and it is on the PhishDestroy blocklist.
基础设施
The domain was registered on 2026-05-20 through Realtime Register B.V., about three months before we detected it. That gap suggests the name was held in reserve before the campaign went live. The site was hosted on Ultahost, Inc. in the Netherlands, which has no connection to a UK bank. Its free Let's Encrypt certificate gave it a padlock icon, which proves nothing about who runs a site.
What to do
If you entered NatWest login details here, contact NatWest right away using the number on your card or the official app. Change your password and PIN, and ask the bank to review recent payments and payees. If you shared one-time codes or card details, tell the bank so it can block the card and watch for fraudulent transfers. Report the message that sent you to the page to your provider and the bank. Defenders should block the domain and look for similar "natwest" lookalike names registered around the same time.
web.natwestaccessfinance.com was a phishing page impersonating NatWest, built to steal online banking logins and personal data from UK bank customers.
AI摘要
Overview web.natwestaccessfinance.com is an impersonation phishing page posing as NatWest under the title "Natwestaccessfinance." It targets NatWest customers and anyone looking for finance from the bank. PhishDestroy first flagged it on 2026-08-30. The site has been offline since 2026-09-11, and on 2026-10-19 its DNS was still inactive. How the scam works The page title and the domain both combine the NatWest name with "access finance" to look like an official bank or lending portal. Victims typically arrive through a text, email or ad and see a login or application screen. That screen captures customer numbers, passwords, PINs, one-time codes and personal details. The attackers use them to sign in to the real account, move money or approve payments before the victim notices. Evidence Ten of 91 VirusTotal engines flagged the domain when it was checked on 2026-08-31. The engines that flagged it include alphaMountain.ai, BitDefender, CRDF, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft and Kaspersky. These are separate vendors, so their agreement supports the phishing verdict independently of our own classification. Spamhaus lists the domain on its DBL as a phishing domain, and it is on the PhishDestroy blocklist. Infrastructure The domain was registered on 2026-05-20 through Realtime Register B.V., about three months before we detected it. That gap suggests the name was held in reserve before the campaign went live. The site was hosted on Ultahost, Inc. in the Netherlands, which has no connection to a UK bank. Its free Let's Encrypt certificate gave it a padlock icon, which proves nothing about who runs a site. What to do If you entered NatWest login details here, contact NatWest right away using the number on your card or the official app. Change your password and PIN, and ask the bank to review recent payments and payees. If you shared one-time codes or card details, tell the bank so it can block the card and watch for fraudulent transfers. Report the message that sent you to the page to your provider and the bank. Defenders should block the domain and look for similar "natwest" lookalike names registered around the same time. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a0506e-932d-77a2-b577-109ab23cce8e/ VirusTotal report: https://www.virustotal.com/gui/domain/web.natwestaccessfinance.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=web.natwestaccessfinance.com Archived copy: https://web.archive.org/web/20260830021415/https://web.natwestaccessfinance.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
证据层Availability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP注册
观测时间线last reachable: 2026-09-04 22:16 UTCcurrent episode first observed: 2026-09-30 16:14 UTCobserved RIP window: 2026-09-04 22:16 UTC → 2026-09-30 16:14 UTC · 617.98hmidpoint estimate ≈ 2026-09-17 19:15 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 109.176.207.222


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT