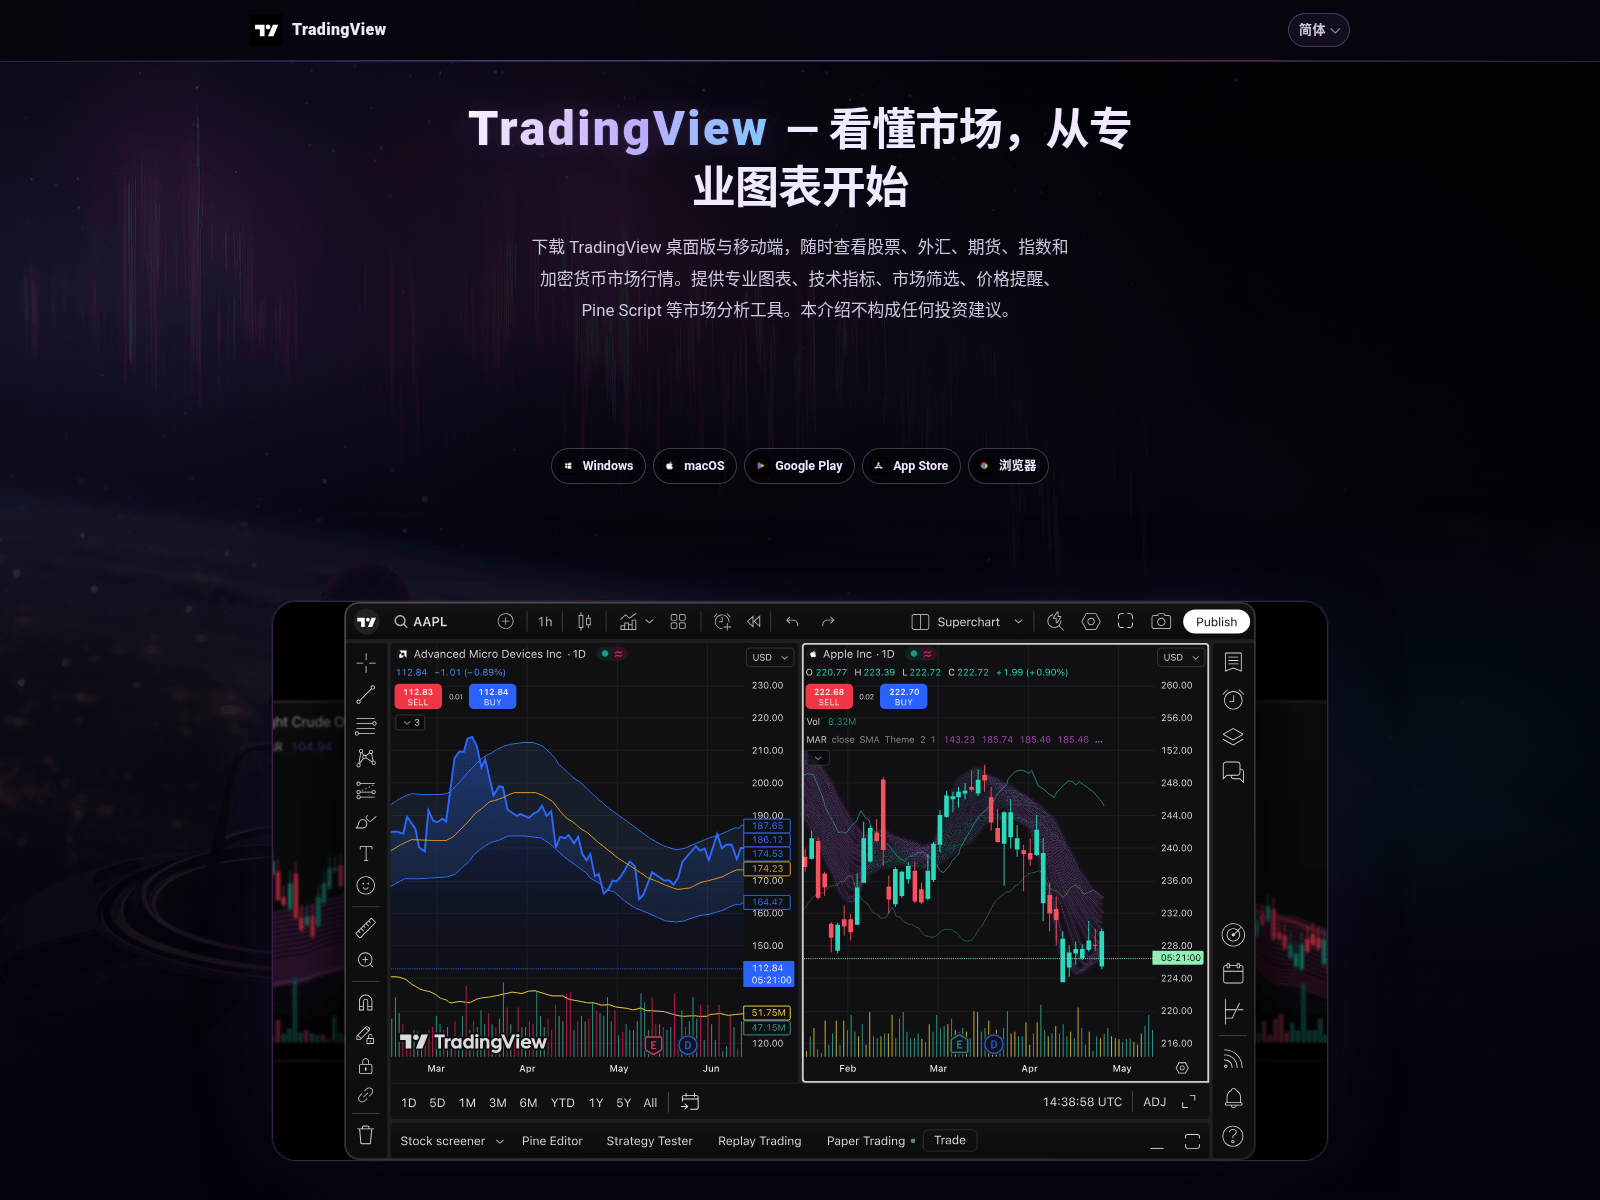
The domain tv-tradingview.net mimics the TradingView platform in Chinese, offering application downloads while operating independently of tradingview.com. Visitors should avoid downloading unverified software from this address and use tradingview.com instead.
URLScan截图 · 2026-11-21 00:13 UTC · SHA-256 1e40c0df…e3aee3d
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
TradingView interface copy and software downloads
The page opens with the TradingView logo and a bold Chinese headline reading "TradingView — 看懂市场,从专业图表开始". Below the header, descriptive text invites users to download desktop and mobile applications with phrases like "下载 TradingView 桌面版与移动端,随时查看股票、外汇、期货". The interface includes interactive buttons labeled "Windows", "macos", "Google Play", "App Store", and "浏览器". Below these buttons, an embedded preview displays financial charts with asset tickers like AAPL and technical indicator toolbars. The layout replicates the legitimate service to encourage users into downloading external binaries or accessing store links.
Independent security analysis and vendor telemetry
9 of 92 engines on VirusTotal flagged it on 19 Nov 2026, where Kaspersky, BitDefender and Fortinet are among the engines that flag the domain as malicious or phishing. PhishDestroy scores the evidence against it at 75/100 (critical), categorizing the threat level as critical due to its deceptive presentation. This confirms that the address is recognized by multiple independent filters as a risk.
Shared hosting and related look-alike infrastructure
2 other reported domains resolve to the same IP address and 178 use the same nameserver pair, connecting this domain to related pages such as brave-browser.co and tv-tradingview.app. These neighboring addresses host pages titled "Brave 浏览器|快速、安全、私密的网页浏览器" and "TradingView 金融行情图表与技柺分析平台 | 股票外汇加密货币行情", pointing to shared operational infrastructure.
tv-tradingview.net mimics the TradingView financial charts interface in Chinese for app downloads, flagged by 9 VirusTotal engines. Avoid it.
AI摘要
TradingView interface copy and software downloads The page opens with the TradingView logo and a bold Chinese headline reading "TradingView — 看懂市场,从专业图表开始". Below the header, descriptive text invites users to download desktop and mobile applications with phrases like "下载 TradingView 桌面版与移动端,随时查看股票、外汇、期货". The interface includes interactive buttons labeled "Windows", "macos", "Google Play", "App Store", and "浏览器". Below these buttons, an embedded preview displays financial charts with asset tickers like AAPL and technical indicator toolbars. The layout replicates the legitimate service to encourage users into downloading external binaries or accessing store links. Independent security analysis and vendor telemetry 9 of 92 engines on VirusTotal flagged it on 19 Nov 2026, where Kaspersky, BitDefender and Fortinet are among the engines that flag the domain as malicious or phishing. PhishDestroy scores the evidence against it at 75/100 (critical), categorizing the threat level as critical due to its deceptive presentation. This confirms that the address is recognized by multiple independent filters as a risk. Shared hosting and related look-alike infrastructure 2 other reported domains resolve to the same IP address and 178 use the same nameserver pair, connecting this domain to related pages such as brave-browser.co and tv-tradingview.app. These neighboring addresses host pages titled "Brave 浏览器|快速、安全、私密的网页浏览器" and "TradingView 金融行情图表与技柺分析平台 | 股票外汇加密货币行情", pointing to shared operational infrastructure.
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:12 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:12 UTClast content: 2026-11-22 11:12 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 Hosting Concepts
 112.121.183.106


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT