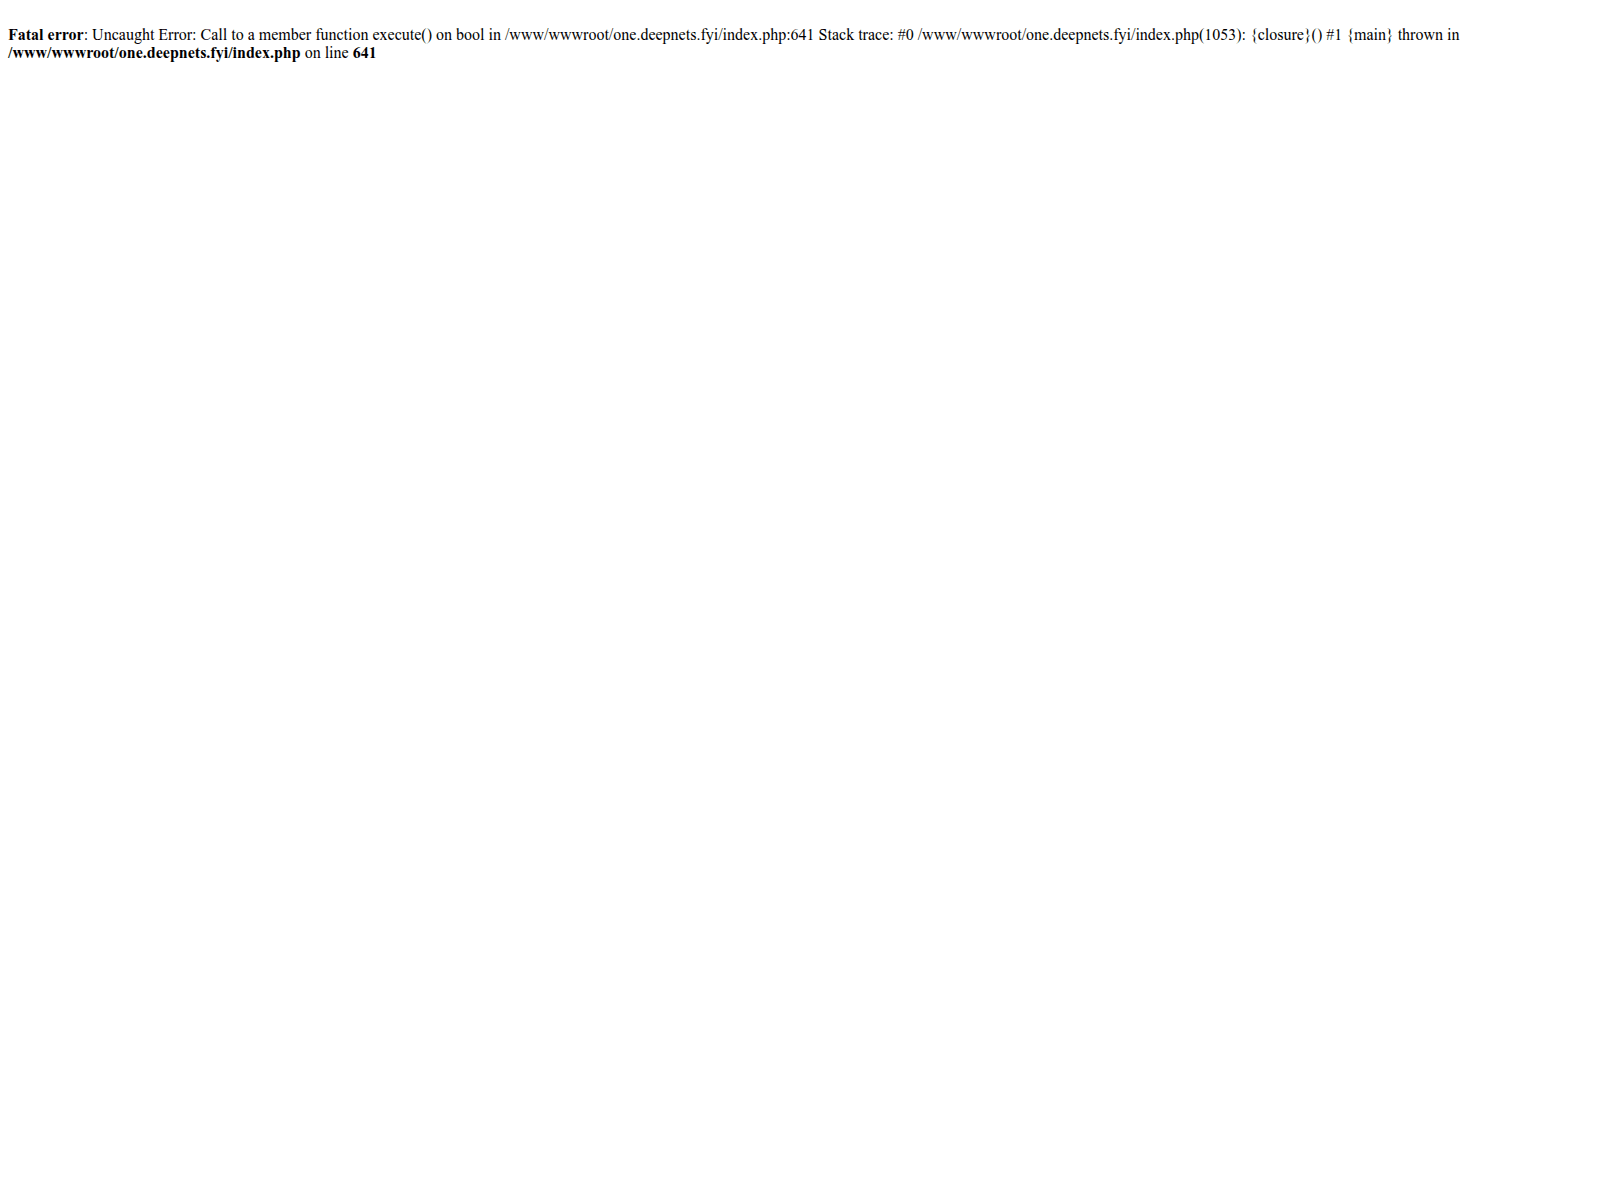
state-whatsapp.com presents a broken PHP error page that mimics the WhatsApp brand through its address while hiding its actual content. Visitors should avoid interacting with this domain and use the official whatsapp.com instead.
URLScan截图 · 2026-11-03 04:39 UTC · SHA-256 5071163f…3f70494
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Page layout and error output
The page at state-whatsapp.com displays a raw PHP error message rather than a functional web interface. At the top, the screen shows a bold "Fatal error: Uncaught Error: Call to member function execute() on bool in /www/wwwroot/one.deepnets.fyi/index.php:641" followed by a full stack trace detailing file paths and closure functions. No forms, buttons, or branding elements load successfully because the underlying script execution halts immediately. The address itself incorporates the WhatsApp brand name to appear connected to the messaging service, even though the true platform operates exclusively at whatsapp.com. Visitors encountering this server fault should close the tab immediately, as broken application states often precede malicious payload delivery or credential collection once fixed.
Security evaluations and independent detections
Security scanners including ESET, BitDefender and Fortinet classify the URL as a threat, PhishDestroy scores the evidence against it at 75/100 (critical). This confirms the address served malicious operations despite its broken appearance, matching a larger pattern where improperly deployed scripts expose server paths while phishing campaigns are being prepared.
Shared server infrastructure and campaign patterns
The underlying hosting setup connects this address to a wider network of suspicious properties. Specifically, 202 other reported domains resolve to the same IP address and 273 use the same nameserver pair, pointing to a heavily reused hosting environment. Neighbouring domains such as cors-whatsapp.com, column-whatsapp.com and style-whatsapp.com reside on the same infrastructure. Additionally, its IP address has 7 abuse reports on AbuseIPDB (port scanning, hacking and brute force), further establishing the risky nature of the underlying network resources.
state-whatsapp.com — PHP error page on WhatsApp domain
AI 描述
state-whatsapp.com displays a raw PHP error screen while flagged by Spamhaus DBL and 16 VirusTotal engines. Do not interact with the page and use whatsapp.com.
AI摘要
Page layout and error output The page at state-whatsapp.com displays a raw PHP error message rather than a functional web interface. At the top, the screen shows a bold "Fatal error: Uncaught Error: Call to member function execute() on bool in /www/wwwroot/one.deepnets.fyi/index.php:641" followed by a full stack trace detailing file paths and closure functions. No forms, buttons, or branding elements load successfully because the underlying script execution halts immediately. The address itself incorporates the WhatsApp brand name to appear connected to the messaging service, even though the true platform operates exclusively at whatsapp.com. Visitors encountering this server fault should close the tab immediately, as broken application states often precede malicious payload delivery or credential collection once fixed. Security evaluations and independent detections Security scanners including ESET, BitDefender and Fortinet classify the URL as a threat, PhishDestroy scores the evidence against it at 75/100 (critical). This confirms the address served malicious operations despite its broken appearance, matching a larger pattern where improperly deployed scripts expose server paths while phishing campaigns are being prepared. Shared server infrastructure and campaign patterns The underlying hosting setup connects this address to a wider network of suspicious properties. Specifically, 202 other reported domains resolve to the same IP address and 273 use the same nameserver pair, pointing to a heavily reused hosting environment. Neighbouring domains such as cors-whatsapp.com, column-whatsapp.com and style-whatsapp.com reside on the same infrastructure. Additionally, its IP address has 7 abuse reports on AbuseIPDB (port scanning, hacking and brute force), further establishing the risky nature of the underlying network resources.
最新的 HTTP 观察结果RedirectingHTTP redirect observed80%2026-11-22 11:14 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:14 UTClast content: 2026-11-21 11:15 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
技术 · 1 identified
HSTS
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.

 66.203.149.22


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT