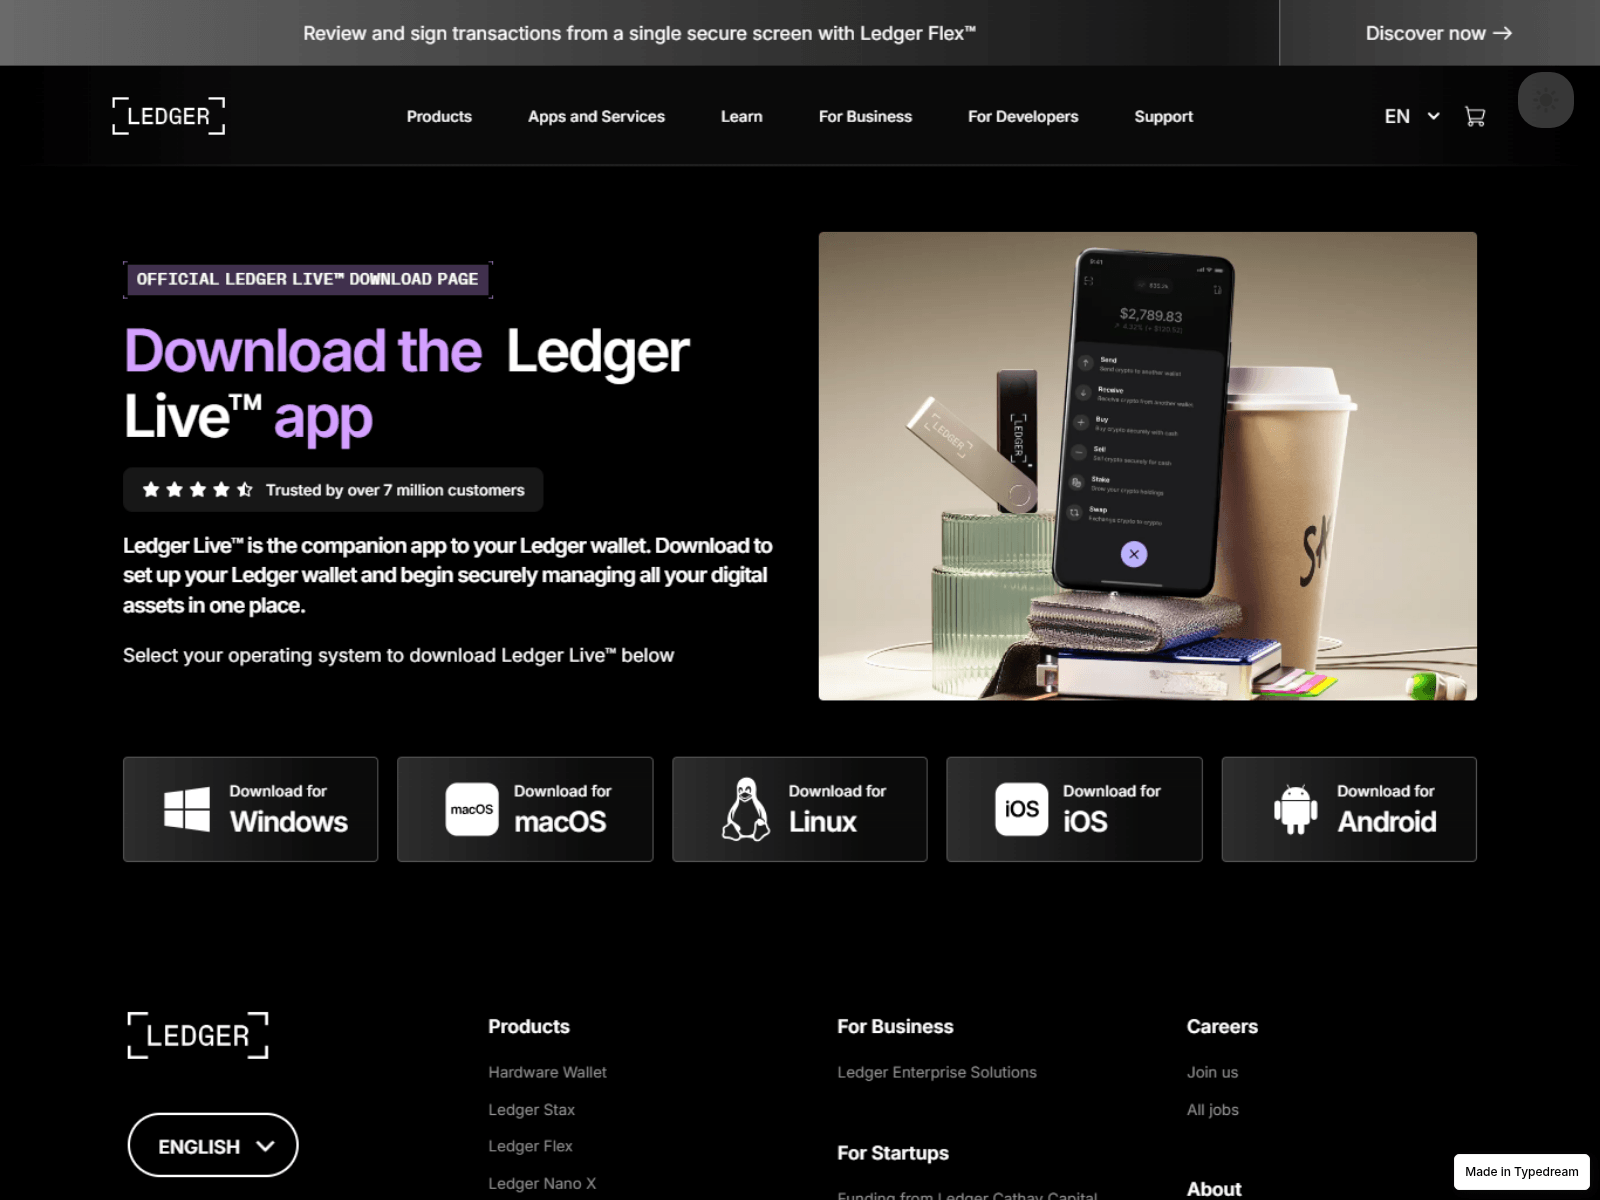
PhishDestroy listed start-ldgercom-faq.typedream.app as suspicious based on automated analysis and external vendor detections. The recorded page title reads "Ledger.com/Start® | Getting started — Ledger", which does not match the official Ledger domain. The domain was first observed by PhishDestroy on 2026-10-27 and returned an HTTP 200 response on that date.
诈骗手法解析
The detections point to a typical brand‑impersonation phishing approach, where attackers create pages that look like legitimate Ledger documentation to lure visitors into revealing credentials or downloading malicious content. No specific credential‑phishing form or wallet‑draining script was observed on the page, so the exact mechanism remains uncertain.
证据
VirusTotal reported seven malicious detections from ninety‑two engines on 2026-10-27, including ESET, Emsisoft, Fortinet, Kaspersky, LevelBlue, Netcraft and alphaMountain.ai. urlscan.io gave a malicious verdict with a 100 % phishing score and tagged the Ledger brand on 2026-10-27. The external OpenPhish blocklist flagged the domain, while Google Safe Browsing did not flag it on the same day. PhishDestroy recorded the domain in its internal blocklist on 2026-10-27. OTX showed zero pulses on 2026-10-27.
基础设施
The recorded IP address was 188.114.97.3 on 2026-10-27, with additional Cloudflare A records 104.21.37.85 and 172.67.206.36. TLS was provided by Google Trust Services (WE1) and was valid from 2026-09-23 to 2026-12-22. The domain age was zero days at first sighting, while the apex typedream.app is 2 081 days old. The site was served via Cloudflare using a Typedream platform built with Next.js and React.
What to do
If you visited the page, avoid entering any credentials or downloading files and verify Ledger documentation directly from ledger.com. If you submitted sensitive information, change any affected passwords and monitor related accounts for unusual activity. Organizations should block access to this exact domain and review network logs for connections to the recorded IP address.
PhishDestroy flags start-ldgercom-faq.typedream.app as a suspicious Ledger‑impersonating site after multiple vendor detections and a malicious urlscan verdict.
AI摘要
Overview PhishDestroy listed start-ldgercom-faq.typedream.app as suspicious based on automated analysis and external vendor detections. The recorded page title reads "Ledger.com/Start® | Getting started — Ledger", which does not match the official Ledger domain. The domain was first observed by PhishDestroy on 2026-10-27 and returned an HTTP 200 response on that date. How the scam works The detections point to a typical brand‑impersonation phishing approach, where attackers create pages that look like legitimate Ledger documentation to lure visitors into revealing credentials or downloading malicious content. No specific credential‑phishing form or wallet‑draining script was observed on the page, so the exact mechanism remains uncertain. Evidence VirusTotal reported seven malicious detections from ninety‑two engines on 2026-10-27, including ESET, Emsisoft, Fortinet, Kaspersky, LevelBlue, Netcraft and alphaMountain.ai. urlscan.io gave a malicious verdict with a 100 % phishing score and tagged the Ledger brand on 2026-10-27. The external OpenPhish blocklist flagged the domain, while Google Safe Browsing did not flag it on the same day. PhishDestroy recorded the domain in its internal blocklist on 2026-10-27. OTX showed zero pulses on 2026-10-27. Infrastructure The recorded IP address was 188.114.97.3 on 2026-10-27, with additional Cloudflare A records 104.21.37.85 and 172.67.206.36. TLS was provided by Google Trust Services (WE1) and was valid from 2026-09-23 to 2026-12-22. The domain age was zero days at first sighting, while the apex typedream.app is 2 081 days old. The site was served via Cloudflare using a Typedream platform built with Next.js and React. What to do If you visited the page, avoid entering any credentials or downloading files and verify Ledger documentation directly from ledger.com. If you submitted sensitive information, change any affected passwords and monitor related accounts for unusual activity. Organizations should block access to this exact domain and review network logs for connections to the recorded IP address. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17b7e-6a79-7110-9def-dd1fe309eaf3/ Cloudflare Radar report: https://radar.cloudflare.com/scan/9584a073-13af-4f59-818c-a8f42d98b3f4 Stored capture screenshot: https://urlscan.io/screenshots/01a17b7e-6a79-7110-9def-dd1fe309eaf3.png Cloudflare Radar screenshot (2026-10-27T03:50:56Z): https://screenshots.phishdestroy.io/cf/9584a073-13af-4f59-818c-a8f42d98b3f4.png URLScan screenshot (2026-10-27T03:49:03Z): https://screenshots.phishdestroy.io/us/01a17b79-b04b-7556-8042-cfcbce1e515d.png URLScan capture report: https://urlscan.io/result/01a17b79-b04b-7556-8042-cfcbce1e515d/ URLScan screenshot (2026-10-27T03:53:02Z): https://screenshots.phishdestroy.io/us/01a17b7d-5ce8-76ca-9b91-9c3aaa96ce54.png URLScan capture report: https://urlscan.io/result/01a17b7d-5ce8-76ca-9b91-9c3aaa96ce54/ VirusTotal report: https://www.virustotal.com/gui/domain/start-ldgercom-faq.typedream.app Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=start-ldgercom-faq.typedream.app Archived copy: https://web.archive.org/web/20261027034643/https://start-ldgercom-faq.typedream.app/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Ogurl: https://start-ldgercom-faq.typedream.page/; Title: Ledger.com/Start® | Getting started — Ledger; Ogtype: website; Ogtitle: Ledger.com/Start® | Getting started — Ledger; Ogsitename: start-ldgercom-faq; Description: A website made with Typedream.; Twittercard: summary; Twittersite: @typedreamHQ; Ogdescription: A website made with Typedream.
Technologies: Node.js, React, Google Cloud, Next.js, cdnjs, Quicklink, Google Font API, Google Cloud CDN, Cloudflare, Webpack, Open Graph, Module Federation, HTTP/3

 188.114.96.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT