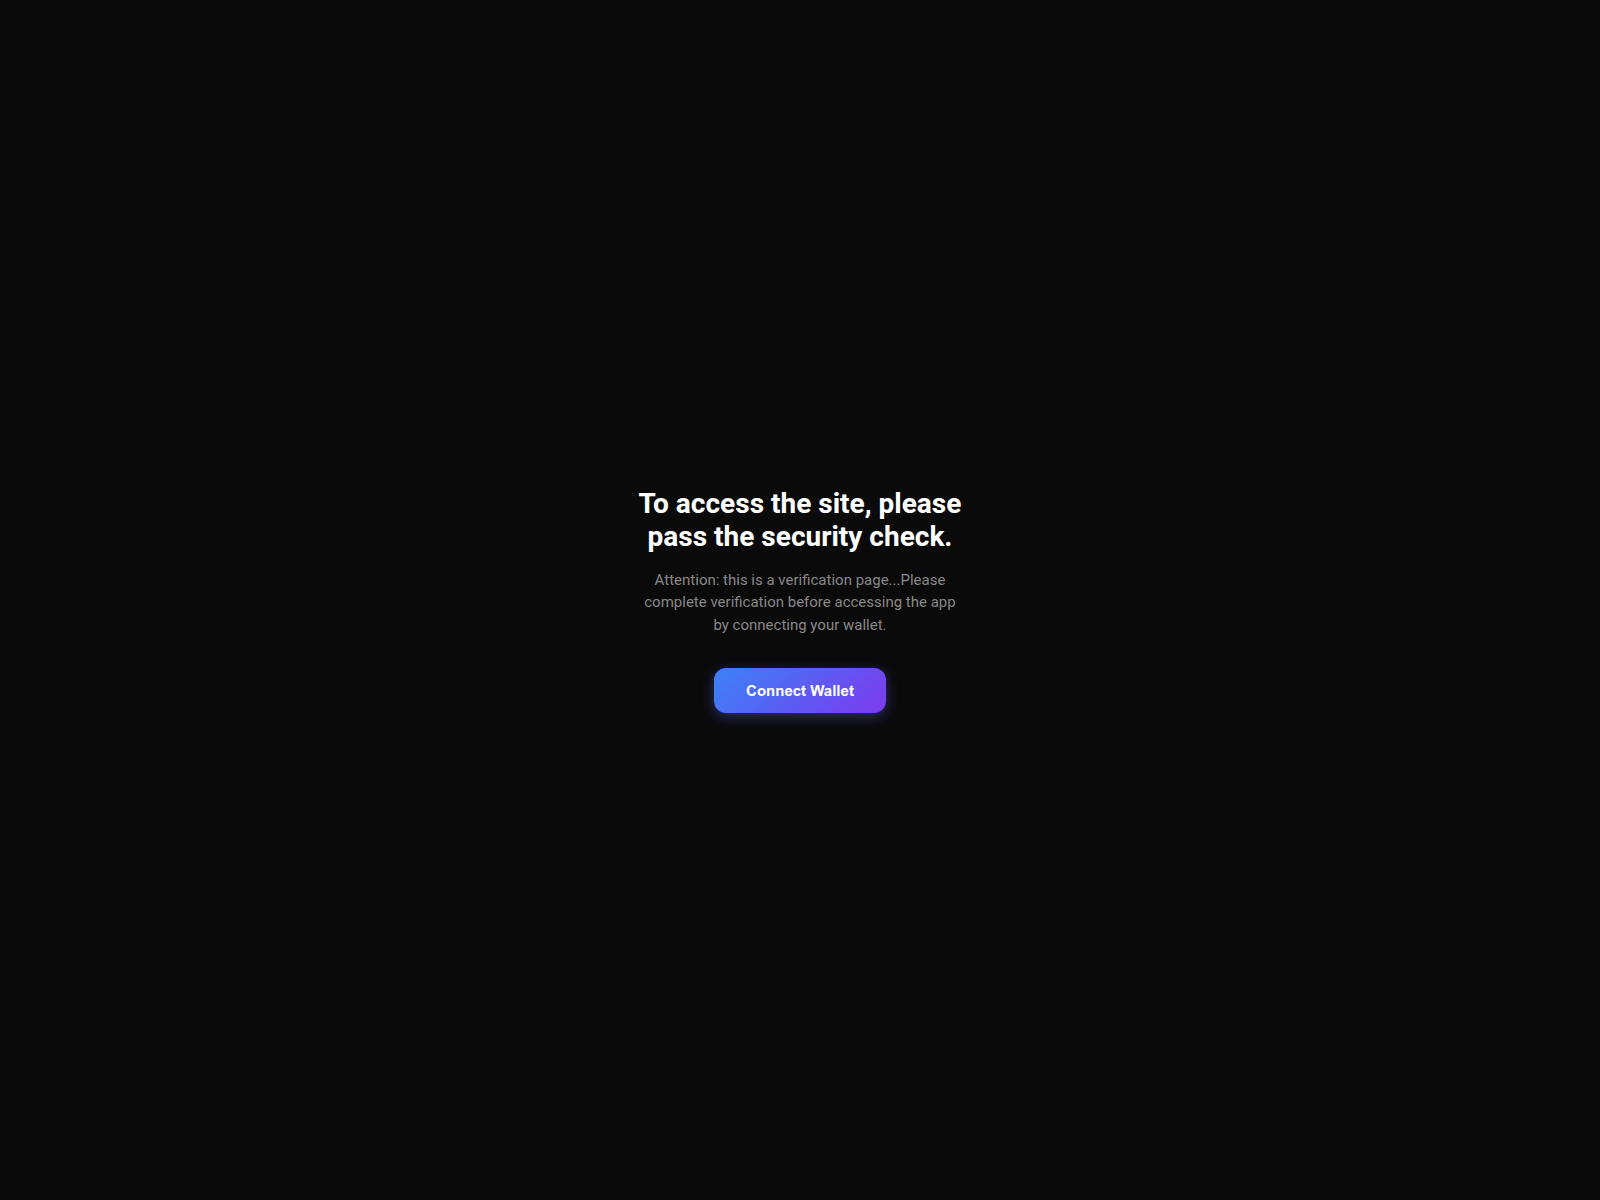
The domain ruji.network, now offline, is identified as a phishing threat by 5 out of 91 VirusTotal vendors. Hosted on Amazon's infrastructure, it employs a Let's Encrypt SSL certificate, a common tactic to lend legitimacy to phishing sites. PhishDestroy has flagged this domain on its public blocklist, highlighting its malicious nature.
Registered with Dynadot Inc, ruji.network was created on June 9, 2026, and detected by PhishDestroy on June 18, 2026. The domain's quick takedown indicates effective intervention, yet its initial operation period underscores the need for rapid detection systems. The platform risk score of 68 out of 100 suggests a significant threat level, while the abuse score of 21 out of 100 reflects moderate malicious activity.
Despite being offline, ruji.network's presence in the threat landscape emphasizes the importance of early detection. The domain's use of Let's Encrypt SSL and Amazon hosting showcases how legitimate services can be manipulated for phishing purposes. This incident serves as a reminder of the evolving tactics employed by cybercriminals to bypass traditional security measures.
ruji.network is a phishing domain flagged by 5/91 vendors, hosted on Amazon infrastructure. It uses Let's Encrypt SSL.
AI摘要
The domain ruji.network, now offline, is identified as a phishing threat by 5 out of 91 VirusTotal vendors. Hosted on Amazon's infrastructure, it employs a Let's Encrypt SSL certificate, a common tactic to lend legitimacy to phishing sites. PhishDestroy has flagged this domain on its public blocklist, highlighting its malicious nature. Registered with Dynadot Inc, ruji.network was created on June 9, 2026, and detected by PhishDestroy on June 18, 2026. The domain's quick takedown indicates effective intervention, yet its initial operation period underscores the need for rapid detection systems. The platform risk score of 68 out of 100 suggests a significant threat level, while the abuse score of 21 out of 100 reflects moderate malicious activity. Despite being offline, ruji.network's presence in the threat landscape emphasizes the importance of early detection. The domain's use of Let's Encrypt SSL and Amazon hosting showcases how legitimate services can be manipulated for phishing purposes. This incident serves as a reminder of the evolving tactics employed by cybercriminals to bypass traditional security measures.
最新的 HTTP 观察结果RedirectingHTTP redirect observed80%2026-11-22 11:18 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:18 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 Dynadot


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT