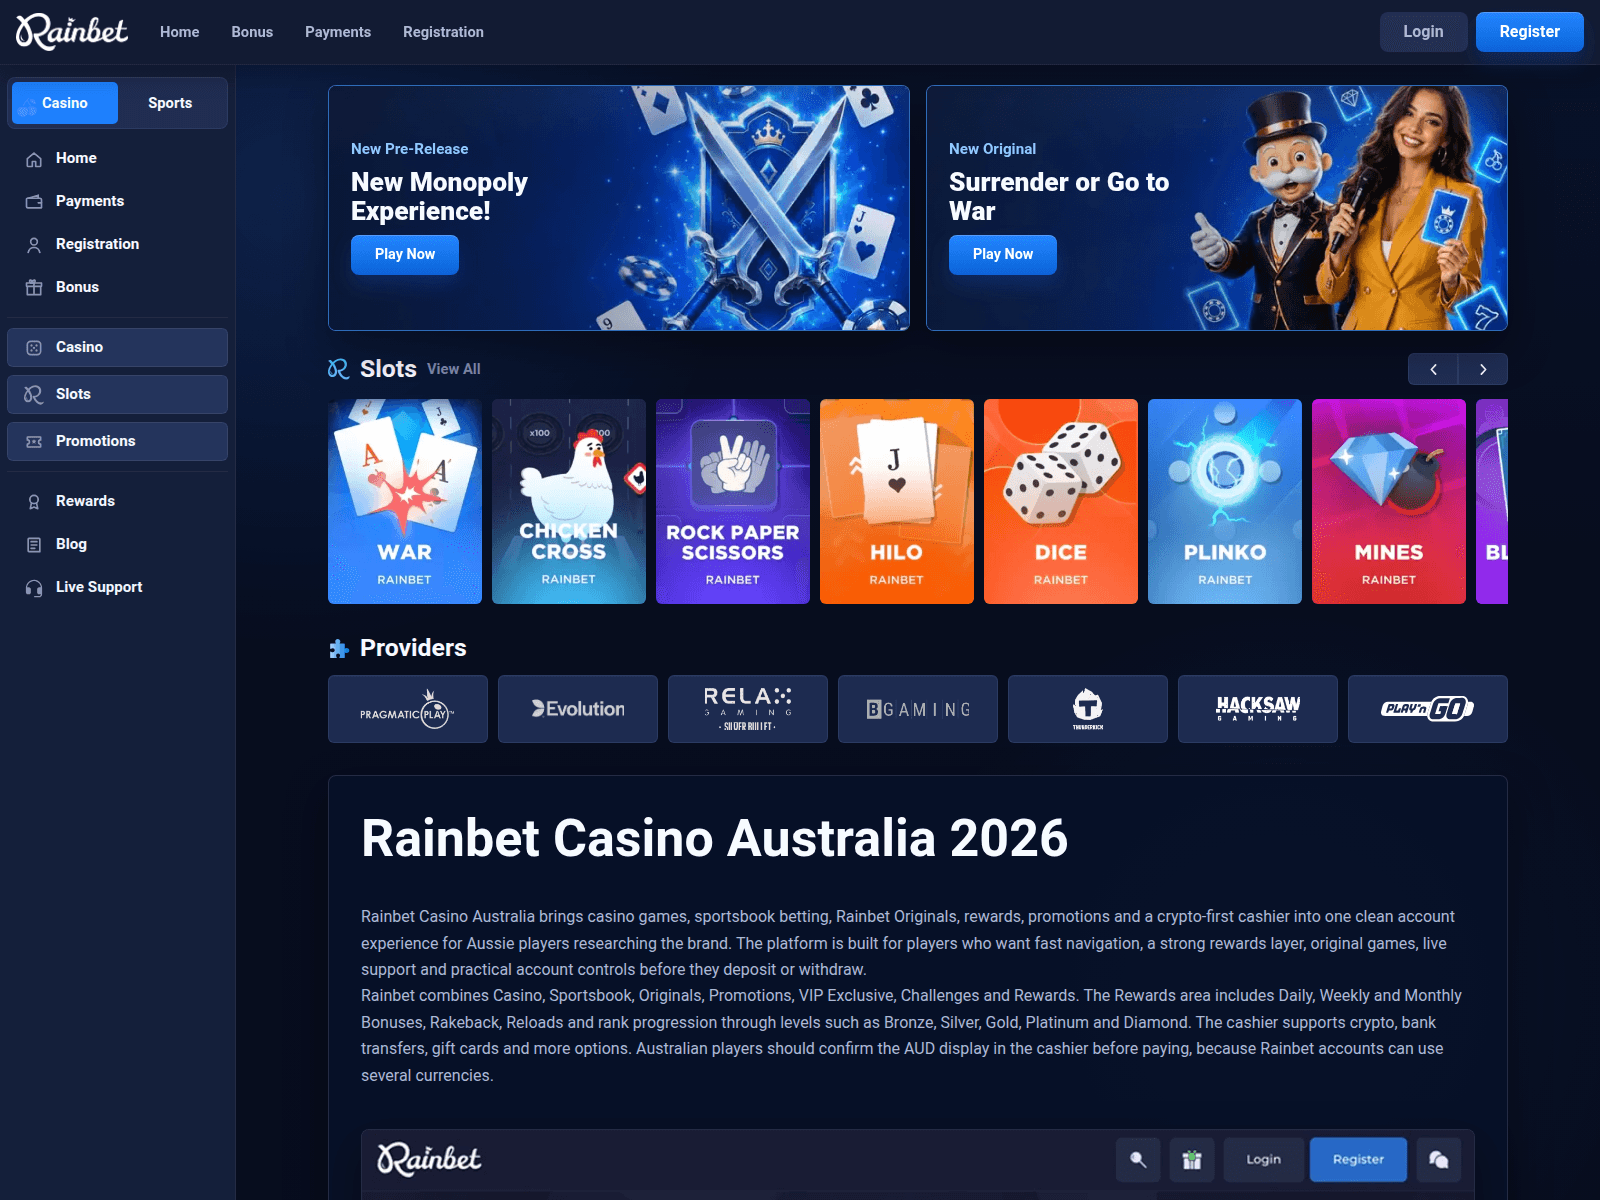
rainbet-australia-casino.com is a gambling site flagged as fraudulent. It trades on the Rainbet Casino name and targets Australian players with the page title "Rainbet Casino Australia 2026, bonus, payment and mobile." PhishDestroy first flagged it on 2026-07-31. On 2026-10-19 the site was still online and serving content, so it remains a live risk.
诈骗手法解析
The page title covers what a player wants to know before signing up: bonuses, payment options and mobile play. Fraudulent casino sites of this kind use a familiar brand and generous welcome offers to get visitors to register and deposit. The trouble usually starts when the player tries to cash out. Winnings get frozen, bonus terms suddenly block withdrawals, or the site demands an extra "verification" or "withdrawal" fee that never releases the balance. Victims can lose every deposit, plus any personal and payment details they handed over during sign-up.
证据
On 2026-09-15, 11 of 89 VirusTotal engines flagged the domain. They include ChainPatrol, alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF, Forcepoint ThreatSeeker, Fortinet and G-Data. That is a modest share, but the vendors are independent of each other and span crypto-focused feeds, browser-protection services and traditional security firms. MetaMask and SEAL list the domain alongside PhishDestroy, and Spamhaus carries it in its DBL as a phishing domain. It also appears in three AlienVault OTX threat pulses, so other researchers have tracked it separately.
基础设施
The domain was registered on 2026-05-08 through Realtime Register B.V., about twelve weeks before PhishDestroy flagged it. A brand-new domain with a well-known casino name built into it is typical of sites set up quickly to catch search traffic. It is hosted on G-Core Labs S.A. infrastructure in the Netherlands, far from the Australian audience it targets. Its free Let's Encrypt certificate means the padlock in the browser proves only that the connection is encrypted, not that the operator is legitimate.
What to do
Do not deposit any more money, and do not pay any fee promised to unlock a withdrawal, because more payments rarely return anything. If you paid by card or bank transfer, contact your bank right away to dispute the charges. Keep screenshots of your account, balance and messages from the site. If you reused your sign-up password anywhere else, change it on those accounts. Expect follow-up offers from "fund recovery" services and ignore them, as they are a common second scam. Defenders should block the domain at DNS and proxy level and take in Spamhaus DBL and community crypto blocklists so similar casino lookalikes are caught early.
rainbet-australia-casino.com — Fake Rainbet Casino Site
AI 描述
rainbet-australia-casino.com is a fraudulent gambling site using the Rainbet Casino name to lure Australian players into deposits and bonus offers.
AI摘要
Overview rainbet-australia-casino.com is a gambling site flagged as fraudulent. It trades on the Rainbet Casino name and targets Australian players with the page title "Rainbet Casino Australia 2026, bonus, payment and mobile." PhishDestroy first flagged it on 2026-07-31. On 2026-10-19 the site was still online and serving content, so it remains a live risk. How the scam works The page title covers what a player wants to know before signing up: bonuses, payment options and mobile play. Fraudulent casino sites of this kind use a familiar brand and generous welcome offers to get visitors to register and deposit. The trouble usually starts when the player tries to cash out. Winnings get frozen, bonus terms suddenly block withdrawals, or the site demands an extra "verification" or "withdrawal" fee that never releases the balance. Victims can lose every deposit, plus any personal and payment details they handed over during sign-up. Evidence On 2026-09-15, 11 of 89 VirusTotal engines flagged the domain. They include ChainPatrol, alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF, Forcepoint ThreatSeeker, Fortinet and G-Data. That is a modest share, but the vendors are independent of each other and span crypto-focused feeds, browser-protection services and traditional security firms. MetaMask and SEAL list the domain alongside PhishDestroy, and Spamhaus carries it in its DBL as a phishing domain. It also appears in three AlienVault OTX threat pulses, so other researchers have tracked it separately. Infrastructure The domain was registered on 2026-05-08 through Realtime Register B.V., about twelve weeks before PhishDestroy flagged it. A brand-new domain with a well-known casino name built into it is typical of sites set up quickly to catch search traffic. It is hosted on G-Core Labs S.A. infrastructure in the Netherlands, far from the Australian audience it targets. Its free Let's Encrypt certificate means the padlock in the browser proves only that the connection is encrypted, not that the operator is legitimate. What to do Do not deposit any more money, and do not pay any fee promised to unlock a withdrawal, because more payments rarely return anything. If you paid by card or bank transfer, contact your bank right away to dispute the charges. Keep screenshots of your account, balance and messages from the site. If you reused your sign-up password anywhere else, change it on those accounts. Expect follow-up offers from "fund recovery" services and ignore them, as they are a common second scam. Defenders should block the domain at DNS and proxy level and take in Spamhaus DBL and community crypto blocklists so similar casino lookalikes are caught early. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a06eca-f2ee-748d-8133-94f7d7690c7a/ VirusTotal report: https://www.virustotal.com/gui/domain/rainbet-australia-casino.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=rainbet-australia-casino.com Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:39 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:39 UTClast content: 2026-11-22 11:39 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
赌场/博彩牌照核验
未经核实的博彩牌照
This domain markets casino/gambling services. Scam casinos routinely display fake Curaçao, MGA, or Kahnawake license badges that don’t exist in the real registries. 存款前,请务必通过官方监管机构数据库核对许可证编号。 If the site shows a seal but no clickable registry link — or the linked registry page doesn’t exist — treat it as fraudulent.


 Realtime


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT