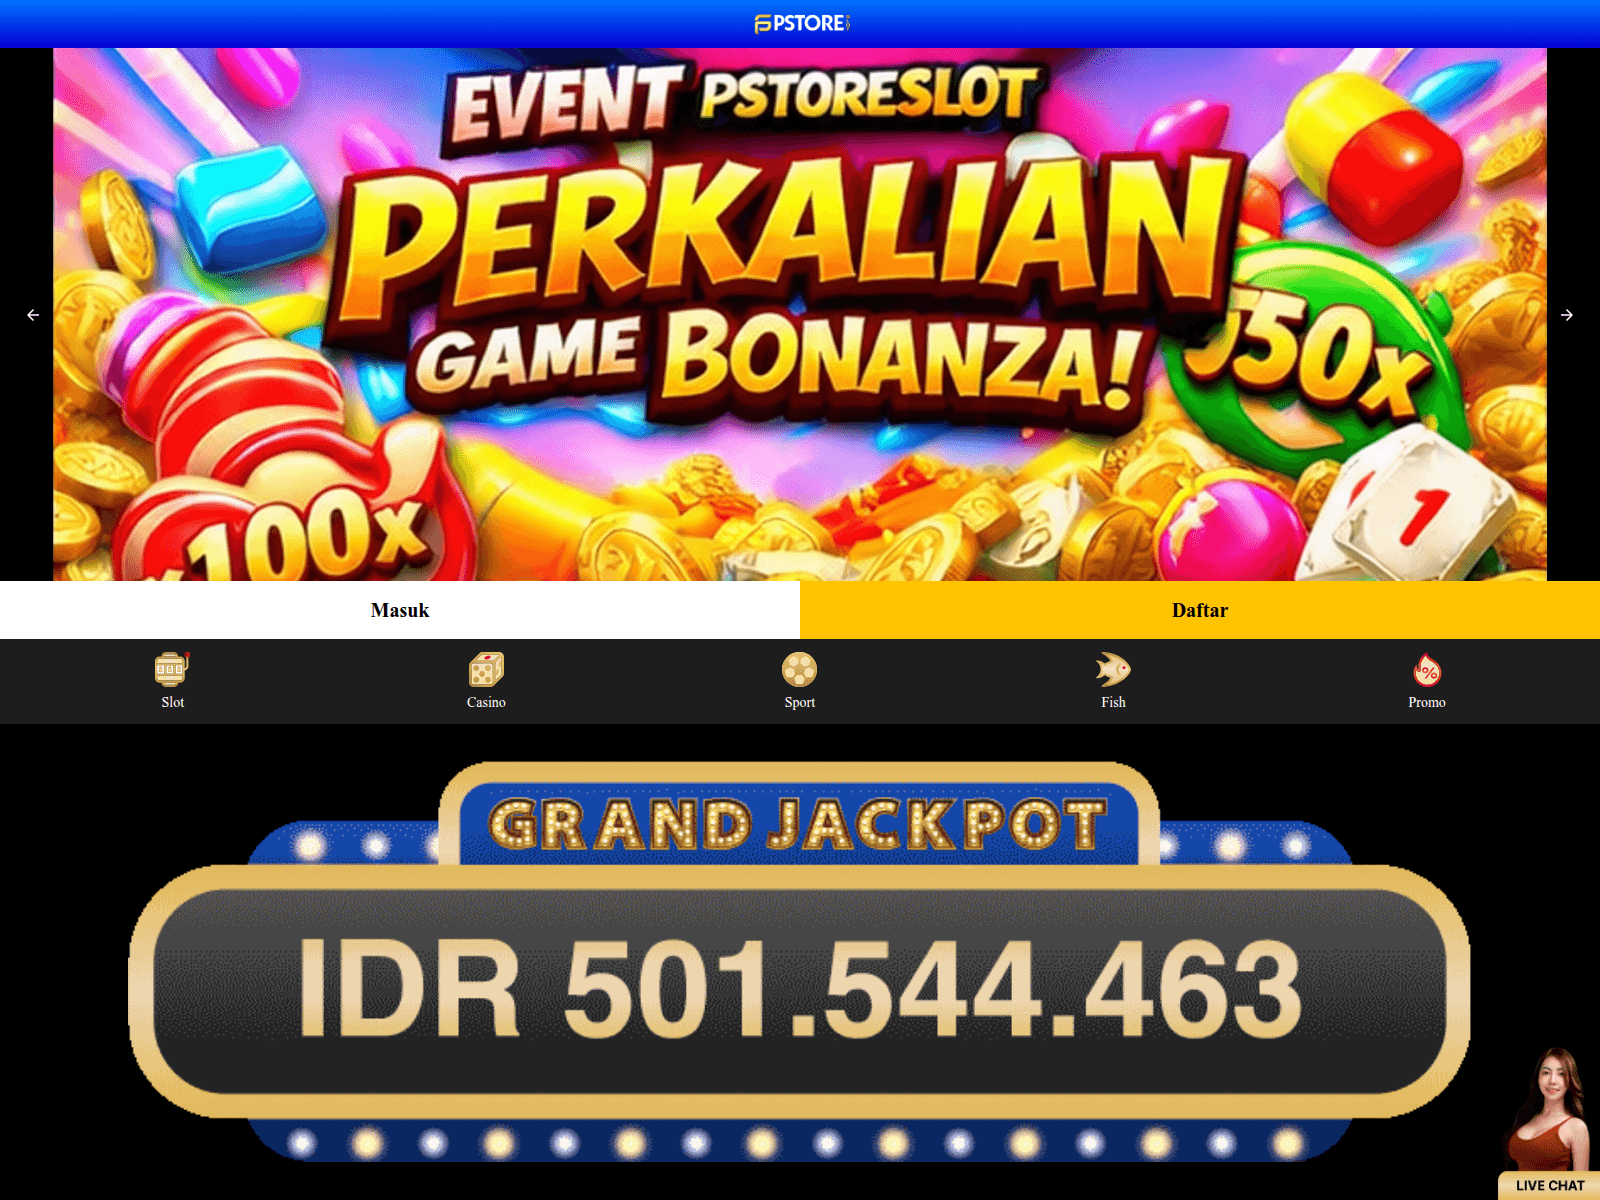
On 2026-11-17, pstoreslot-amp1.xyz redirected to www.pstoreslot-amp1.xyz. The destination page displays a bright promotional banner for an online gaming event featuring colorful candy and coin graphics alongside text about slot bonuses. Below the banner, navigation options for Masuk and Daftar are provided alongside category icons for slots, casino games, sports, and promos. A prominent grand jackpot counter displays a large IDR currency figure, while a live chat button remains anchored in the corner of the interface.
URLScan截图 · 2026-11-17 22:18 UTC · SHA-256 494e8370…d5cdea6
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-17, pstoreslot-amp1.xyz redirected to www.pstoreslot-amp1.xyz. The destination page displays a bright promotional banner for an online gaming event featuring colorful candy and coin graphics alongside text about slot bonuses. Below the banner, navigation options for Masuk and Daftar are provided alongside category icons for slots, casino games, sports, and promos. A prominent grand jackpot counter displays a large IDR currency figure, while a live chat button remains anchored in the corner of the interface.
The stored VirusTotal domain result reports 6 detections out of 92 engines. CRDF reported "malicious"; VIPRE reported "malware".
pstoreslot-amp1.xyz: Online Gaming and Promotional Slot Site
AI 描述
PhishDestroy examines pstoreslot-amp1.xyz, analyzing visible online gaming banners, grand jackpot displays, and promotional content.
AI摘要
On 2026-11-17, pstoreslot-amp1.xyz redirected to www.pstoreslot-amp1.xyz. The destination page displays a bright promotional banner for an online gaming event featuring colorful candy and coin graphics alongside text about slot bonuses. Below the banner, navigation options for Masuk and Daftar are provided alongside category icons for slots, casino games, sports, and promos. A prominent grand jackpot counter displays a large IDR currency figure, while a live chat button remains anchored in the corner of the interface. The stored VirusTotal domain result reports 6 detections out of 92 engines. CRDF reported "malicious"; VIPRE reported "malware".
No sri: https://cdn.ampproject.org/v0.mjs, https://cdn.ampproject.org/v0.js, https://cdn.ampproject.org/v0/amp-analytics-0.1.mjs, https://cdn.ampproject.org/v0/amp-analytics-0.1.js, https://cdn.ampproject.org/v0/amp-carousel-0.1.mjs, https://cdn.ampproject.org/v0/amp-carousel-0.1.js; Third party scripts: 6
最新的 HTTP 观察结果RedirectingHTTP redirect observed80%2026-11-22 11:13 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:13 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 NameCheap
 104.21.3.22


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT