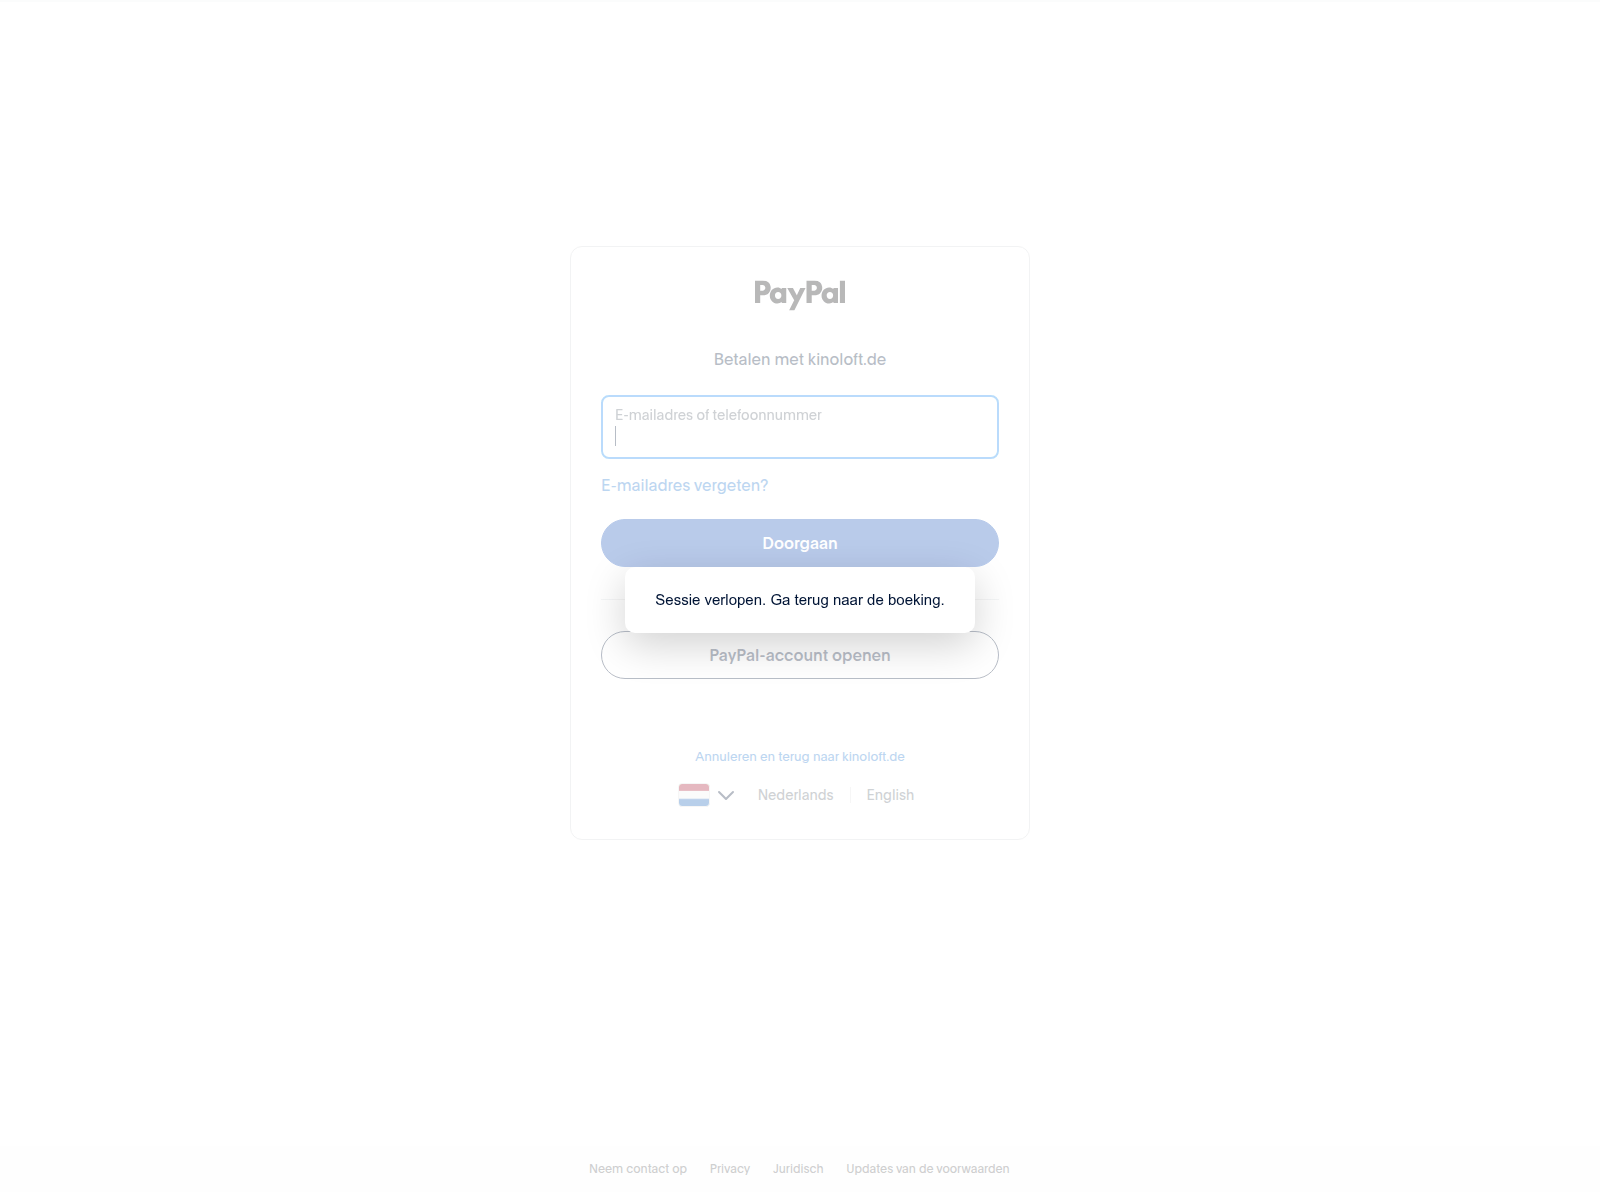
The site paypal.kinoloft.de hosted a fraudulent login page mimicking PayPal in Dutch, asking visitors to enter their account credentials. If you entered your password here, immediately change your credentials on the official PayPal site at paypal.com and secure your account.
URLScan截图 · 2026-11-21 23:19 UTC · SHA-256 1bea28a5…4ea35ad
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Dutch PayPal login clone design
The page at paypal.kinoloft.de displays the recognizable PayPal branding with the heading "PayPal" and a subtitle reading "Betalen met kinoloft.de". It features an input field labeled "E-mailadres of telefoonnummer" for email or phone number entries, accompanied by a prompt for forgotten credentials. A blue confirmation button reads "Doorgaan", positioned above an overlay popup stating "Sessie verlopen. Ga terug naar de boeking." Additional links offer to create a new account or return to kinoloft.de, while a language selector defaults to Dutch with flags for the Netherlands. Footer links include terms of service and privacy details. The layout is designed to harvest credentials by masquerading as a standard authentication portal.
Credential harvesting mechanisms and vendor telemetry
The form captures account credentials submitted by the user, routing them directly to an unauthorized third-party backend while offering no legitimate authentication services. Because Spamhaus DBL lists it as phishing, 11 of 92 engines on VirusTotal flagged it on 16 Nov 2026, and Cloudflare Radar rated it malicious (phishing), this is a confirmed malicious page rather than an isolated anomaly. Security solutions such as ESET, BitDefender and Fortinet identify the URL as a credential harvesting threat. PhishDestroy's evidence score for it is 90/100 (critical).
Shared infrastructure and related domains
The underlying hosting arrangement connects this site to a broader network of deceptive pages operated by the same actors. Specifically, 3 other reported domains resolve to the same IP address and 8 use the same nameserver pair. Related infrastructure includes paypal.kinoberry.de, paypal.kinodora.de and paypal.kinofino.de, which host similar fraudulent login or checkout templates designed to deceive users across multiple domains.
paypal.kinoloft.de — Deceptive PayPal login form in Dutch
AI 描述
paypal.kinoloft.de presented a fraudulent PayPal authentication portal, flagged by Spamhaus DBL and 11 VirusTotal engines. Do not submit account details.
AI摘要
Dutch PayPal login clone design The page at paypal.kinoloft.de displays the recognizable PayPal branding with the heading "PayPal" and a subtitle reading "Betalen met kinoloft.de". It features an input field labeled "E-mailadres of telefoonnummer" for email or phone number entries, accompanied by a prompt for forgotten credentials. A blue confirmation button reads "Doorgaan", positioned above an overlay popup stating "Sessie verlopen. Ga terug naar de boeking." Additional links offer to create a new account or return to kinoloft.de, while a language selector defaults to Dutch with flags for the Netherlands. Footer links include terms of service and privacy details. The layout is designed to harvest credentials by masquerading as a standard authentication portal. Credential harvesting mechanisms and vendor telemetry The form captures account credentials submitted by the user, routing them directly to an unauthorized third-party backend while offering no legitimate authentication services. Because Spamhaus DBL lists it as phishing, 11 of 92 engines on VirusTotal flagged it on 16 Nov 2026, and Cloudflare Radar rated it malicious (phishing), this is a confirmed malicious page rather than an isolated anomaly. Security solutions such as ESET, BitDefender and Fortinet identify the URL as a credential harvesting threat. PhishDestroy's evidence score for it is 90/100 (critical). Shared infrastructure and related domains The underlying hosting arrangement connects this site to a broader network of deceptive pages operated by the same actors. Specifically, 3 other reported domains resolve to the same IP address and 8 use the same nameserver pair. Related infrastructure includes paypal.kinoberry.de, paypal.kinodora.de and paypal.kinofino.de, which host similar fraudulent login or checkout templates designed to deceive users across multiple domains.

 150.241.66.223


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT