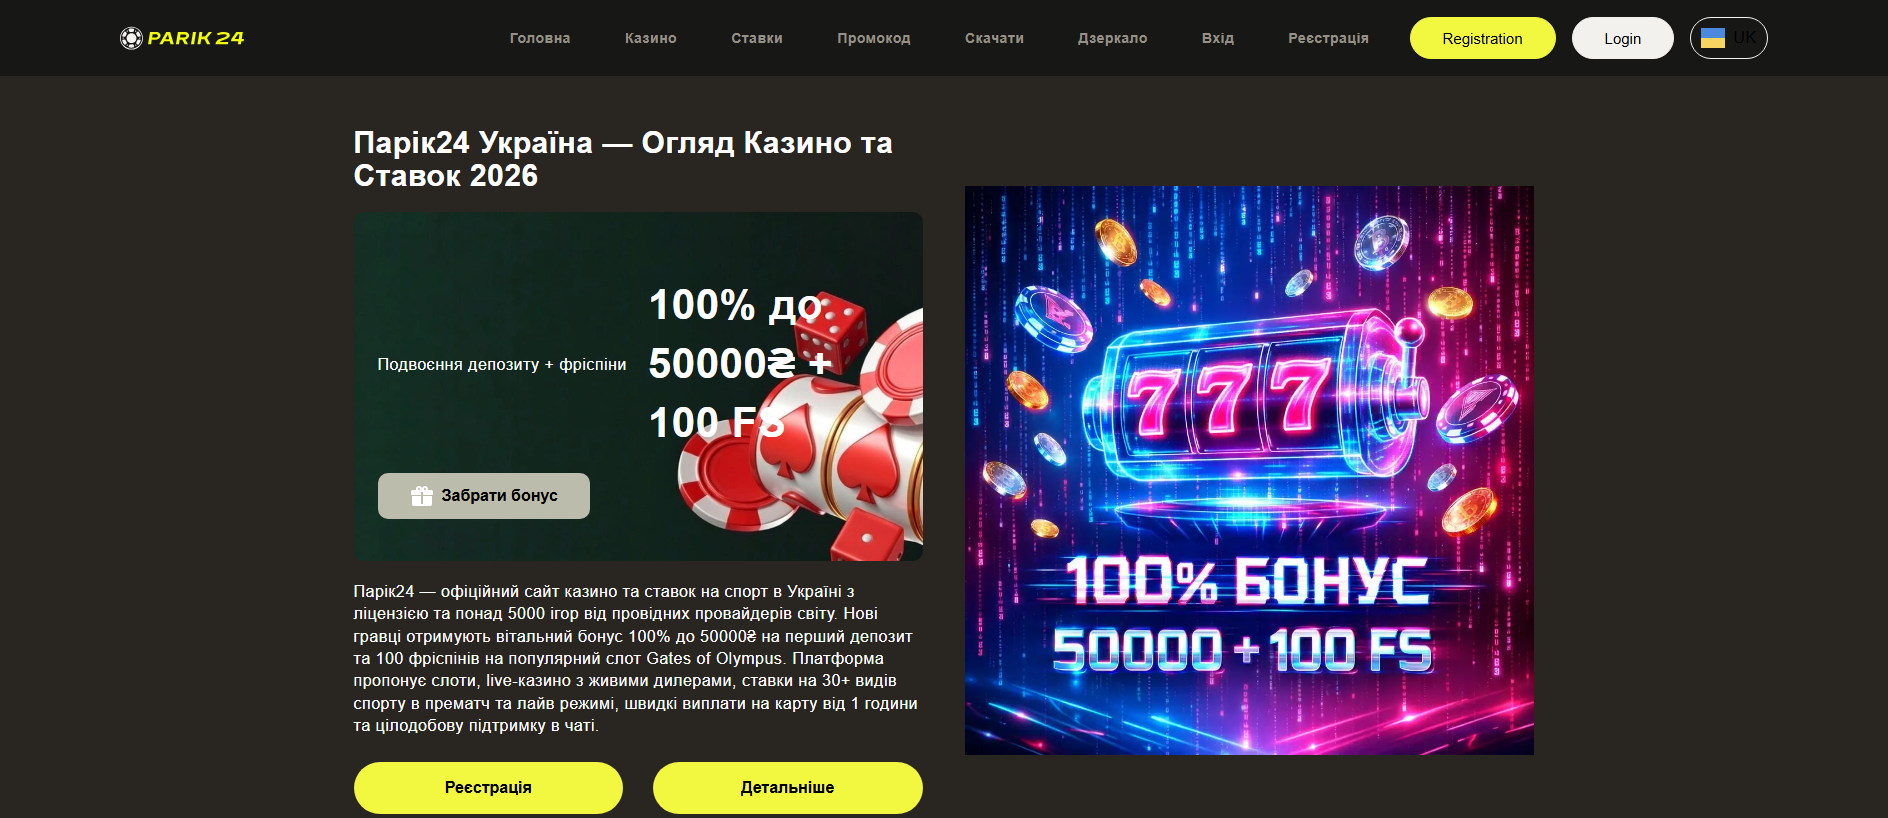
pari24.online is an impersonation phishing site that traded on the Cloudflare name. It targeted people who trust Cloudflare branding, including website owners and users who see Cloudflare screens while browsing. PhishDestroy first caught it on 2026-09-18, and the site has been offline since that same day. On our latest check, 2026-10-19, it was still dead and its content was blocked by the provider.
诈骗手法解析
Impersonation phishing borrows the look of a trusted brand so that a login form or a request for data seems routine. With Cloudflare as the cover, a victim may believe they are signing into a dashboard or passing a security check, and then hands over account credentials or other details the operator can reuse. The page title now reads "Suspected Phishing | Cloudflare", which is Cloudflare's own warning interstitial. Our classification remains impersonation phishing.
证据
On 2026-09-19, VirusTotal showed 15 of 89 security engines flagging the domain. They include alphaMountain.ai, BitDefender, Chong Lua Dao, CyRadar, Forcepoint ThreatSeeker, Fortinet, G-Data and Gridinsoft. These vendors run their checks independently, so the agreement goes beyond PhishDestroy's own listing. The domain also appears in 4 AlienVault OTX threat pulses, which means other researchers have tracked it as well.
基础设施
The domain was registered through NAMECHEAP INC on 2026-01-08, about eight months before it surfaced as phishing. A domain that sits unused for that long before going live is a common way to avoid filters aimed at brand-new registrations. Traffic passed through Cloudflare, Inc. network space geolocated to Canada. The provider has since blocked the content, and that is why the site is unreachable.
What to do
If you entered a password on this site, change it at once, starting with your Cloudflare account and then any other service that used the same password. Turn on two-factor authentication, sign out all active sessions, and look over recent account activity and API tokens for anything you did not create. If you handed over other personal or payment details, watch for follow-up phishing messages and alert your bank where it applies. Defenders should block pari24.online at DNS and the web proxy, then search their logs for visits from 2026-09-18 onward so they can find affected users.
pari24.online is an impersonation phishing domain abusing the Cloudflare brand to deceive visitors into handing over credentials or other sensitive data.
AI摘要
Overview pari24.online is an impersonation phishing site that traded on the Cloudflare name. It targeted people who trust Cloudflare branding, including website owners and users who see Cloudflare screens while browsing. PhishDestroy first caught it on 2026-09-18, and the site has been offline since that same day. On our latest check, 2026-10-19, it was still dead and its content was blocked by the provider. How the scam works Impersonation phishing borrows the look of a trusted brand so that a login form or a request for data seems routine. With Cloudflare as the cover, a victim may believe they are signing into a dashboard or passing a security check, and then hands over account credentials or other details the operator can reuse. The page title now reads "Suspected Phishing | Cloudflare", which is Cloudflare's own warning interstitial. Our classification remains impersonation phishing. Evidence On 2026-09-19, VirusTotal showed 15 of 89 security engines flagging the domain. They include alphaMountain.ai, BitDefender, Chong Lua Dao, CyRadar, Forcepoint ThreatSeeker, Fortinet, G-Data and Gridinsoft. These vendors run their checks independently, so the agreement goes beyond PhishDestroy's own listing. The domain also appears in 4 AlienVault OTX threat pulses, which means other researchers have tracked it as well. Infrastructure The domain was registered through NAMECHEAP INC on 2026-01-08, about eight months before it surfaced as phishing. A domain that sits unused for that long before going live is a common way to avoid filters aimed at brand-new registrations. Traffic passed through Cloudflare, Inc. network space geolocated to Canada. The provider has since blocked the content, and that is why the site is unreachable. What to do If you entered a password on this site, change it at once, starting with your Cloudflare account and then any other service that used the same password. Turn on two-factor authentication, sign out all active sessions, and look over recent account activity and API tokens for anything you did not create. If you handed over other personal or payment details, watch for follow-up phishing messages and alert your bank where it applies. Defenders should block pari24.online at DNS and the web proxy, then search their logs for visits from 2026-09-18 onward so they can find affected users. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a0b39d-36fc-70d9-8765-e6d9bb5c57e9/ VirusTotal report: https://www.virustotal.com/gui/domain/pari24.online Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=pari24.online Archived copy: https://web.archive.org/web/20260918082555/https://pari24.online/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/


 Namecheap
 104.21.71.46


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 MyWOT