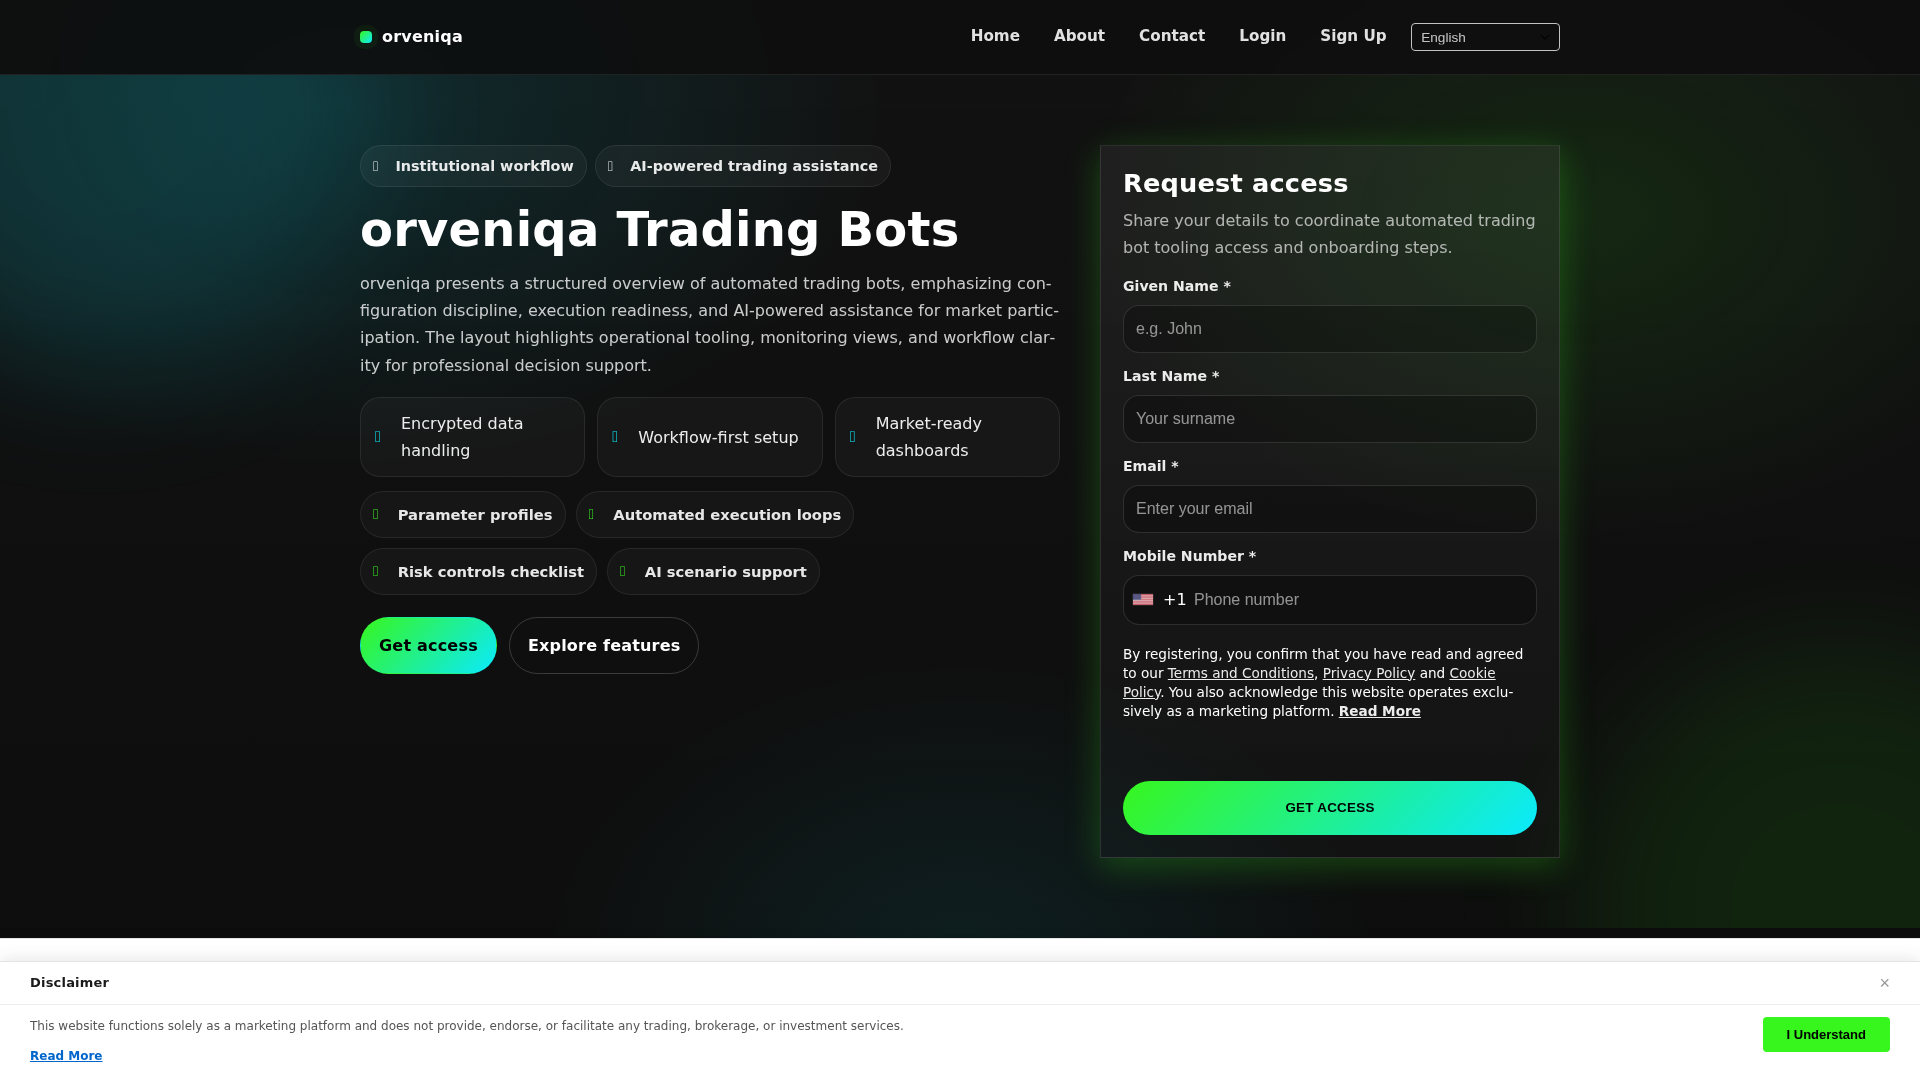
On 2026-11-01, orveniqa.shop was captured showing a dark landing page headed "orveniqa Trading Bots" with tags for institutional workflow and AI-powered trading assistance. The page describes a structured overview of automated trading bots, listing features such as encrypted data handling, workflow-first setup, market-ready dashboards, parameter profiles, automated execution loops, risk controls checklist, and AI scenario support, alongside "Get access" and "Explore features" buttons. A "Request access" panel collects given name, last name, email, and mobile number, with a "GET ACCESS" submit button.

分析报告仅提供英文版本
页面标题: “orveniqa | a premium AI trading platform | Official Website”
On 2026-11-01, orveniqa.shop was captured showing a dark landing page headed "orveniqa Trading Bots" with tags for institutional workflow and AI-powered trading assistance. The page describes a structured overview of automated trading bots, listing features such as encrypted data handling, workflow-first setup, market-ready dashboards, parameter profiles, automated execution loops, risk controls checklist, and AI scenario support, alongside "Get access" and "Explore features" buttons. A "Request access" panel collects given name, last name, email, and mobile number, with a "GET ACCESS" submit button.
The stored VirusTotal domain result reports 18 detections out of 92 engines. DNS8 reported "suspicious"; ESET reported "suspicious".
orveniqa.shop: Recorded trading bot landing page with access request form
AI 描述
PhishDestroy records the orveniqa.shop landing page presenting automated trading bot features and a request-access form for coordinating onboarding steps.
AI摘要
On 2026-11-01, orveniqa.shop was captured showing a dark landing page headed "orveniqa Trading Bots" with tags for institutional workflow and AI-powered trading assistance. The page describes a structured overview of automated trading bots, listing features such as encrypted data handling, workflow-first setup, market-ready dashboards, parameter profiles, automated execution loops, risk controls checklist, and AI scenario support, alongside "Get access" and "Explore features" buttons. A "Request access" panel collects given name, last name, email, and mobile number, with a "GET ACCESS" submit button. The stored VirusTotal domain result reports 18 detections out of 92 engines. DNS8 reported "suspicious"; ESET reported "suspicious".
The Tranco rank (how much traffic) is rather low The website was reported in the last 30 days as threat by DNSFilter This website was reported by IPQS for phishing. This website has been classified as suspicious by IPQS
证据层Availability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP注册
观测时间线last reachable: 2026-11-02 23:21 UTClast content: 2026-11-02 11:31 UTCcurrent episode first observed: 2026-11-03 22:21 UTCobserved RIP window: 2026-11-02 23:21 UTC → 2026-11-03 22:21 UTC · 22.98hmidpoint estimate ≈ 2026-11-03 10:51 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.