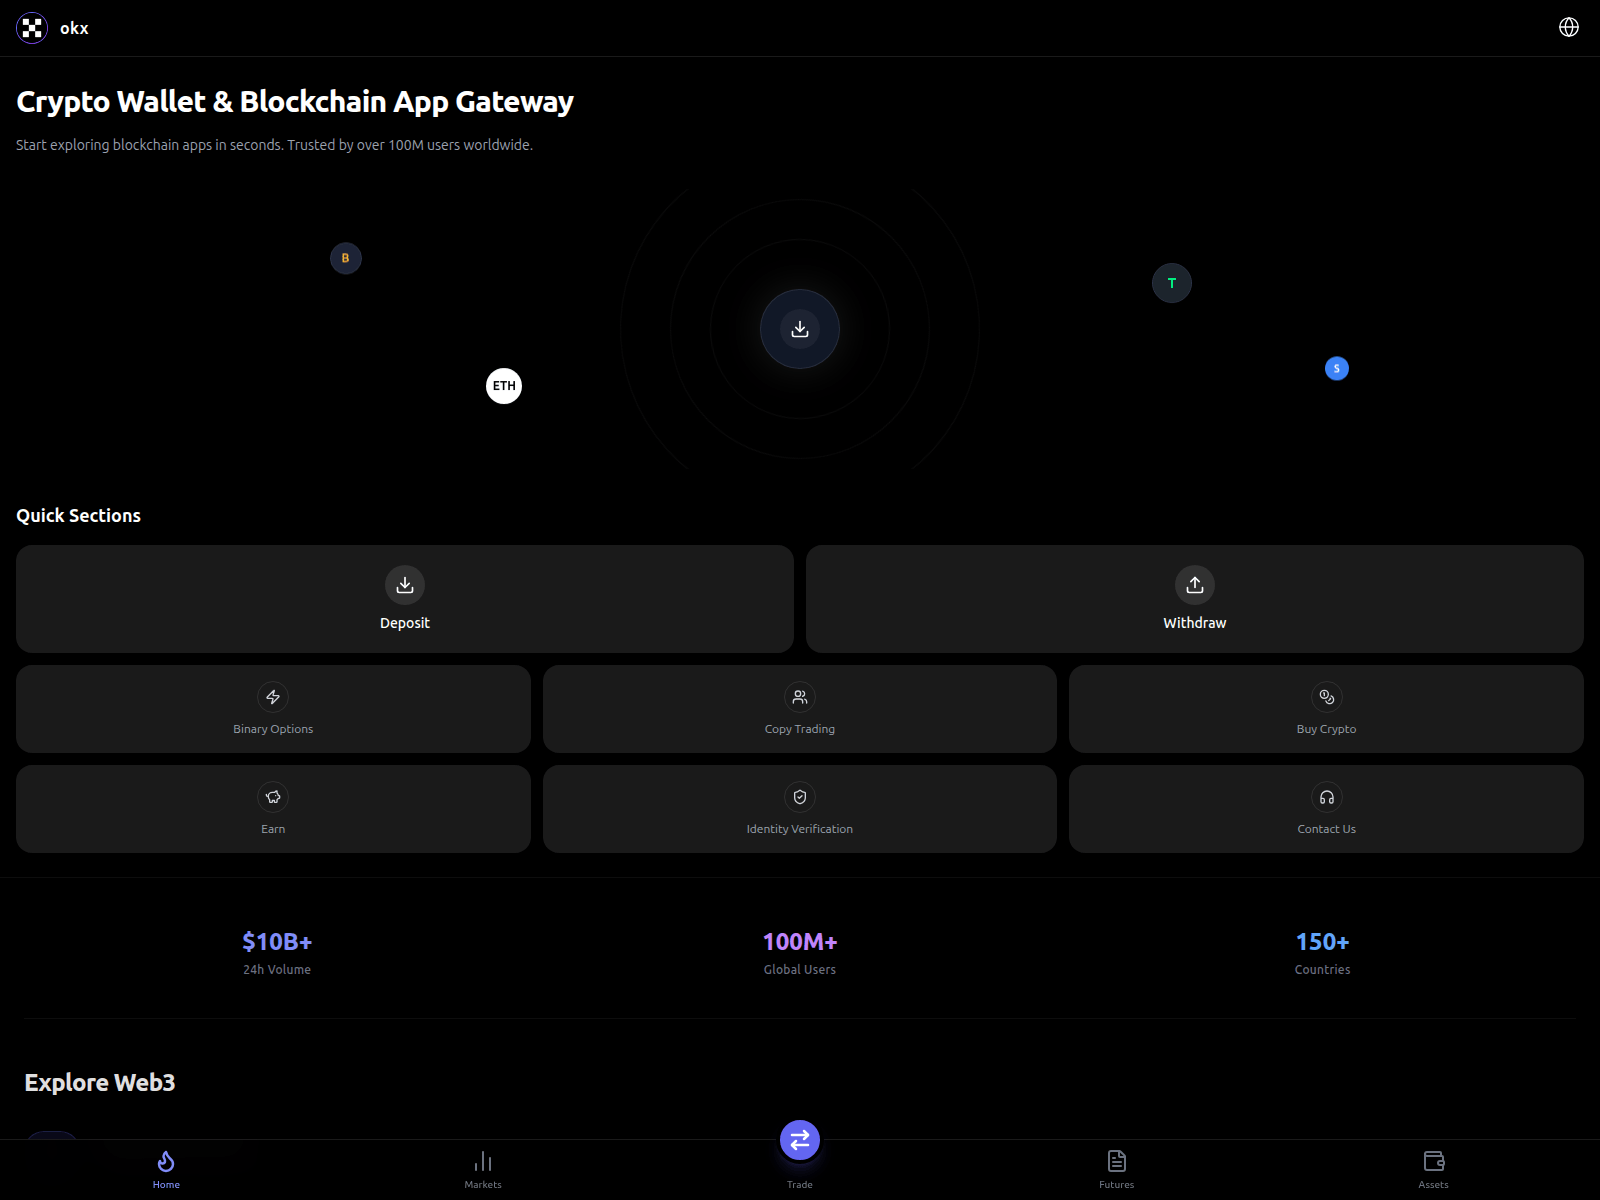
On 2026-11-09, okx-usdd.xyz displayed a dark-themed page headed "Crypto Wallet & Blockchain App Gateway," with a subtitle inviting visitors to start exploring blockchain apps and claiming trust from over 100M users worldwide. A central download icon sits among floating token badges labeled B, ETH, T and S. Below, a Quick Sections grid offers Deposit, Withdraw, Binary Options, Copy Trading, Buy Crypto, Earn, Identity Verification and Contact Us tiles, followed by statistics claiming $10B+ 24h volume, 100M+ global users and 150+ countries, plus an Explore Web3 heading and a bottom navigation bar.
URLScan截图 · 2026-11-09 13:30 UTC · SHA-256 40fe746d…71e5739
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-09, okx-usdd.xyz displayed a dark-themed page headed "Crypto Wallet & Blockchain App Gateway," with a subtitle inviting visitors to start exploring blockchain apps and claiming trust from over 100M users worldwide. A central download icon sits among floating token badges labeled B, ETH, T and S. Below, a Quick Sections grid offers Deposit, Withdraw, Binary Options, Copy Trading, Buy Crypto, Earn, Identity Verification and Contact Us tiles, followed by statistics claiming $10B+ 24h volume, 100M+ global users and 150+ countries, plus an Explore Web3 heading and a bottom navigation bar.
The stored VirusTotal domain result reports 12 detections out of 92 engines. CRDF reported "malicious"; ESET reported "phishing".
PhishDestroy records okx-usdd.xyz as a page presenting a Crypto Wallet & Blockchain App Gateway with deposit, withdraw, trading and identity verification sections.
AI摘要
On 2026-11-09, okx-usdd.xyz displayed a dark-themed page headed "Crypto Wallet & Blockchain App Gateway," with a subtitle inviting visitors to start exploring blockchain apps and claiming trust from over 100M users worldwide. A central download icon sits among floating token badges labeled B, ETH, T and S. Below, a Quick Sections grid offers Deposit, Withdraw, Binary Options, Copy Trading, Buy Crypto, Earn, Identity Verification and Contact Us tiles, followed by statistics claiming $10B+ 24h volume, 100M+ global users and 150+ countries, plus an Explore Web3 heading and a bottom navigation bar. The stored VirusTotal domain result reports 12 detections out of 92 engines. CRDF reported "malicious"; ESET reported "phishing".
证据层Availability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP注册
观测时间线last reachable: 2026-11-16 11:05 UTClast content: 2026-11-16 11:05 UTCcurrent episode first observed: 2026-11-17 17:12 UTCobserved RIP window: 2026-11-16 11:05 UTC → 2026-11-17 17:12 UTC · 30.13hmidpoint estimate ≈ 2026-11-17 02:09 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 85.137.56.230


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT